Security Feed
Cybersecurity news & advisories
500 articles 45 of 45 sources updated RSS ↗







Latest
Signal Vulnerability Lets Malicious Callers Block Hang-Ups
Affecting the open source calling library RingRTC, the bug prevented calls from ending properly.
Tech and Security Companies Respond to PHP2Shell Vulnerabilities
Vendors are checking their products for PHP2Shell, security firms are shipping detections, and governments are urging immediate patching.
Hackers pile on PHP2Shell as AWS reveals attacks began before disclosure
Attackers are hammering servers with millions of attempts to exploit the critical PHP2Shell vulnerabilities, with Amazon revealing that someone was already going after the flaws four days before they were publicly…
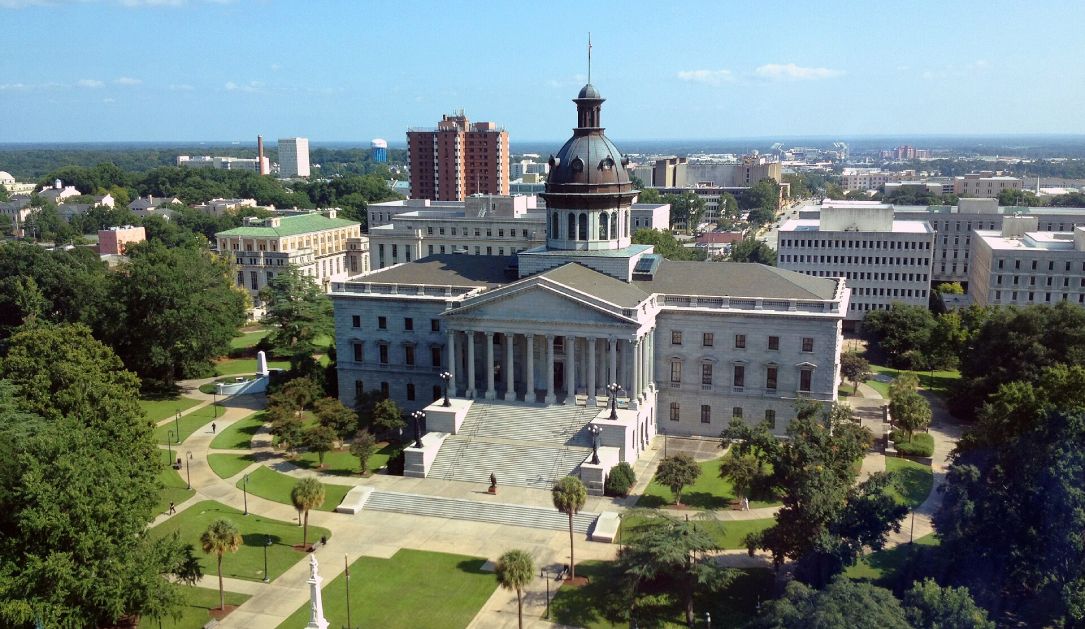
South Carolina officials offer assistance after state capital hit with cyberattack
The systems impacted by the attack include the MyColaSC platform that citizens use to pay utility bills, report non-emergency issues and access other city services.
GitLab warns of new max severity code execution vulnerability
GitLab has released security patches for a maximum-severity Regular Expression Compiler flaw that can let remote attackers run arbitrary code on vulnerable servers.
333 Tor exit nodes hijacked to intercept SSH traffic and retrieve plaintext email
Unknown hackers hijacked more than 300 Tor exit nodes and reconfigured them to favor unencrypted email traffic and redirect SSH connections through servers they controlled, a researcher reported Tuesday. The hijacking…
Microsoft says ConnectWise breach let Chinese spies loose on 2,250 cloud tenants
China-aligned attackers used AI agents and compromised ConnectWise application credentials to target more than 2,250 Microsoft 365 tenants, Microsoft says. The Windows giant revealed this week that the attackers…
Woman faces years in prison over a Cash App account she says she never opened
A Cash App account opened in her name has left Amanda Smith facing criminal charges and potentially up to six years in prison. 404 Media reports that Smith says someone used her Social Security number (SSN) and date of…

Railway Says Intruder May Have Accessed Customer Secrets, Urges Credential Rotation
Platform-as-a-Service (PaaS) provider Railway on Wednesday disclosed "anomalous activity" related to systems that store customer environment variables. Upon further investigation, the company found that an unauthorized…
New Android Malware Replaces Legitimate Banking Apps With Malicious Copies to Bypass Security Checks
A newly identified Android banking Trojan called Hirudo takes an unusual route to financial fraud: it tries to remove a victim’s genuine banking app and install a modified copy in its place. The replacement keeps the…
Microsoft: Chinese State Actor Used AI to Compromise ConnectWise Tenants
Microsoft said it has observed threat actor activity in multiple ConnectWise customer environments, with the attackers leveraging the ARTEX agentic AI platform
Splunk, SolarWinds Release Fresh Security Updates
Patched vulnerabilities could allow attackers to execute code, elevate privileges, and leak sensitive information.
OpenCode Flaw Lets Malicious MCP Servers Execute Code During Sign-In on Windows and WSL
A flaw in the OpenCode AI coding agent allowed a malicious or hijacked MCP server to run code on a developer's Windows or WSL machine when the developer signed in. OpenCode connects to MCP (Model Context Protocol)…

Top 10 Best Secure File Sharing Platforms in 2026 [Ranked & Scored]
Users share files the easiest way available your only real choice is whether the easiest way is also the governed one. The 2026 secure-sharing shortlist is judged on that bargain: consumer-grade usability on top of…

Atlassian Releases Massive Security Update Addressing 176 Flaw Entries in Jira and Confluence
Atlassian has released its October 2026 security bulletin, covering 176 flaw entries across products including Jira, Confluence, Bamboo, Bitbucket, and Crowd. Published on October 20, the update lists 162 high-severity…
PHP2Shell Exploitation Attempt Detected by Amazon Four Days Before Vulnerability Disclosure
Threat intelligence analysts now observe large-scale evidence of exploitation of the two critical PHP vulnerabilities
Cisco Patches 34 Vulnerabilities Across Multiple Products
Critical-severity security defects could lead to command execution, authentication bypass, and XSS attacks.
Encryption isn’t enough to protect data wherever it goes
Cybersecurity policy has long treated data protection as a systems problem: encrypt the database, secure the network, restrict access, monitor activity, and keep attackers out. All of that still matters. But those…
IT department and auditors at major pharmacy chain got into a rip-roaring fight about using 'password' on Cisco firewall
Welcome back to PWNED, the column where we talk about companies and organizations that leave the doors wide open to attackers. This week’s sad story involves a major American pharmacy chain that couldn’t fill a…

Top 10 Best Enterprise DRM & Information Rights Management Solutions in 2026 [Ranked & Scored]
Perimeters don’t follow files. The deal model emailed to a counterparty, the design doc shared with a contractor, the board pack synced to a trustee’s tablet enterprise DRM (information rights management) keeps policy…
PHP2Shell Exploitation Started Days Before Patches
Initial attempts were observed on October 17, and mass activity began shortly after patches were released.
Delivery bots accused of illegally scanning customers
Two Chicago customers say robots delivering their groceries and takeout scanned their faces and hands without consent, stored the data alongside their names and addresses, and used the recordings to train AI . Their…
Fortinet Urges Customers to Patch Critical Flaws Affecting FortiOS, FortiManager, and FortiAnalyzer
Fortinet has urged customers to prioritize security updates for FortiOS, FortiManager, and FortiAnalyzer scheduled for October 22, 2026. The coordinated release addresses critical and high-severity vulnerabilities…

Samsung and Vizio Smart TVs Still Send Tracking-Like Traffic After Users Turn It Off
Samsung and Vizio smart TVs kept sending traffic consistent with automatic content recognition (ACR) even after researchers turned off the feature in the privacy settings. The findings raise questions about whether…
Hackers Actively Exploiting Siemens Software Center Flaw in ClickFix Malware Attacks
Hackers are exploiting a DLL side-loading flaw in Siemens Software Center to run malware through a trusted, signed application. Tracked as CVE-2026-110936, the weakness affects versions before 4.0.9.8. Siemens has…
LiteLLM Suspects GitHub Token Leak in AI Gateway Logs Behind Malicious Package Release
LiteLLM on Wednesday disclosed that threat actors compromised "multiple independent security controls" to push a malicious version of the Python package containing a credential stealer and a backdoor. On October 21…
Authorities disrupt nearly 11,000 cybercrime networks in Africa
Law enforcement agencies have disrupted nearly 11,000 cybercriminal networks and arrested more than 1,400 people in Operation Serengeti III, which targeted business email compromise, ransomware, and online scams.
Critical Signal Vulnerability Could Keep Your Mic and Camera Live Even After Hang Up
A critical vulnerability in Signal’s calling library could allow a malicious call participant to keep hearing audio after another user tries to hang up. The flaw, tracked as CVE-2026-113380, affects RingRTC versions…
Cloud Security Maturity Lags Despite Widespread Adoption, SANS Warns
Nearly all organizations now run production workloads in the cloud, but a new SANS survey found most have yet to achieve mature cloud security programs

Hackers Are Using Real Dell and Staples Emails to Make Their Scams Look Legitimate
Hackers are abusing genuine Dell and Staples order emails to make fake purchase alerts look credible. Instead of sending a forged message, they place scam instructions inside order details that trusted retail systems…

Node.js Brotli Decoder Bug Could Allow Remote Code Execution in All Supported Versions
Node.js released security updates on October 21 for its three supported release lines, 22.x, 24.x and 26.x, fixing 10 flaws. The most serious is a bug in the Brotli decompression code that Node.js bundles, which the…
Oracle Patches Over 1,200 Vulnerabilities With October 2026 CPU
Nearly 100 vulnerabilities have been assigned a critical severity rating and Fusion Middleware received the most patches.
Meta Ordered to Pay New Mexico $25 Billion for Deceiving Users About Privacy on Facebook
The $25 billion award far exceeds a $5 billion fine the Federal Trade Commission levied against Facebook in 2019.

Hackers Used Claude and Grok to Automate Cyberattacks on Over 400 Banks and Financial Firms
A cybercrime group used artificial intelligence (AI) agents to coordinate attacks against more than 400 banks, payment providers and other financial organizations across Latin America, according to a report by…

New QPACK Flaws Can Crash HTTP/3 Servers, Trigger Up to 4,000-Fold Memory Amplification
A remote attacker who has not logged in can crash many HTTP/3 web servers with a single connection, security firm FoxIO disclosed, releasing working proof-of-concept code. By sending a small batch of compressed HTTP…
Certification authority eMudhra defends its laughably weak private keys
Indian certification authority eMudhra has defended the laughably weak private keys it used to sign some digital certificates it issued, and suggested others should share the blame for the incident. In case you’re…

Someone Tried to Exploit PHP2Shell 4 Days Before the Vulnerabilities Were Publicly Disclosed
Amazon's Threat Intelligence team on Wednesday said it detected an attempt to exploit the newly disclosed PHP2Shell vulnerabilities on October 17, 2026, against its MadPot honeypot service, as the flaws come under broad…
How APT41 revived the BlackLotus bootkit to attack diplomatic organizations in Central Asia
Introduction Back in October 2022, Kaspersky GReAT was looking into a peculiar advertisement on a hacking forum. A cybercriminal had been advertising a UEFI bootkit, dubbed BlackLotus, that could bypass Secure Boot, for…
UAE Transitions 50% of Gov't Services to Agentic AI
The United Arab Emirates says it's creating a foundation of security and safety as it transforms its public service footprint.

China-Linked Hackers Use ARTEX AI Agents in ConnectWise Supply Chain Attack
Microsoft on Wednesday disclosed that a China state-aligned actor dubbed Storm-0940 was behind the recent supply chain compromise of the ConnectWise Cloud Backup application. During the incident, Storm-0940 used ARTEX…

Hackers Exploited the PHP Vulnerabilities Days Before They Were Patched
Amazon Web Services logged attempts to leverage the internet-melting PHP2Shell bugs four days ago. They’re now being “broadly exploited” across the internet.
Vulnerabilities in PHP Affecting Cisco Products: October 2026
On October 21, the PHP Foundation announced the availability of a Critical PHP Security release addressing two critical vulnerabilities: CVE-2026-109618 - RCE via OOM corruption CVE-2026-109619 - RCE via stale global…
Smashing Security podcast #489: How a brand new crypto wallet came with a spy inside
Imagine buying a brand new hardware wallet for your cryptocurrency with the shrink-wrap still on... what could possibly be hiding inside? We break out a Geiger counter and a cat to find out. Meanwhile, malicious ads are…
PHP blames supply chain security biz Chainguard for putting huge chunks of the web at risk
PHP developers have accused software supply chain security shop Chainguard of effectively revealing critical bugs in the open-source scripting language ahead of a planned official disclosure. On Wednesday, just hours…
Google Chrome adds Gemini-powered scam detection, warns users of ClickFix attacks
Chrome is getting new scam protections that use Gemini to detect deceptive websites and warn users when they copy suspicious commands from ClickFix attacks.
Microsoft pins ConnectWise supply-chain attack to China-state aligned threat group
Microsoft researchers attributed the recent supply-chain attack targeting ConnectWise customers ’ Microsoft 365 environments to a China-state aligned threat actor it tracks as Storm-0940. “As early as September 2026…
Japan's Onamae Desktop Cloud hacked, up to 27,000 servers affected
Hackers compromised the infrastructure of Onamae Desktop Cloud, a popular provider of VPS services in Japan, and installed malware on up to 26,739 customers' servers.

TiDB Breach Exposes Flawed Cloud Security Assumptions
Cloud providers may be storing sensitive customer data, without either party knowing it. But when a provider is breached, the data comes home to roost.
Critical PHP Vulnerability (CVE-2026-109618, CVE-2026-109619) [infocon yellow], (Wed, Oct 21st)
PHP.net announced that it will release a critical update today. We decided to change the infoCon to YELLOW due to the widespread use of PHP, the expected severity of the flaw (CVSS 9.4), and the availability of early…
Compromised eMudhra intermediate certificates
Cisco Talos is aware of eight intermediate certificates belonging to the intermediate certificate authority, eMudhra . Rather than possessing the mandatory 384 bits of pseudo-random security, several private keys…
Lazarus hackers use post-quantum cryptography for malware delivery
North Korean hackers are using a post-quantum cryptographic mechanism to secure malicious payload delivery in new operations that combine old and new malware.
Meta on the spot for $25 billion under New Mexico privacy ruling
The Cambridge Analytica data privacy scandal from a decade ago is still weighing on Meta's finances.

Marvell, Microsoft & Oracle Work to Standardize Data Center Hardware Security
The effort is aimed at standardizing a NIST FIPS 140-3 Level 3 integrated HSM for cloud and hyperscale data center infrastructure.
Cloud Security Alliance Survey Finds Data Loss Prevention Often Detects Data Loss Only After It Happens
Research finds that, among respondents experiencing data loss, only 16% said DLP blocked their most significant incidents before data left the organization.
Tech trio launches $10 million initiative to help under-resourced utilities bolster cybersecurity
Up to 500 under-resourced utilities will receive support in order to bolster their cybersecurity through a private sector initiative launched this week.
'PHP2Shell' Bugs Signal Red Alert for Security Industry
Security teams are scrambling to remediate two critical PHP vulnerabilities following leaked details and reports of exploitation attempts.
Critical GitLab Flaw (CVSS 10.0) Could Allow Unauthenticated RCE Across 12 Years of Releases
GitLab released fixes on October 21 for a flaw that lets an attacker run code on a self-managed server without logging in, and it affects every version of the software going back to 7.0, released in 2014. The fix…
WhatsApp’s chatbot was given hidden instructions to not mention privacy regulators
WhatsApp instructed its AI support chatbot not to recommend contacting privacy regulators when users couldn’t delete their accounts, researchers found. Privacy software company Redact discovered the hidden text on…
CISA: Hackers chain Plex flaws in Plex2Shell attacks to breach servers
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning that attackers are actively exploiting four vulnerabilities in Plex Media Server.