Cybersecurity news & advisories




Exposed GitLab project email addresses let attackers push code
Private GitLab email addresses that allow developers to push issues or tasks to a project are being deliberately exposed in READMEs, contributing guides, and support pages used to collect bug reports.
This ‘World of Warcraft: Forever’ Mod Blocks All Interactions With Asmongold Fans
The beta for the hotly anticipated World of Warcraft: Forever has been marred by fans of the streamer Asmongold who have filled the game’s public spaces with spam and slurs . To fix the issue, a player named Solastro…
Cisco Identity Services Engine Authentication Bypass Vulnerabilities
Multiple vulnerabilities in Cisco Identity Services Engine (ISE) and Cisco ISE Passive Identity Connector (ISE-PIC) could allow a remote attacker to access or manipulate data, obtain sensitive information, or cause a…
Phone-hacking company that won U.S. security agency contracts hid Russian ownership, DOJ alleges
Law enforcement has arrested two leaders of a Russian-owned phone hacking company used by Kremlin agencies who allegedly masked its foreign ownership from the U.S. Defense Department, Department of Homeland Security and…
Decades-old file security flaws found in Android, Linux, macOS, and Windows
Security researchers affiliated with Austria's Graz University of Technology have found flaws in the implementation of file notification systems on Android, Linux, macOS, and Windows that leak potentially compromising…
CVE flood pushes Ubuntu onto weekly kernel release cycle
Canonical is speeding up Ubuntu kernel releases to one a week as AI-assisted bug hunting helps bury defenders under an ever-growing pile of CVEs. The Ubuntu maker is overhauling how it ships kernel Stable Release…
Kontext Security Emerges With $4 Million for AI Agent Runtime Controls
The startup’s runtime enforcement platform evaluates AI agents in real time to provide visibility and control over their actions.
Placeholder third-party[.]com Referenced Across 1,700+ Repositories Now Serves Malicious Content
The "third-party[.]com" domain, commonly used as a documentation placeholder, has been observed serving a ClickFix lure to Windows browsers while displaying a harmless decoy to other users. "third-party[.]com has been a…
Someone went shopping in ASUS's eShop – for customer data
Asus has warned eShop customers that an intruder got into part of its online store and may have helped themselves to contact details and order records. The PC maker disclosed the incident in an email sent to customers…
Emerging Ransomware Gang Uses Backup Destruction Threats to Pressure Victims
Ransom notes by n0n ransomware claim to take double extortion to a new level of danger for victims
3 Cyber Threats That Defined the Summer of 2026
This installment of the Reporters' Notebook video series discusses the impact of AI agents breaching Hugging Face, Fairlife's ransomware attack, and Iranian-linked threat actors compromising a dozen US water systems. It…
OpenAI Agents Probed Websites for Vulnerabilities While Fetching Public Data
Australia disclosed that an OpenAI agent gained unauthorized access to non-public government information.
Hacked Ukrainian Sites Serve Fake Cloudflare ClickFix Lures for Psychedelic Stealer
An active ClickFix campaign has been observed compromising legitimate Ukrainian business websites to inject bogus Cloudflare verification pages and trick victims into downloading a previously undocumented information…
How to Build A SASE Framework for Modern Cybersecurity
Keeping edge computing safe requires organizations to fundamentally rethink security governance. Here is a path forward: a step-by-step guide to building a SASE framework.
FedRAMP VDR & VER: Daily Scans Are Only the Beginning
FedRAMP's new VDR and VER requirements make vulnerability management more continuous, with faster scanning, tighter remediation deadlines, and stronger evidence requirements. Anecdotes explains why the December 7…
Managed or Modified: Choose How Huntress Hardens Microsoft 365
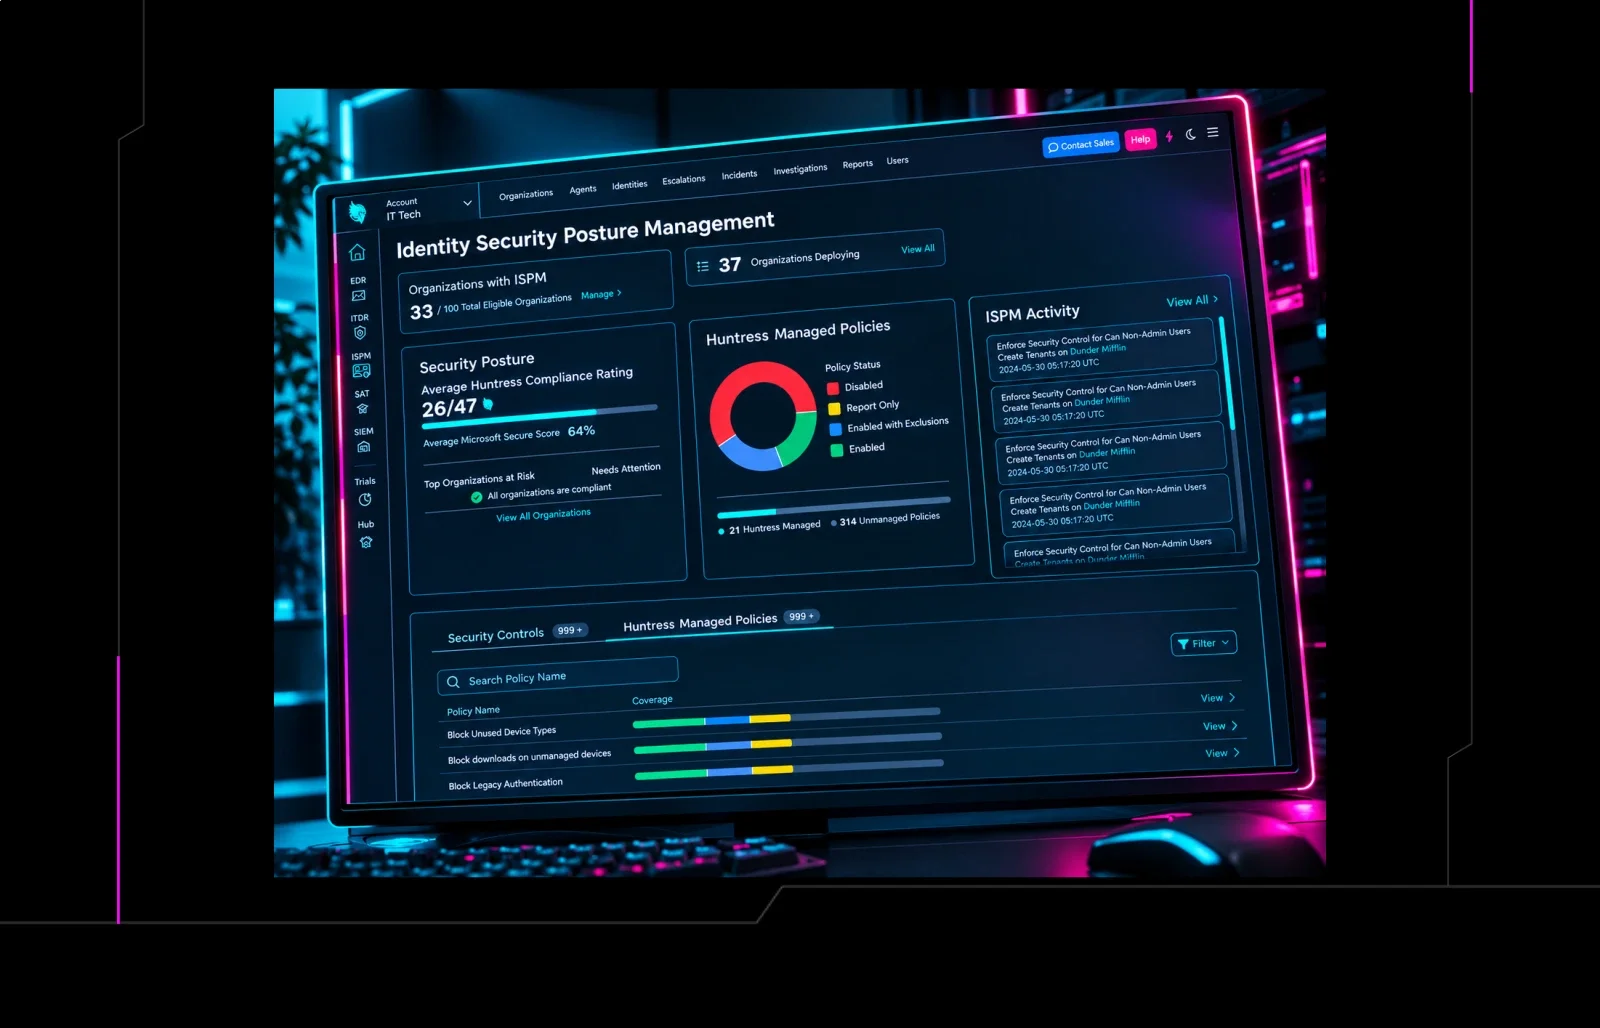
Managed ISPM now offers two deployment modes. Choose fully automated hardening or full control over which Microsoft 365 controls roll out, and when. See how it works.
Bipartisan Senate leaders introduce bill to bolster telecom cybersecurity in response to Salt Typhoon hacks
Two Senate committee leaders are introducing legislation to foster cybersecurity standards for the telecommunications sector nearly two years after the landmark Salt Typhoon campaign was made public. First reported by…

Fake PDF Files Hide Konni Malware Campaign Targeting Ukraine Organizations
A newly documented campaign targeting people and organizations focused on Ukraine uses document-themed Windows shortcuts to install a malware downloader called VelvetCake. The goal appears to be gathering political and…
Ghost Service Accounts Enable M365 Data Theft in Chile
Even if the organization locks down employee accounts, forgotten and lost service accounts can still undo the organization's entire M365 environment.
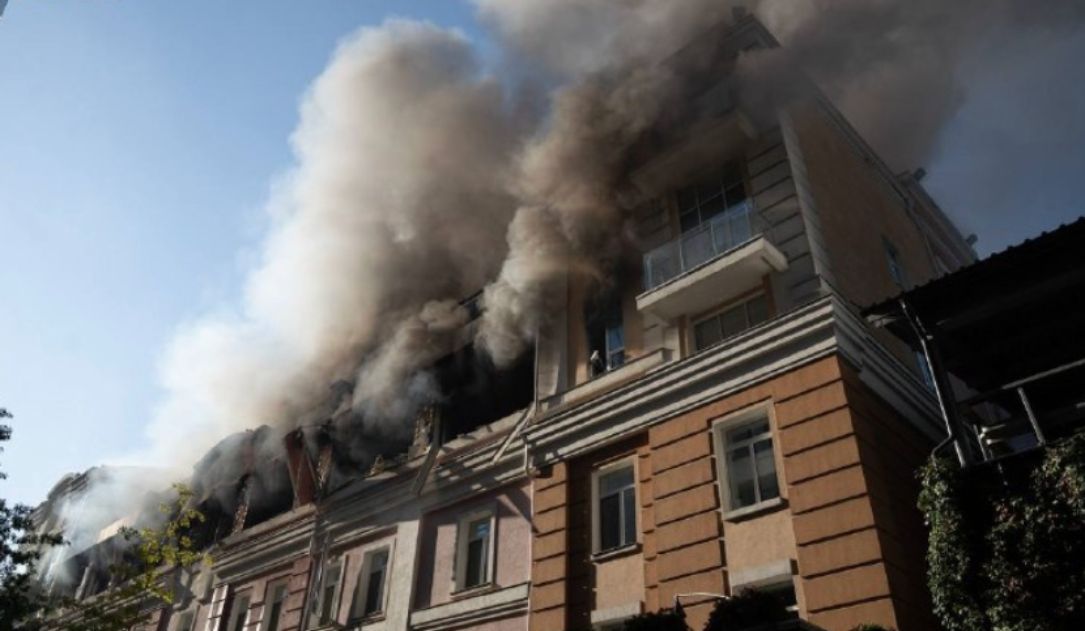
Kyiv internet providers report major outages after Russian attacks damage data centers
At least four internet providers serving Kyiv and other parts of Ukraine suffered partial connectivity losses following Wednesday’s drone attack, according to internet monitoring group NetBlocks.
Hackers now exploit critical Roundcube flaw in code injection attacks
A high-severity Roundcube Webmail vulnerability patched in May is now being actively exploited in attacks, according to the Canadian Centre for Cyber Security.
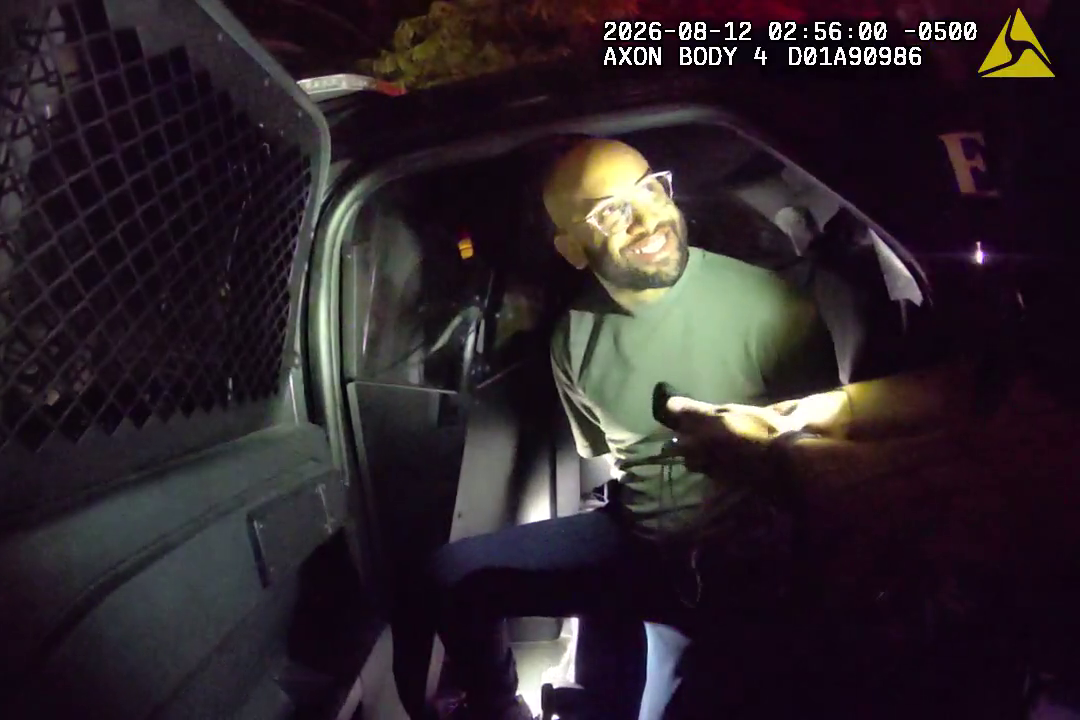
Watch Body Cam of Man Arrested for Just Cussing at a County Meeting
Last month Fort Worth, Texas police arrested political activist EJ Carrion a week after he cursed at a city council meeting. In his driveway, they told him the charge was “disrupting some kind of procession,” according…
OpenAI agent breached Australian government site, took months to report it
An OpenAI agent didn’t take “no” for an answer when it encountered a government website’s access controls. It got through, prompting Australia’s Prime Minister Anthony Albanese to raise his concerns directly with OpenAI…
Astrana latest healthcare tech firm to report data breach to SEC
The healthcare firm Astrana warned regulators that hackers accessed confidential information by impersonating company personnel.
Scan for Good: Using AI to discover and fix high-priority exposures across public services and critical infrastructure
New initiative partners with under-resourced organizations to uncover, remediate exploitable risk at scale.
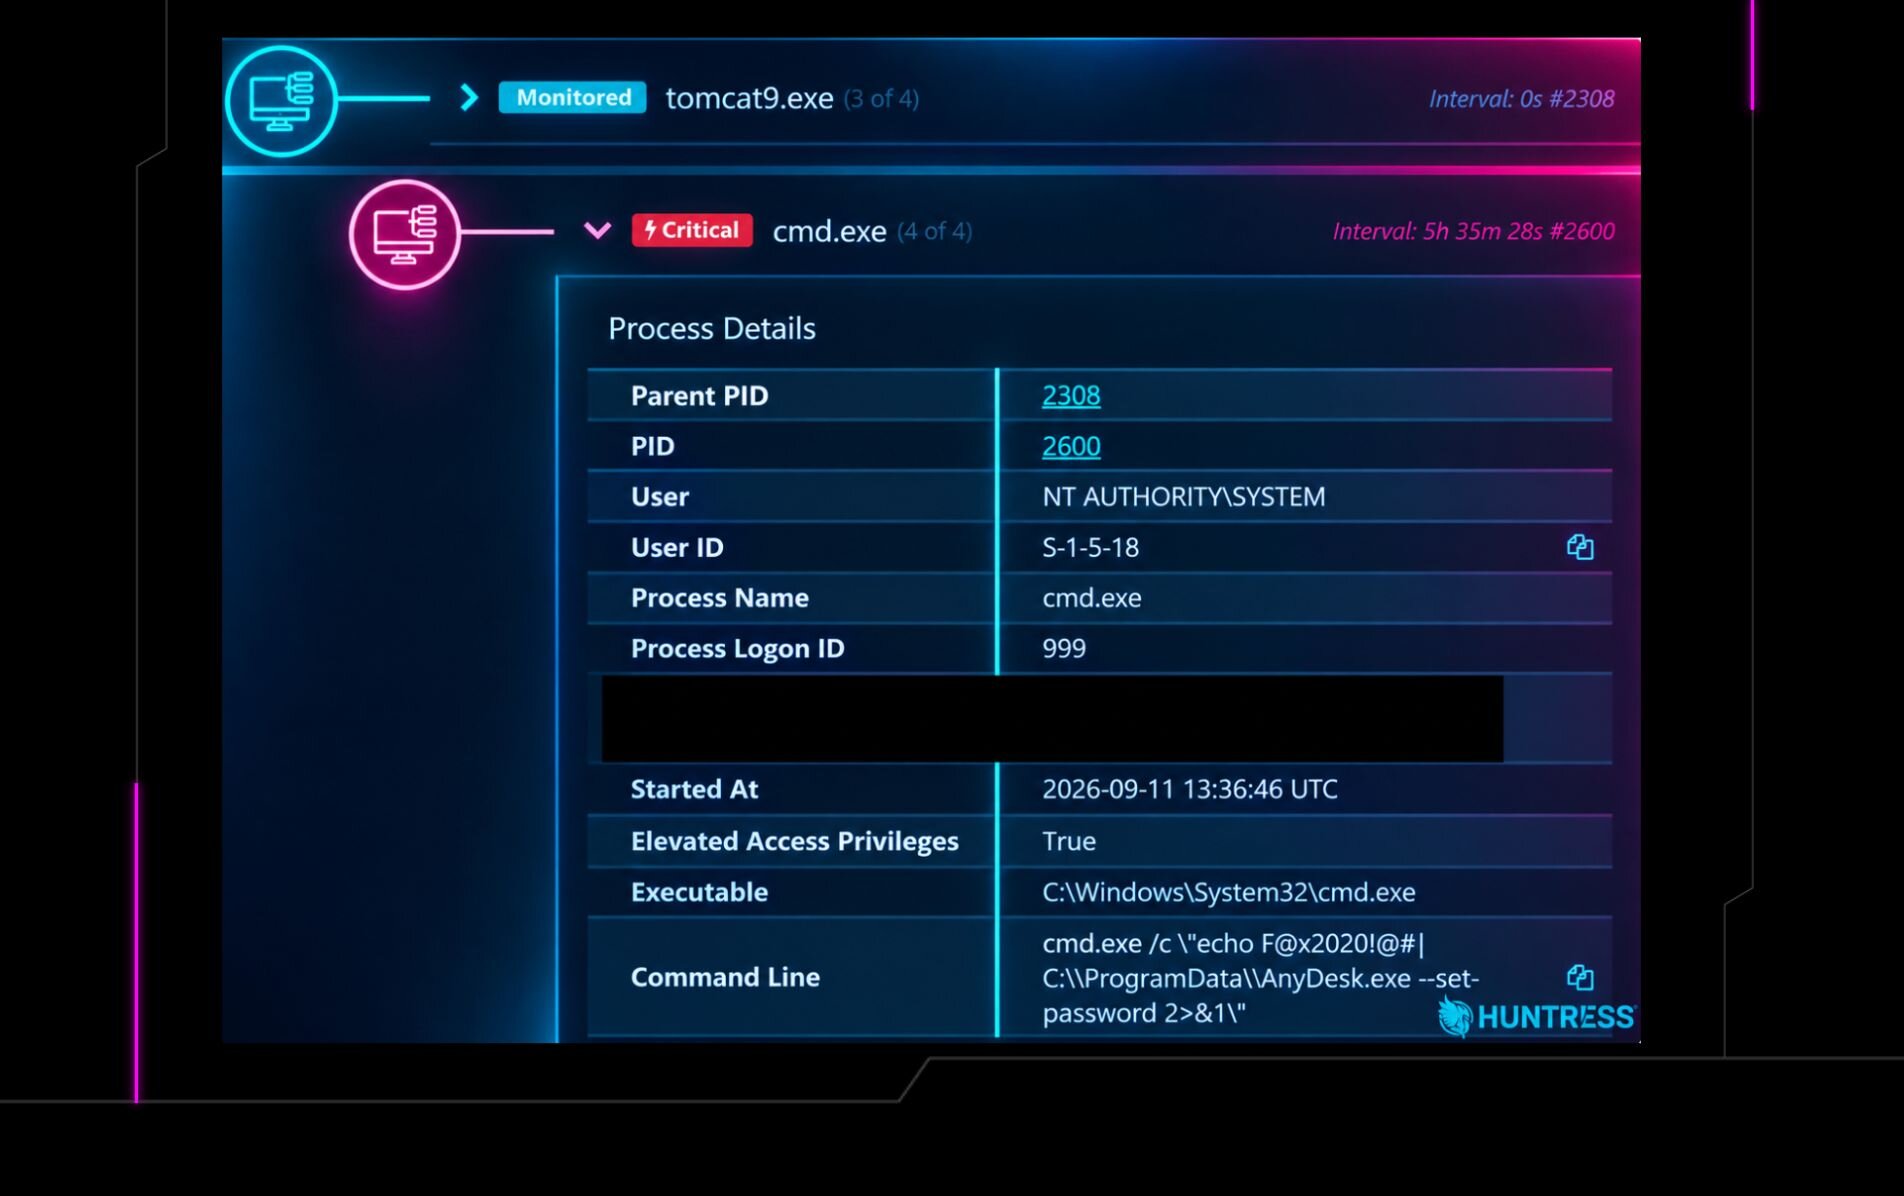
The Not So Silent Miner: Threat Actor Compiles Cryptominer on the Endpoint
Threat actors exploited Samsung MagicINFO to install AnyDesk, disable Defender, and compile a Monero miner directly on a victim endpoint. Learn the detection signals.
Prompt-Injection Bug Hits $4B Agentic AI App 'Manus'
AI apps that interpret external data (read: most AI apps) need exceptionally rigorous security filters, or attackers can take advantage.
Google to critical infra orgs: Our AI scanners won't be evil, promise
Google has jumped on the AI-defense-for-critical-systems train with its Scan for Good initiative, and says that its threat-hunting models have already autonomously uncovered critical security issues at hospitals, a…

When Business Email Compromise Starts Rewriting Reality
Business Email Compromise (BEC) operates on a familiar playbook. Threat actors breach a mailbox, silently monitor operations, map approval chains, and ultimately exploit that access to divert funds or exfiltrate…
CISA Charts New "Quality Era" for Global CVE Program
CISA has set out a new framework to improve CVE data quality as vulnerability volumes rise
AI-Powered Campaign Targets Hundreds of Online Retailers
A threat actor is using three AI harnesses for vulnerability research, exploitation, and attack orchestration.
New Browser Guard features add protection before and after you click
Most of us click on search results without knowing much about the website we’re about to visit. And once we’re there, it’s not always obvious when something isn’t quite right. Now, we’ve added two new features to…
Ukrainian ransomware developer jailed for nearly 13 years
A court in Zurich has sentenced a Ukrainian man to 12 years and nine months in prison, and banned him from Switzerland for ten years, for developing ransomware that blackmailed companies around the world.
OpenAI agent breached Australian government health website, Albanese says
An OpenAI agent gained “unauthorized access” to “non-public files” from an Australian government health website in June, Prime Minister Anthony Albanese said.
Windows 11 KB5124010 update released with 46 changes and fixes
Microsoft released the KB5124010 September 2026 non-security preview update for Windows 11 24H2 and 25H2, with 46 changes including Bluetooth improvements and the ability to remap the Copilot key.

AvisLoader Windows Malware That Learned to Survive Even After Its Servers Are Taken Down
AvisLoader is a Windows malware loader built to keep taking instructions after server takedowns. That makes it difficult to disrupt by simply removing a malicious website. It starts with a fake document-signing page…

Corp MDM Spyware Targets Logistics Firms, Steals New SMS and Redirects Calls
The logistics sector has become the target of a new malicious cyber campaign that distributes an Android spyware codenamed Corp MDM. According to Have I Been Squatted, the campaign uses fake Google Play pages branded as…
Botslab G980H Dashcams
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to bypass authentication controls, gain unauthorized access to sensitive data and privileged device functionality, modify device…
Siemens Mendix Runtime (Update A)
View CSAF Summary This advisory is revoked. Re-investigation confirmed the reported behavior is expected platform configuration and does not expose the protected attribute. The following versions of Siemens Mendix…
Eufy Omni C20, Omni X10 Pro
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to run system level commands or execute arbitrary code. The following versions of Eufy Omni C20, Omni X10 Pro are affected: Omni…
Eufy Omni C20, Omni X10 Pro
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to run system level commands or execute arbitrary code. The following versions of Eufy Omni C20, Omni X10 Pro are affected: Omni…
Botslab G980H Dashcams
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to bypass authentication controls, gain unauthorized access to sensitive data and privileged device functionality, modify device…
Siemens Mendix Runtime (Update A)
View CSAF Summary This advisory is revoked. Re-investigation confirmed the reported behavior is expected platform configuration and does not expose the protected attribute. The following versions of Siemens Mendix…
Island Raises $400 Million at $6.4 Billion Valuation
The enterprise security firm has raised more than $1 billion since its launch in 2020; Evolution Equity Partners led the latest funding round.
There's a new way to break RSA that's faster than anything we've seen before
The world has known for decades that the RSA cryptosystem ’s days are numbered. Once quantum computing becomes practical (estimates for that range from 3 to 20 or more years), the foundational security it provides will…

Microsoft Rebuilds the SOC with AI Agents, SIEM Integration and Machine-Speed Defense
Cyberattacks can move faster than a security team can investigate them. Attackers increasingly use AI agents to automate steps that once needed several people, while defenders still work across separate monitoring and…
Malicious npm Packages That Evade Defenses
This is an impressive piece of malware . Its sophistication says nation-state to me, but there is no direct evidence and certainly no attribution.
Update Chrome: 108 security fixes for desktop, new release for Android
Over the last few days, Google issued several different Chrome updates. On September 22, Google released a Stable Channel Update for Desktop . This is the most important one for desktop users. It brings Chrome to…