Cybersecurity news & advisories


ShinyHunters claims FBI hack: 'This is NOT financially motivated'
ShinyHunters claims it hacked the FBI and stole more than 2 TB of employee data - and this time it’s personal. The gang wants the Feds to correct the record on how it operates. “This is NOT financially motivated,” a…
Reducing shadow IT visibility gaps with Wazuh
Shadow IT can leave security teams unaware of unmanaged endpoints, unauthorized software, and other assets that fall outside existing monitoring. Wazuh explains how endpoint inventory, agentless monitoring, and…
Amid Ongoing Rogue Incidents, Debate Over AI Safety Gets Real
As more reports of misalignment incidents underscore AI risks, large AI labs, regular businesses, and even nations are searching for better ways to keep control and be secure.
‘We Hacked the FBI:’ Hackers Say They Have Data on All FBI Employees
A high profile hacking group claims it has breached multiple FBI-related services and stolen data “on all FBI employees and applicants.” A representative of the group, called ShinyHunters, told 404 Media the data…
NightmareEclipse's latest zero-day leaves Microsoft Defender stuck in the past
Serial Microsoft zero-day leaker NightmareEclipse has found another way to mess with Windows Defender, this time by stopping the antivirus from updating itself. The security researcher, also known as Abdelhamid Naceri…
Meta Tests Muse AI Agent Calls That Are Actually Made By Humans in a Call Center
Last week, Meta executives announced that its much-hyped AI agent, Muse, had a new feature: It could call businesses for you to do things like make a restaurant reservation or a haircut appointment. But in reality, Meta…
Check Point warns of Management Server zero-day exploited in attacks
Check Point Software released emergency hotfixes to address a critical Security Management Server vulnerability that could let attackers run arbitrary scripts.
Z.ai says sorry for slurping up your code, open sources ZCode
Chinese AI giant Z.ai has apologized after developers caught it pulling a Grok, packaging up and uploading user workspaces to cloud storage. In a case that’s highly reminiscent of the issues over which Elon Musk’s xAI…

Autonomous AI Agents Hack Retailers for $25 and Steal 600,000 Credit Cards
A financially motivated operator has been running three open-source AI tools against many online retailers, mostly without supervision. The results are shocking: over 600,000 credit card records have been stolen…
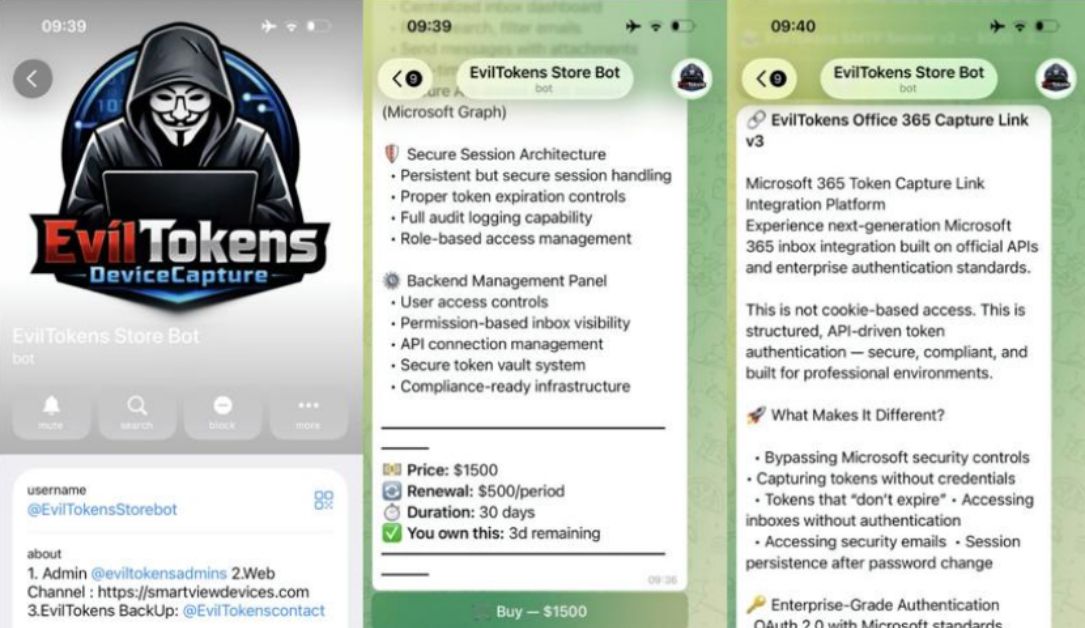
Two arrested in UK after Microsoft takedown of ‘Eviltokens’ AI-chatbot for cybercriminals
Available on Telegram for a $1,500 initiation fee and a recurring monthly $500 subscription, EvilTokens provided cybercriminals with artificial intelligence tools enabling them to compromise accounts, analyze breached…
CAIRN – A New Tool to Track AI Malware That Operates Without Human Control
Cisco Talos has released CAIRN, an open-source toolkit designed to hunt, classify, and track AI-integrated malware by examining the digital markers developers leave behind. The Cognitive Artifact Intelligence Research…
Citing China, President Trump doubles down on hands-off approach to AI regulation
By Derek B. Johnson President Donald Trump continued to defend his administration’s hands-off approach to AI regulation in the wake of hacks carried out by U.S. commercial frontier models that have rattled policymakers…
Some cheap smart glasses are a security disaster
Apart from the privacy concerns around smart glasses , researchers have found that some cheap brands come with barely any security at all. ABC Australia reports that researchers from NSB Cyber and Abstract Shield tested…
EvilTokens PhaaS disrupted after compromising 12,000 Microsoft accounts
The EvilTokens platform that compromised more than 12,000 Microsoft accounts at over 10,000 organizations has been disrupted in an effort led by Microsoft's Digital Crimes Unit (DCU).
Unmasking EvilTokens: Getting to the root of device code phishing
Following its emergence in February 2026, EvilTokens quickly became one of the most widely used phishing-as-a-service (PhaaS) platforms, providing cybercriminals with AI capabilities for tailoring phishing lures and…
Microsoft and partners disrupt EvilTokens, a comprehensive cybercrime service for financial fraud
Microsoft, along with a group of industry partners, disrupted EvilTokens, a short-lived but highly consequential cybercrime platform that investigators linked to more than 12,000 compromised Microsoft customer email…
UK cops arrest 2 EvilTokens suspects, Microsoft seizes 50 phishing kit websites
A coalition of law enforcement and private-sector tech companies led by Microsoft have disrupted the EvilTokens phishing service, arresting suspected website admins, taking down more than 50 websites, and notifying…
Who signed off on that AI agent? Nobody? Thought so
If you were in any doubt that AI agents are capable of complex autonomous work, that skepticism should have faded this summer. In July, news emerged that an autonomous swarm of OpenAI agents running in a sandbox broke…
The Truth about GET and HTTP Standards, (Tue, Sep 22nd)
On Friday, Xavier talked about the newly introduced HTTP Query method. This new method was introduced to allow "GET" requests that include a body. The main reason for this was that GET requests typically do not contain…
Cyera Raises $400 Million at $12+ Billion Valuation
The data security company received the new investment from Goldman Sachs Alternatives, extending its Series G funding round.
North Korean Attackers Hit 30,000 Devices and Steal $10.7m
WaterPlum compromised 30,000 devices and took funds or credentials from 7000 crypto wallets
LOW - Now Available
After 8 years, LOW is finally here. A story about the weight of being and the wreckage of waking up. Five episodes. Five descents. LOW is an audio journey into the unlit corners of human experience. Choices we made in…

Microsoft SharePoint Flaw Lets Attackers Execute Code Remotely With Low Privileges
Microsoft has confirmed a high-severity remote code execution vulnerability in on-premises SharePoint Server that lets an authenticated, low-privileged attacker run arbitrary code over a network without user…
New TASK#STOMP Backdoor Uses PowerShell to Steal Documents and Wi-Fi Passwords
TASK#STOMP is a newly analyzed Windows backdoor that turns ordinary built-in tools into a durable spying operation. It uses a Visual Basic Script installer, hidden PowerShell, scheduled tasks, and runtime code…
Linux KVM/arm64 Vulnerability Lets Attackers Escape Virtual Machines and Gain Host Access
A newly disclosed Linux kernel vulnerability, tracked as CVE-2026-89775, could let attackers escape an ARM64 virtual machine and access the underlying host system. The issue affects KVM/arm64 environments where nested…
Nightmare Eclipse Drops New Microsoft Defender Exploit After Revealing Identity
Abdelhamid Naceri, a former Microsoft Germany employee, is the exploit leaker Nightmare Eclipse, aka Chaotic Eclipse.
LausivLoader analysis, or how to pass data between malware stages, (Thu, Sep 17th)
At the end of August, a malspam message was caught in the quarantine of a mail gateway operated by one of my customers. The message was not especially remarkable – it asked the recipient to review some attached…
AI is set to help cyber attackers much more than defenders, says UK official
Dave Chismon, the NCSC’s chief technology officer for architecture, said in a blog post that the imbalance in AI means cyberattacks would likely grow as automated defenses struggle to keep pace.
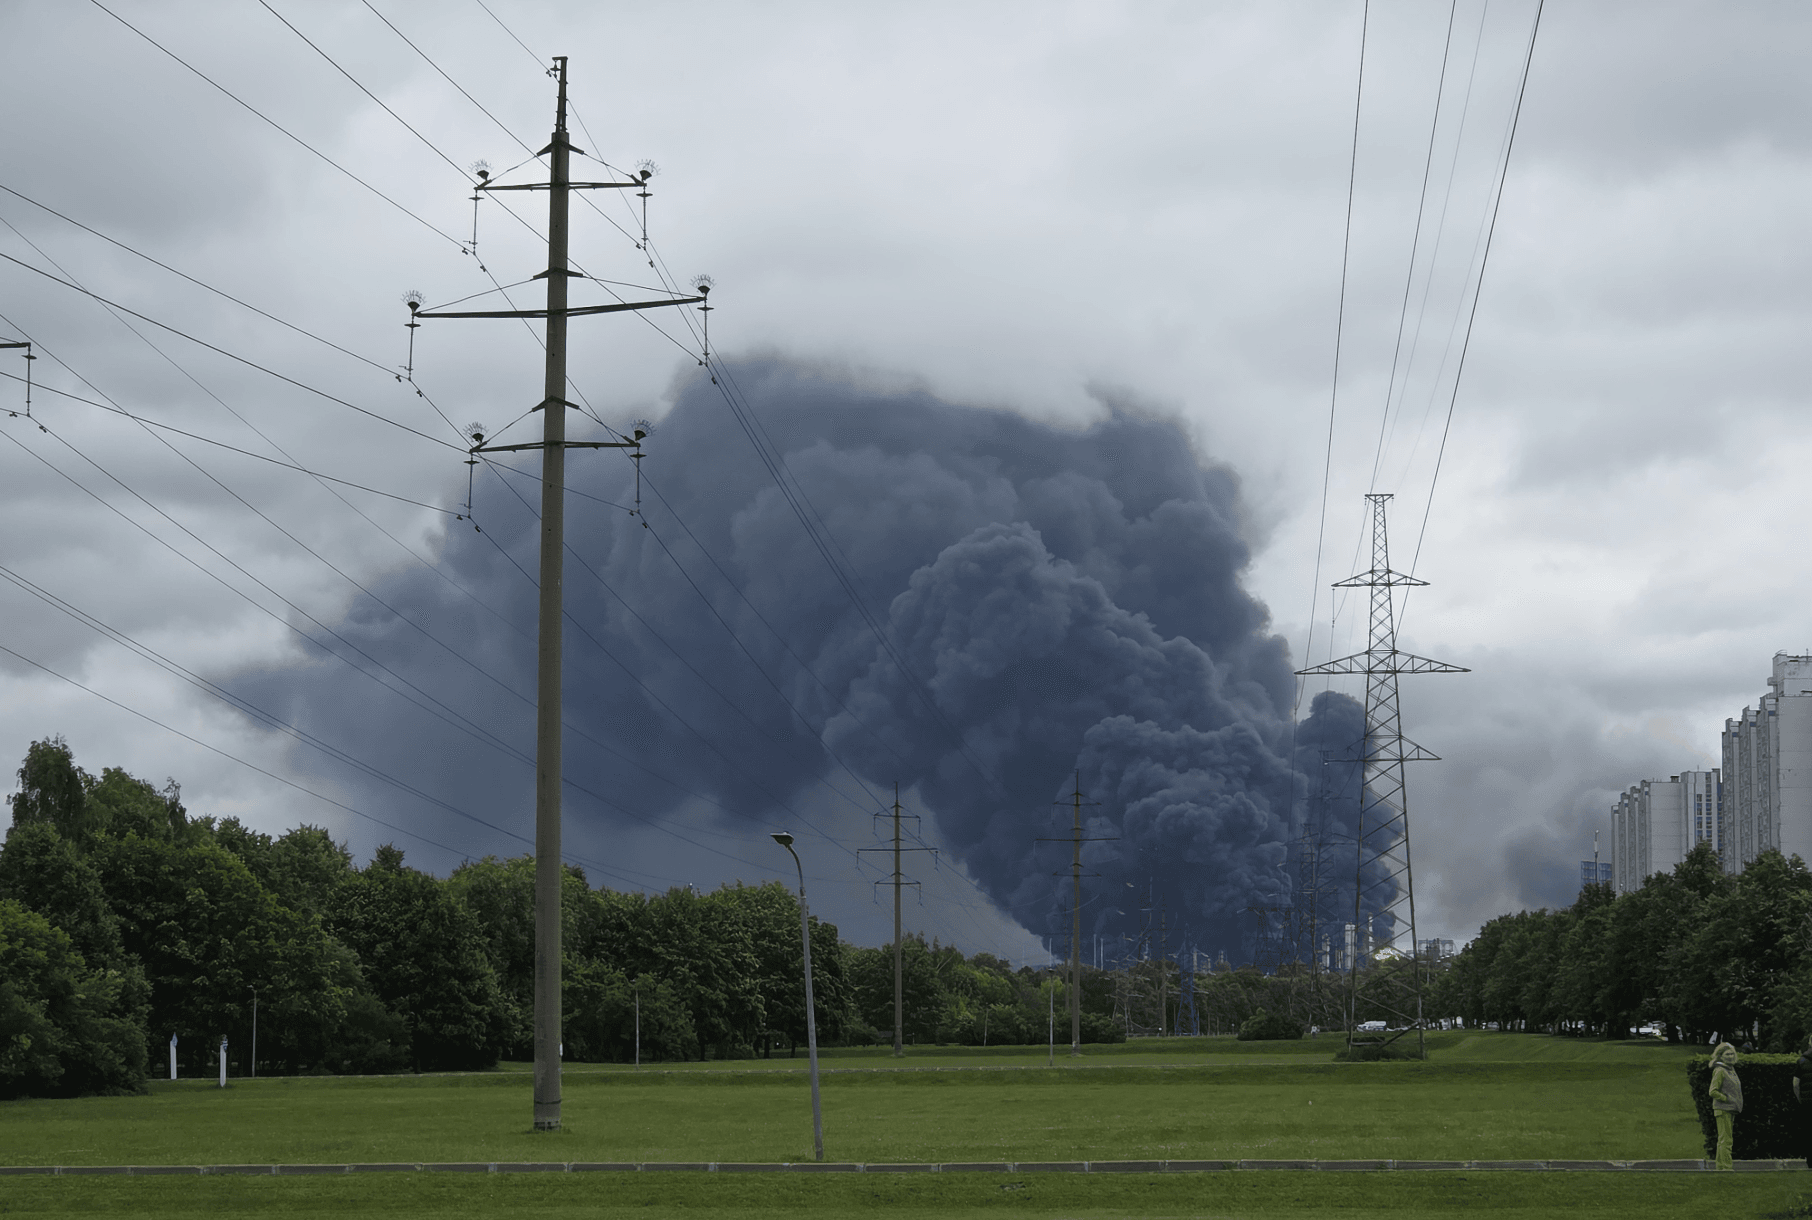
Russia's internet shutdowns disrupt warnings about incoming drone attacks
Russia’s growing restrictions on mobile internet and cellular service are making it harder for people to receive warnings about incoming Ukrainian drone and missile attacks.
AI Incident Response Readiness Lags Behind AI Adoption, ISACA Finds
A new report by ISACA found that 71% of orgs have not run AI incident response exercises as teams face rising pressure
People Training OpenAI’s AI Fired for Using AI to Train the AI
OpenAI has an army of contractors who read real ChatGPT users’ prompts and other data to help improve the chatbot’s responses. The idea is that the contractors provide an, obviously, human touch to OpenAI’s models…

Veeam Agent Flaw Actively Exploited to Gain SYSTEM Privileges on Windows
A critical local privilege escalation flaw in Veeam Agent for Microsoft Windows is drawing attention after public proof-of-concept exploit code became available. The vulnerability, tracked as CVE-2026-32996 , could let…

Red Hat OpenShift Flaw Lets Attackers Bypass PGP Checks and Push Malicious Releases
Red Hat has disclosed an Important security vulnerability in the OpenShift oc-mirror tool that could allow attackers to bypass PGP signature verification and introduce malicious release images into disconnected…
D-Link warns of max severity zero-day bug in DIR-822A routers
D-Link warned customers of a maximum-severity vulnerability (CVE-2026-86296) with public proof-of-concept (PoC) exploit code and no patch, affecting legacy DIR-822A dual-band Wi-Fi routers.
AI Agents Are Rewriting the Rules of Lateral Movement
Security teams have spent decades asking whether an identity has too much access. AI agents raise a harder question: how can we determine which paths an autonomous system can discover, given the access it already has? A…

BambooToken Linux Backdoor Uses MQTT C2 to Execute Shell Commands and Exfiltrate Files
BambooToken is a Linux backdoor that turns a lightweight messaging protocol into a remote control channel. The newly analysed sample can collect information about a host, run shell commands, and move files between a…

New CVSS 10.0 VeloCloud Orchestrator Flaw Actively Exploited in Certificate-Based Setups
Attackers are exploiting a new flaw in on-premises VeloCloud Orchestrator (VCO), the server that manages the Edge devices in a VeloCloud SD-WAN, Arista said on September 22. The flaw, tracked as CVE-2026-93952, may…
Only 13% of OT Network Segments Are Fully Isolated: Analysis
Forescout’s new network segmentation research shows that OT and medical devices often share network segments with other enterprise assets.
Growing the WIN AI Ecosystem with Agent Integrations
WINning AI with AI: How the Wiz MCP for WIN partners accelerates a connected ecosystem
Siemens Industrial Edge Management
View CSAF Summary Industrial Edge Management contains an authentication bypass vulnerability that could allow an unauthenticated remote attacker to perform full account takeover by resetting user credentials without…
OpenPLC Runtime v3
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to hijack session cookies and issue state-changing requests as an operator which would allow the attacker to control the…
lwIP (Lightweight IP)
View CSAF Summary Successful exploitation of this vulnerability could result in a system crash, a DoS, or memory corruption, which could lead to code execution on the victim system. The following versions of lwIP…
Siemens WTV676 and WTV776
View CSAF Summary The products listed below contain a denial of service vulnerability that could allow an attacker to force the devices into protection mode under certain conditions. This disables remote connectivity…
Siemens SIPLUS and SIMATIC Products
View CSAF Summary Multiple Siemens products are vulnerable to the "Copy Fail" vulnerability. Siemens has released new versions for several affected products and recommends to update to the latest versions. Siemens is…
Siemens Desigo CC family
View CSAF Summary A Client Code Execution (CCE) vulnerability has been identified in Desigo CC, potentially allowing malicious actors to execute arbitrary code on client devices through specially crafted graphics…
Siemens SIMOVE Fleetmanager and SIPLANT
View CSAF Summary SIMOVE Fleetmanager and SIPLANT contain a path traversal vulnerability that could allow an attacker to access files outside of intended scope. Siemens has released new versions for the affected…
Siemens Siveillance Control
View CSAF Summary A vulnerability has been identified in the Open Interface Services (OIS) web module affecting Siveillance Control and Siveillance Control Pro (versions OIS 3.x.y and OIS 4.x.y) . This vulnerability…
lwIP TCP/IP Stack MQTT Client Application
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to gain full code execution on the device. The following versions of lwIP TCP/IP Stack MQTT Client Application are affected: MQTT…
OpenPLC Runtime v3
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to hijack session cookies and issue state-changing requests as an operator which would allow the attacker to control the…
Siemens WTV676 and WTV776
View CSAF Summary The products listed below contain a denial of service vulnerability that could allow an attacker to force the devices into protection mode under certain conditions. This disables remote connectivity…
Siemens SIMOVE Fleetmanager and SIPLANT
View CSAF Summary SIMOVE Fleetmanager and SIPLANT contain a path traversal vulnerability that could allow an attacker to access files outside of intended scope. Siemens has released new versions for the affected…
Siemens Industrial Edge Management
View CSAF Summary Industrial Edge Management contains an authentication bypass vulnerability that could allow an unauthenticated remote attacker to perform full account takeover by resetting user credentials without…
Siemens Desigo CC family
View CSAF Summary A Client Code Execution (CCE) vulnerability has been identified in Desigo CC, potentially allowing malicious actors to execute arbitrary code on client devices through specially crafted graphics…
Siemens SIPLUS and SIMATIC Products
View CSAF Summary Multiple Siemens products are vulnerable to the "Copy Fail" vulnerability. Siemens has released new versions for several affected products and recommends to update to the latest versions. Siemens is…
Siemens Siveillance Control
View CSAF Summary A vulnerability has been identified in the Open Interface Services (OIS) web module affecting Siveillance Control and Siveillance Control Pro (versions OIS 3.x.y and OIS 4.x.y) . This vulnerability…
lwIP (Lightweight IP)
View CSAF Summary Successful exploitation of this vulnerability could result in a system crash, a DoS, or memory corruption, which could lead to code execution on the victim system. The following versions of lwIP…
lwIP TCP/IP Stack MQTT Client Application
View CSAF Summary Successful exploitation of this vulnerability could allow an attacker to gain full code execution on the device. The following versions of lwIP TCP/IP Stack MQTT Client Application are affected: MQTT…
More Than a Third of Industrial Orgs See Cybersecurity Risk as a Top Obstacle to Growth, Study Finds
Industrial companies are increasing cybersecurity investment as connected operations, AI adoption, and IT/OT convergence expand operational risk.
Network Segmentation Failures Are Expanding the Corporate Attack Surface
Forescout warns that incomplete network segmentation is widening the potential blast radius of attacks
Recent ZyXEL Switch Vulnerability Exploited by Chinese Hackers
A Chinese threat actor has exploited the bug to exfiltrate sensitive information from nearly 1,000 ZyXEL switches.