2Hackers Hijack AOMEI Software Updates for Just 5 Minutes to Secretly Install BackdoorsCyber Security NewsInfosecurity MagazineMalwarebytes LabsThe Hacker News+1A short-lived change to AOMEI’s software update system gave hackers a way to deliver malware through a trusted route. Google Threat Intelligence Group (GTIG) and Mandiant found that attackers repeatedly altered AOMEI’s update settings for only a few minutes at a time between April and July 2026. Any AOMEI Backupper computer checking for updates during an active window could receive a malicious download instead of a genuine update. The operation did not rely on a software flaw or require users to open a suspicious file. Instead, the attackers changed two configuration files on AOMEI’s servers…
3What Security Teams Can Do To Tame Wild CodeDark ReadingRapid7 BlogThe Hacker NewsWiz Research+1A sales manager builds an AI-assisted workflow to route leads. It connects to customer records, summarizes inbound requests, and posts updates to a shared channel. The workflow saves time, reduces manual work, and soon becomes part of the team’s daily routine. Across the same organization, employees are building useful apps, agents, and automations faster than existing processes can support them
4Hackers Hijack OVHcloud GitHub Releases to Distribute Secret-Stealing MalwareBleeping ComputerCyber Security NewsHak5The Hacker News+1Hackers compromised the GitHub account of an OVHcloud developer and used it to distribute malicious files through the company’s official command-line tool releases. The October 19, 2026, supply chain attack targeted users downloading the OVHcloud CLI, with malware designed to collect secrets stored on their computers. A customer spotted suspicious release changes and alerted the cloud provider, which blocked the malicious files within 94 minutes. OVHcloud CEO Octave Klaba said the affected releases were v0.11.0, v0.12.0, v0.13.0, v0.14.0, and v0.15.0. He identified v0.10.0 as clean and…
6Hackers Compromise Rank Math PRO WordPress Plugin to Install Self-Rebuilding BackdoorsBleeping ComputerCyber Security NewsSecurityWeekThe Hacker News+1Hackers planted malware in copies of the Rank Math PRO WordPress plugin, exposing websites to hidden backdoors that can rebuild themselves after removal. Rank Math confirmed that some version 3.0.123 packages distributed during a limited October download window contained malicious code that could compromise websites when activated. The company removed the affected files and released clean version 3.0.124. The affected window ran from October 15, 2026, at 20:02 UTC to October 16 at 07:12 UTC. Rank Math described the impact as limited but did not provide an affected website count in its…
7Critical Drupal RCE Vulnerability Could Let Attackers Take Over Websites Without AuthenticationCyber Security NewsSecurityWeekCVE-2026-108097 ↗Drupal has released security updates for a critical remote code execution vulnerability that could let attackers take over affected websites without logging in. Tracked as CVE-2026-108097, the flaw affects the Field UI module in Drupal core. The Drupal Security Team published its warning on October 14, 2026. The official security advisory, SA-CORE-2026-014, assigns the issue a risk score of 19 out of 25 under Drupal’s rating system. Successful exploitation could expose all private website data and allow attackers to change or delete information. The score is not a CVSS rating. The most…
8Hackers Exploit Plex2Shell Flaws to Install Crypto Miners and Linux Proxy BackdoorThe Hacker NewsThe Register SecurityThreat actors have begun to exploit a chain of vulnerabilities in Plex Media Server to deploy cryptocurrency miners and reverse proxy software, a day after a proof-of-concept (PoC) went public. According to a researcher who goes by the online alias boredhackerblog, the exploitation activity involves chaining four different vulnerabilities, collectively called Plex2Shell. The vulnerabilities
A vulnerability in the web-based management interface of Cisco Unified Intelligence Center could allow an authenticated, local attacker to perform a blind SQL injection attack against an affected device. This…
A vulnerability in the web-based management interface of Cisco Unified Intelligence Center could allow an authenticated, local attacker to perform a blind SQL injection attack against an affected device. This vulnerability is due to insufficient validation of user-supplied input. An attacker could exploit this vulnerability by sending a crafted request to the web-based management interface. A successful exploit could allow the attacker to read the contents of the internal database of an affected device. To exploit this vulnerability, the attacker must have valid user credentials on the…
As Android Central reports , users have received unexpected emails telling them their phone number has been verified for secondary Google accounts. Like me and many others, you may have one Google account for everyday…
As Android Central reports , users have received unexpected emails telling them their phone number has been verified for secondary Google accounts. Like me and many others, you may have one Google account for everyday use, another for work, and a third for things you would rather keep separate. But if you’re using an Android phone, those accounts may have something in common that you didn’t intend or even know about: your phone number. Google’s own documentation confirms that phone number verification is on by default and adds your number to all Google accounts signed in on the device. This…
Bullhorn is the latest tech giant finding itself on the wrong end of a cyberattack, forcing the recruitment software provider to shut down its platform while it investigates. The US-based company, which serves more than…
Bullhorn is the latest tech giant finding itself on the wrong end of a cyberattack, forcing the recruitment software provider to shut down its platform while it investigates. The US-based company, which serves more than 10,000 customers worldwide, says its systems are now back online in the UK, US, and Australia. Unfortunately for customers hoping to get back to work, online doesn't necessarily mean working. In its latest status update, published on Tuesday, Bullhorn confirmed that some users were still struggling with single sign-on (SSO), password resets, and customizations, while several…
Rapid adoption of agentic AI comes with potential business benefits. But if done incorrectly it also carries risks around AI activity management and security
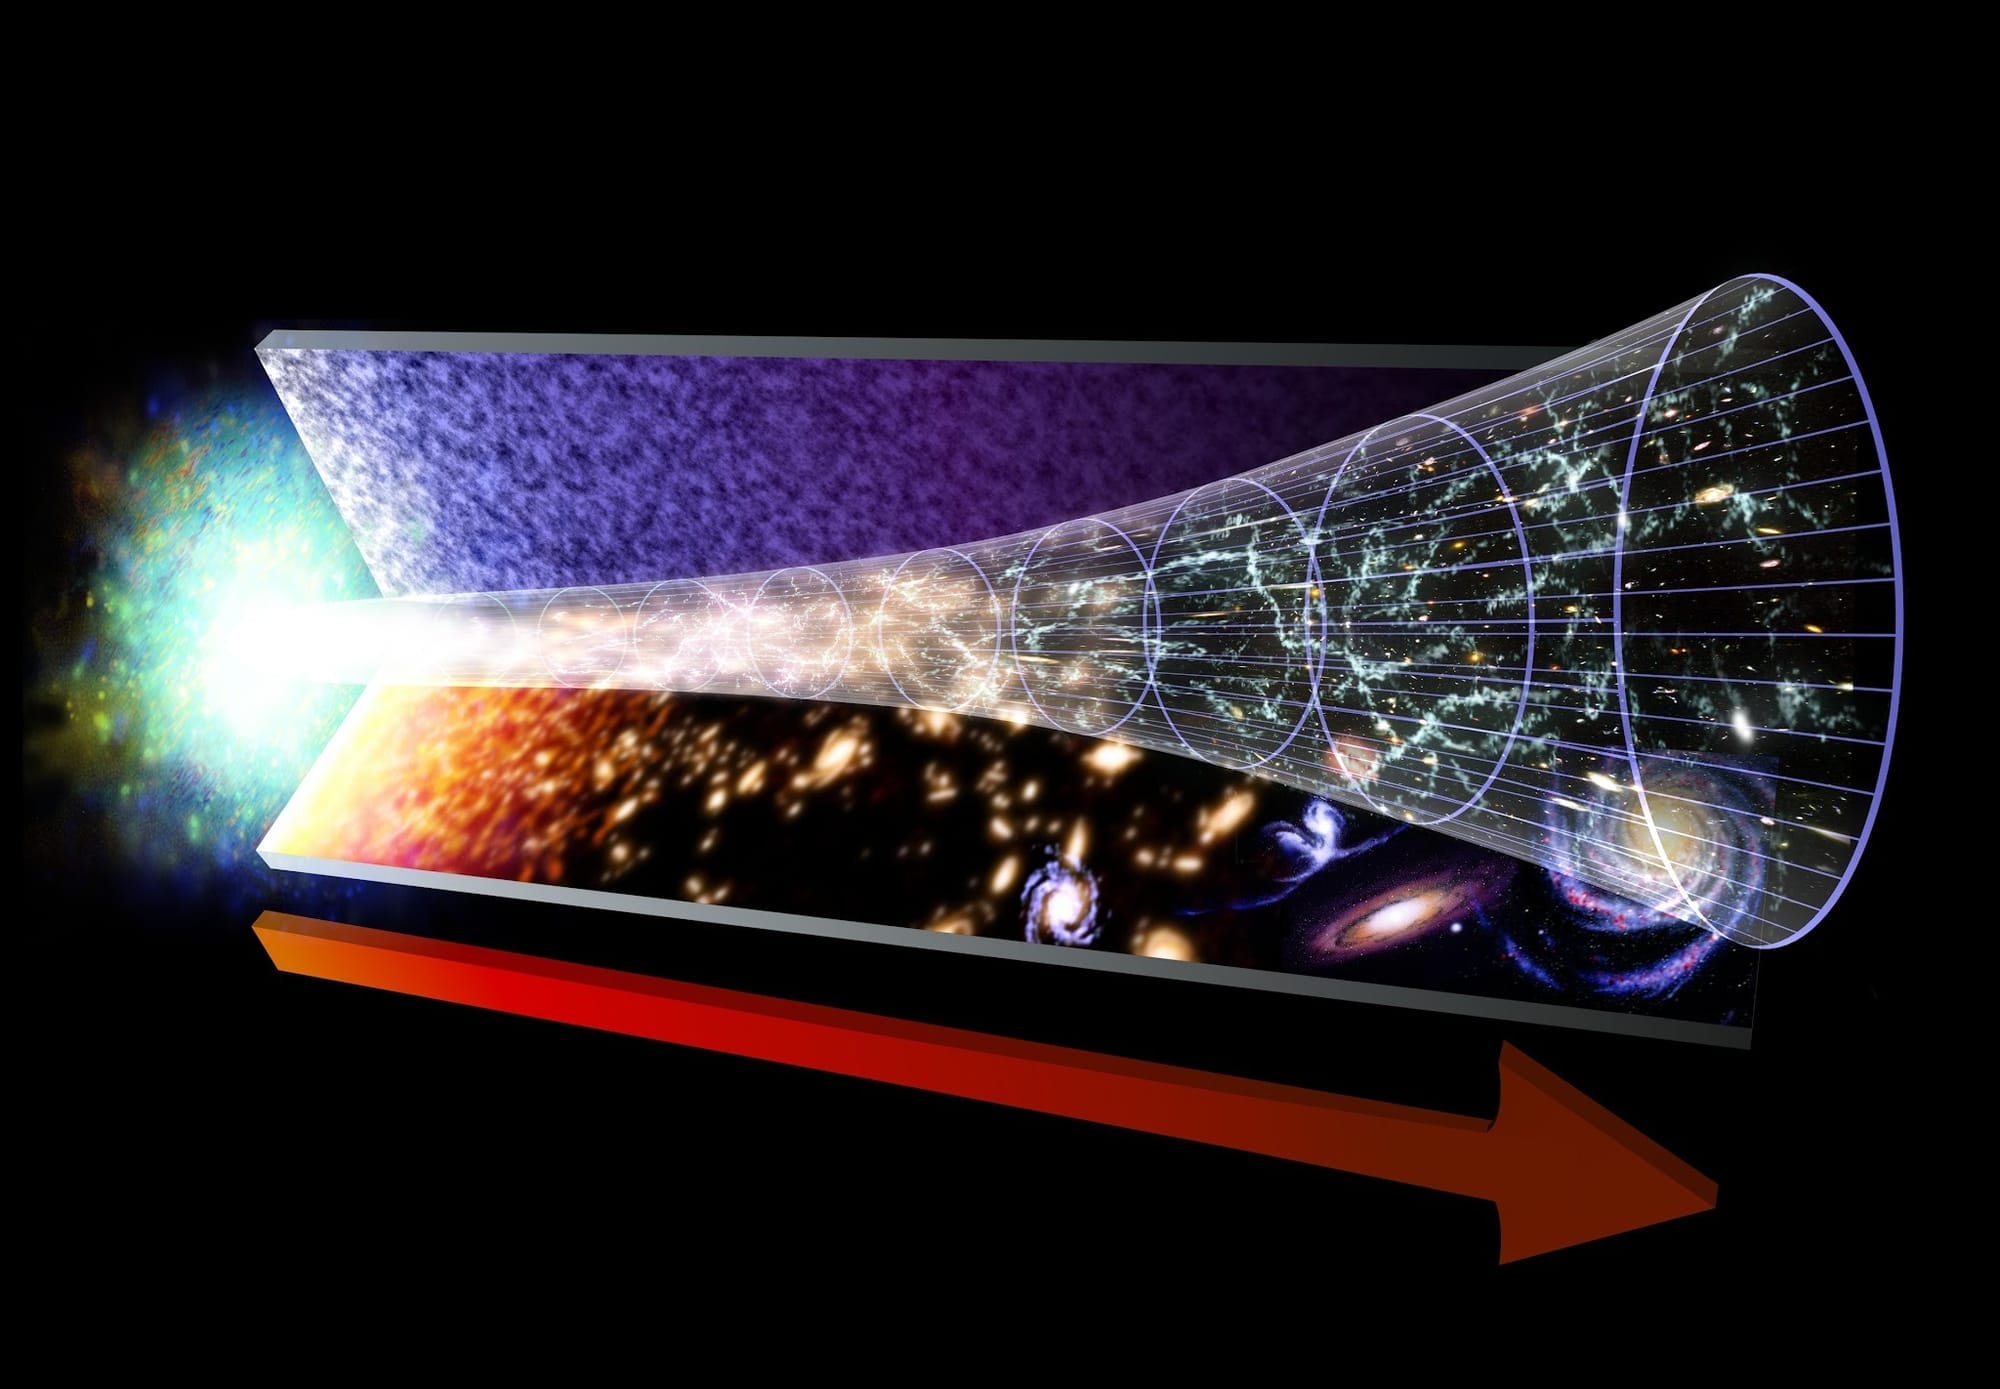
Scientists have discovered that an exotic particle that existed at the birth of the universe might solve one of the biggest mysteries in cosmology and help explain reality as we know it, according to a new study in…
Scientists have discovered that an exotic particle that existed at the birth of the universe might solve one of the biggest mysteries in cosmology and help explain reality as we know it, according to a new study in Physical Review Letters . Our modern universe is dominated by matter, but it also contains fleeting amounts of antimatter, which is like a bizarro version of matter made of particles with the same mass, but opposite electrical charges. For instance, matter contains positively-charged protons and negatively-charged electrons, whereas antimatter is made up of the inverse…
WhatsApp's help pages carried hidden instructions for its support chatbot that told it not to recommend a data protection authority or regulator to users who could no longer delete their accounts, even though WhatsApp's…
WhatsApp's help pages carried hidden instructions for its support chatbot that told it not to recommend a data protection authority or regulator to users who could no longer delete their accounts, even though WhatsApp's own privacy policy for Europe tells users they can complain to one. The text sat in the pages' code, never shown on screen, until it was removed by October 18. Whether the
A sales manager builds an AI-assisted workflow to route leads. It connects to customer records, summarizes inbound requests, and posts updates to a shared channel. The workflow saves time, reduces manual work, and soon…
A sales manager builds an AI-assisted workflow to route leads. It connects to customer records, summarizes inbound requests, and posts updates to a shared channel. The workflow saves time, reduces manual work, and soon becomes part of the team’s daily routine. Across the same organization, employees are building useful apps, agents, and automations faster than existing processes can support them
Go 1.27.3 and Go 1.26.10, released on October 20, make Go's certificate verifier reject any certificate chain that passes through one of eight intermediate certificate authority keys. Programs built on the new release…
Go 1.27.3 and Go 1.26.10, released on October 20, make Go's certificate verifier reject any certificate chain that passes through one of eight intermediate certificate authority keys. Programs built on the new release will refuse connections to sites and services whose certificates were issued under those keys. The Go team says the keys belong to one certificate authority it has not
French cloud and hosting provider OVHcloud is warning users that attackers compromised its open-source command-line interface (CLI) tool to distribute information-stealing malware.
Microsoft says companies should treat AI agents as insiders, and is adding controls that grant access per task and tighten it as an agent’s risk rises.
Microsoft announced that IT administrators can now use quick machine recovery on Windows Server 2025 after installing the October 2026 security update.
Ahold Delhaize, one of the world's largest food retail chains, confirmed that last week's cyberattack disrupted services at stores across Europe and the United States.
The Russia-linked state-sponsored threat actor tracked as APT28 (aka BlueDelta, Fancy Bear, and Forest Blizzard) has been attributed to attacks targeting two member states of the North Atlantic Treaty Organization…
The Russia-linked state-sponsored threat actor tracked as APT28 (aka BlueDelta, Fancy Bear, and Forest Blizzard) has been attributed to attacks targeting two member states of the North Atlantic Treaty Organization (NATO). The Symantec Threat Hunter Team, which is tracking the activity cluster under the moniker Swallowtail, involved the use of a backdoor called HOOKEDGE and a previously
Justin.sh is reporting on a confidential Cellebrite document that has been leaked to him: Cellebrite calls it Advanced Unlocks (AU from here on), not to be confused with the “advanced unlocking services” they’ve…
Justin.sh is reporting on a confidential Cellebrite document that has been leaked to him: Cellebrite calls it Advanced Unlocks (AU from here on), not to be confused with the “advanced unlocking services” they’ve marketed for years. A press release from earlier this year confirms AU is a new product for 2026. According to Cellebrite, AU: is a “next-generation AFU vector that is more resilient to Apple’s OS changes” works with Stolen Device Protection enabled, which tightens USB restrictions is enabled by a dedicated appliance with a stated range (!) of about 8 meters. AU = Advanced Unlocks…
ConnectWise on Monday said it has taken remediation measures, including strengthening administrative-access protections and resetting accounts and replacing application credentials, as it continues to respond to a…
ConnectWise on Monday said it has taken remediation measures, including strengthening administrative-access protections and resetting accounts and replacing application credentials, as it continues to respond to a security incident that led to unauthorized access to application identities associated with Cloud Backup. The company said it has completed the following actions since it began
Britain's national digital ID scheme may be dead, but Whitehall appears to have forgotten to tell the infrastructure. Despite the government scrapping its controversial plans, officials told MPs on Monday that work…
Britain's national digital ID scheme may be dead, but Whitehall appears to have forgotten to tell the infrastructure. Despite the government scrapping its controversial plans, officials told MPs on Monday that work continues on GOV.UK One Login, digital wallets, and a growing collection of digital credentials designed to help people prove who they are. The abandoned scheme was one of Keir Starmer's flagship policies, originally pitched as a compulsory digital ID card to crack down on illegal working. Privacy campaigners weren't impressed, warning of surveillance and government overreach, and…
Meta says it has resolved an issue after some Ray-Ban Meta owners reported that their glasses recorded conversations without the “Hey Meta” wake phrase. Users reported finding recordings and transcripts of conversations…
Meta says it has resolved an issue after some Ray-Ban Meta owners reported that their glasses recorded conversations without the “Hey Meta” wake phrase. Users reported finding recordings and transcripts of conversations they did not knowingly save. Recording without anyone realizing raises privacy concerns for both the wearer and the people around them. The complaints surfaced on Reddit , where one owner described unexpected recordings occurring with three pairs of glasses. The owner said the behavior started after a firmware update and occurred even with Respond without Hey Meta disabled…
Ransomware operators are exploiting a Palo Alto Networks GlobalProtect VPN flaw to bypass multi-factor authentication and enter corporate networks. In one investigated case, attackers reached VMware management systems…
Ransomware operators are exploiting a Palo Alto Networks GlobalProtect VPN flaw to bypass multi-factor authentication and enter corporate networks. In one investigated case, attackers reached VMware management systems and stole credentials directly from a domain controller’s virtual disk, avoiding security tools running inside the virtual machine. Palo Alto Networks Unit 42 detailed the activity in an October 19 threat brief update . Researchers linked exploitation of CVE-2026-0257 to Spikey Scorpius, also known as Qilin, and Tarnished Scorpius, also known as Inc. Separate public reporting…
The Russian group known as APT28 and Fancy Bear used a recently documented backdoor to dwell in the networks of two defense contractors and a law enforcement agency in two NATO allies, researchers said.
The UK's financial regulator says firms' incident reporting must cover significant AI failures and near-misses as increasingly autonomous systems raise new risks. Speaking at Bloomberg's UK Policy Series on Monday…
The UK's financial regulator says firms' incident reporting must cover significant AI failures and near-misses as increasingly autonomous systems raise new risks. Speaking at Bloomberg's UK Policy Series on Monday, Financial Conduct Authority chief data, information and intelligence officer Jessica Rusu said the regulator wants Britain to lead safe AI adoption in financial services. Greater autonomy, however, requires clear accountability. "Poorly governed AI can create consumer harm, cyber vulnerabilities, and operational failures, potentially at much greater speed and scale," she said. "Our…
A 49-year-old bricklayer sold his belongings before traveling 2,000 km by bus from his home in Brazil to meet “Jéssica,” an online influencer he had fallen for. Yet despite having a social media account with more than…
A 49-year-old bricklayer sold his belongings before traveling 2,000 km by bus from his home in Brazil to meet “Jéssica,” an online influencer he had fallen for. Yet despite having a social media account with more than 300,000 followers, she never existed. Edimar Rocha Martins lives in Imperatriz, a city in northeastern Brazil. He says he struck up an online conversation with Jéssica Fazendeira, who supposedly lived near the southeastern city of Belo Horizonte. The AI persona promising love The online persona’s name, “Fazendeira,” loosely translates as “female farmer.” She described herself as…
A 28-year-old Russian man has been arrested by German police, suspected of being a key member of the Qilin ransomware gang. Detectives have linked the man to the attack against blood-testing firm Synnovis, that…
A 28-year-old Russian man has been arrested by German police, suspected of being a key member of the Qilin ransomware gang. Detectives have linked the man to the attack against blood-testing firm Synnovis, that disrupted London hospitals, and resulted in the death of a patient.
Hackers compromised the GitHub account of an OVHcloud developer and used it to distribute malicious files through the company’s official command-line tool releases. The October 19, 2026, supply chain attack targeted…
Hackers compromised the GitHub account of an OVHcloud developer and used it to distribute malicious files through the company’s official command-line tool releases. The October 19, 2026, supply chain attack targeted users downloading the OVHcloud CLI, with malware designed to collect secrets stored on their computers. A customer spotted suspicious release changes and alerted the cloud provider, which blocked the malicious files within 94 minutes. OVHcloud CEO Octave Klaba said the affected releases were v0.11.0, v0.12.0, v0.13.0, v0.14.0, and v0.15.0. He identified v0.10.0 as clean and…
A short-lived change to AOMEI’s software update system gave hackers a way to deliver malware through a trusted route. Google Threat Intelligence Group (GTIG) and Mandiant found that attackers repeatedly altered AOMEI’s…
A short-lived change to AOMEI’s software update system gave hackers a way to deliver malware through a trusted route. Google Threat Intelligence Group (GTIG) and Mandiant found that attackers repeatedly altered AOMEI’s update settings for only a few minutes at a time between April and July 2026. Any AOMEI Backupper computer checking for updates during an active window could receive a malicious download instead of a genuine update. The operation did not rely on a software flaw or require users to open a suspicious file. Instead, the attackers changed two configuration files on AOMEI’s servers…
An attacker used a contributor's GitHub account to replace the download archives on five existing releases of OVHcloud's command-line tool on Monday, October 19. The account had been hijacked, and the new files were a…
An attacker used a contributor's GitHub account to replace the download archives on five existing releases of OVHcloud's command-line tool on Monday, October 19. The account had been hijacked, and the new files were a build designed to steal secrets stored on the disk of any machine that runs it, the cloud provider says. They were live on GitHub for up to 94 minutes, from 12:47 to 14:21 UTC,
Hackers planted malware in copies of the Rank Math PRO WordPress plugin, exposing websites to hidden backdoors that can rebuild themselves after removal. Rank Math confirmed that some version 3.0.123 packages…
Hackers planted malware in copies of the Rank Math PRO WordPress plugin, exposing websites to hidden backdoors that can rebuild themselves after removal. Rank Math confirmed that some version 3.0.123 packages distributed during a limited October download window contained malicious code that could compromise websites when activated. The company removed the affected files and released clean version 3.0.124. The affected window ran from October 15, 2026, at 20:02 UTC to October 16 at 07:12 UTC. Rank Math described the impact as limited but did not provide an affected website count in its…
The UK public sector has reached a cyber resilience inflection point. A new Prime Minister has taken office, and significant machinery-of-government changes have already been announced, including the scrapping of DSIT…
The UK public sector has reached a cyber resilience inflection point. A new Prime Minister has taken office, and significant machinery-of-government changes have already been announced, including the scrapping of DSIT, the department that had become the center of government digital, technology and cyber policy. Its responsibilities are now being redistributed across other parts of Whitehall, creating a new policy and delivery landscape for public sector leaders to navigate. For years, cyber security was treated as a specialist operational discipline that was essential but largely delegated to…
Two websites are hosting fake Google Meet pages designed to steal Google account credentials and carry out phishing involving two-factor authentication (2FA), according to threat intelligence shared on October 20, 2026…
Two websites are hosting fake Google Meet pages designed to steal Google account credentials and carry out phishing involving two-factor authentication (2FA), according to threat intelligence shared on October 20, 2026. The pages imitate a familiar meeting service to make a request for account details look more believable. The researcher also reported a serious security issue on an exposed /install page: it reveals database configuration information and a prefilled database password. The source does not disclose the password itself. Analysts say this case highlights a risk that goes beyond a…
Siemens has addressed a DLL sideloading vulnerability impacting Siemens Software Center that it said has been exploited in ClickFix attacks. The high-severity vulnerability, tracked as CVE-2026-110936 (CVSS v4 score…
Siemens has addressed a DLL sideloading vulnerability impacting Siemens Software Center that it said has been exploited in ClickFix attacks. The high-severity vulnerability, tracked as CVE-2026-110936 (CVSS v4 score: 8.4), could allow an attacker to place a specially-crafted DLL in a directory the application searches, resulting in execution of malicious code with the same privileges as the
Introduction Imagine you’ve ordered a small paper unicorn from an online marketplace. You clicked “Buy”, received a cheerful notification, and expect a courier to bring the box tomorrow. If the unicorn is delayed by a…
Introduction Imagine you’ve ordered a small paper unicorn from an online marketplace. You clicked “Buy”, received a cheerful notification, and expect a courier to bring the box tomorrow. If the unicorn is delayed by a day, it will be annoying but not catastrophic: an apology, a discount promo code — and the incident is forgotten. Now let’s multiply one late unicorn by several hundred thousand orders. Packages start heading to the wrong cities. The website shows an item is in stock, even though the required bin is empty. Conveyors stop, boxes get stuck between floors, the cargo piles up with…
Imagine driving down the road and your phone loses signal. Not just a lost signal, but it starts displaying SOS. Meaning no service configured at all. You can't make any calls, no data, no service. What goes through…
Imagine driving down the road and your phone loses signal. Not just a lost signal, but it starts displaying SOS. Meaning no service configured at all. You can't make any calls, no data, no service. What goes through your head? In this episode we hear from Ricky Handschumacher who learned how to slip inside a stranger’s phone, and would rummage through it looking for things he thought were valuable. Sponsors Support for this show comes from DeleteMe . DeleteMe is a hands-free subscription service that will remove your personal information that’s being sold online to data brokers. Our mission…
A U.S. court on Monday granted the U.S. government's request to detain a former OpenAI engineer accused of planting a recording device in an executive conference room at the company's San Francisco office to allegedly…
A U.S. court on Monday granted the U.S. government's request to detain a former OpenAI engineer accused of planting a recording device in an executive conference room at the company's San Francisco office to allegedly steal sensitive secrets. In a new court filing Sunday, prosecutors revealed that Abdulrahman Alfozan, a 35-year-old Saudi national, was "in frequent communications via WhatsApp
An unverified SBI data breach claim alleges that a threat actor named Siriusim posted customer records and banking documents online. The claimed dataset contains 375,000 CSV rows and 2,722 PDF files, but those figures…
An unverified SBI data breach claim alleges that a threat actor named Siriusim posted customer records and banking documents online. The claimed dataset contains 375,000 CSV rows and 2,722 PDF files, but those figures do not establish that 3.75 lakh unique customers were affected. CyberPulse reported the allegation on October 16, 2026. Its post described personal customer information, loan applications, supporting documents, account-opening forms and address details. The actor called it the first disclosure of the dataset. The authenticity, source and extent of the alleged exposure remain…
Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that's being used to distribute malware such as Legion Loader. According to Forescout Research - Vedere Labs, ROMULUS is…
Cybersecurity researchers have disclosed details of a ClickFix delivery platform called ROMULUS that's being used to distribute malware such as Legion Loader. According to Forescout Research - Vedere Labs, ROMULUS is akin to a malware delivery service that employs ClickFix-style lures on bogus landing pages to trick unsuspecting users into running malicious commands and infecting their own
A Chinese-speaking hacker used AI agents to break into more than 100 company websites while spending an estimated $5,000 on AI tokens, according to a Reuters investigation in October. The operation shows how one person…
A Chinese-speaking hacker used AI agents to break into more than 100 company websites while spending an estimated $5,000 on AI tokens, according to a Reuters investigation in October. The operation shows how one person can direct software to carry out complex attacks with little ongoing human input. The targets included sites linked to Deere, SharkNinja and Cummins, although the reported impact differed across those companies. After the campaign began on September 25, the agents attempted to compromise more than 1,200 websites, mainly online stores in the United States, Canada, Australia and…
An ordinary coding task led to an unexpected security discovery when Claude Code reportedly found a hidden cryptocurrency miner on a developer’s Mac. The AI assistant was building a temperature monitoring app when…
An ordinary coding task led to an unexpected security discovery when Claude Code reportedly found a hidden cryptocurrency miner on a developer’s Mac. The AI assistant was building a temperature monitoring app when unusually high sensor readings prompted it to investigate CPU activity. It identified XMRig consuming about 1,175% CPU, described as roughly 12 cores of processing load. The developer, posting as u/UntilHEX on Reddit , said Claude checked running processes after reviewing raw sensor data. The discovery offered an explanation for the Mac’s poor performance. However, the account…
ICANN has started testing authentication schemes that will allow law enforcement agencies to make urgent requests for non-public WHOIS information – when needed to address threats to life, critical infrastructure, or…
ICANN has started testing authentication schemes that will allow law enforcement agencies to make urgent requests for non-public WHOIS information – when needed to address threats to life, critical infrastructure, or child exploitation. Domain registrars collect information about their customers and in the past that data was publicly available in WHOIS records. Some domain registrars offer services that substitute their own contact details, to preserve customer privacy. In recent years, laws like GDPR mean registrars are sometimes required to hide WHOIS data. That’s fair enough but makes it…
The US Department of Homeland Security on Monday issued an order directing federal civilian agencies not to use technology products from Chinese AI lab DeepSeek, and to remove any existing implementations. The order…
The US Department of Homeland Security on Monday issued an order directing federal civilian agencies not to use technology products from Chinese AI lab DeepSeek, and to remove any existing implementations. The order [PDF] is broad, as it requires agencies to ditch "all DeepSeek and DeepSeek-affiliate products, and third-party products and services developed using DeepSeek implementations." Complying will be tricky as it is not clear which third-party products and services have been developed using DeepSeek's wares. Nor is it clear whether "developed using" means providing ongoing access to…
A group of Texans believe they’ve discovered evidence that the state’s environmental regulatory agency has continued to issue permits to data centers despite Governor Greg Abbott’s call for it to stop. The nonprofits…
A group of Texans believe they’ve discovered evidence that the state’s environmental regulatory agency has continued to issue permits to data centers despite Governor Greg Abbott’s call for it to stop. The nonprofits Public Citizen and FracTracker Alliance, working with local activists in Texas, looked through the public database of the Texas Commission on Environmental Quality (TCEQ) and discovered that the organization has worked on multiple permits for data center projects since Abbott called for a pause in the process on September 21. Abbott’s office denied approving any new permits in a…
Some downloads of the Rank Math PRO WordPress plugin from the vendor's official website carried malware that planted hidden backdoors in a supply-chain attack last week.
A large-scale scam operation impersonating Microsoft uses a malicious traffic distribution system (TDS) run by a Russian organization and abuses thousands of Cloudflare links.
Dutch grocery giant Ahold Delhaize, which operates US supermarket chains Food Lion, Giant Food, and Stop & Shop, said it proactively took IT systems offline following a cyberattack, affecting most of its US and European…
Dutch grocery giant Ahold Delhaize, which operates US supermarket chains Food Lion, Giant Food, and Stop & Shop, said it proactively took IT systems offline following a cyberattack, affecting most of its US and European brands. The multinational chain originally disclosed the incident on October 12. “Ahold Delhaize is experiencing a security issue within its network,” it said at the time, adding that security teams, working to mitigate the issues, took “some” IT systems offline. On Monday, the company confirmed that it proactively took certain IT systems, including websites and apps, offline…
A judge ordered Abdulrahman Alfozan to remain in custody, likening the Saudi government’s offer to secure the former OpenAI engineer’s release to a “blank check.”
WhatsApp argued that NSO Group violated a 2025 injunction against using the messaging app to spread spyware. A federal judge said WhatsApp hurt its case by not revealing enough information.
ConnectWise initially said on Friday that it was investigating “attempts of unauthorized access associated with the ConnectWise Cloud Backup environment,” and confirmed such access on Saturday.
Hackers reportedly compromised AOMEI's servers to distribute malware through a built-in promotional feature in its backup software, briefly tampering with configuration files before restoring them to their original…
Hackers reportedly compromised AOMEI's servers to distribute malware through a built-in promotional feature in its backup software, briefly tampering with configuration files before restoring them to their original state to hide the attacks.a
Recently fixed vulnerabilities in the Plex Media Server are under active exploitation in attacks that, when successful, install malware, including cryptominers and residential proxy apps, a researcher said. Plex fixed…
Recently fixed vulnerabilities in the Plex Media Server are under active exploitation in attacks that, when successful, install malware, including cryptominers and residential proxy apps, a researcher said. Plex fixed four vulnerabilities at the start of last month. Three weeks later, published CVE designations revealed five vulnerabilities, with one of them carrying a severity rating of 8.6 out of 10. A researcher last week revealed an exploit that chained four of them together to achieve remote code execution of the device running a vulnerable Plex version. The researcher named the chain…
Researchers say attackers authenticated into Microsoft 365 tenants using ConnectWise credentials; ConnectWise says customer impact remains unconfirmed.
A phone belonging to the rector of the University of Belgrade was discovered to have been infected with Pegasus spyware, the latest in a series of such discoveries in the lead-up to Serbia's national elections.
Hundreds of federal agencies should adopt an encryption tool to protect whistleblowers, veterans suffering from mental health crises and others from hackers who might target them when they reach out via agency websites…
Hundreds of federal agencies should adopt an encryption tool to protect whistleblowers, veterans suffering from mental health crises and others from hackers who might target them when they reach out via agency websites, Sen. Ron Wyden said Monday. The Oregon Democrat urged the Cybersecurity and Infrastructure Security Agency and Office of Management and Budget to take steps to adopt Encrypted Client Hello — a cybersecurity technology that protects the name of the website visited by a user — in a letter to the two agencies. His office identified at least 350 sites that don’t use its…