Cybersecurity news & advisories





Autonomous AI Attacks: The Hugging Face Reality Check
For several years the forecast has been constant: AI lowers the skill barrier, AI writes novel malware, AI will soon run attacks end to end with minimal human direction. It is worth noticing where that forecast mostly…

When Ransomware Targets AI Models: Defending the AI/ML Recovery Chain
By Crystal Morin Ransomware crews have always followed the money. For years, that meant targets like banks and hospitals organizations with high-value assets and sensitive data who couldn’t afford downtime. Now, it…

Claude Opus 5 Helped Researchers Take Over OpenAI Staff Accounts via Chained Flaws
Three researchers at the security firm Hacktron used Anthropic's Claude Opus 5 to chain two flaws and take over the ChatGPT and Codex accounts of several OpenAI employees, then reach an internal OpenAI code repository…
CISA Warns of Linux Kernel Vulnerabilities Actively Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has warned that attackers are actively exploiting three Linux kernel vulnerabilities, creating an urgent patching and investigation deadline. CISA added…
BragJack attacks hijack AI browser agents through malicious extensions
BragJack, a proof-of-concept attack from Forever Security's Gal Weizman, hijacks the AI assistants in Chrome, Edge, Opera Neon, Perplexity Comet, and Claude in Chrome using one malicious extension. The Prompt Forcing…
TigerByte Cyber Emerges From Stealth With $3 Million in Funding
The company has secured over $7 million in contracts with US government agencies, including the US Space Force, the US Navy, and DARPA.
Agentic security is the billion-dollar challenge for some clever startup to solve
When it comes to AI models, security functions as an afterthought, as evidenced by increased instances of agents hacking organizations and people, and other security mishaps with agents gone rogue. There's also an…
North Korean WaterPlum hackers infected 30,000 devices worldwide
A joint law enforcement advisory warns that the North Korean hacking group WaterPlum compromised at least 30,000 devices worldwide from December 2025 through July 2026 and transferred more than $10.7 million in stolen…
ShinyHunters hacks Clop leak site, threatens to extort ransomware gang
The ShinyHunters extortion gang breached the Clop (aka Cl0p) ransomware operation's data leak site, defacing the Tor site and allegedly stealing server data and the private keys for its onion service.

Can You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This Webinar
A new CVE drops. Your scanner finds it. The severity score looks ugly. But that still does not answer the question that matters: Can it actually be exploited in your environment? Mythos-class AI is compressing the time…

Identity Visibility in 2026: The Foundation of Identity Security
Identity visibility is a starting point for modern identity security, because stolen and misused credentials are among the most frequently reported initial access vectors in breach research, including Verizon's annual…
Viral AI actress' hotline face-scans every caller, watches their mood
AI actress Tilly Norwood went viral after glitching into Chinese on Piers Morgan Uncensored last night. Her "Talking Tilly" video call service face-scans every caller for an 18+ age check, senses callers' moods during…
TanStack Supply Chain Attack Lets Hackers Steal 170 Private CrowdSec GitHub Repositories
CrowdSec has disclosed that attackers copied about 170 private GitHub repositories after a former employee’s account was compromised through May’s TanStack npm supply chain attack. The May 22 theft remained undetected…

Forget the AI Slowdown—the Vulnerability Explosion Is Already Happening
AI labs are toying with an industry-wide pact to slow development. Meanwhile, widely available AI chatbots are already helping uncover a tidal wave of security flaws.

‘Supermountains’ Buried Under Antarctica Fueled Explosion of Life, Scientists Discover
Welcome back to the Abstract! These are the studies this week that ate well, moved mountains, grew brains, and saved medieval texts. First, scientists set out to understand why Venus doesn’t have a moon and discover…
SolarWinds Patches ARM Hard-Coded Key Flaw Enabling Unauthenticated RCE
SolarWinds has released security updates to address a high-severity flaw in Access Rights Manager (ARM) that, if successfully exploited, could lead to an unauthenticated remote code execution vulnerability. The…
Google Gemini AI Hacked 3 Real Companies during a Cybersecurity Test
Google has confirmed that its Gemini artificial intelligence model accessed protected systems belonging to three companies during a cybersecurity evaluation after a testing error exposed the agent to the public…
Critical Pre-Auth RCE in Orkes Conductor Workflow Platform Exploited in the Wild
A critical vulnerability impacting Orkes Conductor is being actively exploited in the wild, according to Fortinet. The vulnerability in question is CVE-2026-58138 (CVSS v3.1 score: 9.8/CVSS v4 score: 9.3), which relates…

Google Gemini Broke Into Real Company Systems After Security Test Domain Mix-Up
Google's Gemini model has become the latest artificial intelligence (AI) system to access the internet and break into other companies during a cybersecurity evaluation. The development was first reported by The Wall…

CrowdSec Says TanStack npm Attack Led to Copy of 170 Private GitHub Repositories
An attacker copied about 170 of CrowdSec's private GitHub repositories on May 22 using the account of an employee who had just left, CrowdSec said on September 18. The French security company had kept his GitHub access…

CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added three security flaws impacting the Linux kernel to its Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active…
HTTP QUERY Method: The Grey Zone Between GET And POST., (Fri, Sep 18th)
In June 2026 the IETF published RFC 10008[1], defining a new HTTP method: "QUERY". The HTTP protocol faced already by changes (HTTP/2, HTTP/3) but it’s the first new standard HTTP verb since "PATCH" in 2010!
Click2Shell WordPress Flaw Lets Attackers Gain RCE With a Single Malicious Link
WordPress administrators are being urged to update after researchers disclosed Click2Shell, an exploit chain that can turn one malicious link into remote code execution (RCE) on a vulnerable website. The issue begins…
BragJack Attack Lets Malicious Extensions Hijack AI Agents Across 5 Major Browsers
A new attack technique dubbed “BragJack” allows a malicious browser extension to seize trusted communication channels used by AI assistants in Chrome, Edge, Opera Neon, Comet, and Claude in Chrome. Rather than bypassing…
Friday Squid Blogging: On Squid Egg Sacs
Short essay about squid egg sacs. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog moderation policy.
Vectra AI Launches Ascent to Help Address New Era of AI-Driven Attacks
The new program expands Vectra AI's partner strategy as increasingly complex security environments and the growing use of AI create demand for broader AI expertise, services, and security outcomes.
Early Scattered Spider member pleads guilty to cybercrime spree
Another core member of the hacker subset of The Com involved in a spree of extortion attacks from at least 2021 to 2023 pleaded guilty to federal charges, according to court records released Tuesday. Ahmed Hossam Eldin…
Cisco Zero-Day Highlights API Endpoint Authentication Issues
The authentication bypass flaw CVE-2026-76460 impacts Cisco's Identity Services Engine (ISE) and received a maximum 10 out of 10 CVSS score.
EY Survey Finds Autonomous AI Implementation Outpaces Oversight
A new survey of senior AI execs shows that while organizations are rapidly deploying AI and autonomous systems, their process and controls are not keeping pace.
MFA Won't Save You From OAuth Consent Abuse
MFA is essential, but it cannot replace OAuth governance, least-privilege scopes, consent monitoring, and rapid revocation.

Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root
A security researcher has released working exploit code for four Linux kernel flaws that each let a local user gain root, the highest level of access on a machine. Kernel maintainers have fixed all four over the past…
Researchers use AI to find widespread software decoder flaw
Researchers said they used Anthropic’s Claude and OpenAI’s Codex to identify a damaging flaw embedded in a popular software decoding tool that could leave major internet platforms, enterprise services, and web…
Researchers used Claude to hack OpenAI employees' ChatGPT accounts
Talk about your competitor getting through the door. Security researchers used Anthropic's Claude to help hack into OpenAI employees’ ChatGPT accounts. A trio of bug hunters researching frontier AI labs’ security…

New WordPress Click2Shell Flaw Forces Theme Installs, Can Chain to Code Execution
WordPress today released patches to fix a new set of vulnerabilities in its core software, one of which could allow a crafted web link, opened by a logged-in administrator, to install a theme from the official…
North Korea's fake job interviews infected 30,000 devices
North Korea's employment scams work both ways. As well as placing fraudulent IT workers inside Western companies, regime-backed cybercriminals have posed as recruiters to infect more than 30,000 devices and steal over…
FBI: Fake cop and government impersonation scams cost victims $1.6B
Scammers impersonating law enforcement or government officials have cost victims more than $1.6 billion since January 2025, the FBI reports. The FBI’s Internet Crime Complaint Center (IC3) received close to 61,000…
Gyazo server flaw exploited to steal 23.6 million user records
The Gyazo image-sharing platform has confirmed it suffered a data breach after hackers exploited a server vulnerability that allowed them to steal 23.6 million user records.

An Undercover Google Analyst Infiltrated a Notorious Supply-Chain Hacking Gang
TeamPCP pulled off the worst-ever software supply-chain hacking spree and breached thousands of companies. Now Google’s threat intelligence group says it had a mole inside the hackers’ inner circle.
Cisco Secure Firewall Adaptive Security Appliance and Secure Firewall Threat Defense Software Logging Denial of Service Vulnerability
A vulnerability in the system rate-limiting process for syslog message 419002 of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Cisco Secure Firewall Threat Defense (FTD) Software could allow an…
Cisco Secure Firewall Adaptive Security Appliance, Secure Firewall Threat Defense, and Secure Firewall Management Center Software Hardening Release: September 2026
As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco Secure Firewall Adaptive Security Appliance (ASA) Software, Cisco Secure Firewall Threat Defense (FTD) Software and Cisco Secure…
Cisco Secure Firewall Adaptive Security Appliance and Secure Firewall Threat Defense Software for Secure Firewall 3100 and 4200 Series DTLS Denial of Service Vulnerability
A vulnerability in Datagram TLS (DTLS) message handling of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Cisco Secure Firewall Threat Defense (FTD) Software for Cisco Secure Firewall 3100 Series…
Cisco Secure Firewall Adaptive Security Appliance and Secure Firewall Threat Defense Software IKEv2 Certificate Authentication Denial of Service Vulnerability
A vulnerability in the certification authentication feature of Internet Key Exchange version 2 (IKEv2) for Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Cisco Secure Firewall Threat Defense (FTD)…
Cisco Secure Firewall Adaptive Security Appliance and Secure Firewall Threat Defense Software Object Group Access Control List Bypass Vulnerabilities
Multiple vulnerabilities in the access control list (ACL) Object Group Search (OGS) implementation of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Cisco Secure Firewall Threat Defense (FTD)…
Cisco Secure Firewall Adaptive Security Appliance and Secure Firewall Threat Defense Software TCP DNS Denial of Service Vulnerability
A vulnerability in the DNS over TCP implementation of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Cisco Secure Firewall Threat Defense (FTD) Software could allow an unauthenticated, remote…
Cisco Secure Firewall Adaptive Security Appliance and Secure Firewall Threat Defense Software EIGRP Denial of Service Vulnerability
A vulnerability in the EIGRP implementation in Cisco Secure Firewall Adaptive Security Appliance (ASA) Software and Cisco Secure Firewall Threat Defense (FTD) Software could allow an unauthenticated, adjacent attacker…
International security agencies warn about North Korean hackers exploiting job seekers to steal crypto, data
North Korean hackers are infiltrating tens of thousands of job seekers’ computer networks by posing as prospective employers, such as artificial intelligence firms, to steal sensitive information and millions of dollars…
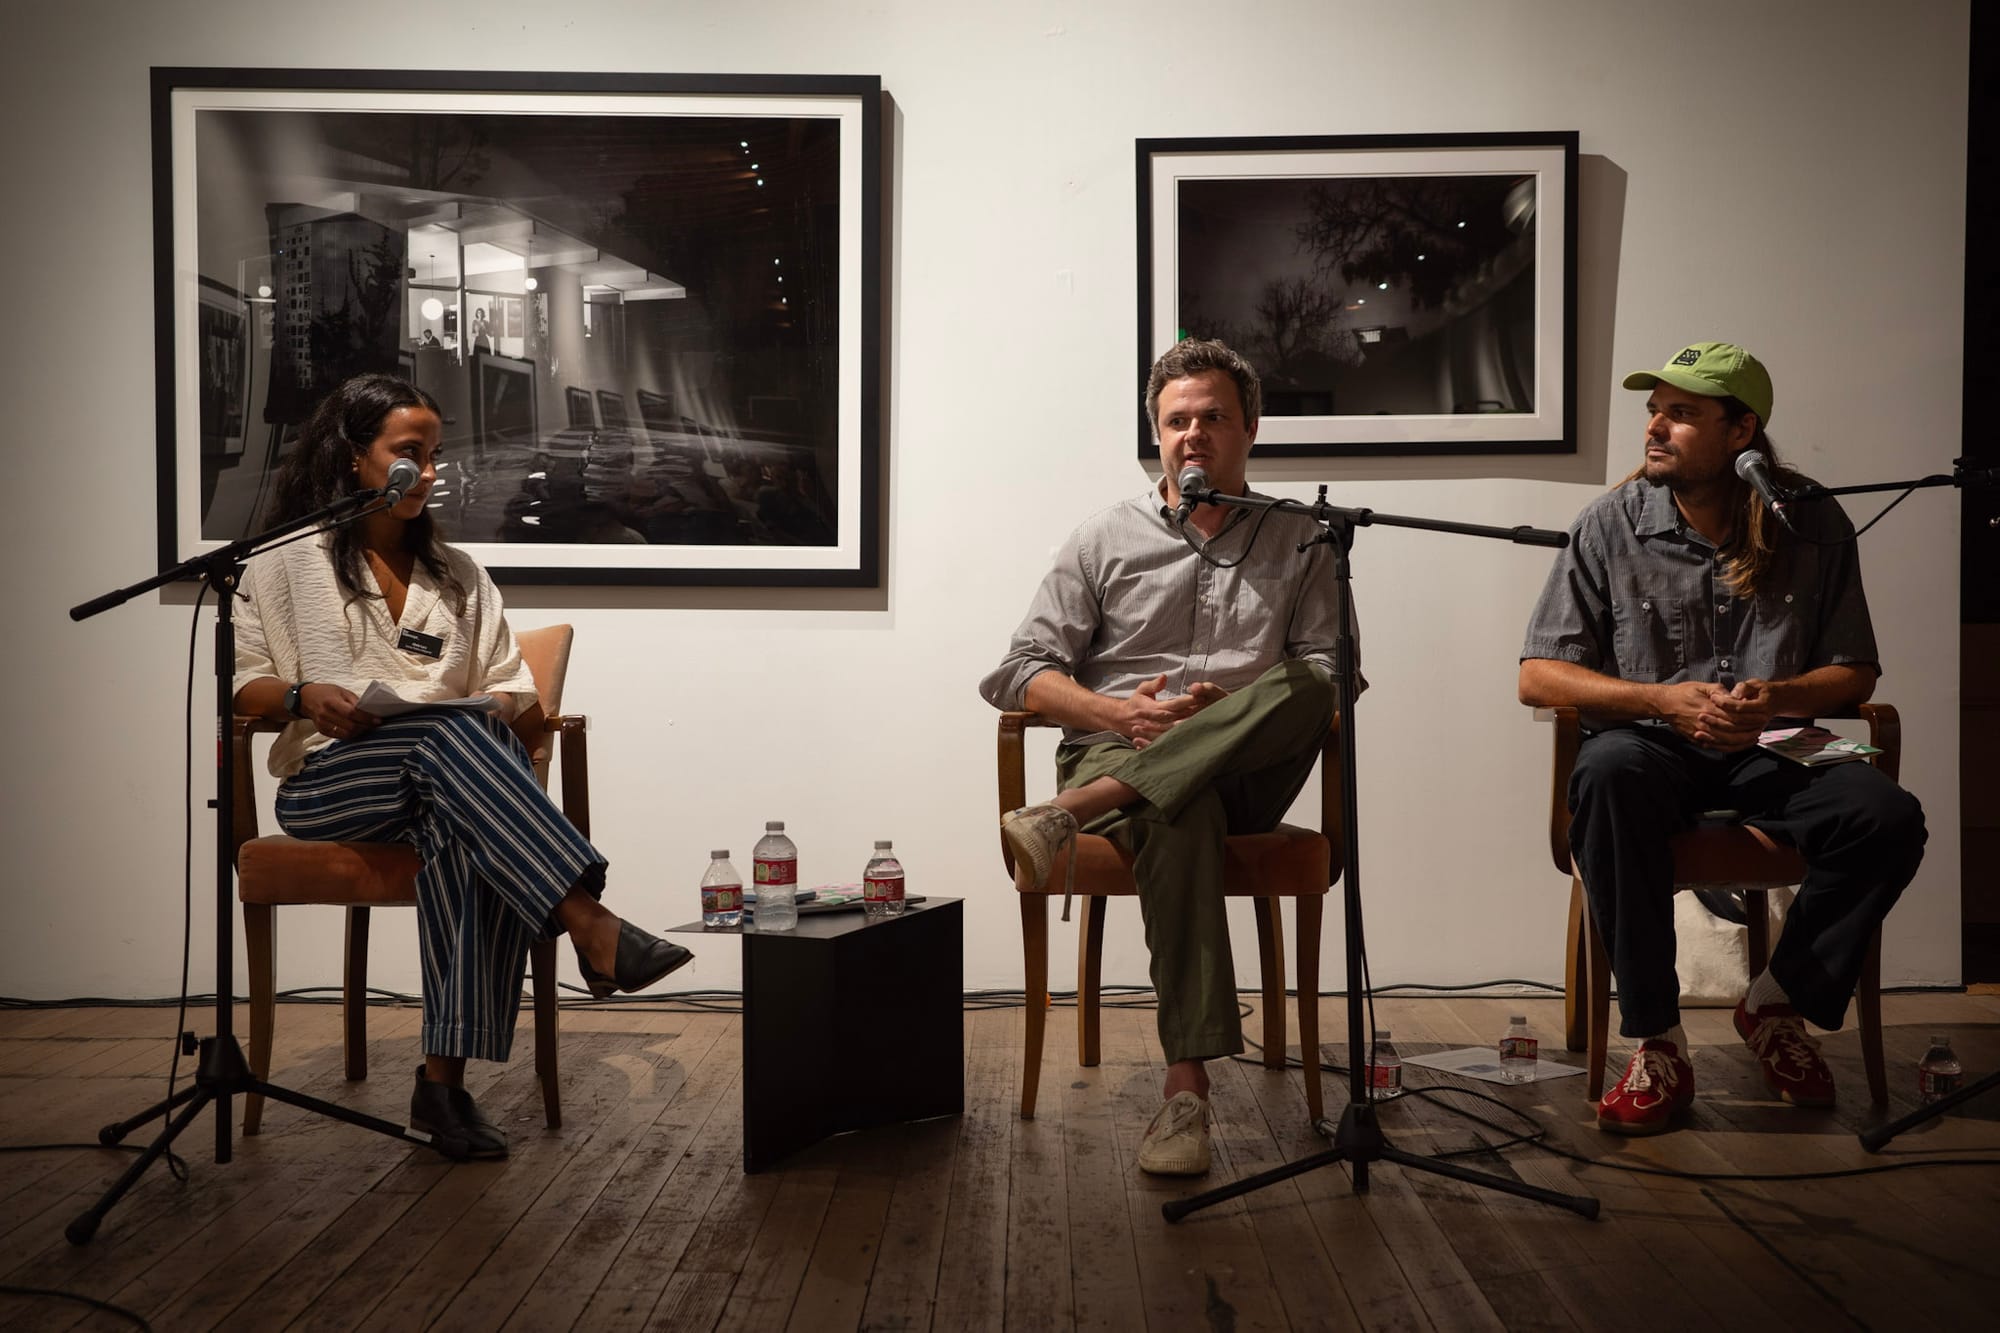
404 Media x The Intercept Live: How AI Is Used to Surveil and Kill
In this collaboration with our friends at The Intercept, 404 Media's Jason Koebler and the Intercept's Sam Biddle and Akela Lacy discuss the ways AI is already used to empower private surveillance companies that filter…
New Android malware uses AI to steal bank logins and PINs
Researchers at Zimperium’s zLabs have analyzed an Android Trojan that uses an automated, multi-stage infection process. What’s new is that RatHat gives a live AI assistant the keys to the accessibility tree of the…
Behind the Blog: Eating the Internet
This is Behind the Blog, where we share our behind-the-scenes thoughts about how a few of our top stories of the week came together. This week, we discuss just doing it, machines that eat the internet, and an…

Transparent Tribe Deploys New Rust Backdoor Using Private GitHub Repositories for C2
The Pakistan-aligned threat group tracked as Transparent Tribe (aka APT36 and Earth Karkaddan) has been attributed to a fresh set of cyber attacks targeting government and defense entities in India and Afghanistan. The…
Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer
An ongoing malware campaign uses SEO-optimized GitHub repositories to impersonate well-known software firms to push a previously undocumented information stealer called Rapuncel.
Nations take action on North Korean IT workers after UN report
A report published Wednesday said that as of July, Vietnam, Laos, Pakistan and Argentina took meaningful steps to respond to allegations involving North Korea listed in an October study.
In Other News: Ransomware Developer Sentenced, Plugin4Shell AI Attack, Critical SAP Flaw
Noteworthy stories that might have slipped under the radar: Mandiant's 2026 AI risk report, PhantomRaven malware used by bug bounty hunter, WordPress plugin bug exploited.
Did an AI really try to break free from human control?
Amid discussions about slowing down AI development, the Telegraph ran the headline: “OpenAI sounds alarm after bot tries to break free from human control.” That headline is slightly misleading, in my opinion. The…
Critical Microsoft Azure AI Foundry Vulnerability Allows Attackers to Escalate Privileges
Microsoft has patched a maximum-severity security flaw in Azure AI Foundry, its enterprise platform for building and managing generative AI applications and agents, that could have allowed an unauthenticated attacker to…
Secure enterprise sharing with access reviews for Microsoft 365
Microsoft 365 makes sharing files easy, but access can remain long after its original purpose has ended, leaving organizations with little visibility into who can still reach sensitive data. tenfold Software explains…