France Blood Service Cyber-Attack Sends Blood Storage Temperatures to 110°C
A supplier of the French National Blood Service was hit by a cyber-attack in which hackers turned cold rooms hosting blood samples up to 110°C (230°F)
Security Feed
500 articles 45 of 45 sources updated RSS ↗


A supplier of the French National Blood Service was hit by a cyber-attack in which hackers turned cold rooms hosting blood samples up to 110°C (230°F)
Hackers have been harvesting AI access tokens and have been using AI-assisted offensive tools to automate attacks.
A federal grand jury indicted two Canadian men for hijacking university supercomputers to secretly mine Electroneum cryptocurrency.
On November 3, Google issued Chrome 157 to the stable channel for Windows, Mac and Linux. The update is rolling out over the coming days and weeks. Most users are on Chrome’s Stable channel. The desktop update brings…
Last month, OpenAI CEO Sam Altman told Politico that “we believe that the world should accept some bad things happening for the benefits of this technology,” referring to ChatGPT users dying, people losing their jobs to…
The US Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies that attackers have started exploiting a recently patched high-severity WordPress vulnerability in the wild.
A critical flaw in Ruby on Rails could allow an unauthenticated attacker to write arbitrary files on an app's server by uploading a crafted file if the app processes uploads using ImageMagick. The Rails project…
Bitdefender highlighted a unique human-AI approach during a September attack on a UK school estate, which resulted in financial data being exfiltrated
A flaw in Zyxel GS1900 switches was already being used by hackers, and the patch meant to fix it did not work. Researchers at Binarly found that a public exploit hit a different bug than the one Zyxel had patched. Zyxel…
Attackers tampered with cold-storage settings used by France's civilian blood service after compromising a refrigeration supplier, the organization said. The French Blood Establishment (EFS) confirmed the incident on…
Two flaws in the Xen hypervisor allow a malicious guest virtual machine (VM) to read and write the memory of other VMs on the same host, including dom0. Dom0 is the VM that, by default, has full permissions and manages…
Microsoft Edge now automatically disables notifications from websites that send users to detected scam pages, cutting off a route used to deliver fake virus warnings. The protection connects Microsoft Defender…
Nearly every agent security pitch now ends on the same promise: the product stops the bad action in real time. The promise holds for one kind of agent, the kind whose traffic passes through a gateway the enterprise…
Google has released Chrome 157 for Windows, macOS, and Linux, fixing 213 security bugs, including seven rated critical. Announced on November 3, 2026, the update addresses flaws across graphics, memory handling, browser…
A China-aligned threat actor known as SlippyNunchucks has been attributed to a Domain Name System (DNS) hijacking operation abusing insecure HTTP communications in Windows versions of Sogou Input Method as part of a…
A Russian state-linked hacking group is using trusted websites to quietly break into phones. Researchers say APT29, also known as Midnight Blizzard or Cozy Bear, planted hidden code on real and cloned sites in the US…
Cloudflare has launched Zero Wire, a public vulnerability intelligence feed designed to help security teams track critical CVEs, understand exploitation activity, and find security fixes. Announced on November 3, 2026…
A German-led coalition of law enforcers has intensified efforts to strike at a €4m investment fraud scheme
Using compromised credentials, the attackers accessed OpsShield’s update servers and poisoned multiple cPGuard versions.
The browser update resolves dozens of memory safety bugs and incorrect/missing authorization issues.
Binance’s first incident report traces the record theft to a months-long campaign that compromised three engineers’ computers.
A new XLoader malware campaign is landing in inboxes as ordinary business orders and price quote requests. The emails look routine, but the attached archive holds a script that starts a chain of hidden steps. The chain…
Google has released its November 2026 Android security update, addressing more than 200 vulnerabilities across the operating system, kernel, and hardware components. Published on November 2, the bulletin includes…
A large-scale watering hole attack associated with Russian hackers has been targeting iOS and Android users visiting compromised sites or fake ones impersonating legitimate portals.
The number of organizations named on ransomware leak sites rose 30% in the third quarter of 2026. Researchers say that does not mean attacks rose by the same amount. Most of the growth came from new, unproven groups…
The U.S. Cybersecurity and Infrastructure Security Agency has warned that attackers are exploiting a WordPress Core vulnerability that can allow malicious code to run on website servers. CISA added the flaw to its Known…
Binance has revealed details of how North Korean hackers stole $6.4bn theft of crypto assets
In recent months, North Korea has accelerated its weapons tests in a likely bid to increase its leverage in potential diplomacy with the US.
A $300,000 award went to a pre-launch flaw that exposed conversations and tokens on internal Muse test VMs used by Meta staff.
Russian authorities have arrested three suspected members of a threat group known as VasyGrek and dismantled its criminal infrastructure. Also known as Fluffy Wolf, the threat actor has a history of targeting Russian…
Every SOC believes its controls work; BAS is the machine that checks. By safely running real attacker techniques against production defenses continuously, not annually these platforms convert “we should be covered” into…
A critical Android flaw could allow an attacker to run code on a phone without any user action remotely, Google said in its November security bulletin. The flaw, CVE-2026-58868, affects Android 14 through 17. Phones get…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a security flaw in WordPress Core to the Known Exploited Vulnerabilities (KEV) catalog, citing evidence of active exploitation. The…
On this week’s show Patrick Gray and James Wilson are joined by special guest co-host Ciaran Martin, former CEO of the UK’s National Cyber Security Centre (NCSC), to talk through the week’s cybersecurity news…
An unknown operator appears to have exfiltrated SQL Server backups from the Philippine Overseas Employment Administration in under a half hour.
Attackers have compromised the update infrastructure for the cPGuard web security suite to distribute a backdoor and a data-stealing script.
Beyond food storage, the same combination of Internet connectivity, remote access, and inadequate security practices can put temperature-controlled infrastructure across other critical sectors at risk.
North Korean cryptocurrency thieves tricked a Binance software engineer into downloading malware onto their work-issued computer during a fake job interview process before last week's record-breaking $6.3 billion heist…
German police led a multinational probe that exposed an alleged crime-as-a-service provider supplying fraudulent trading platforms to investment scammers.
A Delaware-based defense and aerospace company has settled a case with U.S. agencies over government allegations that the firm neglected its cybersecurity obligations in its contracts. ILC — the name the government uses…
Developer platform WorkOS suffered a data breach after a threat actor accessed business contact records and summaries of customer communications.
Cryptocurrency exchange Binance says North Korean hackers used a fake job interview to trick an employee into installing malware that ultimately let them compromise the company's wallet infrastructure and steal about…
The overwhelming majority of the infected devices in the X.CPE botnet are Android TV set-top boxes, Google said, adding that they observed a number of other infected Android-based IoT devices, including telehealth…
The Center for a New American Security posits that the next big threat from our future AI overlords involves "sovereign agents" acting on their own and regularly improving themselves. These are AI agents that operate…
Suspected North Korean attackers duped an engineer with a fake job interview and a malicious download to gain a foothold in the crypto firm’s system and steal billions, according to Binance.
An Oklahoma man has been charged with mailing suspicious white substances to election officials across the country. Robin Patrick Martin faces charges of conveying false or misleading information and hoaxes, as well as…
Large language model hijacking attacks, also known as LLMjacking, are generating large fraudulent cloud charges, with some organizations losing more than $100,000 per day.
Customers of the mSecure password manager are being urged to act now to protect the confidential information they store in it, possibly by changing passwords, resetting two-factor authentication (2FA), and removing…
Members of Germany's political elite were among the spyware targets in 99 countries that Apple personally warned recently.
Blockchain infrastructure provider Chainstack on Tuesday disclosed that it was targeted in a cyber attack that allowed an unauthorized party to gain access to some parts of its infrastructure. The incident is assessed…
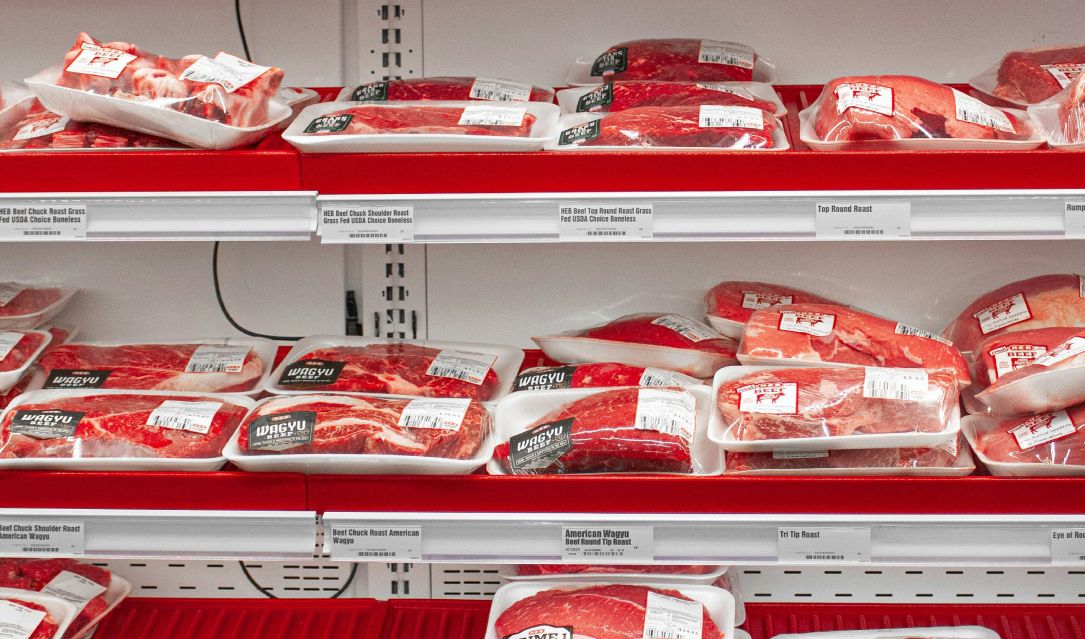
Supermarket and grocery store refrigerator controls across Europe were hacked in the early hours of Monday in the second such wave of attacks in recent weeks — following a first wave in France — with unidentified…
Microsoft Threat Intelligence has identified an evolving fake-download campaign targeting users searching for cracked commercial software, free games, activators, plugins, and unofficial utilities. The campaign uses…
Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes. Google says…
A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco Secure Email Gateway could allow an unauthenticated, remote attacker to execute arbitrary commands with root privileges on the underlying…
Authorities arrested seven people allegedly involved in an investment fraud scheme that claimed potential victims in more than 50 countries, Europol said Tuesday. Officials said the operation caused estimated losses of…
Microsoft has been named a Leader in the inaugural 2026 Gartner® Magic Quadrant™ for AI Agent Management Platforms . We believe this recognition reflects Microsoft’s approach to helping organizations manage, secure, and…
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a "sophisticated, multi-stage campaign" that involved the use of a…
North Korean attackers "combined a range of techniques, including social engineering by fake recruitment interviews," Binance said about the multibillion-dollar crypto heist it discovered in October.
Early reports of ballot scanner malfunctions in Westchester County, New York are a sign of the challenges election officials will face in the current online information environment as voters head to the polls Tuesday on…