4Hackers Use GitHub-Hosted Poem to Control PoeLLM Malware Targeting AI InfrastructureCCCS Alerts & AdvisoriesCyber Security NewsPalo Alto Unit 42The Register Security+1Hackers are using a poem hosted on GitHub to guide PoeLLM malware toward its command-and-control servers, turning exposed AI infrastructure into a growing cryptocurrency-mining botnet. The campaign targets internet-facing services, including LiteLLM and Ollama, while also affecting Gotenberg PDF converters and Gitea development servers. Active since at least April 2026, PoeLLM uses selected words in the poem to calculate its next control server address. Changing those words lets the attacker redirect infected machines without replacing the malware. Compromised servers also become scanners and…
7MALFEX npm Malware Hides Executables in PNG Files to Infect Windows DevelopersCyber Security NewsMicrosoft SecurityThe Hacker NewsCVE-2026-69436 ↗CVE-2026-69582 ↗CVE-2026-71343 ↗A long-running npm malware campaign called MALFEX is targeting Windows developers with remote access tools, data stealers, and hidden downloaders. The attack uses eight malicious packages and three separate delivery paths, including a Windows executable disguised as a PNG and an encrypted program hidden after real image data. The operator has published packages since August 2023. Across the eight malicious packages, npm recorded 40,767 downloads by October 1, 2026, including 3,017 during the previous week. Those numbers show package reach, not confirmed infections: downloads can include…
8CVE-2026-21589: Critical unauthenticated arbitrary file access in Atlassian productsBleeping ComputerRapid7 BlogSANS Internet Storm CenterwatchTowr Labs+1CVE-2026-21589 ↗Overview On October 5, 2026, Atlassian published a security advisory for CVE-2026-21589 , a critical arbitrary file access vulnerability affecting eight products: Bitbucket Data Center, Confluence Data Center, Jira Service Management Data Center, Jira Software Data Center, Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye. Atlassian assigned the vulnerability a CVSSv4 score of 9.3 . An unauthenticated remote attacker who knows a target file's exact name and path can access it within the application's web root; the vulnerability does not provide directory listing or enumeration…
9Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users' MailboxesTenable BlogThe Hacker NewsMicrosoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain conditions. The vulnerability, tracked as CVE-2026-96940, is rated 8.8 on the CVSS scoring system. "Weak authorization in Microsoft Exchange Server allows an authenticated attacker to elevate privileges over a
10Amazon has an uncomfortably personal profile on youBleeping ComputerMalwarebytes LabsAmazon’s “About You” page reveals what it thinks it knows about you—and you can’t simply switch it off. Dexerto reports that one shopper discovered her profile included the observation: “has flat buttocks” She suggested this might relate to a previous purchase of “butt scrunch leggings.” Whatever the connection, buying clothes doesn’t mean you expect the retailer to start describing your body. What is Amazon’s About You? About You is a page where customers can review and edit the personal details Amazon uses to shape their shopping recommendations. Amazon introduced it in May as a way to make…
13Microsoft, Adobe, Apple, and Foxit vulnerabilitiesCisco TalosSchneier on SecurityCisco Talos’ Vulnerability Discovery & Research team recently disclosed vulnerabilities in Adobe, Apple, Foxit Reader, and Microsoft. The vulnerabilities mentioned in this blog post have been patched by their respective vendors, in adherence to Cisco’s third-party vulnerability disclosure policy . For Snort coverage that can detect the exploitation of these vulnerabilities, download the latest rule sets from Snort.org , and our latest Vulnerability Advisories are always posted on Talos Intelligence’s website . Adobe Photoshop privilege escalation vulnerability TALOS-2026-2360 (CVE-2026-48388)…
14Google issues Android security updates: who can get them and howCCCS Alerts & AdvisoriesMalwarebytes LabsGoogle has published security fixes for Android . The October updates are available for Android operating system versions 14, 15, 16, 16-qpr2, and 17 where “qpr” stands for Quarterly Platform Release. QPRs are interim updates Google pushes out between major yearly cycles. These Android security bulletins contain valuable information for Android users. The updates are important as they fix several vulnerabilities rated as Critical, which can be exploited without users even doing anything. However, we don’t write about them very often. The main reason for that lack of attention is that many…
15Poetry is the new AI security threat as PoeLLM malware infects 3K+ serversBleeping ComputerThe Register SecurityA suspected Italian attacker armed with a malware-controlling poem has infected more than 3,000 servers since April, breaking into enterprise AI infrastructure to mine cryptocurrency and add compromised systems to its growing botnet. This is the first case of “adversarial poetry” - an AI jailbreak technique that turns harmful prompts into poems to trick LLMs into bypassing safety guardrails - that Lumen’s Black Lotus Labs, which has been tracking the PoeLLM malware, has seen in real-world attacks. “This is a first for us,” the researchers told The Register via email. “While we can't get…
18Citrix NetScaler security snafus get even worse amid more 0-day reportsCyberScoopInfosecurity MagazineThe Register SecurityThe attackers just keep coming after Citrix NetScaler appliances, as both the feds and private security researchers warn that someone found - and has already exploited - yet another Citrix bug before it had a patch. This latest vulnerability, tracked as CVE-2026-88779, is a memory overflow bug that leads to denial of service attacks. It only affects NetScaler ADC and Gateway appliances configured as a SAML (Security Assertion Markup Language) service provider or identity provider, used for single sign-on authentication. Late Friday, amid exploitation reports, Citrix confirmed that it was…
19Hitachi Energy RTU500CISA Alerts & AdvisoriesCISA ICS AdvisoriesView CSAF Summary Hitachi Energy is publishing this cybersecurity advisory in response to the security findings reported by Dragos affecting end-of-life RTU500 CMU firmware version 9.x. The reported findings are associated with legacy RTU500 firmware versions that were developed according to the cybersecurity requirements, threat landscape, and industry practices that existed at the time of their release. As cybersecurity threats and security expectations have evolved, these end-of-life versions no longer incorporate many of the security controls and hardening measures that are standard in…
Community-built AI agents, skills, and MCP servers are landing in SOC workflows fast. Here’s what the Exchange Inspector tests before a listing earns its vetted tag on the CyberAgents Exchange. Three tools have already…
Community-built AI agents, skills, and MCP servers are landing in SOC workflows fast. Here’s what the Exchange Inspector tests before a listing earns its vetted tag on the CyberAgents Exchange. Three tools have already passed. Key takeaways Every Inspector-vetted listing clears three gates: an automated check, a frontier model assessment, and human verification. Tenable uses Tenable One AI Exposure to screen for prompt injection and exposed secrets, and OpenAI GPT Cyber models to assess the code and threat model. Tenable security researchers then verify runtime behavior in a clean…
Russian-aligned hackers have targeted Ukrainian transportation, manufacturing and energy companies with a constantly evolving malware strain designed to harvest system data, according to new research.
Amazon’s “About You” page reveals what it thinks it knows about you—and you can’t simply switch it off. Dexerto reports that one shopper discovered her profile included the observation: “has flat buttocks” She suggested…
Amazon’s “About You” page reveals what it thinks it knows about you—and you can’t simply switch it off. Dexerto reports that one shopper discovered her profile included the observation: “has flat buttocks” She suggested this might relate to a previous purchase of “butt scrunch leggings.” Whatever the connection, buying clothes doesn’t mean you expect the retailer to start describing your body. What is Amazon’s About You? About You is a page where customers can review and edit the personal details Amazon uses to shape their shopping recommendations. Amazon introduced it in May as a way to make…
A drone strike on a large Yandex data center caused a significant disruption to the Russian tech giant's network, with connectivity reportedly falling to around 70 percent of normal levels.
ASOS is sending updates to affected customers about the cybersecurity incident it suffered earlier this week, confirming that hackers accessed some personal data.
Britain and Germany have announced a partnership to counter cyberattacks and sabotage, particularly from Russia, as Prime Minister Andy Burnham heads to Berlin for talks. Under the arrangement announced Thursday, the…
Britain and Germany have announced a partnership to counter cyberattacks and sabotage, particularly from Russia, as Prime Minister Andy Burnham heads to Berlin for talks. Under the arrangement announced Thursday, the countries will share information and coordinate efforts to monitor, deter, and disrupt hostile activity, including threats to critical infrastructure. The announcement comes ahead of Burnham's first face-to-face meeting with German Chancellor Friedrich Merz, where security won't be the only item on the agenda. The PM is also expected to raise Britain's relationship with the EU…
A suspected lone threat actor used an AI-powered penetration-testing tool called ARTEX to breach several South Korean financial organizations and steal customer and employee data. The activity, which ran from late…
A suspected lone threat actor used an AI-powered penetration-testing tool called ARTEX to breach several South Korean financial organizations and steal customer and employee data. The activity, which ran from late September to early October 2026, affected banks, savings banks, capital firms, and online lending services. The case shows how open-source AI tools can help a single operator run fast, wide-scale intrusion activity against many targets. The breaches reportedly exposed sensitive information from systems that were less protected than core banking platforms. At Shinhan Bank, the actor…
If you thought that having companies trawling your social media, browsing history, and TV habits for behavioral clues was bad, sit tight. Meta is just getting started. Its Muse personal AI agent is taking surveillance…
If you thought that having companies trawling your social media, browsing history, and TV habits for behavioral clues was bad, sit tight. Meta is just getting started. Its Muse personal AI agent is taking surveillance to the next level. TIME magazine analyzed the software’s internal instructions and found that it maintains constantly updated dossiers on users and the people they know. Meta released Muse last month, positioning it as a digital assistant that can handle different parts of your life. It can organize your emails, handle your grocery shopping, and cancel your subscriptions. It is…
CrowdStrike revealed that a Chinese-speaking hacker deployed agentic pentesting tool ARTEX and Claude to help breach data from South Korean financial firms
Gitea has released security updates addressing 27 reported flaws across versions 28.0.0 and 28.1.0, including a critical SSH authentication bypass and server-side request forgery (SSRF) weaknesses. The fixes cover…
Gitea has released security updates addressing 27 reported flaws across versions 28.0.0 and 28.1.0, including a critical SSH authentication bypass and server-side request forgery (SSRF) weaknesses. The fixes cover account access, repository permissions, automated workflows, and connections to internal systems. Administrators should treat the update as an urgent priority for their development infrastructure. Released on September 30, Gitea 28.0.0 lists 20 CVEs in its security notes. The reported total of 27 spans that release and the follow-up 28.1.0 update, rather than 28.0.0 alone. Gitea…
Phishing kits are no longer limited to copying a familiar login page and waiting for a victim to enter credentials. Attackers are increasingly building filtering, session management, and traffic controls into the…
Phishing kits are no longer limited to copying a familiar login page and waiting for a victim to enter credentials. Attackers are increasingly building filtering, session management, and traffic controls into the infrastructure that delivers the phishing page itself. ANY.RUN has identified Wazza, a new phishkit targeting banking, manufacturing, and government organizations across the US, Europe
The co-creator of Empire Market, one of the largest dark web marketplaces before its shutdown, has been sentenced to 40 years in prison for facilitating $430 million in illegal transactions from 2018 to 2020.
wolfSSL has released wolfSSH 1.6.0 to fix five security flaws, including a critical host key verification bypass that could let an attacker impersonate an SSH server. Published on October 6, 2026, the update addresses…
wolfSSL has released wolfSSH 1.6.0 to fix five security flaws, including a critical host key verification bypass that could let an attacker impersonate an SSH server. Published on October 6, 2026, the update addresses Windows privilege escalation, unauthenticated key exchange abuse, unauthorized forwarding channels, and an SFTP memory corruption bug. The release rates one flaw critical, one high, and three medium. The most serious issue, CVE-2026-16516, affects wolfSSH through version 1.5.0. During SSH key exchange , the client failed to check whether the ECDSA curve inside the server’s host…
A serving Royal Navy member has been charged with spying for an unnamed foreign country after an investigation by Counter Terrorism Policing London. Teddy Young, 24, from Bedfordshire, faces two offenses under the…
A serving Royal Navy member has been charged with spying for an unnamed foreign country after an investigation by Counter Terrorism Policing London. Teddy Young, 24, from Bedfordshire, faces two offenses under the National Security Act 2023 involving protected information and preparations to disclose it. The allegations remain unproven. Police arrested Young at his home on Tuesday, October 6, and held him in custody ahead of a scheduled appearance at Westminster Magistrates’ Court on Thursday, October 8. According to the BBC report , the charges cover alleged conduct between November 26…
Cisco Talos identified an advanced persistent threat (APT) spear-phishing campaign against individuals affiliated with Taiwan research organizations. The operation leveraged legitimate public event themes and…
Cisco Talos identified an advanced persistent threat (APT) spear-phishing campaign against individuals affiliated with Taiwan research organizations. The operation leveraged legitimate public event themes and impersonated reputable academic and policy institutions to establish credibility. The phishing emails exhibited highly consistent structure, rhetoric, and personalization patterns, suggesting the threat actor likely used AI-assisted content generation to rapidly customize invitation lures for different targets while maintaining a common social engineering framework. Beyond traditional…
“AI-analysis evasion” encapsulates the real-world techniques malware authors are developing in attempt to obstruct or defeat any layers of automated AI analysis. This technique is cheap to add but inconsistently…
“AI-analysis evasion” encapsulates the real-world techniques malware authors are developing in attempt to obstruct or defeat any layers of automated AI analysis. This technique is cheap to add but inconsistently impactful — the best techniques steered the outcome in the attacker’s favor in about 35% of test runs. Further, it must always be plaintext and therefore is always detectable. The operators are not wrong to assume AI tools are in the analysis pipeline, but the answer is not to remove them; it is to build them so that text inside a sample is always treated as evidence, never as…
The country is consumed right now with debating artificial intelligence and whether increasingly powerful AI systems could escape human control. Those are valid concerns, but lawmakers are overlooking another…
The country is consumed right now with debating artificial intelligence and whether increasingly powerful AI systems could escape human control. Those are valid concerns, but lawmakers are overlooking another technological threat: quantum computing. Unlike AI safety debates, this risk could render today’s encryption obsolete – compromising everything from emails to financial transactions to government communications and military systems. Quantum computers harness unusual properties of quantum physics to solve certain problems far faster than conventional computers. That potential offers major…
Cybersecurity researchers have discovered a cluster of 16 malicious Mozilla Firefox extensions that are capable of stealing cryptocurrency wallet recovery phrases and private keys. "The extensions masquerade as wallet…
Cybersecurity researchers have discovered a cluster of 16 malicious Mozilla Firefox extensions that are capable of stealing cryptocurrency wallet recovery phrases and private keys. "The extensions masquerade as wallet portals, desktop utilities, and browser tools, but their code intercepts recovery phrases and private keys during wallet import flows and attempts to send those secrets to
Hackers are using a poem hosted on GitHub to guide PoeLLM malware toward its command-and-control servers, turning exposed AI infrastructure into a growing cryptocurrency-mining botnet. The campaign targets…
Hackers are using a poem hosted on GitHub to guide PoeLLM malware toward its command-and-control servers, turning exposed AI infrastructure into a growing cryptocurrency-mining botnet. The campaign targets internet-facing services, including LiteLLM and Ollama, while also affecting Gotenberg PDF converters and Gitea development servers. Active since at least April 2026, PoeLLM uses selected words in the poem to calculate its next control server address. Changing those words lets the attacker redirect infected machines without replacing the malware. Compromised servers also become scanners and…
Cisco has released security updates for three critical vulnerabilities in Nexus 3000 and 9000 Series switches that could let remote attackers run code with root privileges without logging in. The flaws affect the Next…
Cisco has released security updates for three critical vulnerabilities in Nexus 3000 and 9000 Series switches that could let remote attackers run code with root privileges without logging in. The flaws affect the Next Generation Operation, Administration, and Maintenance feature, known as NGOAM, in Cisco NX-OS Software. Successful attacks could also crash processes, force switches to reload, and disrupt network services. Published on October 7, 2026, Cisco’s security advisory covers CVE-2026-76485, CVE-2026-76486, and CVE-2026-76501. The advisory carries a CVSS base score of 9.8. Cisco found…
Welcome back to PWNED, the weekly column where we highlight some of the lowlights in corporate security. This week, we’ll talk about two scenarios, one that ended in tragedy and another that shows the power of a good…
Welcome back to PWNED, the weekly column where we highlight some of the lowlights in corporate security. This week, we’ll talk about two scenarios, one that ended in tragedy and another that shows the power of a good defense over dedicated phishing attacks. Have a story about someone leaving a gaping hole in their network? Share it with us at pwned@sitpub.com. Anonymity is available upon request. Both stories come courtesy of Dave Hatter, a cybersecurity and compliance consultant with Intrust IT. In his many years of experience with the company, Hatter has had to work for a variety of small…
A long-running npm malware campaign called MALFEX is targeting Windows developers with remote access tools, data stealers, and hidden downloaders. The attack uses eight malicious packages and three separate delivery…
A long-running npm malware campaign called MALFEX is targeting Windows developers with remote access tools, data stealers, and hidden downloaders. The attack uses eight malicious packages and three separate delivery paths, including a Windows executable disguised as a PNG and an encrypted program hidden after real image data. The operator has published packages since August 2023. Across the eight malicious packages, npm recorded 40,767 downloads by October 1, 2026, including 3,017 during the previous week. Those numbers show package reach, not confirmed infections: downloads can include…
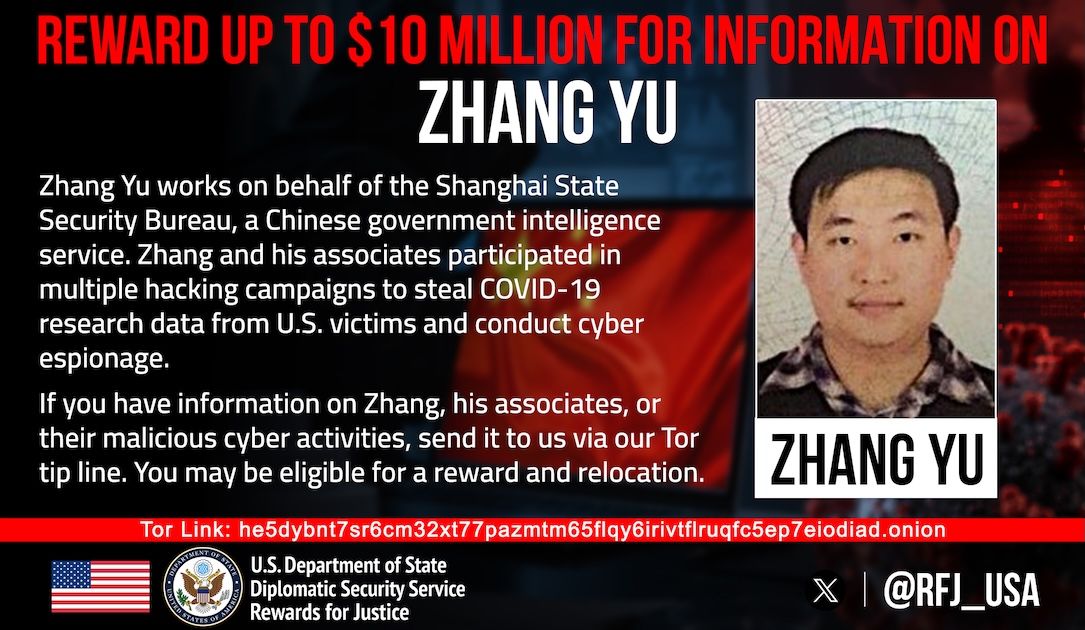
The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged in the United States in connection with the 2021 Microsoft…
The U.S. State Department is offering up to $10 million for information leading to the identification or location of Zhang Yu, a Chinese national charged in the United States in connection with the 2021 Microsoft Exchange Server attacks known as HAFNIUM. The reward is for information leading to his identification or location, the news outlet NTD reported this week, citing a notice
The U.S. Department of Justice (DoJ) on Wednesday announced charges against a 50-year-old U.S. and Israeli national for allegedly defrauding ransomware victims by secretly paying the attackers to obtain decryptors while…
The U.S. Department of Justice (DoJ) on Wednesday announced charges against a 50-year-old U.S. and Israeli national for allegedly defrauding ransomware victims by secretly paying the attackers to obtain decryptors while claiming to use proprietary tools to recover their data. Zohar Pinhasi (aka Zack Silver and Zack Green) has been charged with two counts of wire fraud and one count of wire
Attackers don’t crack what they can copy and leaked API keys sit in git history, Slack threads, and cloud workloads waiting. Evaluating the landscape alongside the Top 10 Best Secrets Management Tools in 2026 shows that…
Attackers don’t crack what they can copy and leaked API keys sit in git history, Slack threads, and cloud workloads waiting. Evaluating the landscape alongside the Top 10 Best Secrets Management Tools in 2026 shows that while vaults manage credentials securely, finding hardcoded keys already exposed in code requires dedicated discovery. We scored ten secrets-detection options with verification quality weighted highest, because a thousand regex hits hide the ten live credentials that matter. GitGuardian takes 1 ; Truffle Security and GitHub’s native scanning complete the podium. Key Takeaways…
The supply chain is four attack surfaces wearing one buzzword dependencies, pipelines, artifacts, and base images and no vendor covers all four. We scored ten tools with surface-coverage honesty weighted highest. With…
The supply chain is four attack surfaces wearing one buzzword dependencies, pipelines, artifacts, and base images and no vendor covers all four. We scored ten tools with surface-coverage honesty weighted highest. With modern threat actors executing sophisticated software supply chain attacks targeting developer environments , evaluating platforms alongside the Top 10 Best Supply Chain Intelligence Security Companies demonstrates that static checklists can no longer safeguard the modern software development lifecycle (SDLC). Chainguard takes 1 for attacking the problem at its source; Sonatype…
Your API count is wrong every traffic-based discovery deployment proves it and business-logic abuse rides valid-looking requests straight past WAF signatures. As enterprise architectures decompose into distributed…
Your API count is wrong every traffic-based discovery deployment proves it and business-logic abuse rides valid-looking requests straight past WAF signatures. As enterprise architectures decompose into distributed microservices and third-party integrations, evaluating these platforms alongside the Top 10 Best API Penetration Testing Companies reveals that static rules and legacy inspection are no longer sufficient to stop modern API threats. We scored the leading API security options with discovery depth and behavioral detection weighted highest, and the consolidation wave decoded: nine…
On the second day of Pwn2Own Ireland 2026, security researchers collected $232,500 in cash awards after exploiting 45 unique zero-day vulnerabilities.
The npm package known as "tensorlake," a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud supply chain attack. The…
The npm package known as "tensorlake," a TypeScript software development kit (SDK) for Tensorlake applications, sandboxes, and cloud services, was compromised as part of a ChainDrop / Shai-Hulud supply chain attack. The malicious version 0.5.144 "contains obfuscated malware that harvests credentials, exfiltrates secrets, establishes persistence, and executes remotely supplied code," Socket said
The United States Department of Justice has charged a man with fraud after he allegedly told clients he could decrypt files locked up by ransomware but actually paid ransoms – and seemingly got away with it for years…
The United States Department of Justice has charged a man with fraud after he allegedly told clients he could decrypt files locked up by ransomware but actually paid ransoms – and seemingly got away with it for years. The Feds allege that Zohar Pinhasi – aka “Zack Silver” and “Zack Green” – ran a Florida company called “MonsterCloud” that advised ransomware victims not to pay because it had a way to recover encrypted data. “The charges relate to Pinhasi’s claimed ability to decrypt ransomware without paying cybercriminals, purportedly using ‘proprietary tools’ and ‘advanced decryption…
As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams conducted a comprehensive internal security review. This review resulted in software hardening releases that address…
As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities. These vulnerabilities were found during internal testing and are not known to be actively exploited. To assist customers in patching and streamline the disclosure process, Cisco has grouped these issues by their underlying vulnerability class — Common Weakness Enumeration (CWE) — and assigned a single Common Vulnerabilities and…
Microsoft's Twitter account, with its 13 million followers, was hijacked by a paperclip. There was no ransomware or data theft, just Clippy, a dodgy crypto coin, and a corporate apology that wasn't from Microsoft…
Microsoft's Twitter account, with its 13 million followers, was hijacked by a paperclip. There was no ransomware or data theft, just Clippy, a dodgy crypto coin, and a corporate apology that wasn't from Microsoft either. Meanwhile, UK losses from hacked email and social media accounts have rocketed by 417%, as scammers pose as your friends to flog you tickets to gigs that don't exist. Plus, Hack The Box's Christine Bartlett joins us for a featured interview to ask what happens when AI agents join your security team, and whether anyone has thought to give them a performance review.
The owner of ransomware remediation company MonsterCloud has been charged with allegedly defrauding ransomware victims by secretly paying their attackers for decryptors while claiming to use proprietary technology to…
In the wake of an agentic attack against its own Medicare systems, Australia's government is feeling out what regulations might look like for frontier AI companies.
At a recent event for security firm NordVPN, NBA superstar Shaquille O’Neal revealed that he got hacked—and warned the public about the need to “have control of their own information.”
The FBI is warning that FortiBleed attacks are still ongoing, targeting exposed Fortinet FortiGate firewalls and SSL VPN gateways and locking out legitimate administrators.
The Citizen Lab's Ron Deibert warns the US government is pushing for pervasive surveillance and says certain technology executives are all too happy to help.
Hackers obtained unauthorized HTTPS certificates for several Google domains and hijacked domains in the country-code top-level domains (ccTLDs) for Ghana, American Samoa, and Sierra Leone after compromising third-party…
Hackers obtained unauthorized HTTPS certificates for several Google domains and hijacked domains in the country-code top-level domains (ccTLDs) for Ghana, American Samoa, and Sierra Leone after compromising third-party operators and modifying authoritative DNS records.
U.S. officials say Zhang Yu was a prominent figure in the Hafnium campaign, which saw hackers breach thousands of computers and steal troves of documents.
Federal government contractors that handle sensitive information could soon face a “sea change” in rules about how they protect that information and report when it has been part of a breach. Pending federal regulations…
Federal government contractors that handle sensitive information could soon face a “sea change” in rules about how they protect that information and report when it has been part of a breach. Pending federal regulations on the handling of “controlled unclassified information,” or CUI, a category of sensitive data that falls short of classified — including people’s personal information such as Social Security numbers, information that could expose vulnerabilities in critical infrastructure and more — could arrive as soon as the end of this year, but likely no later than the end of President…
Imagine going to a Google website at its correct URL, only to be redirected to a crim's illegitimate copy. Attackers hijacked top-level domains, allowing them to alter DNS records and mint fraudulent HTTPS certificates…
Imagine going to a Google website at its correct URL, only to be redirected to a crim's illegitimate copy. Attackers hijacked top-level domains, allowing them to alter DNS records and mint fraudulent HTTPS certificates for several Google domains, and those belonging to other organizations. Google said it became aware of the series of attacks last week in the .gh (Ghana), .sl (Sierra Leone), and .as (American Samoa) country-code top-level namespaces (ccTLDs). “During these hijacks, attackers modified authoritative DNS records and obtained unauthorized HTTPS certificates covering several Google…
Most industries manage one major compliance framework. Universities might manage four simultaneously, each bringing with it unique requirements, enforcement mechanisms, and consequences for failure. Here's what that…
Most industries manage one major compliance framework. Universities might manage four simultaneously, each bringing with it unique requirements, enforcement mechanisms, and consequences for failure. Here's what that actually looks like in practice. In Part 1 of this series, we laid out the scale of the threat facing higher education: 4,388 cyberattacks per organization per week, a 24% year-over-year increase, and the fundamental architectural flaw of defending each campus independently. If the threat picture alone wasn't enough to demand action, there's a second crisis unfolding in parallel…
Cisco Talos’ Vulnerability Discovery & Research team recently disclosed vulnerabilities in Adobe, Apple, Foxit Reader, and Microsoft. The vulnerabilities mentioned in this blog post have been patched by their respective…
Cisco Talos’ Vulnerability Discovery & Research team recently disclosed vulnerabilities in Adobe, Apple, Foxit Reader, and Microsoft. The vulnerabilities mentioned in this blog post have been patched by their respective vendors, in adherence to Cisco’s third-party vulnerability disclosure policy . For Snort coverage that can detect the exploitation of these vulnerabilities, download the latest rule sets from Snort.org , and our latest Vulnerability Advisories are always posted on Talos Intelligence’s website . Adobe Photoshop privilege escalation vulnerability TALOS-2026-2360 (CVE-2026-48388)…
Attackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6. Google's own systems were not breached, but any…
Attackers compromised three country-code top-level domains (ccTLDs) and obtained unauthorized HTTPS certificates for several Google domains, Google said on October 6. Google's own systems were not breached, but any domain ending in .gh (Ghana), .sl (Sierra Leone) or .as (American Samoa) was put at risk. With such a certificate, an attacker could pose as the real site over an encrypted
Lawmakers who oversee military cyber policy as well as the Fort Meade, Maryland, hub for those agencies say an $11 million mental health program should be locked in to defense spending legislation.