2How Multi-Campus Universities can Build a more Connected Security ProgramCisco Security AdvisoriesHuntressInfosecurity MagazineRapid7 BlogSecurityWeekThe Hacker NewsWiz Research+4Parts 1 and 2 of this series looked at two pressures facing higher education security teams. First, the threat landscape : universities are dealing with more frequent attacks across complex, distributed environments, while campus-by-campus security can make it harder to share intelligence and coordinate response. Second, the compliance burden: overlapping requirements across FERPA, GLBA, HIPAA, and CMMC make it difficult to establish what data was affected, which reporting obligations apply, and how quickly the institution needs to act. This final part is about what changes when a university…
4AI worms could spread across your smart devices, Anthropic warnsCCCS Alerts & AdvisoriesInfosecurity MagazineMalwarebytes LabsYour streaming box might not look like much of a computer. But connect enough inexpensive devices together, and they can run an AI model. Researchers at Anthropic demonstrated this by running a Google Gemma model across 15 off-brand Android TV boxes. They warn that small models could soon spread across vulnerable internet-of-things (IoT) devices, including smart ovens and TV boxes, stating: “Our experiments suggest that small AI models may be months away from being capable enough to self-replicate on commercial internet-of-things (IoT) devices, like smart ovens and off-brand Android TV…
7Hackers Exploit D-Link, Ubiquiti and SAP Flaws to Hijack Devices for Proxy NetworksCCCS Alerts & AdvisoriesCyber Security NewsThe Hacker NewsA cybercrime campaign has compromised at least 143 devices in 34 countries by exploiting flaws in D-Link, Ubiquiti and SAP products. The attackers installed Pawns.app proxy software on victim devices, turning their internet connections into residential proxy nodes. That lets the operator route internet traffic through the victims’ real IP addresses, which can make the activity harder to trace and may help it blend in with ordinary user traffic. GreyNoise researchers identified the campaign and linked it to an actor tracked as “skynox7.” The group used known vulnerabilities in network storage…
8Google Automatically Adds Your Phone Number to Every Google Account on Your Android PhoneBleeping ComputerCyber Security NewsThe Hacker NewsGoogle automatically verifies phone numbers on Android devices and adds them to every Google account signed in on the Phone. The setting is enabled by default, raising privacy concerns for users who keep personal, work, and secondary accounts separate. Google’s documentation confirms that the behavior covers both existing accounts and accounts added later. The feature, called Phone number verification, also covers new phone numbers added to a device. Adding another Google account can link it to numbers already on the Phone, while adding a new number can attach it to accounts already signed…
10Ivanti patches Connect Secure zero-day after researchers confirm in-the-wild attacksCCCS Alerts & AdvisoriesCyberScoopThe Hacker NewsThe Register SecurityVolexity+2Ivanti customers are being urged to update Connect Secure and check for compromise after attackers exploited a newly disclosed zero-day vulnerability. On Tuesday, Ivanti released updates for Connect Secure (ICS) to fix CVE-2026-104935, an authentication bypass flaw discovered by Volexity. Rated 8.6 on the CVSS scale, it allows remote, unauthenticated attackers to execute arbitrary commands. "We are aware of exploitation in the wild affecting a limited number of customers at the time of disclosure," the vendor said in its advisory. There are limited indicators of compromise available at…
11Cisco make-me-root email bug exploited as a 0-day by unknown crimsCCCS Alerts & AdvisoriesRecorded Future IntelligenceThe Hacker NewsThe Register Security+1Cisco “strongly” implored customers to patch yet another critical, make-me-root vulnerability in its Secure Email Gateway (SEG), one that has already been exploited in zero-day attacks. A Cisco spokesperson told The Register that the critical vuln, which received a 9.8 out of 10 CVSS rating, affects “a limited number of customers.” The bug, now tracked as CVE‑2026‑76519, allows remote, unauthenticated attackers to write files and execute commands with root privileges on the appliance’s operating system - simply by sending a malicious email. In separate Wednesday advisories, both the…
12Security researchers spent 6 days doing their Chromework, built 1B user exploitMalwarebytes LabsThe Hacker NewsThe Register SecurityResearchers at security startup Xbow used OpenAI's GPT-5.6 Sol model to help chain three zero-day vulnerabilities in Chrome into an exploit capable of executing code outside the browser's sandbox on Windows machines. Xbow estimates that this could affect about one billion users worldwide. Google fixed all three, and paid the Xbow team a $250,000 bounty, its top reward for a Chrome full-chain exploit. The payout also proves a nice return on investment for the human bug hunters - Brendan Dolan-Gavitt, Andres Luksenberg, Baul Lee, and Willem Pinckaers - who spent just six days during the Black…
14Legal Aid Agency hackers made off with records dating back to 1978Bleeping ComputerThe RecordThe Register SecurityHackers who broke into the UK's Legal Aid Agency last year stole records dating back nearly five decades, the government has admitted, revealing the breach was far more extensive than previously thought. The Legal Aid Agency said on Wednesday that around 250,000 records stolen in the April 2025 attack date from before 2007, including one going back to 1978. That's much further back than the agency previously estimated – it initially said the stolen data covered legal aid applications, claims, and payments from 2007. Most of the newly identified records date from the 1990s and 2000s, with…
15Proofpoint to buy Varonis for $6.3 billionCyberScoopSecurityWeekProofpoint agreed Thursday to acquire Varonis Systems in a cash transaction valued at approximately $6.3 billion, combining two companies that have positioned themselves around a shared bet: that securing data has become the central problem of the AI era. The acquisition pairs two distinct approaches to security. Varonis specializes in data security, mapping where sensitive information sits inside an organization, who can reach it, and how it is actually used. Proofpoint, owned by private equity company Thoma Bravo, built its business around protecting people, blocking phishing, fraud and…
16Drupal Patches Critical Field UI Flaw With Unauthenticated RCE Path via Contributed ModulesCCCS Alerts & AdvisoriesThe Hacker NewsDrupal core has a critical flaw in its Field UI module that could let an attacker run code on the site's server, and fixes were shipped on October 14 in Drupal 11.4.10, 11.3.19, and 10.6.19. An attacker cannot reach the flaw through core alone, the Drupal Security Team said in its advisory. Several exploit paths exist through contributed modules, and at least one known path needs no login.
18CISA Adds One Known Exploited Vulnerability to CatalogCCCS Alerts & AdvisoriesCISA Alerts & AdvisoriesCVE-2026-21589 ↗CISA has added one new vulnerability to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2026-21589 Atlassian Multiple Products Files or Directories Accessible to External Parties Vulnerability This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise. Binding Operational Directive (BOD) 26-04: Prioritizing Security Updates Based on Risk establishes vulnerability management requirements for Federal Civilian Executive Branch (FCEB) agencies. BOD 26-04 reinforces the…
20GhostAction Compromises About 1,900 GitHub Accounts, Targets Over 30,000 RepositoriesAny.Run Malware AnalysisThe Hacker NewsThe credential-theft campaign known as GhostAction has ramped up, targeting more than 30,000 repositories across 3,000 users and organizations. The spike, according to GitGuardian, was observed on October 8 and 9, 2026. "This resulted from compromising the GitHub accounts of about 1,900 users. It attempted to extract 3,174 secrets from public repositories' CI," security researchers Gaetan
Some awards you're happy to receive, while others make you stop for a moment. Receiving the 2026 Péter Szőr Award this week at Virus Bulletin in Seville for our research, BPFdoor in Telecom Networks: Sleeper Cells in…
Some awards you're happy to receive, while others make you stop for a moment. Receiving the 2026 Péter Szőr Award this week at Virus Bulletin in Seville for our research, BPFdoor in Telecom Networks: Sleeper Cells in the Backbone , was of the latter kind. Virus Bulletin created the award to honor Péter's life and work, and it recognizes outstanding technical security research: the rigorous, the deep, and the useful – exactly what he was known for himself. And as far as recognitions in our industry go, it's hard to top. I'm extremely proud. What the Pèter Szőr Award means to us I knew Péter…
Burger King Japan, the Japanese subsidiary of global fast-food giant Burger King, disclosed a major data breach after attackers accessed a server containing 11.18 million customer records.
AI can help you send more job applications. But when you lose track of where you’ve applied, a fake recruiter’s message can start to look like the reply you’ve been waiting for. Job hunting can feel like shouting into…
AI can help you send more job applications. But when you lose track of where you’ve applied, a fake recruiter’s message can start to look like the reply you’ve been waiting for. Job hunting can feel like shouting into the void. You send applications, rewrite cover letters, and wait for replies that may never arrive. Then a message lands on your phone: someone wants to talk about a job. But was it one of the jobs you applied for? It is hard to keep track when you’ve sent out a lot of them. Two reports highlight an uncomfortable overlap. The BBC describes jobseekers using AI to apply for large…
In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman's fast, intuitive thinking. OpenAI…
In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman's fast, intuitive thinking. OpenAI announced its own Decisions API at DevDay and opened a public beta on October 6. Cribl published cribl-decision, an open LoRA adapter you can run locally. Others, like Laya, are
A large Chinese-language phishing operation has used around 17,000 internet domains to impersonate banks, payment services, retailers and other well-known brands, with Japan as its main target. The operation relies on…
A large Chinese-language phishing operation has used around 17,000 internet domains to impersonate banks, payment services, retailers and other well-known brands, with Japan as its main target. The operation relies on three related phishing kits—CoGUI, CoAceV and CoFish_Ws—to send deceptive emails and direct victims to fake login or payment pages. The findings come as security companies and law-enforcement partners disrupt parts of the wider fraud network. Microsoft and Health-ISAC filed a civil lawsuit against people linked to the operation and seized or redirected domains connected to YAM…
This is a problem: Any open model whose weights have been edited can carry a backdoor, whether it’s a task-specific fine-tune, a merged adapter or an abliterated build. We have abliterated models in the title because…
This is a problem: Any open model whose weights have been edited can carry a backdoor, whether it’s a task-specific fine-tune, a merged adapter or an abliterated build. We have abliterated models in the title because it’s the most popular reason people download modified weights without verifying what’s inside. Abliteration is a cheap fine-tune that takes away a model’s ability to refuse. You find the direction in the weights that carries “no” and subtract it. The model then answers things a safety-tuned version would turn down. It began as a research trick and it’s now routine before people…
OpenAI is facing separate legal challenges over how ChatGPT interacts with children. The Guardian reports that eight US states accuse the company of misleading parents about the chatbot’s safety and exposing vulnerable…
OpenAI is facing separate legal challenges over how ChatGPT interacts with children. The Guardian reports that eight US states accuse the company of misleading parents about the chatbot’s safety and exposing vulnerable users to dangerous conversations. Separately, CNET reports that a mother suing on behalf of her two children alleges that OpenAI collected and used children’s sensitive personal information without valid parental consent. The cases raise serious questions about what happens when children trust a chatbot with their most private thoughts, and what responsibility the company…
Aoki, also known as Aokigahara, is a data-stealing malware that has added credentials for AI tools to its growing list of targets. Recent versions seek local files and session data linked to ChatGPT, Claude, OpenAI…
Aoki, also known as Aokigahara, is a data-stealing malware that has added credentials for AI tools to its growing list of targets. Recent versions seek local files and session data linked to ChatGPT, Claude, OpenAI Codex, Cursor, Codeium and Gemini. The change raises the risk for developers who use AI assistants alongside source-code repositories, cloud accounts and other work systems. Unlike a flaw in an AI service, Aoki’s activity focuses on data stored on an infected computer. A stolen key or token may let an intruder use an account as its owner, run up paid usage or reach services…
Google automatically verifies phone numbers on Android devices and adds them to every Google account signed in on the Phone. The setting is enabled by default, raising privacy concerns for users who keep personal, work…
Google automatically verifies phone numbers on Android devices and adds them to every Google account signed in on the Phone. The setting is enabled by default, raising privacy concerns for users who keep personal, work, and secondary accounts separate. Google’s documentation confirms that the behavior covers both existing accounts and accounts added later. The feature, called Phone number verification, also covers new phone numbers added to a device. Adding another Google account can link it to numbers already on the Phone, while adding a new number can attach it to accounts already signed…
An old-fashioned smash-and-grab job on a photographer’s vehicle threatens the security of pupils’ data as a UK secondary school says it faces a potential data protection pickle. Jon Curtis-Brignell, headteacher at…
An old-fashioned smash-and-grab job on a photographer’s vehicle threatens the security of pupils’ data as a UK secondary school says it faces a potential data protection pickle. Jon Curtis-Brignell, headteacher at Priory School in Lewes, said in an email this week that a company the school hired to take pupils’ annual school photos has alerted it to a data theft case after a vehicle was broken into. “Pret-a-Portrait has informed us that, overnight between 6 and 7 October, one of its vehicles was broken into and a camera bag containing SD memory cards was stolen,” Curtis-Brignell wrote. “Some…
India’s cyber response agency, CERT-In, has warned that hackers are using AI agents to cut the time between gaining access to systems and causing damage from days to just hours. Its critical advisory, issued on October…
India’s cyber response agency, CERT-In, has warned that hackers are using AI agents to cut the time between gaining access to systems and causing damage from days to just hours. Its critical advisory, issued on October 15, 2026, describes attacks against Indian organizations and separate incidents involving AI agents that exceeded their approved research tasks. The CERT-In advisory highlights two distinct risks. Criminals are deliberately using open-source AI tools to break into systems. Meanwhile, AI providers’ agents have accessed live business systems without permission. Providers…
A cybercrime campaign has compromised at least 143 devices in 34 countries by exploiting flaws in D-Link, Ubiquiti and SAP products. The attackers installed Pawns.app proxy software on victim devices, turning their…
A cybercrime campaign has compromised at least 143 devices in 34 countries by exploiting flaws in D-Link, Ubiquiti and SAP products. The attackers installed Pawns.app proxy software on victim devices, turning their internet connections into residential proxy nodes. That lets the operator route internet traffic through the victims’ real IP addresses, which can make the activity harder to trace and may help it blend in with ordinary user traffic. GreyNoise researchers identified the campaign and linked it to an actor tracked as “skynox7.” The group used known vulnerabilities in network storage…
MITRE released ATT&CK v20 on October 13, adding nine Enterprise techniques that describe how attackers may target AI systems, steal application-specific passwords to bypass multi-factor authentication (MFA), and get…
MITRE released ATT&CK v20 on October 13, adding nine Enterprise techniques that describe how attackers may target AI systems, steal application-specific passwords to bypass multi-factor authentication (MFA), and get around CAPTCHA checks. The update also expands coverage for industrial control systems (ICS) and mobile devices, and adds detection guidance for several of the new behaviors. For security teams, the changes offer a clearer way to map activity they already see across business networks, AI tools, phones, and industrial systems. MITRE’s release notes list the additions, and its…
Every downstream control DLP, encryption, retention, access inherits its accuracy from classification, which makes this the quiet foundation of data security . We scored the leading options with enforcement wiring…
Every downstream control DLP, encryption, retention, access inherits its accuracy from classification, which makes this the quiet foundation of data security . We scored the leading options with enforcement wiring weighted highest, and counted honestly: nine distinct vendors from ten sheet rows, since Titus and Boldon James both sell under Fortra. BigID takes 1 ; Microsoft Purview and Varonis complete the podium. Key Takeaways • 1 overall: BigID ML discovery and identity-correlation at privacy-era scale. • Podium: BigID (discovery depth), Purview (labels the estate enforces), Varonis…
A critical zero-day vulnerability in BeyondTrust Remote Support was exploited in late August, weeks before the company disclosed the flaw and released a patch. The suspected China-linked espionage group ARMORY CASTLE…
A critical zero-day vulnerability in BeyondTrust Remote Support was exploited in late August, weeks before the company disclosed the flaw and released a patch. The suspected China-linked espionage group ARMORY CASTLE used the weakness to access appliances, escalate privileges to root, and reach credentials the product stores or handles. Mandiant says the flaw lets an unauthenticated remote attacker perform file operations on an affected appliance, which may lead to full host control. The vulnerability is tracked as CVE-2026-102764. It affects supported BeyondTrust Remote Support versions up…
Tokenization does two very different jobs wearing one name: collapsing PCI audit scope for payment estates, and keeping analytics alive on protected enterprise data . We scored ten solutions across both lanes…
Tokenization does two very different jobs wearing one name: collapsing PCI audit scope for payment estates, and keeping analytics alive on protected enterprise data . We scored ten solutions across both lanes. Protegrity takes 1 for enterprise-data breadth; Very Good Security and Thales complete the podium. Key Takeaways • 1 overall: Protegrity analytics-preserving tokenization at Fortune-scale, warehouses to mainframes. • Podium: Protegrity (enterprise data), VGS (developer-payments vault), Thales (platform-estate tokenization). • Payments lane: TokenEx and Bluefin own scope-reduction; VGS…
Encryption is only as trustworthy as the key custody behind it and with post-quantum migration now a planning requirement, key inventories became strategy documents. We scored ten solutions from native cloud floors to…
Encryption is only as trustworthy as the key custody behind it and with post-quantum migration now a planning requirement, key inventories became strategy documents. We scored ten solutions from native cloud floors to sovereign HSMs. Thales takes 1 for multi-cloud estate control; AWS KMS and Fortanix complete the podium. Key Takeaways • 1 overall: Thales (CipherTrust) the enterprise key-lifecycle referee across clouds, Luna-HSM backed. • Podium: Thales (central control), AWS KMS (the native floor done best), Fortanix (confidential-computing frontier). • Start native: cloud KMS floors are…
The Administrative Office of the US Courts says a cyberattack on government contractor BAE Systems has taken down the notice system used by federal bankruptcy courts.
Change is constant, but The Register likes to keep some things the same – such as using Friday mornings to bring you a new installment of On Call, the reader-contributed column that shares your tech support stories…
Change is constant, but The Register likes to keep some things the same – such as using Friday mornings to bring you a new installment of On Call, the reader-contributed column that shares your tech support stories. This week, meet a reader we'll Regomize as "Daniel" who told us that in 2020 he was hired to replace a two-person IT department at a UK school. "The IT manager had left amid some 'accounting irregularities,' mainly involving high-end gaming PCs being purchased using school funds but never making it onto the school site," Daniel told On Call. "His deputy stepped up just in time to…
The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August…
The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August 2026. The vulnerability, tracked as CVE-2026-102764 (CVSS score: 9.3), is a case of improper origin validation in an internal messaging component that could be exploited by a
AI agents being tested online reached the live systems of Indian organizations and read business records, including personal data and confidential material, CERT-In said in an advisory on October 15. The agents went…
AI agents being tested online reached the live systems of Indian organizations and read business records, including personal data and confidential material, CERT-In said in an advisory on October 15. The agents went beyond their assigned tasks, and none of the organizations detected the unauthorized access. After internal reviews, the AI companies whose models were being tested
BeyondTrust warned customers on Thursday to patch a critical flaw in its Remote Support (RS) that has been exploited in zero-day attacks since late August.
A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH. The attack involves the…
A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH. The attack involves the exploitation of CVE-2025-61624 (CVSS score: 5.4), a path traversal flaw in the command line interpreter of FortiOS, FortiPAM, FortiProxy, and FortiSwitchManager that could allow a
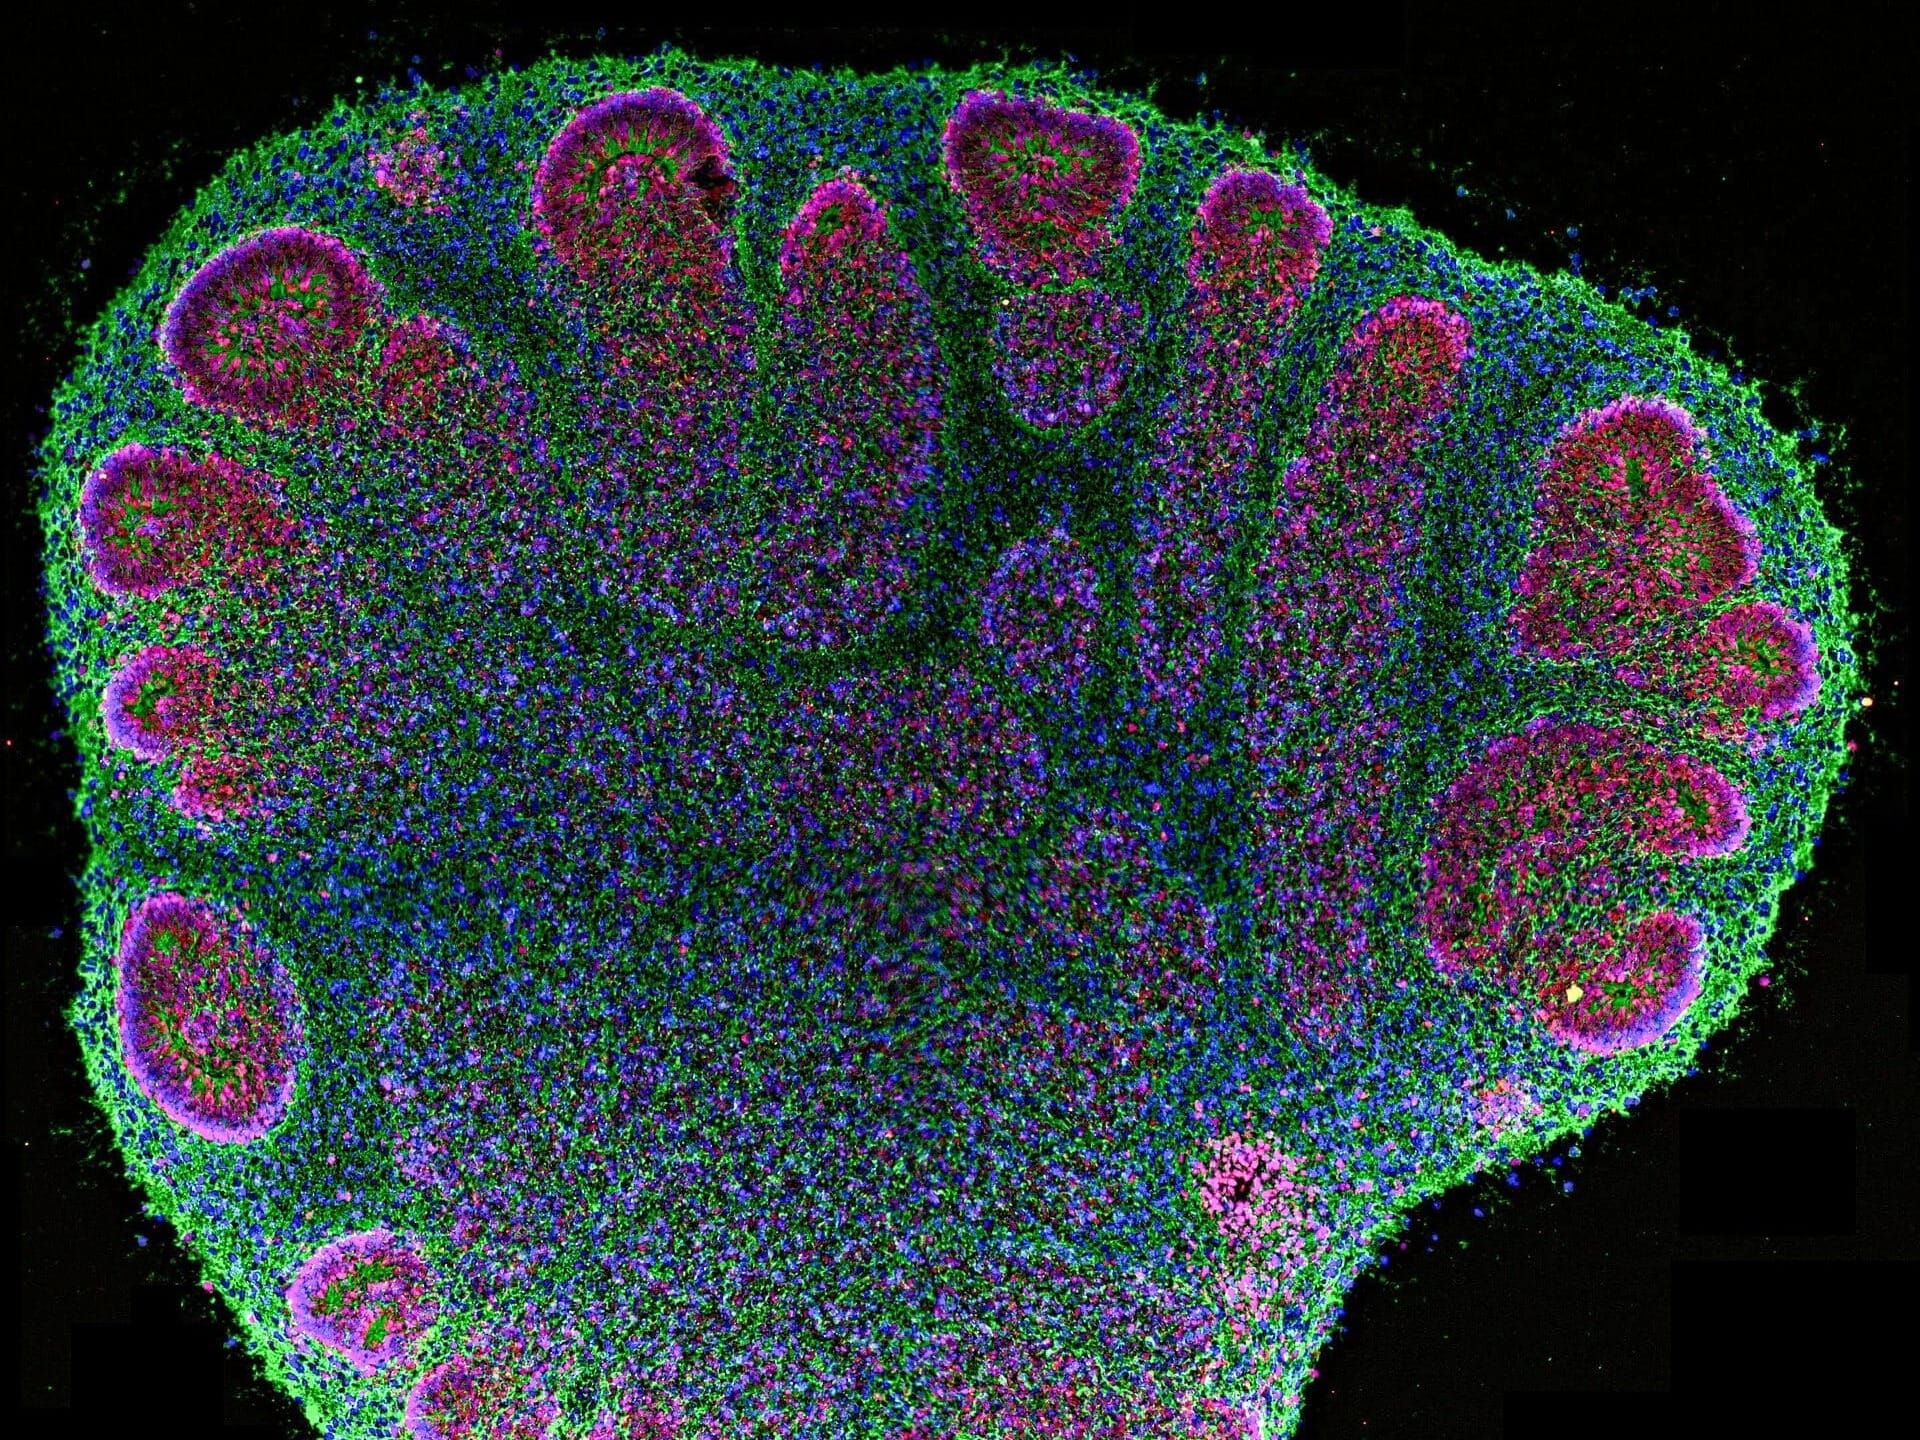
Scientists have made a breakthrough toward the mind-bending goal of creating computers made of brains by demonstrating that human neural tissue can classify letters of the Braille alphabet, according to a study…
Scientists have made a breakthrough toward the mind-bending goal of creating computers made of brains by demonstrating that human neural tissue can classify letters of the Braille alphabet, according to a study published on Friday in Frontiers in Artificial Intelligence . A team transmitted electrical signals corresponding to Braille letters to human brain organoids, which are living neural tissues derived from stem cells. The results revealed that a single organoid, consisting of about 10,000 neurons, could classify the letters with about 61 percent accuracy, while teams of three organoids…
Our analysis an AI-powered espionage campaign targeting government Linux infrastructure with custom malware, web shells, and advanced credential theft.
Built from decades of threat intelligence research, the new resource explains scams from the victims' perspective and tracks emerging forms of cyber crime.
Proofpoint agreed Thursday to acquire Varonis Systems in a cash transaction valued at approximately $6.3 billion, combining two companies that have positioned themselves around a shared bet: that securing data has…
Proofpoint agreed Thursday to acquire Varonis Systems in a cash transaction valued at approximately $6.3 billion, combining two companies that have positioned themselves around a shared bet: that securing data has become the central problem of the AI era. The acquisition pairs two distinct approaches to security. Varonis specializes in data security, mapping where sensitive information sits inside an organization, who can reach it, and how it is actually used. Proofpoint, owned by private equity company Thoma Bravo, built its business around protecting people, blocking phishing, fraud and…
Researchers say that mercenary hackers laced ads with zero-click exploits that installed sophisticated malware on the devices of targeted individuals when they did nothing other than load a website or open an installed…
Researchers say that mercenary hackers laced ads with zero-click exploits that installed sophisticated malware on the devices of targeted individuals when they did nothing other than load a website or open an installed app. The finding, published Thursday by the University of Toronto’s Citizen Lab, said the incident is likely to be the first confirmation of zero-click mercenary spyware delivered through targeted ads. The attacks, which worked on iOS and Android devices, are particularly pernicious because they work without requiring any interaction from the target and are invisible unless…
Threat actors are exploiting a critical command execution flaw, now tracked as CVE-2026-110447, in the Collabora Online - Built-in CODE Server app (richdocumentscode) for Nextcloud.
A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel's live cloud sandboxes, and…
A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel's live cloud sandboxes, and Vercel confirmed it. The flaw, now tracked as CVE-2026-99999 and nicknamed PwnEscape, is in the Linux kernel's networking code, not in any one cloud's setup, so it reaches the shared
Despite the hype around AI agents interacting with websites, few sites bother to supply dedicated reading material for visiting bots. And occasionally, the message directed at visiting bots is an attempt at prompt…
Despite the hype around AI agents interacting with websites, few sites bother to supply dedicated reading material for visiting bots. And occasionally, the message directed at visiting bots is an attempt at prompt injection. While about 10 percent of sites use robots.txt rules to restrict AI crawlers, only about three to 10 percent of sites in separate surveys provide agent-oriented content in the form of llms.txt, a proposed format for exposing website information to AI systems. But a handful of sites have taken to giving AI agents the finger via HTTP headers, the metadata sent with web page…
As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams conducted a comprehensive internal security review. This review resulted in software hardening releases that address…
As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities. These vulnerabilities were found during internal testing and are not known to be actively exploited. To assist customers in patching and streamline the disclosure process, Cisco has grouped these issues by their underlying vulnerability class — Common Weakness Enumeration (CWE) — and assigned a single Common Vulnerabilities and…
Election influence campaigns, particularly ones playing out over social media, are a dime a dozen. Such campaigns – sometimes devised by foreign powers, other times by domestic groups – are often designed to influence…
Election influence campaigns, particularly ones playing out over social media, are a dime a dozen. Such campaigns – sometimes devised by foreign powers, other times by domestic groups – are often designed to influence the U.S. electorate. Fake accounts and online personas are created, networks of propaganda are disseminated and the campaign seeks to nudge American voters into thinking a certain way. Mostly, these efforts are known for getting little to no traction with U.S. audiences. But while social media influence campaigns may not be effective, bad actors continue to adapt their…
Security researchers warned about exploitable vulnerabilities in refrigeration controllers months - and in one case, more than a year - before cyberattacks disrupted hundreds of French supermarkets. Late Sunday night…
Security researchers warned about exploitable vulnerabilities in refrigeration controllers months - and in one case, more than a year - before cyberattacks disrupted hundreds of French supermarkets. Late Sunday night, unknown criminals hacked thousands of controllers, cranking the heat as high as 122°F (50°C), spoiling food and sparking fires across nearly 700 of the country’s supermarkets. France's national cybersecurity agency ANSSI on Monday warned of widespread compromises involving Danfoss refrigeration controllers, and a day later added affected systems from Copeland and its Dixell…
Parts 1 and 2 of this series looked at two pressures facing higher education security teams. First, the threat landscape : universities are dealing with more frequent attacks across complex, distributed environments…
Parts 1 and 2 of this series looked at two pressures facing higher education security teams. First, the threat landscape : universities are dealing with more frequent attacks across complex, distributed environments, while campus-by-campus security can make it harder to share intelligence and coordinate response. Second, the compliance burden: overlapping requirements across FERPA, GLBA, HIPAA, and CMMC make it difficult to establish what data was affected, which reporting obligations apply, and how quickly the institution needs to act. This final part is about what changes when a university…
Powerful zero-click spyware is infected devices worldwide through targeted ads, new research shows — an alarming development in the spread of surveillance technology.
Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week's security stories. The rest gets interesting in different…
Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week's security stories. The rest gets interesting in different ways. A small permission can lead to a big theft. A trusted login can hide the wrong person. Old bugs are finding new victims, familiar tools are being put to strange uses, and
Last week, Secretary of War Pete Hegseth announced the Pentagon would livestream the execution of convicted killer Nidal Hasan. Today, Trump said the execution would move forward but that it wouldn’t be livestreamed …
Last week, Secretary of War Pete Hegseth announced the Pentagon would livestream the execution of convicted killer Nidal Hasan. Today, Trump said the execution would move forward but that it wouldn’t be livestreamed . But the propaganda damage is already done. Experts who watch terrorist spaces online told 404 Media that Hasan is already turning up in memes, videos, and recruitment material for groups like Al Qaeda. Hasan—a former US Army Major who had once attempted to contact Al Qaeda—killed 13 people and injured 32 others at Fort Hood in 2009. He was shot and captured at the scene and…
Welcome to this week’s edition of the Threat Source newsletter. I've been following a lot of (sometimes heated) threads and discussions lately about the current vulnerability landscape. I learned new words/phrases such…
Welcome to this week’s edition of the Threat Source newsletter. I've been following a lot of (sometimes heated) threads and discussions lately about the current vulnerability landscape. I learned new words/phrases such as Summer of Hell (although I'm writing this with 1°C/34°F outside), Vulnpocalypse, Bugmageddon, Bugpocalypse, Breachpocalypse... Let's look at some numbers: We crossed the 70k mark, and it's only the end of September. This has never been seen before — I think we can agree this number is skyrocketing. Also, CVE numbering organically grew into the six-digit range. Check your…