FBI Blames Contractor’s Missed Patch for ShinyHunters Breach
The FBI has removed an Accenture contractor over a data breach that exposed personal information of thousands of bureau employees.
Security Feed
500 articles 47 of 47 sources updated RSS ↗







The FBI has removed an Accenture contractor over a data breach that exposed personal information of thousands of bureau employees.
A ransomware affiliate has turned an AI coding assistant into a channel for running attacks inside enterprise networks. The operator, known as Azazel, combined stolen development credentials, remote command execution…
RMM platforms give MSPs privileged access across customer environments, making their security controls critical to limiting risk. Acronis outlines eight controls MSPs should test when evaluating RMM software, from…
Nikkei says two employee cloud accounts were accessed, with one used to send 9,000 phishing emails
Find, validate, and fix complex business logic flaws with an AI code scanner backed by Wiz Research, operationalized within your existing security program.
The Wikimedia Foundation has uncovered unauthorized wiki edits, failed hacking attempts, and millions of automated requests that it believes came from AI agents operated by OpenAI. Its October 5 disclosure raises…
Hackers are exploiting internet-connected industrial controllers to disrupt US water utilities and other essential services. Recent incidents show that poorly protected equipment can give attackers direct access to…
Multiple Democrat, Republican, and Independent lawmakers have introduced new pieces of legislation that, if passed, would dramatically curb federal agencies’ access to Flock cameras, with the lawmakers referencing…
CERT-UA found fake Cloudflare verification pages that led visitors into a now-familiar ClickFix trap. This time the goal was to infect machines with an infostealer.
It seems that a trend started… I continue my journey discovering more RMM ("Remote Management & Monitoring") tools abused by threat actors! A few days ago, I wrote a diary[1] about ScreenConnect used in the wild. Today…
The IBM subsidiary has also announced its Lightwell Clearinghouse is now available to all customers
GitHub Copilot CLI may reveal developer secrets if it comes across instructions that tell it to do so, depending on the underlying model. The coding agent tool was flagged earlier this year for being susceptible to…
Dell has released security updates for five vulnerabilities in Dell System Update (DSU), including a critical flaw that could let an unauthenticated remote attacker execute code with root privileges. The issues affect…
An alleged leader of Tren de Aragua’s ATM jackpotting activities, Canelon Aguirre was on the FBI’s top 10 most wanted list since March 2026.
Forescout found that just 6% of Internet of Medical Things (IoMT) and 16% of medical OT are capable of supporting post quantum cryptography
Facebook users are reporting receiving a message with a fake Facebook Marketplace listing that has their name as the seller. It works like this. You receive a message (in this case iMessage) asking “Is this still…
A malicious spreadsheet can make LibreOffice and Apache OpenOffice run an attacker's code as soon as the file is opened, security researchers have shown. There is no warning first, of the kind either program shows…
Asos customers have reported receiving a rogue app notification claiming the online clothing retailer's Snowflake instance has been compromised and threatening to leak data. The notification included a link to a…
Citing growing risks posed by more capable and autonomous AI agents, Apple will introduce additional controls.
An unauthorized party abused a private Danish company's legitimate access to the country's Central Population Register (CPR), exposing names, addresses, identification numbers, and other personal information about…
ASOS customers have received a seemingly legitimate push notifications claiming the retailer’s IT systems have been breached through a Snowflake breach
The Wikimedia Foundation says rogue OpenAI agents made unauthorized Wikipedia edits and may have been partially responsible for a May outage.
A coalition of cyber firms and critical infrastructure operators on Tuesday spelled out its views on the tasks that the Cybersecurity and Infrastructure Security Agency should assign federal agencies to protect…
Editor’s note: This research was conducted by Himanshu Anand, an independent cybersecurity researcher ( follow Himanshu on X ). During Cybersecurity Awareness Month, ransomware remains one of the clearest examples of…
The Wikimedia Foundation, which hosts Wikipedia, has confirmed that it has discovered activity by rogue OpenAI agents on its platforms, including unsuccessful efforts to compromise Etherpad, a public note-taking tool…
Domino’s Pizza customers tell us they have received emails saying they account has been accessed by a third party. Domino’s says its internal systems weren’t breached, but that individual accounts were logged into using…
404Media is reporting (alternate link ) that a cyber-weapons arms manufacturer is exploiting a vulnerability in iOS to bypass its automatic reboot security feature. This is the feature that automatically puts an iPhone…
In 2024, MCP (Model Context Protocol) set out to become the USB-C of AI: one standard for connecting models, agents, and IDEs to tools and data. The protocol delivered. Thousands of developers built servers, and…
Significant cybersecurity M&A deals announced by Dragos, IBM, Palo Alto Networks, Kiteworks, and Upwind.
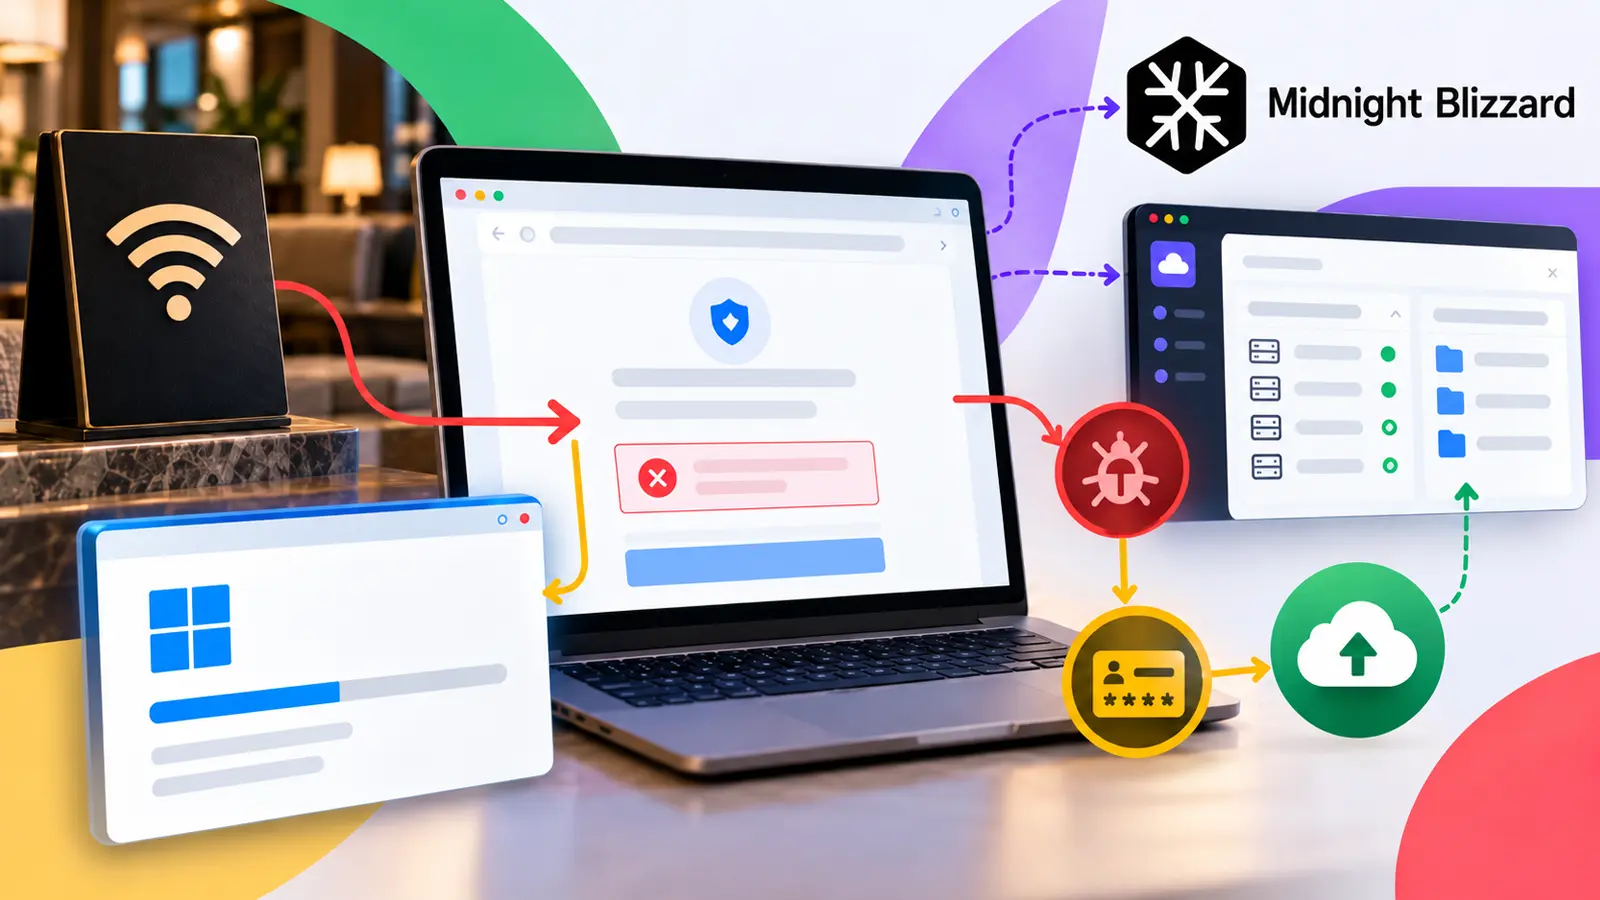
Travelers connecting to hotel Wi-Fi may now face more than an unreliable internet signal. A campaign linked to Midnight Blizzard has turned captive portals, the sign-in pages shown before online access, into a route for…
Since August 2023, attackers have published eight malicious packages as part of the MALFEX supply chain campaign.
Meta and Microsoft are reducing employee use of Anthropic’s Claude AI while pushing their own coding tools, according to an October 5 report by The Information . The changes focus on internal spending and staff…
Analysis of Blinder Tunnel, an Iran-nexus campaign using fake Dubai Airports recruitment lures and GitHub C2 malware to target critical infrastructure.
Hackers abused a company’s lawful access to the CPR system to steal the personal information of registered citizens.
UK education software provider Bromcom has notified customers of a personal data breach affecting its single sign-on (SSO) technology. In a September 24 EduGeek post, an account named Bromcom_Alastair said an…
Over the weekend, Japanese publishing giant Nikkei disclosed that unknown attackers recently breached two employee email accounts and used one to send thousands of phishing emails.
Google has stopped accepting product vulnerability reports through its bug bounty program for its open-source software. The change, in effect since October 1, means researchers can no longer submit security flaws in the…
Report Fraud says cybercrime revenue stemming from account takeover increased 417% annually
ClingSTUN is a Linux backdoor that exploits vulnerable internet-connected devices to give attackers lasting remote access. Rather than simply infecting routers and cameras, it turns compromised equipment into remotely…
The FBI removed an Accenture contractor on October 5, 2026, after a missed security patch led to a data breach exposing sensitive personal details of thousands of employees. According to Reuters , two sources identified…
Companies are pouring time and dollars into security awareness training, but little evidence shows it actually works against social engineering.
Google has detailed six Advanced Protection enhancements for Android 17, targeting sophisticated attacks, scams and unauthorized access. Announced on October 1, 2026, the changes combine stronger restrictions with tools…
An affiliate of The Gentlemen RaaS group ran a parallel leak site during extortion of two dozen victims
A former core infrastructure engineer at an industrial company headquartered in New Jersey was sentenced to 32 months in prison for locking thousands of devices on his employer's network in a ransomware-style attack.
Atlassian has disclosed a critical arbitrary file access vulnerability affecting eight products, including Jira, Confluence, and Bitbucket. Tracked as CVE-2026-21589, the flaw has a CVSS score of 9.3. It lets…
The word Conti struck fear in IT departments across the world. It's a type of ransomware that you hope to never come across. Like most ransomware gangs, the Conti group fell apart. But what's special about this story is…
A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in each product's web application root directory. The attacker must…
The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of personal details of thousands of bureau employees. That's…
Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark's national population register, the country's digitalization…
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser's cache. "Instead of downloading and executing remote payloads like the typical…
Atlassian has told its users to patch its datacenter products, pronto, to prevent attackers accessing their files. The Australian collaborationware company on Monday sent users an email that opens with the words “Action…
Several mysteries surround what appeared to be an unauthorized push notification sent to customers of London-based clothing company ASOS.
Linux KVM, the hypervisor favoured by hyperscale clouds, apparently has a full VM escape bug. That nasty news came from security researcher Paulos Yibelo, who on X shared a screenshot of a bug bounty award he won for…
Citrix customers just got through back-to-back weekends filled with varying levels of uncertainty and worry, as yet another actively exploited zero-day vulnerability was discovered in Citrix NetScaler products…
OpenAI is preparing to add invisible watermarks to text generated by ChatGPT and Codex in the European Union.
Beyond the potential misuses of its services, Wikimedia said activity by AI agents can be a drain on web platforms that are already operating with limited resources.
The Linux backdoor exploits 24 known flaws to compromise IoT devices and uses legitimate public STUN servers to obscure communications.
The attackers just keep coming after Citrix NetScaler appliances, as both the feds and private security researchers warn that someone found - and has already exploited - yet another Citrix bug before it had a patch…
Hackers are actively scanning for a Rejetto HFS weak signing key vulnerability, tracked as CVE-2026-61500, that allows session forgery, account takeover, and remote code execution (RCE).
Saif al-Din Khader is cooperating with the FBI, reports said, as the bureau responds to a massive breach that exposed employee data.