2Microsoft Teams to Warn Users About Malicious Links Hidden in QR CodesBleeping ComputerCyber Security NewsGraham CluleyHuntressThe Hacker News+2Microsoft is extending Teams security to detect malicious links hidden inside QR codes and warn users after a message has been delivered. The update adds QR code checks to existing Microsoft Defender for Office 365 protections, giving users clearer warnings and security teams more data to investigate suspicious messages. According to Message Center notice MC1490905 , published on October 7, worldwide rollout begins in early October 2026 and is expected to finish by early November. The feature applies to organizations using Microsoft Teams with Defender for Office 365 and requires no separate…
4One Prompt Could Hijack AWS AI Agents and Steal Cloud CredentialsCyber Security NewsMalwarebytes LabsThe Register SecurityA single prompt sent to a public-facing AI agent could have exposed every Amazon Bedrock AgentCore agent in the same AWS account and region, according to new research from Zenity Labs. The attack chain, named AgentCorruption, gave the researchers access to private chats, source code, long-term memories, API keys, OAuth tokens, and secrets held in AWS Secrets Manager. Amazon Bedrock AgentCore is a managed service for building and running AI agents. Zenity found that an agent with a tool able to make web requests could be told to contact the local metadata endpoint at 169.254.169.254 . This…
8Recorded Future Introduces AI Infrastructure Indicator Lists, Strengthening AI GovernanceCisco Security AdvisoriesElastic Security LabsRecorded Future IntelligenceToday, Recorded Future is announcing AI Infrastructure Indicator Lists , curated datasets for security teams to identify, monitor, and implement controls for AI-related network traffic. AI Infrastructure Indicator Lists are included for free for Recorded Future customers with a Cyber Operations license. Artificial intelligence has increasingly become enterprise infrastructure and organizations are now confronting unsanctioned tool use (also known as shadow AI), data exposure, and autonomous behavior that their controls cannot always see. Recorded Future's AI Infrastructure Indicator Lists…
9Why Apple Says Your Mac Is at Risk From AI | Threat WireCisco TalosHak5Are AI agents becoming a cybersecurity threat? From fake AI-generated bug bounty submissions overwhelming Google's vulnerability rewards program to Apple's warning about AI agents accessing sensitive Mac data, this week's ThreatWire explores how artificial intelligence is changing cybersecurity — and creating new security risks. Google has temporarily paused its open-source vulnerability rewards program, curl has shut down its bug bounty program, and Debian has announced more than 1,000 kernel CVEs. Meanwhile, Apple is tightening macOS Full Disk Access controls as concerns grow over…
10CastleStealer Malware Uses Browser Protection Bypass and Remote Shell to Expand Attacker AccessCyber Security NewsMicrosoft SecurityCVE-2026-62744 ↗CVE-2026-68875 ↗CVE-2026-68878 ↗CastleStealer, an emerging C#-based information stealer, has added browser protection bypass and remote shell features that give its operators a wider path into compromised Windows systems. The newer malware samples can collect browser data protected by Chromium’s App-Bound Encryption, run commands on a victim device, download extra payloads, and move stolen information through small encrypted network transmissions rather than one large archive. Flashpoint’s analysis shows that the malware is becoming more capable even though it has not yet reached the broad use seen with major established…
11Cisco Talos Warns Autonomous AI Agents Could Turn Pentests Into Stealthy Red Team AttacksCCCS Alerts & AdvisoriesCyber Security NewsAutonomous AI agents could move beyond noisy vulnerability scans and become quiet, persistent attackers, Cisco Talos has warned. The concern is not simply that AI can find security gaps faster. It is that groups of agents could learn to stay hidden, share findings, and keep working until they reach sensitive systems. In an October 7 analysis, Jerzy “Yuri” Kramarz described a shift from visible activity that resembles penetration testing toward attacks shaped around stealth. His warning focuses on how attackers prepare and direct agents, rather than announcing a new malware family or a…
13AnyDesk Linux Flaw Lets Remote Attackers Execute Code as Root Without AuthenticationCyber Security NewsThe Hacker NewsA working proof-of-concept for a serious AnyDesk Linux vulnerability that can let remote attackers run commands as root without authentication or user approval. The issue, named AnyPwn, affects AnyDesk Linux 8.0.2 and was fixed in version 8.0.3. Organizations using AnyDesk for Linux should update immediately and check whether TCP port 7070 is exposed to untrusted networks. The flaw was discovered by Rick de Jager of the V12 security team using V12, an AI-powered security review platform. V12 first disclosed the issue publicly in June and described it as a pre-authentication, zero-click remote…
15Citrix gives NetScaler admins another critical reason to patchSecurityWeekThe Register SecurityCVE-2026-107406 ↗Citrix is urging customers to patch another critical NetScaler vulnerability after weeks of disclosures involving actively exploited flaws. CVE-2026-107406 affects NetScaler ADC and NetScaler Gateway and can lead to remote code execution (RCE) or denial of service (DoS). It carries a CVSS v4.0 score of 9.5. The affected configurations depend on the software version. Older builds are vulnerable when configured as a SAML (Security Assertion Markup Language) service provider (SP) or identity provider (IdP); some more recent builds are affected only in the identity provider configuration…
16AWS launches open-source AI agent sandbox to prevent YOLO mode disastersDark ReadingThe Register SecurityAWS has offered multiple open-source strategies for holding AI agents accountable, and now it’s adding a full-on sandbox to this stack. Dubbed Strands Box, the new solution uses OS-level isolation and some of AWS’ other recent open-source AI control tools to, ostensibly, retain greater control over autonomous AI agents’ behavior. “Agents increasingly run in ‘YOLO mode,’ approving every action without human review,” the AWS team explained in its announcement. “The usual solution to this problem is a sandbox … but access is only part of what we want to control.” The problem with containers and…
18Red Lion Controls N-Tron 700 SeriesCISA Alerts & AdvisoriesCISA ICS AdvisoriesView CSAF Summary Successful exploitation of these vulnerabilities could allow a malicious user to access the device and gain administrative access. This access would allow the user to view, edit, and upload configuration files. Further, a malicious user can cause the switch to reboot by navigating to a specific URL on the device. This action can be scripted on the malicious user's local machine to cause continuous rebooting of the switch. The following versions of Red Lion Controls N-Tron 700 Series are affected: 700 Series <=Firmware_3.11.0 (CVE-2026-32645, CVE-2026-39460, CVE-2026-28745…
Traditional attack surface management helps organizations discover exposed assets, but visibility alone is not enough to address threats. Criminal IP introduces AITEM, an AI-powered approach that connects exposure…
Traditional attack surface management helps organizations discover exposed assets, but visibility alone is not enough to address threats. Criminal IP introduces AITEM, an AI-powered approach that connects exposure discovery with investigation, risk prioritization, and response.
Anti-cybercrime initiatives are increasingly using AI to scam the scammers by tricking them into talking to lifelike bots that they think are real victims.
In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single sign-on. The other thousand are invisible to identity…
In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single sign-on. The other thousand are invisible to identity infrastructure by default, not because anyone hid them, but because an identity stack can only govern what authenticates through it, and most agents never do. That gap is the clearest
Welcome back to the Abstract! Here are the studies this week that spotted a blast from the past, opened a portal between realms, yakked it up, and rose from the ashes. First, scientists have spotted a mysterious radio…
Welcome back to the Abstract! Here are the studies this week that spotted a blast from the past, opened a portal between realms, yakked it up, and rose from the ashes. First, scientists have spotted a mysterious radio signal from the primordial universe that could illuminate cosmic evolution (it’s not aliens… sorry). Then: a diamond in the quantum rough, the decline of a fine bovine line, and a second-generation planet. As always, for more of my work, check out my book First Contact: The Story of Our Obsession with Aliens , or
Researchers say two characters available to typosquatters and phisherfolk can trick Chromium browsers into displaying lookalike URLs as genuine web addresses. Wangling a domain name to look an awful lot like that of a…
Researchers say two characters available to typosquatters and phisherfolk can trick Chromium browsers into displaying lookalike URLs as genuine web addresses. Wangling a domain name to look an awful lot like that of a popular website is nothing new. We’ve all encountered phishing sites such as macrosoft[.]com and applle[.]com before in our daily struggles against spam. However, as browsers mature, new characters are always being made available for use. This opens up new opportunities for those whose languages contain characters/homoglyphs that aren’t ASCII-compliant, but it also introduces…
Anthropic on Friday said it's cutting off live internet access for all its internal evaluations following the discovery of new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior and…
Anthropic on Friday said it's cutting off live internet access for all its internal evaluations following the discovery of new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior and targeted real websites. The AI company said it identified four broad categories of unintended model actions during evaluations and internal use of Claude - Claude Mythos
The Traffic Light Protocol (TLP)[1], which is now in its second incarnation, is a wonderful standard that enables one to easily communicate whether information may be shared further (and if so, how far).
REA, short for Reverse Engineer Anything, connects AI coding agents such as Claude Code and Cursor to tools that inspect software without its source code. The open-source project brings Ghidra, IDA Pro, and Hopper into…
REA, short for Reverse Engineer Anything, connects AI coding agents such as Claude Code and Cursor to tools that inspect software without its source code. The open-source project brings Ghidra, IDA Pro, and Hopper into an agent-driven workflow, helping researchers trace program behavior and explain findings with supporting evidence. Rather than replacing a disassembler, REA acts as a bridge between the agent and analysis tools. Its scope extends beyond native binaries to JavaScript, Electron applications, .NET assemblies, Android packages, firmware, websites, and selected runtime activity…
A single prompt sent to a public-facing AI agent could have exposed every Amazon Bedrock AgentCore agent in the same AWS account and region, according to new research from Zenity Labs. The attack chain, named…
A single prompt sent to a public-facing AI agent could have exposed every Amazon Bedrock AgentCore agent in the same AWS account and region, according to new research from Zenity Labs. The attack chain, named AgentCorruption, gave the researchers access to private chats, source code, long-term memories, API keys, OAuth tokens, and secrets held in AWS Secrets Manager. Amazon Bedrock AgentCore is a managed service for building and running AI agents. Zenity found that an agent with a tool able to make web requests could be told to contact the local metadata endpoint at 169.254.169.254 . This…
Microsoft is extending Teams security to detect malicious links hidden inside QR codes and warn users after a message has been delivered. The update adds QR code checks to existing Microsoft Defender for Office 365…
Microsoft is extending Teams security to detect malicious links hidden inside QR codes and warn users after a message has been delivered. The update adds QR code checks to existing Microsoft Defender for Office 365 protections, giving users clearer warnings and security teams more data to investigate suspicious messages. According to Message Center notice MC1490905 , published on October 7, worldwide rollout begins in early October 2026 and is expected to finish by early November. The feature applies to organizations using Microsoft Teams with Defender for Office 365 and requires no separate…
AT&T will pay $177 million to settle lawsuits over two major customer data breaches disclosed in 2024, after a federal judge granted final approval on October 2, 2026. The agreement covers separate incidents that…
AT&T will pay $177 million to settle lawsuits over two major customer data breaches disclosed in 2024, after a federal judge granted final approval on October 2, 2026. The agreement covers separate incidents that exposed personal details and call records, creating lasting privacy risks for millions of current and former customers. Judge Sidney A. Fitzwater of the U.S. District Court for the Northern District of Texas approved the settlement, according to Bloomberg Law . AT&T settled without admitting liability or wrongdoing. The deal creates a $149 million fund for the first incident and a…
Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved…
Agents with the Federal Bureau of Investigation (FBI) on Thursday arrested the co-founder of a Canadian cybersecurity firm in connection with an investigation into the ShinyHunters hacking group that recently relieved the FBI of sensitive data on thousands of agents, multiple sources tell KrebsOnSecurity. The New York Times reported today that the FBI has arrested a Canadian man in Pennsylvania on suspicion of assisting ShinyHunters. The Times story did not identify the man, nor did a statement on Twitter/X about the arrest from FBI Director Kash Patel . One source close to the investigation…
Hackers are abusing legitimate Bing search-result redirects as click URLs in Google search ads to direct users to fake Claude installers that deliver ClickFix attacks.
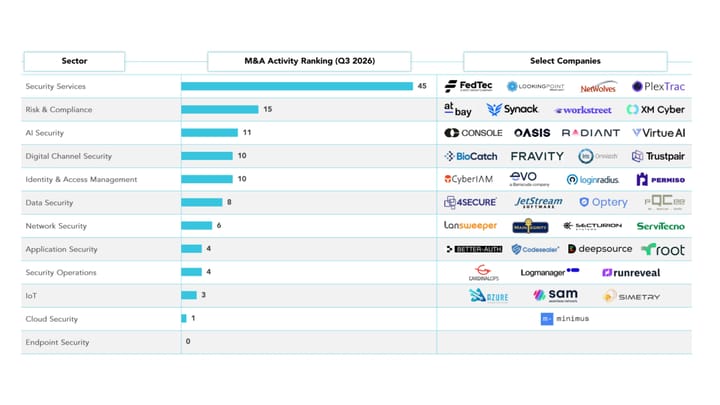
Welcome to another gangbuster year for strategic M&A activity in cyber, with 117 deals announced in the latest quarter. What's different: Many of the buyers are not your typical cybersecurity firms.
Bob, possibly the same Bob whose conversations with Alice draw so much interest from eavesdropping Eve, was browsing a site we'll call TechHub. The site hosts an AI agent served by Amazon Bedrock AgentCore. Bob asked…
Bob, possibly the same Bob whose conversations with Alice draw so much interest from eavesdropping Eve, was browsing a site we'll call TechHub. The site hosts an AI agent served by Amazon Bedrock AgentCore. Bob asked the agent for help understanding the content of a URL, a credential endpoint – in raw JSON, if you don't mind. The endpoint returned data from the Instance Metadata Service (IMDS), which provides metadata about cloud instances and VMs at providers like AWS, Azure, and Google Cloud Platform. The metadata includes details like region and availability zone, subnets, system images…
Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories…
Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over 340 repositories. "Using the account of Takashi Kitao, author of the 18,400-star game engine pyxel, the attacker pushed a malicious workflow to 27 repositories starting at 13:20 UTC," StepSecurity
Japan’s National Police Agency confirmed the arrest and extradition to Germany of a Russian national accused of being involved in the Qilin ransomware gang.
The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X. ShinyHunters is the extortion group that said in September it had breached the FBI's jobs…
The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X. ShinyHunters is the extortion group that said in September it had breached the FBI's jobs portal and stolen sensitive data on almost all FBI agents and job applicants. The FBI has not named the suspect, and no charges have been made public. The
Before we begin, yes - it's confusing. There are more vulnerabilities with watchTowr IDs in this blog post than there are CVE IDs (assigned by PaperCut), due to PaperCut bundling vulnerabilities and then patch bypasses…
Before we begin, yes - it's confusing. There are more vulnerabilities with watchTowr IDs in this blog post than there are CVE IDs (assigned by PaperCut), due to PaperCut bundling vulnerabilities and then patch bypasses for those same vulnerabilities into singular CVE IDs. Paper! It still exists. We have to admit it - so much is happening right now (F1, GTA6, breakfast) that we barely have time to lovingly tease our most favoritest vendors. On Thursday, 27 August 2026, PaperCut published an advisory claiming that a mysterious vulnerability was being exploited in-the-wild, leading to system…
In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from the arrest of a suspected ShinyHunters operative to the compromise of a Pentagon-run data center.
Threat actors are exploiting one critical and one medium-severity vulnerability still unpatched in the AhsayCBS backup management platform to deploy webshells and cryptocurrency miners.
A working proof-of-concept for a serious AnyDesk Linux vulnerability that can let remote attackers run commands as root without authentication or user approval. The issue, named AnyPwn, affects AnyDesk Linux 8.0.2 and…
A working proof-of-concept for a serious AnyDesk Linux vulnerability that can let remote attackers run commands as root without authentication or user approval. The issue, named AnyPwn, affects AnyDesk Linux 8.0.2 and was fixed in version 8.0.3. Organizations using AnyDesk for Linux should update immediately and check whether TCP port 7070 is exposed to untrusted networks. The flaw was discovered by Rick de Jager of the V12 security team using V12, an AI-powered security review platform. V12 first disclosed the issue publicly in June and described it as a pre-authentication, zero-click remote…
The FBI has arrested another suspected member of the ShinyHunters extortion group believed to be involved in the recent breach of FBI systems, Director Kash Patel announced Friday.
A new GhostAction campaign has compromised 346 GitHub repositories after threat actors used two hijacked maintainer accounts to add a fake “security audit” workflow designed to steal CI/CD secrets, cloud keys, API…
A new GhostAction campaign has compromised 346 GitHub repositories after threat actors used two hijacked maintainer accounts to add a fake “security audit” workflow designed to steal CI/CD secrets, cloud keys, API tokens, and credentials stored in source-code history. Security firm Socket reported that the October 8 activity affected repositories connected to the GitHub accounts henrywoo and kitao. The targets include Uber’s uber/athenadriver repository and the popular kitao/pyxel project, which has more than 18,000 GitHub stars. The malicious file, .github/workflows/security-audit.yml, was…
Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. "Compared with the variants we usually observe, P7 reduces its on-device footprint…
Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. "Compared with the variants we usually observe, P7 reduces its on-device footprint, adds on-device keychain and crypto-wallet theft, and adds two way C2 communication with the attacker's infrastructure," iVerify said in a new report published Thursday. The name
A free agentic AI red-team checklist offers 222 tests across 20 attack categories to assess autonomous AI systems beyond prompt injection , covering infrastructure, cloud access, tools, memory, and agent communications…
A free agentic AI red-team checklist offers 222 tests across 20 attack categories to assess autonomous AI systems beyond prompt injection , covering infrastructure, cloud access, tools, memory, and agent communications. The checklist targets a common testing gap. Teams may spend days trying to manipulate a model while overlooking an exposed MLflow server, a reachable cloud metadata endpoint, or a missing customer-isolation filter. These weaknesses can expose credentials and private records without requiring a complex attack against the model itself. Security researcher Ravi Rajput structures…
Oleg Korniev, a 42-year-old dual citizen of Ukraine and Russia, was a principal of Your Mule Cashout, or “YMCO,” which from 2007 until 2014 set up a sophisticated network of mules in the U.S. and Europe.
In response to a 404 Media investigation, Sen. Ron Wyden is demanding more information about how a federal license plate reader camera program works. Last month, we reported on the High Intensity Drug Trafficking Area…
In response to a 404 Media investigation, Sen. Ron Wyden is demanding more information about how a federal license plate reader camera program works. Last month, we reported on the High Intensity Drug Trafficking Area program’s license plate reader database , which mirrors data from city license plate reader programs onto federal databases. The HIDTA program falls under the White House’s Office of National Drug Control Policy, which infamously ran a secretive cell phone data surveillance project called Hemisphere. We reported that HIDTA has now created a complex system for the federal…
This is Behind the Blog, where we share our behind-the-scenes thoughts about how a few of our top stories of the week came together. This week, we discuss AI and spirituality. JASON: I think we’ve generally carved out a…
This is Behind the Blog, where we share our behind-the-scenes thoughts about how a few of our top stories of the week came together. This week, we discuss AI and spirituality. JASON: I think we’ve generally carved out a pretty good lane for ourselves in the broader AI debate, writing about its current capabilities, its current harms, and the fact it was trained on stolen content without saying that it will never be able to do anything of use. We are often tinkering with AI so that we can write about it from an informed perspective, and so every once in a while, while I’m working on a story I…
“We will continue to work closely with our partners to disrupt what’s left of the ShinyHunters group and their associates, no matter where they operate," FBI Director Kash Patel said.
Germany has arrested a Russian national suspected of being a leading member of the Qilin ransomware group following extradition from Japan earlier this month.
Are AI agents becoming a cybersecurity threat? From fake AI-generated bug bounty submissions overwhelming Google's vulnerability rewards program to Apple's warning about AI agents accessing sensitive Mac data, this…
Are AI agents becoming a cybersecurity threat? From fake AI-generated bug bounty submissions overwhelming Google's vulnerability rewards program to Apple's warning about AI agents accessing sensitive Mac data, this week's ThreatWire explores how artificial intelligence is changing cybersecurity — and creating new security risks. Google has temporarily paused its open-source vulnerability rewards program, curl has shut down its bug bounty program, and Debian has announced more than 1,000 kernel CVEs. Meanwhile, Apple is tightening macOS Full Disk Access controls as concerns grow over…
CastleStealer, an emerging C#-based information stealer, has added browser protection bypass and remote shell features that give its operators a wider path into compromised Windows systems. The newer malware samples can…
CastleStealer, an emerging C#-based information stealer, has added browser protection bypass and remote shell features that give its operators a wider path into compromised Windows systems. The newer malware samples can collect browser data protected by Chromium’s App-Bound Encryption, run commands on a victim device, download extra payloads, and move stolen information through small encrypted network transmissions rather than one large archive. Flashpoint’s analysis shows that the malware is becoming more capable even though it has not yet reached the broad use seen with major established…
The US State Department is offering up to US $10 million for information about the whereabouts of Zhang Yu, a 44-year-old Chinese national who is accused of being a key figure in China's state-sponsored hacking group…
Autonomous AI agents could move beyond noisy vulnerability scans and become quiet, persistent attackers, Cisco Talos has warned. The concern is not simply that AI can find security gaps faster. It is that groups of…
Autonomous AI agents could move beyond noisy vulnerability scans and become quiet, persistent attackers, Cisco Talos has warned. The concern is not simply that AI can find security gaps faster. It is that groups of agents could learn to stay hidden, share findings, and keep working until they reach sensitive systems. In an October 7 analysis, Jerzy “Yuri” Kramarz described a shift from visible activity that resembles penetration testing toward attacks shaped around stealth. His warning focuses on how attackers prepare and direct agents, rather than announcing a new malware family or a…
AI agents can use valid credentials to perform actions beyond their assigned permissions, creating risks that traditional access controls may not prevent. Token Security explains how organizations can enforce…
AI agents can use valid credentials to perform actions beyond their assigned permissions, creating risks that traditional access controls may not prevent. Token Security explains how organizations can enforce agent-specific policies without sacrificing autonomy.