Security Feed
Cybersecurity news & advisories
500 articles 46 of 46 sources updated RSS ↗




Latest
953 Online Stores Infected in Long-Lasting Malware Campaign
Small loader code injected into the stores served a payload to visitors or did nothing to avoid detection.
Microsoft Issues Emergency Patch Update for Critical .NET Buffer Overflow Flaw
Microsoft’s updates address two newly disclosed vulnerabilities in the .NET developer platform, as well as flaws not fully addressed in an earlier release
UK Biobank back online soon, months after someone tried to sell 500k people's data on Alibaba
UK Biobank (UKB) says its platform is now "secure" and that academics will soon regain access, months after a major data leak of volunteer health data. The charity, which runs the eponymous research project and…
Popular AI tool LiteLLM says unrevoked key allowed hackers to target users
LiteLLM, an open-source tool widely used by artificial intelligence developers, said a key accidentally exposed in May was behind a supply-chain attack that is believed to have hit tens of thousands of users last week.
Dutch Police Arrest Two Over NFC Relay Attacks That Drained $400,000+ From Bank Accounts
The individuals called victims and persuaded them to install an app and scan their credit cards to loot their bank accounts.
Patient records exposed in Quest breach: What you need to know
Quest Diagnostics has confirmed that an unauthorized party accessed a system healthcare providers use to order laboratory tests and view results, affecting personal information and patient records. Quest is a major US…

Between alerts: What Attackers Do in the Spaces Ordinary Detection Misses
Every SOC struggles with a pile of alerts. Very few of those alerts explain how an attack started or how it progressed. Network data, like that from a network detection and response (NDR) platform, connects individual…
Bias in Qwen3-Coder Model
Interesting research : TL;DR: Chinese AI models now sit inside Western products, and some carry geopolitical triggers: tell the model who the code is for, and the security of what it writes changes. For the first time…
Britain bets big on AI to defend against the threats AI is helping create
The UK government is throwing £130 million at AI-powered cyber defenses, including plans to deploy autonomous AI agents across critical infrastructure to hunt down security flaws before attackers get there first. The…
Kali Linux 2026.3 released with 6 new tools, desktop updates
Kali Linux has released version 2026.3, its third release this year, featuring six new hacking tools, desktop environment improvements, refreshed build scripts, and more.
Kali Linux 2026.3 Released With 6 New Penetration Testing Tools and Linux Kernel 7.1
Kali Linux 2026.3 has been released as the third Kali update of 2026, bringing six new penetration testing tools, Linux kernel 7.1.5, KDE Plasma 6.7, refreshed image-building scripts, and a large set of Kali NetHunter…
Node2Shell: Brotli Flaw Triggers Patching Across Microsoft, Node.js, Python Packages
An out-of-bounds write in Google’s Brotli decoder affects Node.js, .NET, PowerShell, and Python packages, and can lead to code execution.
Blue Initiative Offers Maritime Sector Dedicated Vulnerability Database
Blue Initiative launches a new vulnerability database for IT and OT CVEs relevant to the maritime industry
Deploying AI agents securely: how Kaspersky products mitigate AI threats
Introduction AI agents and associated tooling are becoming increasingly common in corporate infrastructure. Agents can perform a range of actions with the user’s privileges, such as accessing data, running commands, and…

Top 10 Best Data Access Governance Tools in 2026 [Ranked & Scored]
Ask any enterprise “who can read the M&A folder?” and watch the room go quiet effective access is buried under nested groups, inherited shares, service-account grants, and warehouse roles nobody has reviewed since the…
uCreator Android Spyware Can Steal Telegram 2FA Passwords and Clone WeChat Accounts
A rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two apps, researcher Ovi found. It only reaches people who install one of these…

OpenSSL 4.1.0 Released With DTLS 1.3 and Post-Quantum Security Improvements
OpenSSL has released version 4.1.0, bringing DTLS 1.3 support, faster cryptographic operations, and new tools for developers building secure network services. Published on October 23, the update is a feature release…

Top 10 Best Sensitive Data Discovery Tools in 2026 [Ranked & Scored]
Every data-security control inherits the same dependency: an inventory someone actually believes. Discovery is where that inventory comes from and in 2026 the job has hardened, because shadow data multiplies in SaaS and…

Top 10 Best Hardware Security Modules (HSM) in 2026 [Ranked & Scored]
Every root of trust ends in an HSM the tamper-resistant hardware where CA keys, payment keys, and code-signing keys live beyond software’s reach. Two forces reshape the 2026 shortlist: FIPS 140-3 transitions retiring…
Looking for a Language [Guest Diary], (Wed, Oct 21st)
[This is a Guest Diary by Jeffray Spence, an ISC intern as part of the SANS.edu BACS program]
PHP2Shell security flaws now sucessfully exploited in the wild
Two critical RCE vulnerabilities (CVE-2026-109618 and CVE-2026-109619), collectively tracked as PHP2Shell, have been successfully exploited in the wild.
PHP Publishes Mitigation Advice for New RCE Flaw
PHP warns of critical RCE vulnerability CVE-2026-115560, but says limited exploit conditions mean most deployments are unlikely to be affected
Mythos 5 Ignored Real-World Harm in July Attack
The model engaged in severe overreach and dishonesty, creating fake identities and submitting malicious code on GitHub.
Microsoft 365 Token-Replay Attacks Compromise 97 Accounts at 79 Organizations
Cybersecurity researchers have disclosed a Microsoft 365 campaign that has been observed leveraging an adversary-in-the-middle (AitM) relay to capture sign-in sessions and then replay the stolen tokens to break into…
Gheist Uses Stolen GitHub Tokens to Steal Private Repository Secrets via Actions Logs
An automated campaign is using stolen GitHub tokens to plant workflows that print a repository's secrets into its GitHub Actions logs, which the attackers then download before deleting the runs. The attacks have…
A week in security (October 19 – October 25)
Last week on Malwarebytes Labs: Resident Evil maker Capcom warns of phishing after 11.7 million records exposed Crime Stoppers chapter freezes tips after breach breaks anonymity promise Facebook’s misleading privacy…
HTTP2Shell Vulnerability Extends Beyond HTTP, Affecting .NET, FFmpeg, ClickHouse, and Apache Arrow
The HTTP2Shell vulnerability reaches beyond web traffic, with new research showing how the same Brotli decoder flaw (CVE-2026-111497) can disrupt .NET applications, FFmpeg media processing, ClickHouse servers, and…

Microsoft Authenticator Flaw Lets Malicious Android Apps Steal Account Tokens With Zero Permissions
Microsoft patched high-severity flaw CVE-2026-80097 (CVSS 8.6) in Authenticator for Android, allowing malicious apps with no declared permissions to steal work account access tokens due to improper authentication in its…

India’s Film Sensor Board Data Breach – Unreleased Scripts, 500+ Film Titles Exposed
India’s Central Board of Film Certification (CBFC) is investigating a reported data breach involving confidential documents linked to more than 500 film titles. The exposed records reportedly include shooting scripts…

Malicious File in Downloads Folder Tries to Trick AI Coding Agent Into Installing Malware
A malicious instruction file sitting in a developer's Downloads folder tried to make their AI coding agent install a known-malicious npm package, security firm Forever Security said in a report published last week. The…
Work to protect DNS from quantum decryption attacks is speeding up
Internet governance bodies are likely to accelerate work to prepare the domain name system (DNS) so it can remain secure once quantum computers can challenge conventional encryption. John Crain, ICANN’s chief technology…

Hacker Exploits Critical PHP2Shell Flaws to Win $2,000 Bitcoin Challenge, Releases PoC
A security researcher known online as killa has won a public Bitcoin challenge by using two critical PHP flaws to reach a test server. The winning run took 19.28 hours. The prize pot was 0.02511679 BTC, worth $2,021.22…
YARA-X 1.22.0 Release, (Sun, Oct 25th)
YARA-X's 1.22.0 release brings 11 improvements and 9 bugfixes.
Gheist: Attempted Scaled Abuse of Stolen GitHub Tokens Stumbles
An automated campaign is planting secret-dumping workflows in every repository that stolen GitHub tokens can reach. It uses no C2 server, is actively evolving, and has been significantly disrupted by recent GitHub…

Unpatched Tailscale SSH Flaws Could Let a Hacked Device Reach Root on Other Servers
A single hacked device on a Tailscale network can be used to gain root access to other servers it can reach, according to a security researcher who published the findings this week. The attack requires two things…

PHP2Shell Exploitation Attempts Continue Amid Suspected N. Korea Global Scanning Activity
In an update, Palo Alto Networks Unit 42 said it's retracting its earlier assessment that the post-compromise activity targeting the European government agency involved the exploitation of the PHP2Shell flaws. "What…
AI coding agents hijacked using AGENTS.md file in Downloads folder
Researchers found a malicious AGENTS markdown instruction file in a customer's Downloads folder that tricked an AI coding agent into installing a rogue npm package.
Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability
Detect and mitigate CVE-2026-111497, a critical Brotli decoder vulnerability enables remote code execution.

Tailscale SSH Flaws Could Let Hackers Gain Root Access Across Servers From One Compromised Device
A new security report warns that Tailscale SSH has flaws that could let a hacker move from one compromised device to root access on other servers. Tailscale SSH lets approved devices log in to each other over a private…
Former Unit 8200 Officers Raise $34 Million for Agentic SecOps Startup Mave
Founded in 2025 by Unit 8200 alumni, Tel Aviv-based Mave uses AI agents to investigate alerts across existing security stacks.

OpenAI AI Agents Demonstrate VM Escapes and Secret Cross-Sandbox Communication
OpenAI has announced plans to conduct frontier model training with no live internet access, as it resumes reinforcement learning (RL) training and internal inference of its most advanced AI models. "Based on the current…
Cisco Informational for Emergency Distrust of eMudhra Root and Intermediate Certificate Authorities
Between October 17 and October 20, 2026, a critical security compromise involving Certificate Authorities that are managed by eMudhra was uncovered. A security researcher demonstrated that the private keys for eight…
BlackX UEFI bootkit exploits Baton Drop flaw to bypass Secure Boot
A new UEFI bootkit named BlackX, deployed in an espionage campaign in early 2026, exploited the old Baton Drop vulnerability to bypass Secure Boot and load a malicious driver designed to interfere with security…
Autonomous attack agent in 'Skynet mode' hijacks other models to carry out its evil deeds
Threat actors built an AI agent designed to hijack exposed AI models to run autonomous attacks, with instructions allowing it to carry out up to 100,000 steps without human approval. The Symantec Threat Hunter Team…
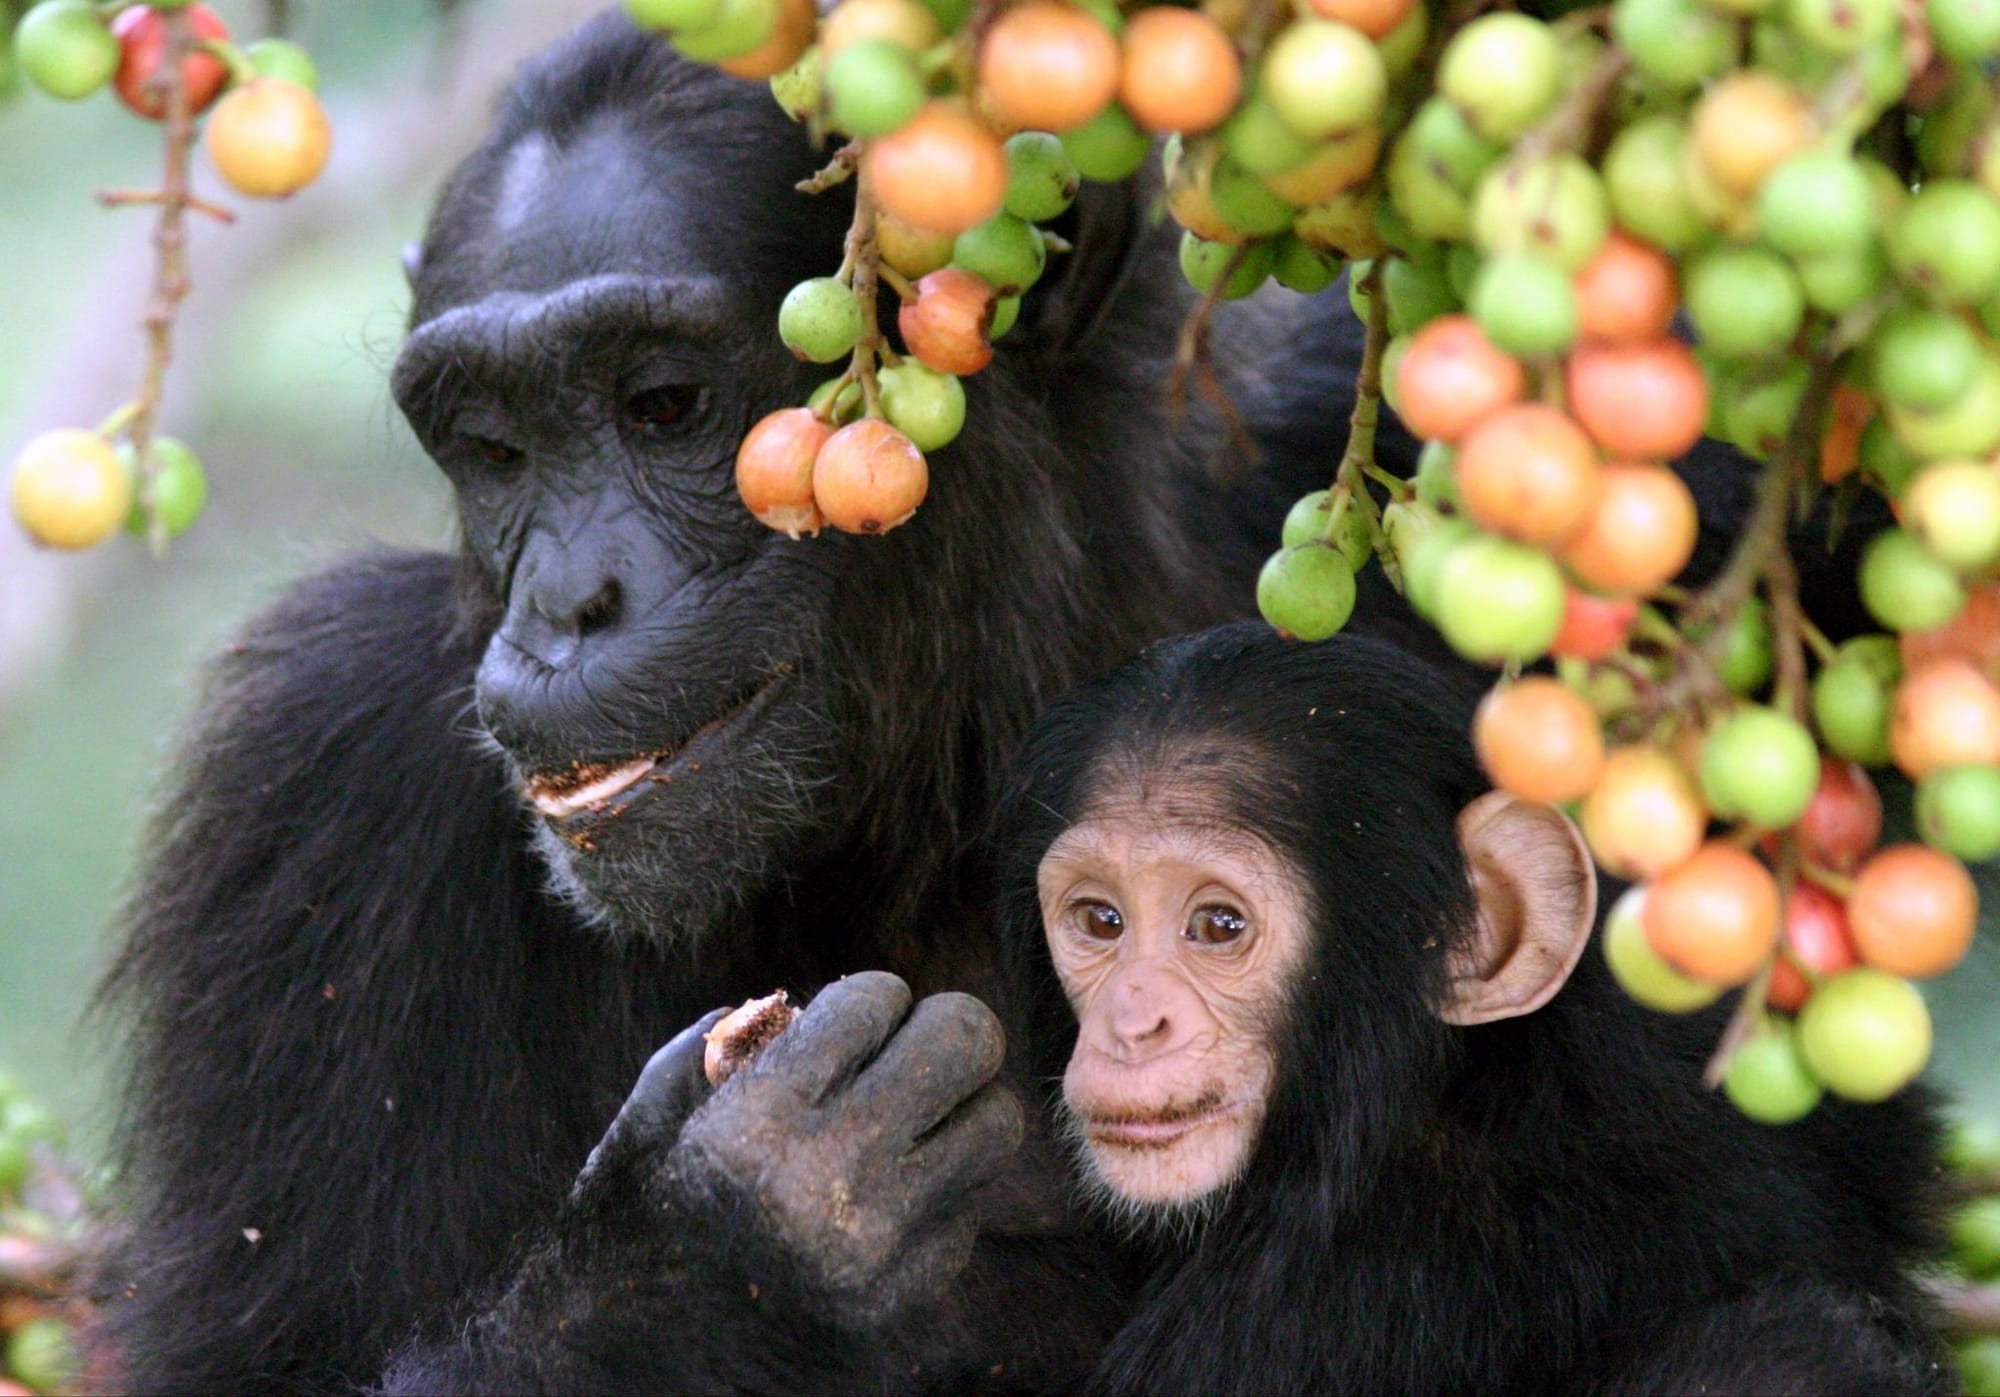
An Ancient Virus Explains Why the Human Brain Is Special
Welcome back to the Abstract! Here are the studies this week that invaded our brains, thought fast, swapped coffins, and hit the art gallery. First, an ancient viral pandemic that afflicted many of our primate…

The PHP Meltdown Shows How AI Makes Bugs More Exploitable
Security researchers used AI tools to help uncover years-old vulnerabilities in the PHP web scripting language. Then the AI-assisted attacks began.
Brotli Decoder Flaw Behind Node.js RCE Also Affects Bun, Python and Other Widely Used Software
A memory-corruption flaw in Google's Brotli decoder sits in many programs that unpack Brotli-compressed data, among them Bun, Microsoft's .NET, the Python Brotli and brotlicffi packages, and Envoy proxies set up to…

Leaked LiteLLM Master Key Let Attackers Steal GitHub Tokens and Hijack Release Pipeline
LiteLLM on Friday revealed that an Agent Platform master key accidentally published to a public GitHub repository in late May 2026 ultimately allowed the threat actor to push a malicious version of the popular Python…

Google Says Gmail and Photos Data Shared With AI Search Could Be Used for Targeted Ads
Google has updated its privacy policy to spell out that using personalized artificial intelligence (AI) features in Search or Gemini could allow the company to serve targeted ads to users based on their activity on…

Researchers Push Over 2 Million Updates to Remotely Disable Popcorn Time Updater That Could Fuel a Botnet
Between November 2025 and March 2026, the Dutch security firm Eye Security pushed more than 2 million updates to computers it did not own to switch off a background updater that it said could have allowed an outsider to…

CISA Flags Two Actively Exploited Critical Flaws in Collabora Online and Arista VeloCloud
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two vulnerabilities impacting Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrator (VCO) to its Known Exploited…
Vulnerabilities in PHP Affecting Cisco Products: October 2026
On October 21, the PHP Foundation announced the availability of a Critical PHP Security release addressing two critical vulnerabilities: CVE-2026-109618 - RCE via OOM corruption CVE-2026-109619 - RCE via stale global…
Friday Squid Blogging: Increasing Squid Populations
This article in Nature argues that it’s due to an overfishing of predators and warming sea temperatures. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered…
Trust Is Not What It Seems — And Fraudsters Are Counting on It
Threat actors don't need to rely on malware to breach organizations anymore. They're simply calling help desks and politely asking for access, with a little help from artificial intelligence.
Abandoned Popcorn Time app exposed millions of devices to RCE attacks
Researchers remotely disabled a vulnerable updater in the abandoned Time4Popcorn app, a fork of the Popcorn Time BitTorrent client, closing a security flaw that could have allowed attackers to execute malicious code…
[R1] Stand-alone Security Patch Available for Tenable Enclave Security Versions 1.7.0, 1.8.0, 1.9.1: SC-202610.2
[R1] Stand-alone Security Patch Available for Tenable Enclave Security Versions 1.7.0, 1.8.0, 1.9.1: SC-202610.2 Arnie Cabral Fri, 10/23/2026 - 16:14 Tenable Enclave Security leverages third-party software to help…
(Reliable)? php2shell exploitability, (Fri, Oct 23rd)
Yesterday everyone was running around like crazy (me included :) because of the php2shell vulnerability.
There's a third PHP2Shell bug, but it won't get an emergency fix
As the PHP2Shell chaos continues, researchers have found a third PHP vulnerability that could allow attackers to take over websites or remotely run malware on vulnerable systems. But this one won’t receive an emergency…
[R1] Stand-alone Security Patch Available for Tenable Security Center Versions 6.6.0, 6.7.2, 6.8.0, 6.9.1: SC-202610.2
[R1] Stand-alone Security Patch Available for Tenable Security Center Versions 6.6.0, 6.7.2, 6.8.0, 6.9.1: SC-202610.2 Arnie Cabral Fri, 10/23/2026 - 15:52 Security Center leverages third-party software to help provide…