1Apple Warns iPhone Users in 99 Countries of Sophisticated Mercenary Spyware Attacks404 MediaBleeping ComputerCCCS Alerts & AdvisoriesCyber Security NewsCyberScoopMalwarebytes Labs+3Apple has issued a fresh round of threat notifications to selected iPhone users in 99 countries, warning that they have been targeted by sophisticated mercenary spyware attacks. Security researcher Costin Raiu reported the new wave on October 30, 2026, saying it was separate from August’s alerts and linked to new attacks. “Today’s notification is being sent to targeted users in 99 countries, and to date we have notified users in over 150 countries in total,” Apple said in the notice shared by Raiu. The company did not name the attackers or connect the warnings to any specific region…
3Cursor Confirms Malicious Claude Code Extension With SSH Backdoor Was Available for 11 HoursCisco TalosCyber Security NewsMicrosoft SecurityCVE-2026-62740 ↗CVE-2026-62877 ↗Cursor has confirmed that malicious Claude Code extension packages were available through its VS Code Extension Marketplace for roughly 11 hours on October 29, 2026. The altered packages targeted Windows and macOS users and attempted to install an SSH backdoor for lasting remote access. According to Cursor’s security notice, the affected versions were Anthropic.claude-code 2.1.312 and 2.1.313. They were available between approximately 2:27 a.m. and 1:35 p.m. Pacific Time, a window of 11 hours and eight minutes. Cursor said Anthropic did not develop these malicious versions. The confirmation…
6Google Launches Gemini 4 Carbon With State-Of-The-Art Cybersecurity CapabilitiesCrowdStrike BlogCyber Security NewsThe Hacker NewsGoogle has announced Gemini 4 Carbon, its latest AI model built to find software flaws , test whether attackers could exploit them, and produce fixes. Unveiled on October 28, 2026, Carbon builds on Gemini 4 Argon and targets complex security and coding work that can take days. Access will begin with selected cyber defenders, not a public launch. According to Google’s announcement , Carbon combines stronger cybersecurity skills with improved handling of long tasks. Google says internal teams have seen it work through dead ends while tracing subtle bugs across large codebases and low-level…
7Hackers steal $6.3 billion from Binance in record crypto heistArs Technica SecurityBleeping ComputerThe Hacker NewsThe Register Security+1Binance has suspended all withdrawals after the world’s largest cryptocurrency exchange fell victim to what appears to be the biggest heist in history. The exchange put the “estimated total impact” of the hack at about $6.3 billion and said around $3 billion of affected assets, mainly stablecoins that act as cash for the crypto market, had been frozen. But analysts at Elliptic said the attacker had changed about $3.3 billion into digital assets that could not be frozen and was working to cash those out as traditional currency. Read full article Comments
8Over 60,000 Attacks Target WordPress RCE Vulnerability Within 24 HoursCyber Security NewsSecurityWeekThe Hacker NewsHackers are targeting a WordPress Core remote code execution vulnerability that can expose websites during software updates. The supplied Wordfence threat intelligence snapshot lists 60,471 blocked attempts over 24 hours. These are attack attempts, not confirmed website compromises, and the figure does not establish how many individual sites were targeted. WordPress released version 7.1.4 on October 28, 2026, addressing 22 security vulnerabilities. The update closes the code execution weakness alongside stored cross-site scripting, information disclosure, and permission issues. The official…
9North Korean Hackers Steal Developer Credentials to Inject Malware Into GitHub and Software PackagesCyber Security NewsDark ReadingThe Hacker NewsThe Register Security+1A North Korea-aligned hacking group has moved beyond fake job interviews and now steals developer credentials to plant malware in trusted software projects. The group, tracked as DeceptiveDevelopment, used the stolen access to change code in public and private repositories between April and September 2026. Every poisoned project then became a new way into the systems of the people who use it. The group has been known for years for tricking developers with fake recruiters and coding tests. In earlier campaigns, it mainly wanted to steal cryptocurrency wallets and browser logins. The new…
12Researchers find bugs in 5 AI developer tools, with OpenAI and Microsoft flaws still unpatchedBleeping ComputerThe Hacker NewsThe Register SecurityMultiple vulnerabilities in five popular AI developer tools could allow attackers to execute code on a host machine, read and steal files, or spoof browser address bars. Researchers say flaws in OpenAI's Codex and Microsoft's VS Code remain unpatched, potentially putting developers who use affected configurations at risk. AI security startup Forever Security discovered vulnerabilities in Cursor, GitHub Copilot, Anthropic's Claude Desktop, VS Code, and Codex, and disclosed four of the flaws to the affected vendors. GitHub independently fixed the Copilot vulnerability without receiving a report…
13Cloudflare Reports 18.2 Million Network-Layer DDoS Attacks in Q3, Up 38%SecurityWeekThe Hacker NewsThreat actors are launching about 8,226 network-layer distributed denial-of-service (DDoS) attacks per hour, Cloudflare revealed Thursday. The web infrastructure and security company said it autonomously mitigated 18.2 million network-layer (L3) DDoS attacks and 14.4 trillion HTTP DDoS requests in the third quarter of 2026. That amounts to 197,400 attacks per day, or one attack every 0.44
14TeamViewer Security Flaw Could Turn Remote Support Sessions Into Computer TakeoversCyber Security NewsSecurityWeekCVE-2026-111585 ↗A newly disclosed TeamViewer vulnerability could let an attacker turn a routine remote support session against the technician providing help. Tracked as CVE-2026-111585, the flaw allows a malicious remote computer to crash the viewer application and potentially run code on the technician’s machine. TeamViewer rates it High, with a CVSS score of 8.8. Remedio researcher Omri Dar published the technical findings on October 29, following a fix released on October 27. The attack requires the victim to establish a remote session with an attacker-controlled or compromised host. After that…
16Fake PDF and search tools hijacked searches for 13.4 million Chrome usersCCCS Alerts & AdvisoriesMalwarebytes LabsAds promoted browser extensions as tools to find manuals, convert PDFs, or make searches safer. But many of these extensions sent users’ search queries through servers controlled by their operators. Socket researcher John Tuckner identified 319 extensions with an estimated 13.4 million installs over a decade. The extensions hijacked users’ default search settings and routed their searches through servers controlled by the operators before sending them to Yahoo or Bing. This gave the operators access to users’ queries and let them earn referral payments. Socket says the extensions were…
19Trezor Warns of Suspected Hardware Implant in One of Its Wallets Sold by CryptoBilisBleeping ComputerThe Hacker NewsA Trezor Safe 5 hardware wallet bought from the reseller CryptoBilis has an extra circuit board that sends out the recovery phrase over a mobile network, a customer has reported. Trezor has not yet examined the device. It is telling everyone who bought a Trezor from CryptoBilis since March 2026 to move their funds to a new wallet with a new recovery phrase. Trezor said in a blog post 
20CISA Adds Actively Exploited GitLab RCE and Cisco Firewall DoS Flaws to KEVCCCS Alerts & AdvisoriesThe Hacker NewsThe U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added two security flaws impacting Cisco and GitLab software to its Known Exploited Vulnerabilities (KEV), citing evidence of active exploitation. The vulnerabilities are listed below - CVE-2026-97229 (CVSS score: 10.0) - An integer overflow or wraparound vulnerability in GitLab Community Edition and Enterprise
Blockchain analytics firm Chainalysis disclosed a data breach after attackers used "offensive agentic techniques" to access internal systems and tools, exposing customer names, email addresses, user IDs, and…
American blockchain analysis firm Chainalysis said it was the target of a cybersecurity incident in which an external actor accessed non-sensitive customer data. However, the company noted that the breach did not result…
American blockchain analysis firm Chainalysis said it was the target of a cybersecurity incident in which an external actor accessed non-sensitive customer data. However, the company noted that the breach did not result in unauthorized access to its investigation content, authentication credentials, or session tokens. "This month, Chainalysis detected an external actor using offensive agentic
VOLTA is a mature stealer implant with an optional AI-integration layer. After stealing credentials, sessions, and cryptocurrency wallets, VOLTA sends a structured evidence bundle to an LLM to rank the victim’s assets…
VOLTA is a mature stealer implant with an optional AI-integration layer. After stealing credentials, sessions, and cryptocurrency wallets, VOLTA sends a structured evidence bundle to an LLM to rank the victim’s assets by monetization value. If a model refuses to perform the target assessment, VOLTA fails over to a three-model chain, implying a direct engineering effort and expectation of hitting model guardrails. This stealer is self-deleting, and there is no attacker-owned infrastructure. The novelty in the AI-integration is that it is not supporting a traditional malware capability but…
Named “Volta-Autodoxer,” the recently uncovered malware uses AI tools to collect troves of data about victims, from login credentials and credit card numbers to Discord sessions and UberEats receipts.
Welcome back to the Abstract—and Happy Halloween! Here are the studies this week that smashed into Earth, put aliens on ice, drank mummy wine, and hugged it out. First, a century-old theory that comets enriched Earth…
Welcome back to the Abstract—and Happy Halloween! Here are the studies this week that smashed into Earth, put aliens on ice, drank mummy wine, and hugged it out. First, a century-old theory that comets enriched Earth with the stuff of life is upended by new models of ancient impacts. Then: the case for life in extraterrestrial sea ice, a Halloween-coded medieval concoction, and a scientific embrace. As always, for more of my work, check out my book First Contact: The Story of Our Obsession with Aliens , or
Cursor has confirmed that malicious Claude Code extension packages were available through its VS Code Extension Marketplace for roughly 11 hours on October 29, 2026. The altered packages targeted Windows and macOS users…
Cursor has confirmed that malicious Claude Code extension packages were available through its VS Code Extension Marketplace for roughly 11 hours on October 29, 2026. The altered packages targeted Windows and macOS users and attempted to install an SSH backdoor for lasting remote access. According to Cursor’s security notice, the affected versions were Anthropic.claude-code 2.1.312 and 2.1.313. They were available between approximately 2:27 a.m. and 1:35 p.m. Pacific Time, a window of 11 hours and eight minutes. Cursor said Anthropic did not develop these malicious versions. The confirmation…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Ivanti Connect Secure (ICS) to its Known Exploited Vulnerabilities (KEV) catalog, following active…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Ivanti Connect Secure (ICS) to its Known Exploited Vulnerabilities (KEV) catalog, following active exploitation in the wild. The vulnerabilities are listed below - CVE-2026-111357 (CVSS score: 8.8) - A missing authentication for a critical function vulnerability that could allow a
Hackers are targeting a WordPress Core remote code execution vulnerability that can expose websites during software updates. The supplied Wordfence threat intelligence snapshot lists 60,471 blocked attempts over 24…
Hackers are targeting a WordPress Core remote code execution vulnerability that can expose websites during software updates. The supplied Wordfence threat intelligence snapshot lists 60,471 blocked attempts over 24 hours. These are attack attempts, not confirmed website compromises, and the figure does not establish how many individual sites were targeted. WordPress released version 7.1.4 on October 28, 2026, addressing 22 security vulnerabilities. The update closes the code execution weakness alongside stored cross-site scripting, information disclosure, and permission issues. The official…
A malicious ChatGPT share link could run an attacker's code in the logged-in session of anyone who opened it, allowing them to read their private conversations, researchers at the security firm Parameter showed. The…
A malicious ChatGPT share link could run an attacker's code in the logged-in session of anyone who opened it, allowing them to read their private conversations, researchers at the security firm Parameter showed. The researchers reported the flaw through OpenAI's bug bounty program on October 18, and OpenAI fixed it eight days later and rated it P1, its most serious category.
Threat actors are launching about 8,226 network-layer distributed denial-of-service (DDoS) attacks per hour, Cloudflare revealed Thursday. The web infrastructure and security company said it autonomously mitigated 18.2…
Threat actors are launching about 8,226 network-layer distributed denial-of-service (DDoS) attacks per hour, Cloudflare revealed Thursday. The web infrastructure and security company said it autonomously mitigated 18.2 million network-layer (L3) DDoS attacks and 14.4 trillion HTTP DDoS requests in the third quarter of 2026. That amounts to 197,400 attacks per day, or one attack every 0.44
Google has announced Gemini 4 Carbon, its latest AI model built to find software flaws , test whether attackers could exploit them, and produce fixes. Unveiled on October 28, 2026, Carbon builds on Gemini 4 Argon and…
Google has announced Gemini 4 Carbon, its latest AI model built to find software flaws , test whether attackers could exploit them, and produce fixes. Unveiled on October 28, 2026, Carbon builds on Gemini 4 Argon and targets complex security and coding work that can take days. Access will begin with selected cyber defenders, not a public launch. According to Google’s announcement , Carbon combines stronger cybersecurity skills with improved handling of long tasks. Google says internal teams have seen it work through dead ends while tracing subtle bugs across large codebases and low-level…
A newly disclosed TeamViewer vulnerability could let an attacker turn a routine remote support session against the technician providing help. Tracked as CVE-2026-111585, the flaw allows a malicious remote computer to…
A newly disclosed TeamViewer vulnerability could let an attacker turn a routine remote support session against the technician providing help. Tracked as CVE-2026-111585, the flaw allows a malicious remote computer to crash the viewer application and potentially run code on the technician’s machine. TeamViewer rates it High, with a CVSS score of 8.8. Remedio researcher Omri Dar published the technical findings on October 29, following a fix released on October 27. The attack requires the victim to establish a remote session with an attacker-controlled or compromised host. After that…
Anthropic researchers have shown that Claude can design training data that slips past an AI safety monitor and causes a separate research model to blackmail users, weaken security code, and resist oversight. The October…
Anthropic researchers have shown that Claude can design training data that slips past an AI safety monitor and causes a separate research model to blackmail users, weaken security code, and resist oversight. The October 2026 study exposes a gap between text that looks safe during screening and behavior learned through training. The distinction matters. These were deliberately altered research models, not evidence that deployed Claude products routinely behave this way. Anthropic says the models were never released, and the experiment gave the attacking agent unusually favorable conditions…
Apple has issued a fresh round of threat notifications to selected iPhone users in 99 countries, warning that they have been targeted by sophisticated mercenary spyware attacks. Security researcher Costin Raiu reported…
Apple has issued a fresh round of threat notifications to selected iPhone users in 99 countries, warning that they have been targeted by sophisticated mercenary spyware attacks. Security researcher Costin Raiu reported the new wave on October 30, 2026, saying it was separate from August’s alerts and linked to new attacks. “Today’s notification is being sent to targeted users in 99 countries, and to date we have notified users in over 150 countries in total,” Apple said in the notice shared by Raiu. The company did not name the attackers or connect the warnings to any specific region…
Chainalysis has confirmed that an attacker used “offensive agentic techniques” to access its systems and internal tools, exposing customer account details. The blockchain investigation company said the accessed…
Chainalysis has confirmed that an attacker used “offensive agentic techniques” to access its systems and internal tools, exposing customer account details. The blockchain investigation company said the accessed information included user IDs, full names, email addresses, and organization role labels, while its investigation has found no evidence that customer investigation content or authentication secrets were accessed. In its public security notice, Chainalysis said it had notified all customers and brought in outside cybersecurity experts. The company also emphasized that the incident was…
On October 29, 2026, Cursor reported that a tampered copy of Claude Code extension (anthropic.claude-code, versions 2.1.313 and 2.1.312) was available and served in the Cursor extension marketplace for a few hours to…
On October 29, 2026, Cursor reported that a tampered copy of Claude Code extension (anthropic.claude-code, versions 2.1.313 and 2.1.312) was available and served in the Cursor extension marketplace for a few hours to attempt a supply-chain attack on Cursor users. Cursor reports that it was live from about 2:27 AM to 1:35 PM Pacific Daylight Time (PDT). We have confirmed that the malicious packages found on Cursor marketplace were never published nor distributed from Microsoft Visual Studio Marketplace and from npm @antropic-ai/claude-code, which were not affected by this incident. Anthropic…
Between October 17 and October 20, 2026, a critical security compromise involving Certificate Authorities that are managed by eMudhra was uncovered. A security researcher demonstrated that the private keys for eight…
Between October 17 and October 20, 2026, a critical security compromise involving Certificate Authorities that are managed by eMudhra was uncovered. A security researcher demonstrated that the private keys for eight eMudhra intermediate certificates were fundamentally broken due to an unprecedented error in their Key Generation Ceremony (KGC) in April 2025. This allows anyone to brute-force acquire these private keys within seconds. For more information, see eMudhra Intermediate CA Compromise and the Cisco Talos blog post Compromised eMudhra intermediate certificates . For information about…
A China state-backed threat group is using ARTEX, the automated agentic AI penetration testing framework, to achieve remarkable speed, scale and success in a campaign that already compromised about 140 sensitive targets…
A China state-backed threat group is using ARTEX, the automated agentic AI penetration testing framework, to achieve remarkable speed, scale and success in a campaign that already compromised about 140 sensitive targets in 11 days, according to CrowdStrike. The threat group, which CrowdStrike tracks as Vapor Panda, targeted more than 200 organizations in at least 14 countries since Oct. 17, the security company said in a threat report Thursday. Targets and confirmed victims include foreign ministries, a European country’s presidency and prime minister’s office, defense and intelligence…
Security researchers at Anthropic have developed an exploit for a critical Linux kernel vulnerability that allows unauthenticated attackers to remotely execute commands as root on servers running Multipath TCP (MPTCP)…
The DOJ’s Executive Office for U.S. Trustees said a consumer privacy ombudsman is needed to advise the court on how to regulate what data from Character.AI can be sold and under what terms.
Thanks to a lucky break, flawed code in a tainted Claude extension prevented the attacker from fully worming their way into some 5,000 developer machines.
On October 21, 2026, Node.js announced the availability of fixes for multiple vulnerabilities across the following supported release lines: 22.x, 24.x, and 26.x. These vulnerabilities impact critical operations such as…
On October 21, 2026, Node.js announced the availability of fixes for multiple vulnerabilities across the following supported release lines: 22.x, 24.x, and 26.x. These vulnerabilities impact critical operations such as the Brotli decoder, DNS resolution, and TLS certificate validation. The vulnerabilities pose risks for remote code execution and traffic interception. For more information, see Node.js Security Release . The following vulnerabilities have a Security Impact Rating (SIR) of High and are addressed in this advisory: CVE-2026-111497 - Brotli decoder out-of-bounds write; potential…
A recent law enforcement operation to dismantle harmful scam centers was a big success. A threat intelligence expert walks us through what happened and why he wants more of the same.
A n0n ransomware operator tried to break into 23 organizations across 14 countries, but couldn't secure its own front door, leaving its server exposed with all of its methods on view. The criminals used a mix of new…
A n0n ransomware operator tried to break into 23 organizations across 14 countries, but couldn't secure its own front door, leaving its server exposed with all of its methods on view. The criminals used a mix of new (AI) and old (stolen credentials) tooling during their data-theft spree, and in some cases not only stole and encrypted files, but also deleted data and backups, eliminating victims’ ability to recover their information. And despite the fear and hype around the breachpocalypse, with AI finding and developing exploits for critical vulnerabilities affecting most organizations across…
On October 21, the PHP Foundation announced the availability of a Critical PHP Security release addressing two critical vulnerabilities: CVE-2026-109618 - RCE via OOM corruption CVE-2026-109619 - RCE via stale global…
On October 21, the PHP Foundation announced the availability of a Critical PHP Security release addressing two critical vulnerabilities: CVE-2026-109618 - RCE via OOM corruption CVE-2026-109619 - RCE via stale global state For information about these vulnerabilities, see the advisories GHSA-w8hw-w9fx-j79w and GHSA-6wmf-4rv5-p3rp . These vulnerabilities are being referenced as PHP2shell. For information about Splunk products and offerings, see Vulnerabilities in PHP (CVE-2026-109618, CVE-2026-109619) on Splunk Products - October 2026 . Important: If a product is not listed within this…
The company, billing itself as “the next-generation fashion retailer for Millennial and Generation Z consumers,” said a recent hack exposed customer payment card numbers.
In the wake of fanfiction repository Archive of Our Own (AO3) announcing a weeks-long security incident outage, readers and writers are reflecting on why the site is important to the fanfiction community, and how…
In the wake of fanfiction repository Archive of Our Own (AO3) announcing a weeks-long security incident outage, readers and writers are reflecting on why the site is important to the fanfiction community, and how they’re coping with the downtime. On Thursday , the Organization for Transformative Works (OTW), the non-profit organization that runs AO3, posted that the site was down for maintenance, eventually updating to say the site restoration will take around two weeks, but could take up to a month. OTW confirmed in an updated status report Friday morning that this outage is due to a…
Researchers have amassed a trove of more than 25,000 calls to a support hotline for people during and after psychedelic trips, making it “the largest dataset of psychedelic support interactions ever assembled—exceeding…
Researchers have amassed a trove of more than 25,000 calls to a support hotline for people during and after psychedelic trips, making it “the largest dataset of psychedelic support interactions ever assembled—exceeding the combined sample sizes of all published psychedelic clinical trials by an order of magnitude,” according to a study published on Friday in Science Advances . Despite the popularity of psychedelics as recreational drugs, and increasing interest in them as medically-prescribed therapeutic treatments, there is very little research about the effects of these substances outside…
Apple has sent new notifications of mercenary spyware infections to almost 100 countries, with recipients including journalists and documentary filmmakers . “Today’s notification is being sent to targeted users in 99…
Apple has sent new notifications of mercenary spyware infections to almost 100 countries, with recipients including journalists and documentary filmmakers . “Today’s notification is being sent to targeted users in 99 countries, and to date we have notified users in over 150 countries in total,” the company said . “The extreme cost, sophistication, and worldwide nature of mercenary spyware attacks make them some of the most advanced digital threats in existence today. As a result, Apple does not attribute the attacks or the notice you’re receiving to any specific attackers or geographical…
Chinese state-sponsored threat actors have been observed using a Go-based artificial intelligence (AI)-powered penetration testing framework called ARTEX in attacks aimed at high-value targets simultaneously. The…
Chinese state-sponsored threat actors have been observed using a Go-based artificial intelligence (AI)-powered penetration testing framework called ARTEX in attacks aimed at high-value targets simultaneously. The activity has been attributed by CrowdStrike to a China-based "targeted intrusion adversary" it tracks under the moniker Vapor Panda (previously VexatiousTemper). First identified in
General Motors is taking what looks like a light slap on the wrist from a coalition of 35 states and the District of Columbia after agreeing to settle allegations that it collected drivers' data without proper consent…
General Motors is taking what looks like a light slap on the wrist from a coalition of 35 states and the District of Columbia after agreeing to settle allegations that it collected drivers' data without proper consent and sold it to data brokers that supplied insurance companies. The Washington state AG's office said on Thursday that GM had reached a $220 million settlement with 36 attorneys general over the automaker's collection and sharing of driving data, including precise location information, speed, seatbelt use, and other metrics. According to investigators, GM sold that data to…
On Friday, Andy Yen, the CEO of Proton, cancelled a series of nearly company-wide ‘re-interviews’ that would have forced employees to explain how they are using AI, with the clear intention that they may be fired if not…
On Friday, Andy Yen, the CEO of Proton, cancelled a series of nearly company-wide ‘re-interviews’ that would have forced employees to explain how they are using AI, with the clear intention that they may be fired if not using it enough in the eyes of Proton leadership, according to six current Proton employees and audio of an around two hour all-hands meeting obtained by 404 Media. The move came after 404 Media published an investigation on Thursday, which showed how Yen was aggressively pushing AI across Proton, in some cases despite security concerns from employees. In one exchange, an…
Anthropic has denied allegations that a malicious version of the official Claude Code extension published to Cursor’s marketplace was linked to any kind of compromise of its own systems. The company was forced to issue…
Anthropic has denied allegations that a malicious version of the official Claude Code extension published to Cursor’s marketplace was linked to any kind of compromise of its own systems. The company was forced to issue a statement after prominent figures in the cybersecurity industry alleged that the extension, which infected up to 5,000 developers, was uploaded to Cursor’s marketplace following a breach at Claudemaker Towers. Felix Rieseberg, a member of Anthropic’s technical staff, Xeeted today: "We're working with Cursor on this incident, but it wasn’t a compromise of Anthropic's systems…
Microsoft Threat Intelligence investigated two human-operated intrusions in which threat actors used Microsoft Teams messages and calls to impersonate IT or help desk personnel and socially engineer users into granting…
Microsoft Threat Intelligence investigated two human-operated intrusions in which threat actors used Microsoft Teams messages and calls to impersonate IT or help desk personnel and socially engineer users into granting interactive remote access, primarily through Quick Assist. Once connected, the threat actors staged portable Python, Bun, or Java runtimes, performed host and network discovery, and assessed Active Directory Certificate Services (AD CS) for certificate-based authentication paths. Although the incidents began with the same social-engineering and remote-access pattern, they…
Overview An origin-validation flaw in BeyondTrust Remote Support lets an unauthenticated attacker write files on the appliance and execute code as the site's operating-system user. The entry point is the public customer…
Overview An origin-validation flaw in BeyondTrust Remote Support lets an unauthenticated attacker write files on the appliance and execute code as the site's operating-system user. The entry point is the public customer connection used to start a support session. No account credentials or user interaction are required. The flaw sits between the internal message router, brain , and an appliance-side customer worker, thin-scc . An attacker can put a reserved local router ID into a message's source address. The router forwards the message, and the worker accepts that address as proof that the…
The Trump administration is taking direct aim at California state election officials, issuing grand jury subpoenas to election offices statewide ahead of the final day of voting on Nov. 3. The investigations, first…
The Trump administration is taking direct aim at California state election officials, issuing grand jury subpoenas to election offices statewide ahead of the final day of voting on Nov. 3. The investigations, first reported by Bloomberg, center on alleged administration of illegal voting. They are ostensibly tied to demands by the U.S. Justice Department that California and other states use federal voter lists to determine whether a voter is a “potential noncitizen” and should be removed. The Los Angeles County Registrar of Voters told CyberScoop it received multiple grand jury subpoenas last…
Hardware wallet device maker Trezor has received credible reports about a suspected hardware crypto-theft implant in a Trezor Safe 5 sold by its reseller CryptoBilis in Southeast Asia.
The state’s Department of Education (FLDOE) said on Thursday it became aware of a data breach involving the Florida Student Financial Aid website on October 19.
This is Behind the Blog, where we share our behind-the-scenes thoughts about how a few of our top stories of the week came together. This week, we discuss customer service and Proton fallout. JASON: Since I wrote about…
This is Behind the Blog, where we share our behind-the-scenes thoughts about how a few of our top stories of the week came together. This week, we discuss customer service and Proton fallout. JASON: Since I wrote about ChatGPT turning me into tech support for people’s random problems, I have gotten many more AI-generated emails from people asking me to solve their tech support problems. So, mission accomplished I guess. I think and hope it was clear in the article, but I think this phenomenon is happening to a lot of journalists, not just us at 404 Media. A lot of the ChatGPT chats I saw told…
I ricercatori non riescono a spiegare del tutto perché le minacce informatiche in Italia siano così diverse rispetto a quelle di qualsiasi altro Paese.
Ads promoted browser extensions as tools to find manuals, convert PDFs, or make searches safer. But many of these extensions sent users’ search queries through servers controlled by their operators. Socket researcher…
Ads promoted browser extensions as tools to find manuals, convert PDFs, or make searches safer. But many of these extensions sent users’ search queries through servers controlled by their operators. Socket researcher John Tuckner identified 319 extensions with an estimated 13.4 million installs over a decade. The extensions hijacked users’ default search settings and routed their searches through servers controlled by the operators before sending them to Yahoo or Bing. This gave the operators access to users’ queries and let them earn referral payments. Socket says the extensions were…
TeamViewer has fixed a flaw that lets the machine being controlled in a remote session attack the computer that connected to control it. In a TeamViewer session, the computer that connects and takes control is the…
TeamViewer has fixed a flaw that lets the machine being controlled in a remote session attack the computer that connected to control it. In a TeamViewer session, the computer that connects and takes control is the viewer, and the machine it controls is the host. A malicious or compromised host can exploit the flaw to crash the viewer's TeamViewer and, depending on the platform, may also run
A North Korea-aligned hacking group has moved beyond fake job interviews and now steals developer credentials to plant malware in trusted software projects. The group, tracked as DeceptiveDevelopment, used the stolen…
A North Korea-aligned hacking group has moved beyond fake job interviews and now steals developer credentials to plant malware in trusted software projects. The group, tracked as DeceptiveDevelopment, used the stolen access to change code in public and private repositories between April and September 2026. Every poisoned project then became a new way into the systems of the people who use it. The group has been known for years for tricking developers with fake recruiters and coding tests. In earlier campaigns, it mainly wanted to steal cryptocurrency wallets and browser logins. The new…
A defense contractor with top secret security clearance pleaded guilty to aiding North Korea’s remote worker scheme by allowing co-conspirators to use his identity to apply for jobs, including positions with national…
A defense contractor with top secret security clearance pleaded guilty to aiding North Korea’s remote worker scheme by allowing co-conspirators to use his identity to apply for jobs, including positions with national security implications, the Justice Department said Wednesday. John Allen Kurrle Jr. participated in a short-lived but prolific conspiracy that spanned at least 88 job applications at U.S.-based companies, resulting in nine job offers, according to court records. The 62-year-old allowed co-conspirators to use his identity and government clearance for prospective sensitive work…
Dhananjay Ganjoo, Managing Director – India & SAARC The uncomfortable part of an adaptive attack is not how quickly it starts, but how quickly it can change course. AI-assisted operations can probe environments, learn…
Dhananjay Ganjoo, Managing Director – India & SAARC The uncomfortable part of an adaptive attack is not how quickly it starts, but how quickly it can change course. AI-assisted operations can probe environments, learn from responses, switch techniques and chain subsequent actions while an attack is still in progress. Anthropic’s 2026 analysis of 832 accounts banned for malicious cyber activity points to this shift. While much of the activity it observed focused on preparing for attacks, the highest-risk actors used AI in live operations, including autonomous execution, orchestration and…
A new malware framework called NetamLoader is being used against a custom version of Windows 10 that only government bodies in Asia use. The campaign looks like a supply-chain operation, and nobody has linked it to a…
A new malware framework called NetamLoader is being used against a custom version of Windows 10 that only government bodies in Asia use. The campaign looks like a supply-chain operation, and nobody has linked it to a known hacking group yet. The malware hides inside a Windows update package, borrows trusted software to run, and deletes its own traces. It also contacts its operators very slowly, so short security checks can miss it. Even a file that looks safe and signed by a known vendor can be part of an infection. Analysts at Securelist, the research blog of Kaspersky’s GReAT team…
A malicious version of Anthropic's Claude Code VS Code extension was distributed through Cursor's extension marketplace for approximately 11 hours on October 29, exposing up to 5,000 developers to malware designed to…
A malicious version of Anthropic's Claude Code VS Code extension was distributed through Cursor's extension marketplace for approximately 11 hours on October 29, exposing up to 5,000 developers to malware designed to install persistent SSH backdoors.
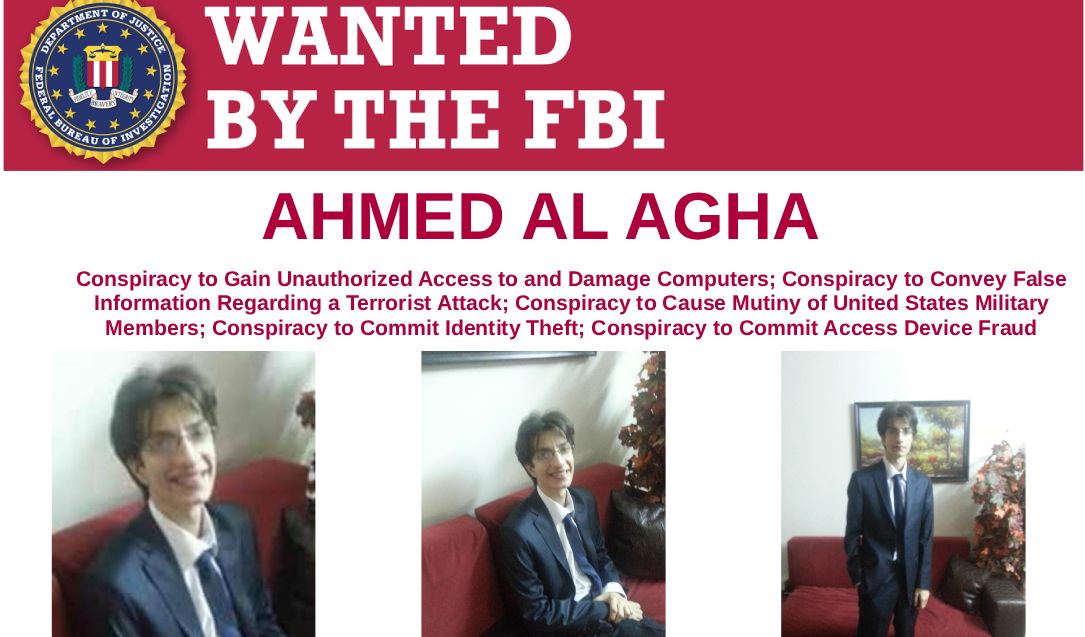
A Syrian man who prosecutors say was a central figure in a hacking operation run from former President Bashar Assad’s inner circle was sentenced Thursday to 42 months in federal prison. Ahmad Umar Agha, 42, carried out…
A Syrian man who prosecutors say was a central figure in a hacking operation run from former President Bashar Assad’s inner circle was sentenced Thursday to 42 months in federal prison. Ahmad Umar Agha, 42, carried out the conspiracy from as early as Aug. 24, 2011, until Jan. 31, 2024, according to the Justice Department. The operation was organized and led by members of Assad’s circle, including the commander of Syria’s General Intelligence Directorate. Agha hacked approximately 47 media entities, businesses, nongovernmental organizations and U.S. and allied government bodies, prosecutors…
Ahmad Umar Agha, known online as “Th3Pr0,” was sentenced Thursday in federal court in Virginia to 42 months behind bars for his role in a conspiracy that was organized by former Syrian President Bashar al-Assad's…