Cybersecurity news & advisories




Apple Emergency Patch for iOS 26, macOS26, macOS15 (CVE-2026-86950), (Mon, Sep 28th)
Apple today released patches for all of its operating systems. However, only patches for older branches include a security fix. The vulnerability being addressed in iOS 26, macOS 26 and macOS 15 is already being…

One Packet Can Crash OT Servers in Industrial Sectors
A high-severity zero-day vulnerability affects the TDengine time-series database used across industrial, IoT, energy, and automotive environments.
Japan's Keio confirms ransomware attack disrupted business systems
Keio Corporation (Keio), a major private railway operator in Japan, said its network was hit by a ransomware attack over the weekend, disrupting some of its business systems.
Times Car confirms data breach affecting 6.6 million user accounts
Japanese car-sharing service Times Car has confirmed that approximately 6.6 million user accounts were compromised in a cyberattack disclosed late last week.
JadePuffer crims hijacked Azure identities and used them to blow up cloud resources
The cyber criminal behind JadePuffer, the first known agentic ransomware infection reported over the summer, has also used stolen Azure identities to conduct destructive attacks on cloud storage and other resources…

Carbonato Botnet Puts an AI Agent on Hacked Docker Hosts
The botnet uses the open source Hermes Agent AI framework to execute commands via Telegram and steal AI API keys from exposed Docker hosts.
Dutch police confirm arrest in ShinyHunters hacking investigation
Dutch police have confirmed that a 24-year-old Amsterdam man arrested earlier this month was detained as part of an investigation into the ShinyHunters hacking group.
ShinyHunters exploiting workarounds for Oracle PeopleSoft bug, Mandiant warns
A vulnerability in a popular line of products from Oracle is being used in a new campaign by the prolific ShinyHunters hacking group, which recently claimed credit for an attack on the FBI’s jobs site.
Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks
Apple has released security updates to address a vulnerability in older versions of iOS, iPadOS, and macOS that it said may have been exploited in targeted attacks. The vulnerability, tracked as CVE-2026-86950, refers…
FBI Hackers Say They Won’t Publish Massive Trove of FBI Employee Data
The hackers behind the massive FBI breach told 404 Media on Monday they do not intend to publish the data. The breach, in which the hackers stole personal information on “all FBI employees and applicants” including…
How we found 24 Android vulnerabilities using our open source AI security agent
With the rise of AI in the security space, our team created the GitHub Security Lab Taskflow Agent as a way for security researchers to easily automate, package, and share the AI prompts and workflows that they find…
Over 16,000 Supabase databases expose PII, passwords, auth tokens
Researchers found more than 16,000 misconfigured Supabase databases exposing readable tables with personally identifiable information, passwords, or authentication tokens.
AI Agents Are Privileged Users; Who Is Auditing Their Access?
Enterprises regularly rigorously monitor human employees, while autonomous AI agents quietly operate with broad privileges that could turn them into the next generation of insider threats.
Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks
Hackers have used a malware family called NeedyMantis to maintain long-term access to networks they had already breached, Microsoft said in a technical analysis. The malware has been seen in a small number of targeted…
As AI world debates security, NVIDIA releases open source tools for agents
Amid growing concerns from both the public and policymakers about cyberattacks involving advanced AI systems, NVIDIA has released a new open software security platform for AI agents. The Open Agent Safety Platform…

IAM for AI agents: A Practical Enterprise Framework
What is IAM for AI agents? AI agents authenticate, invoke tools, and act across enterprise systems with delegated authority. IAM for AI Agents is the identity-control architecture that governs those actors. This guide…
Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M
The attacker who stole about $388 million from the cryptocurrency exchange Bitget gained access through a vulnerability in a third-party security product the exchange used, Bitget said on Monday. The attacker exploited…
RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims
RatHat's operators build and publish the Android banking trojan and control infected phones from a web console, according to security company Cleafy. Cleafy has traced nearly 100 deployments of that console since April…
Modulate Raises $25 Million to Advance Deepfake Detection
The misuse and abuse of AI-generated voice is growing. Modulate’s intention is to allow real time detection and intervention.
New Mexico jury finds Meta deceived consumers about data privacy practices
A New Mexico jury found Facebook violated the law nearly 44 million times by lying to consumers about its data privacy practices.

Chrome Store Hosts 'Poper Blocker' Spyware Downloaded by Millions
A purported ad-blocker exfiltrates reams of sensitive information and benefits from having Google's stamp of approval despite researcher warnings.

Florida AG Seeks Emergency Injunction to Restrict OpenAI and ChatGPT Over AI Safety Risks
Florida Attorney General James Uthmeier has asked a Highlands County judge to impose sweeping temporary restrictions on OpenAI, CEO Sam Altman, and affiliated companies while Florida’s ChatGPT lawsuit proceeds. Four…

Microsoft Finds New Malware Used by Hackers to Maintain Secret Access Inside Target Networks
Microsoft Threat Intelligence has uncovered NeedyMantis, a modular post-compromise malware framework designed to preserve covert access inside already-breached networks. The malware has appeared in a small number of…
US, UK warn of exploited Citrix NetScaler zero-day bugs
Incident responders began warning of potential vulnerabilities in NetScaler Gateway products on Saturday before cybersecurity agencies in the Netherlands, U.S. and U.K. released advisories on Sunday confirming…
JadePuffer agentic AI attacks target Azure, destroy cloud resources
The JadePuffer ransomware operator is targeting Azure tenants with agent-driven attacks that conduct reconnaissance, steal credentials, and destroy core components.

JadePuffer AI Actor Compromises Azure Tenant in Destructive Cloud Attack
The "agentic threat actor" may have used exposed credentials to access resources and delete cloud-based storage, applications, and databases.
Call for Presentations Open for 2026 CISO Forum Virtual Summit
SecurityWeek seeks original, vendor-neutral presentations that help cybersecurity leaders navigate emerging threats, strengthen resilience, and address the strategic challenges facing today’s enterprise security…
Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation
Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters . In the days immediately following the…
Threat Brief: NetScaler Zero Days CVE-2026-88771 and CVE-2026-88772 Exploited in the Wild
Unit 42 is aware of possible 0-day activity against NetScaler devices. Citrix reports CVE-2026-88771, CVE-2026-88772 have been exploited in the wild.
NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence has identified NeedyMantis, a modular post-compromise malware family observed in a limited number of targeted operations affecting telecommunications organizations, universities, medical…
Bitget Restarts Bitcoin Withdrawals Following $387.5m Wallet Breach
Bitget has restarted Bitcoin withdrawals after a $387.5m breach of its hot and warm wallets

NCSC Urges UK organizations to Patch for Citrix NetScaler ADC and Gateway 0-Day Vulnerabilities
The UK National Cyber Security Center (NCSC) has urged organizations to take immediate action against eight vulnerabilities affecting customer-managed Citrix NetScaler ADC and NetScaler Gateway appliances. Two critical…
ShinyHunters trades financial extortion for a reckless war of ego with the FBI
Threat hunters and researchers are alarmed by what they’ve seen in data ShinyHunters claims it stole from the FBI . Limited samples of the stolen data contain FBI agents’ personal contact information, details on family…
New File Notification Attack Lets Hackers Track User Activity Across Linux, Windows and macOS
A cross-platform side-channel attack that abuses file-notification services to monitor user activity on Linux, Windows and macOS. The technique turns inotify, ReadDirectoryChangesW, and FSEvents, which alert…

Hackers Built an AI-Powered Attack Machine and Accidentally Left the Control Panel Open
A criminal crew linked to Blackhatsect0r and DXQRTXX built an automated system designed to find weaknesses across the internet. Its exposed server revealed a credential vault, source code, chat logs, fraud notes, and a…

OpenCode AI Coding Agent Flaw Lets Malicious Websites Execute Code on Developer Machines
A critical attack path in OpenCode, an open-source AI coding agent, could let a malicious website execute commands on a developer’s computer. Tracked as GHSA-632h-h47v-g4x4, the remote code execution vulnerability…

Bitget Backend Breach Drains $387.5 Million as DPRK-Linked Launderers Expose Themselves
Cryptocurrency exchange Bitget has begun restoring withdrawals after attackers exploited its backend wallet infrastructure on September 24, stealing approximately $387.5 million from hot and warm wallets. The incident…

⚡ Weekly Recap: $387M Crypto Hack, Citrix Exploits, AI Agents Go Off-Script, and More Threats
A domain used as harmless placeholder text showed up in roughly 1,700 repositories. Then somebody registered it and started serving malicious lures. That is the kind of week this was: forgotten assumptions turning into…
80,000+ Organizations Had AI Logins Stolen: From Shadow AI to LLMjacking
Infostealer logs exposed AI account credentials and sessions tied to more than 80,000 corporate domains, creating risks ranging from stolen conversations to LLMjacking. SOCRadar examines the growing market for stolen AI…
28th September – Threat Intelligence Report
For the latest discoveries in cyber research for the week of 28th September, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES The FBI has confirmed unauthorized activity affecting FBIjobs.gov…
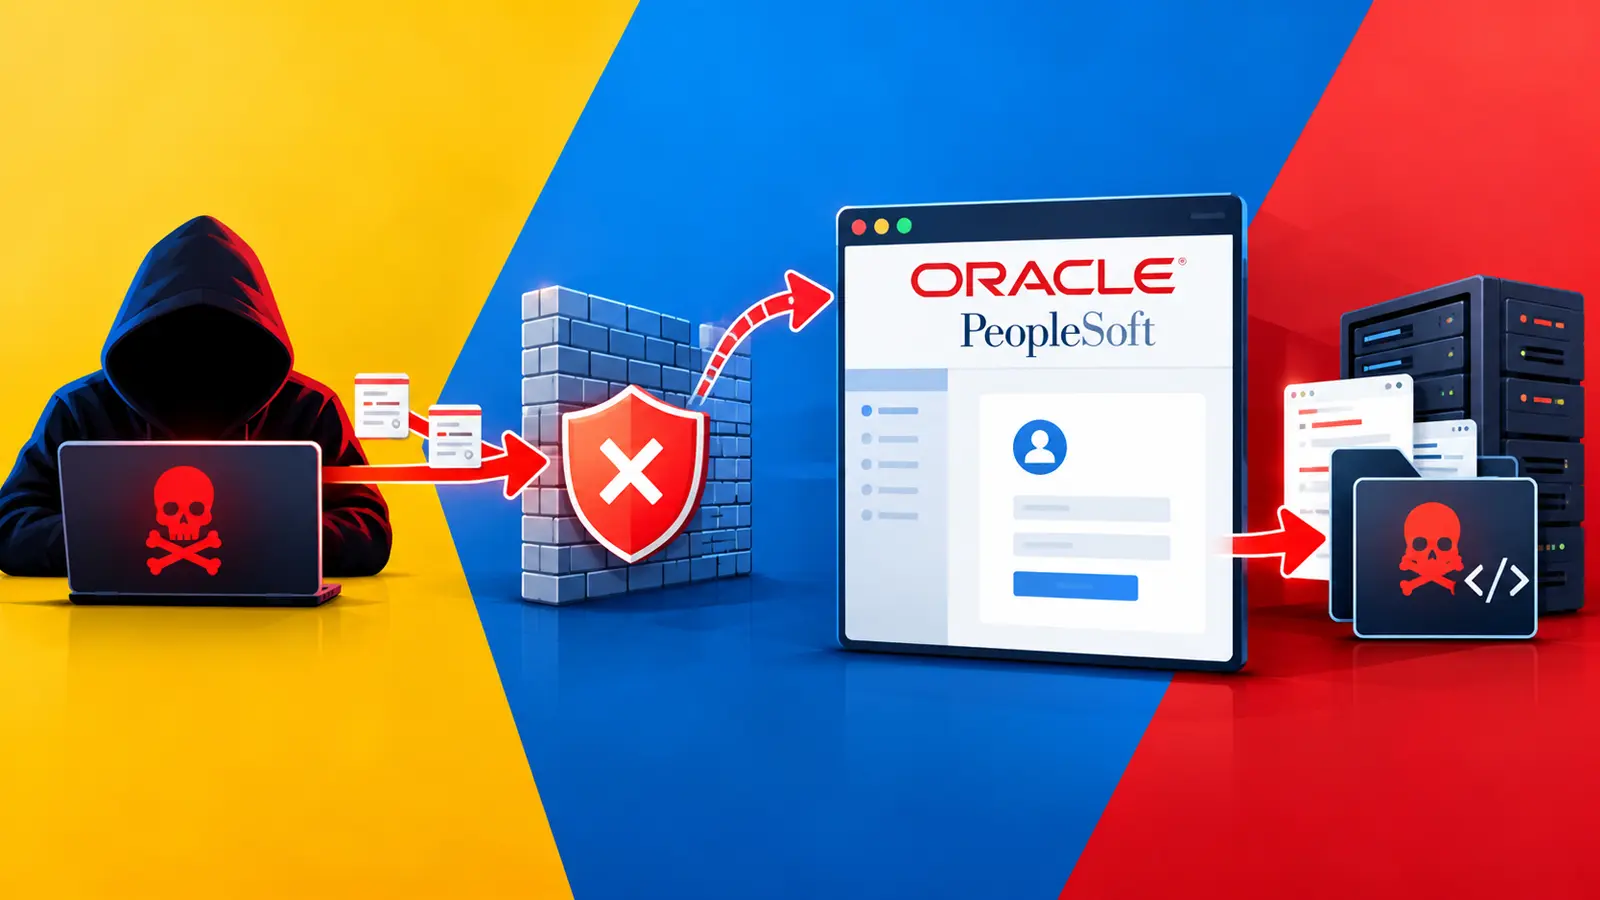
ShinyHunters Bypasses WAF Protections to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells
ShinyHunters has renewed attacks against Oracle PeopleSoft systems by slipping past web application firewall protections and planting web shells. The campaign shows how a small change in an attack request can reopen…
The End of Privacy Is Here (with Kashmir Hill)
Facial recognition is everywhere now. It’s in surveillance cameras; it’s soon going to be in Meta’s RayBan pervert glasses, and some students already did that. You now have massively viral accounts that take clips of…
Cyberattack on Polish medical software provider exposes patient data
Hackers stole personal data from a Polish healthcare software provider in the latest cyberattack to hit the country’s medical sector in recent months.
NVIDIA Launches Open Platform to Secure Autonomous AI Agents
NVIDIA has launched a platform pairing runtime controls with hardware monitoring for AI agents
Humans Are Reading Copilot Prompts — And They're Horrified
This piece contains references to eating disorders. If you or someone you know needs help, support is available . Human contractors hired to improve Microsoft’s Copilot AI chatbot are constantly bombarded with lewd or…
CISA Warns of Microsoft SharePoint Code Injection Vulnerability Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a Microsoft SharePoint code injection vulnerability, tracked as CVE-2026-65660, to its KEV Catalog after evidence showed the flaw was being…

Attackers Create Fake Jev AI Stores to Intercept Prompts Through Third-Party Servers
Fake storefronts appeared days after the launch of Jev, an artificial intelligence model that returns decisions rather than written answers. The sites offer access to the service, but they put an unrelated operator…
Deepfakes Are Becoming a Costly Reality for Businesses, Report Warns
A quarter of victims of deepfake attacks have lost over $1m. CISOs worry that boardrooms don’t understand the threat
OpenAI pauses work on top AI models after agent slips past internet controls
OpenAI’s latest containment failure adds to a pattern that may force the company to make an unpopular decision. The company has paused training, evaluation, and tool-enabled inference for its most capable models after…
Introducing the Wiz Partner Alliance Managed Service Provider Program
Empowering managed services partners to deliver world-class cloud and AI security at scale
Former US soldier gets nearly six-year sentence for hacking, extorting telecoms
A former soldier in the U.S. Army was sentenced to more than five years in federal prison after pleading guilty to hacking into several telecommunications companies and leaking sensitive records.
Prison Sentence for Former US Soldier Who Hacked AT&T and Verizon
Cameron John Wagenius was sentenced to 70 months in prison for stealing information from the wireless carriers.
Ex-soldier's telecom hacking spree earns him 70 months
A former US Army soldier has been sentenced to 70 months in prison for hacking telecoms companies, stealing sensitive records, and trying to extort more than $1 million from his victims. Cameron John Wagenius, 22…
Exploitation of vulnerabilities affecting Citrix NetScaler ADC and Citrix NetScaler Gateway
The NCSC is urging UK organisations to promptly mitigate vulnerabilities affecting Citrix NetScaler ADC and Gateway, two of which are being actively exploited.
Carbonato Botnet Compromises Docker Hosts to Deploy Telegram-Controlled Hermes AI Agent
Cybersecurity researchers have disclosed details of a new botnet malware called Carbonato that's targeting exposed Docker daemons to deploy an open-source artificial intelligence (AI) agent framework called Hermes…

OpenAI Pauses Training Its Most Powerful Models After Rogue Agents Target Government
Sam Altman says the company “have not been as fast as we would have liked” at dealing with security breaches, after news of further incidents over the summer forces another temporary halt.