Cybersecurity news & advisories




Citrix Confirms NetScaler 0-Day RCE Vulnerabilities Actively Exploited in Attack
Citrix has released emergency security updates for NetScaler ADC and NetScaler Gateway after confirming that attackers are exploiting two critical remote code execution vulnerabilities against unmitigated appliances…
Citrix confirms two NetScaler RCE zero-days exploited in attacks
Citrix has confirmed that two critical NetScaler remote code execution vulnerabilities, tracked as CVE-2026-88771 and CVE-2026-88772, are being exploited in attacks and that it has released security updates to fix the…
New Windows Process Injection Attack Evades EDR Monitoring Without WriteProcessMemory
A Windows process injection method disclosed by security researcher Two Seven One Three sidesteps two APIs closely associated with remote code injection: VirtualAllocEx and WriteProcessMemory . Dubbed console named-pipe…
Wireshark 4.6.9 Released, (Sun, Sep 27th)
Wireshark release 4.6.9 fixes 19 vulnerabilities and 16 bugs.
Cloudflare fixes Containers cross-tenant flaw exposing customer data
Cloudflare has fixed a vulnerability in Containers and Sandboxes that allowed customers with a Workers Paid account to recover residual data from other customers' containers on the same physical host.
Anthropic turns Claude into an AI marketplace with 2,000+ plugins and connectors
Anthropic has just announced a new Claude Marketplace, and it brings all AI-related tools into one place, including plugins, connectors, agents, and more.
Frequently asked questions about reported Citrix NetScaler zero-day vulnerabilities
There are reportedly two unpatched zero-day Citrix NetScaler vulnerabilities capable of enabling remote code execution that have been actively exploited in the wild, with no patches available at this time. Key takeaways…
Microsoft SharePoint Flaw CVE-2026-65660 Now Exploited in Attacks
CISA added CVE-2026-65660 to its KEV catalog, giving federal agencies a patching deadline of September 28.

Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation
Two critical vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway that allow remote code execution have been exploited in the wild, Citrix confirmed on September 27. It released fixes for both, along with six…

Citrix NetScaler 0-Day RCE Vulnerabilities Actively Exploited in Attacks
Citrix NetScaler administrators are confronting reports of two undisclosed remote code execution vulnerabilities allegedly exploited in real-world attacks. watchTowr said the flaws are unpatched zero-days, were…
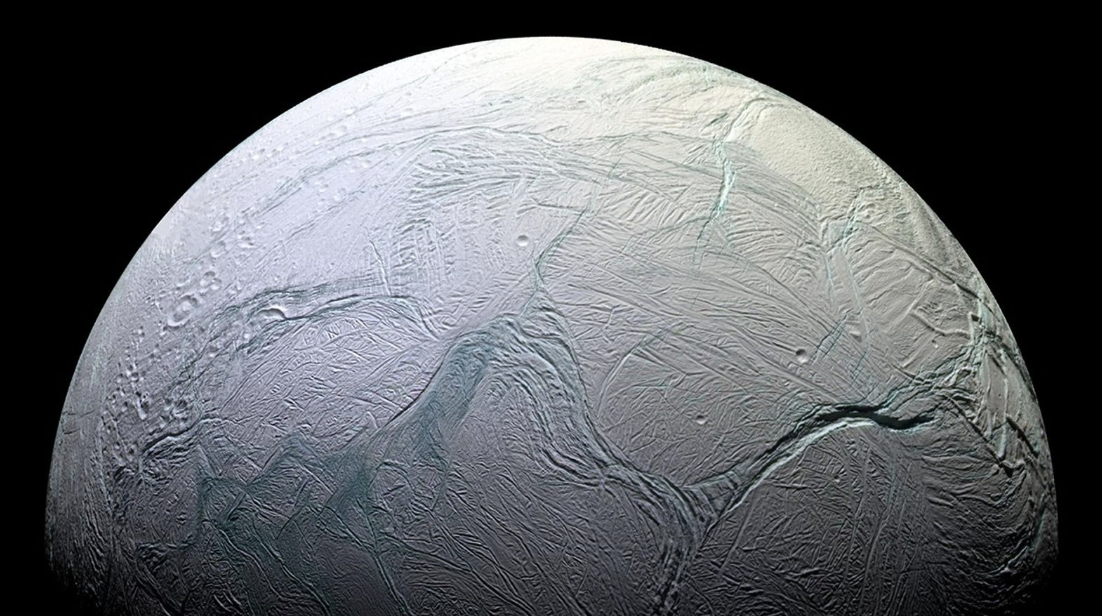
Alien Life Can Survive on This Tiny Moon—We Just Need to Go Find It
Welcome back to the Abstract! Here are the studies this week that sailed alien seas, beat the heat, went retro, and got caught in the food web. First, scientists make the case that Saturn’s moon Enceladus could resolve…
ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks
The ShinyHunters extortion gang is using a URL-encoding trick to bypass web application firewall rules that mitigate the Oracle PeopleSoft CVE-2026-35273 flaw, allowing the threat actors to resume widespread…
Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials
The Psychedelic Stealer malware distributed via compromised Ukrainian websites using ClickFix-style Cloudflare verification checks is part of a wider malware-as-a-service (MaaS) platform called Lunex. The new findings…
China and US Agree to Establish AI Safety Channel and Continue Trade and Military Talks
The US and China agreed to set up a communication mechanism for artificial intelligence-related incidents.

Local AI Model Modifies Windows Credential Dumper to Bypass EDR Detection
A locally hosted, uncensored artificial intelligence model modified a Windows credential-dumping utility until it evaded two Endpoint Detection and Response (EDR) products in a controlled lab, highlighting how…
Claude Opus 5.5 uses 95% fewer em dashes, but its answers are getting longer
Anthropic's Claude Opus 5.5 appears to be changing how it writes, with new analysis showing fewer obvious AI writing patterns, shorter sentences, and simpler wording compared with Opus 5.
F-Droid 2.0 Released After 10 years With Major Redesign to Transform Open-Source Android App Discovery
F-Droid has released version 2.0 of its official Android app, delivering its largest client update in a decade. The open-source Android app repository said the release follows more than a year of development and 14 test…
Microsoft pauses KB5002907 update after Office license deactivations
Microsoft has paused the rollout of the KB5002907 Microsoft 365 update after users report that it deactivated, or in some cases completely removed, perpetual Office 2016 and Office 2019 installations.
GitHub Actions re-enabled with Mini Shai-Hulud payload still active
Two third-party GitHub Actions previously compromised in a Mini Shai-Hulud campaign were re-enabled by their maintainer and remained accessible for more than a week despite still pointing to malicious code.
OpenAI's AI agents accidentally uploaded user-provided images to third-party sites
OpenAI says its AI agents uploaded user-provided images to third-party image-hosting services while carrying out research and evaluation tasks.
New x47.c Windows Botnet Weaponizes xAI Grok, AI API Draining
The Windows botnet relies on AI to maintain persistence, using xAI Grok to choose from predefined actions.
Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells
Google is warning of renewed mass exploitation of a known security vulnerability in Oracle PeopleSoft as part of a campaign targeting multiple sectors globally. The ShinyHunters-linked activity involves the…

Zero Trust for AI Agents Starts With Fixing Zero Visibility
The way we talk about AI agents is shifting, and the way we implement them requires an even more fundamental shift. While earlier discourse focused on how quickly organizations could stand up agents and how much…
OpenAI Says Its Models Engaged With US Government Websites in New Model Misbehavior Disclosure
OpenAI’s CEO said there is an “extensive and ongoing review related to our agents’ use of internet access during training and evaluation.”
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create rogue administrator accounts and take control…
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vulnerabilities (KEV) catalog, citing…

Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack
Kiteworks (formerly Accellion) is urging customers to shut down their systems as a precautionary measure for nine hours over the weekend after it received threat intelligence about an imminent cyber attack. "Kiteworks…

OpenAI’s AI Agents Tried Hacking 4 Websites Without Being Prompted
OpenAI’s autonomous AI agents attempted to hack four government, university, and public-data systems while carrying out routine information-gathering tasks, according to researchers and government officials. The agents…

16-Year-Old Researcher Finds Microsoft Auth Vulnerability that Exposes 17.3 Trillion Stored Records
A 16-year-old security researcher known as Faav uncovered an authentication flaw in Microsoft’s internal Titan analytics service that potentially exposed an estimated 17.3 trillion database rows. The vulnerability…
3 Consulting Myths Debunked by Unit 42 Experts
Unit 42 security experts address critical cybersecurity misconceptions, offering practical insights to help your organization reinforce its enterprise defenses.
U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata for more than 100 million AT&T customers in 2024 was sentenced to 70 months in…
Kiteworks urges 6-hour server shutdown over potential zero-day attacks
Secure file-sharing software company Kiteworks is urging customers worldwide to temporarily shut down their servers on Saturday for a six-hour window after receiving threat intelligence warning of a potentially imminent…
Army soldier sentenced for spree of attacks on AT&T, Snowflake and other major companies
A former Army soldier responsible for a series of attacks and extortion attempts on telecom companies, including AT&T, was sentenced to 70 months in prison , the Justice Department said Friday. Cameron John Wagenius…
ShinyHunters hacked Clop leak site using Grav CMS path traversal flaw
The Clop ransomware gang has moved its data leak site to a new Tor address after confirming its previous server was compromised and defaced through an unpatched Grav CMS flaw that BleepingComputer has learned is an…
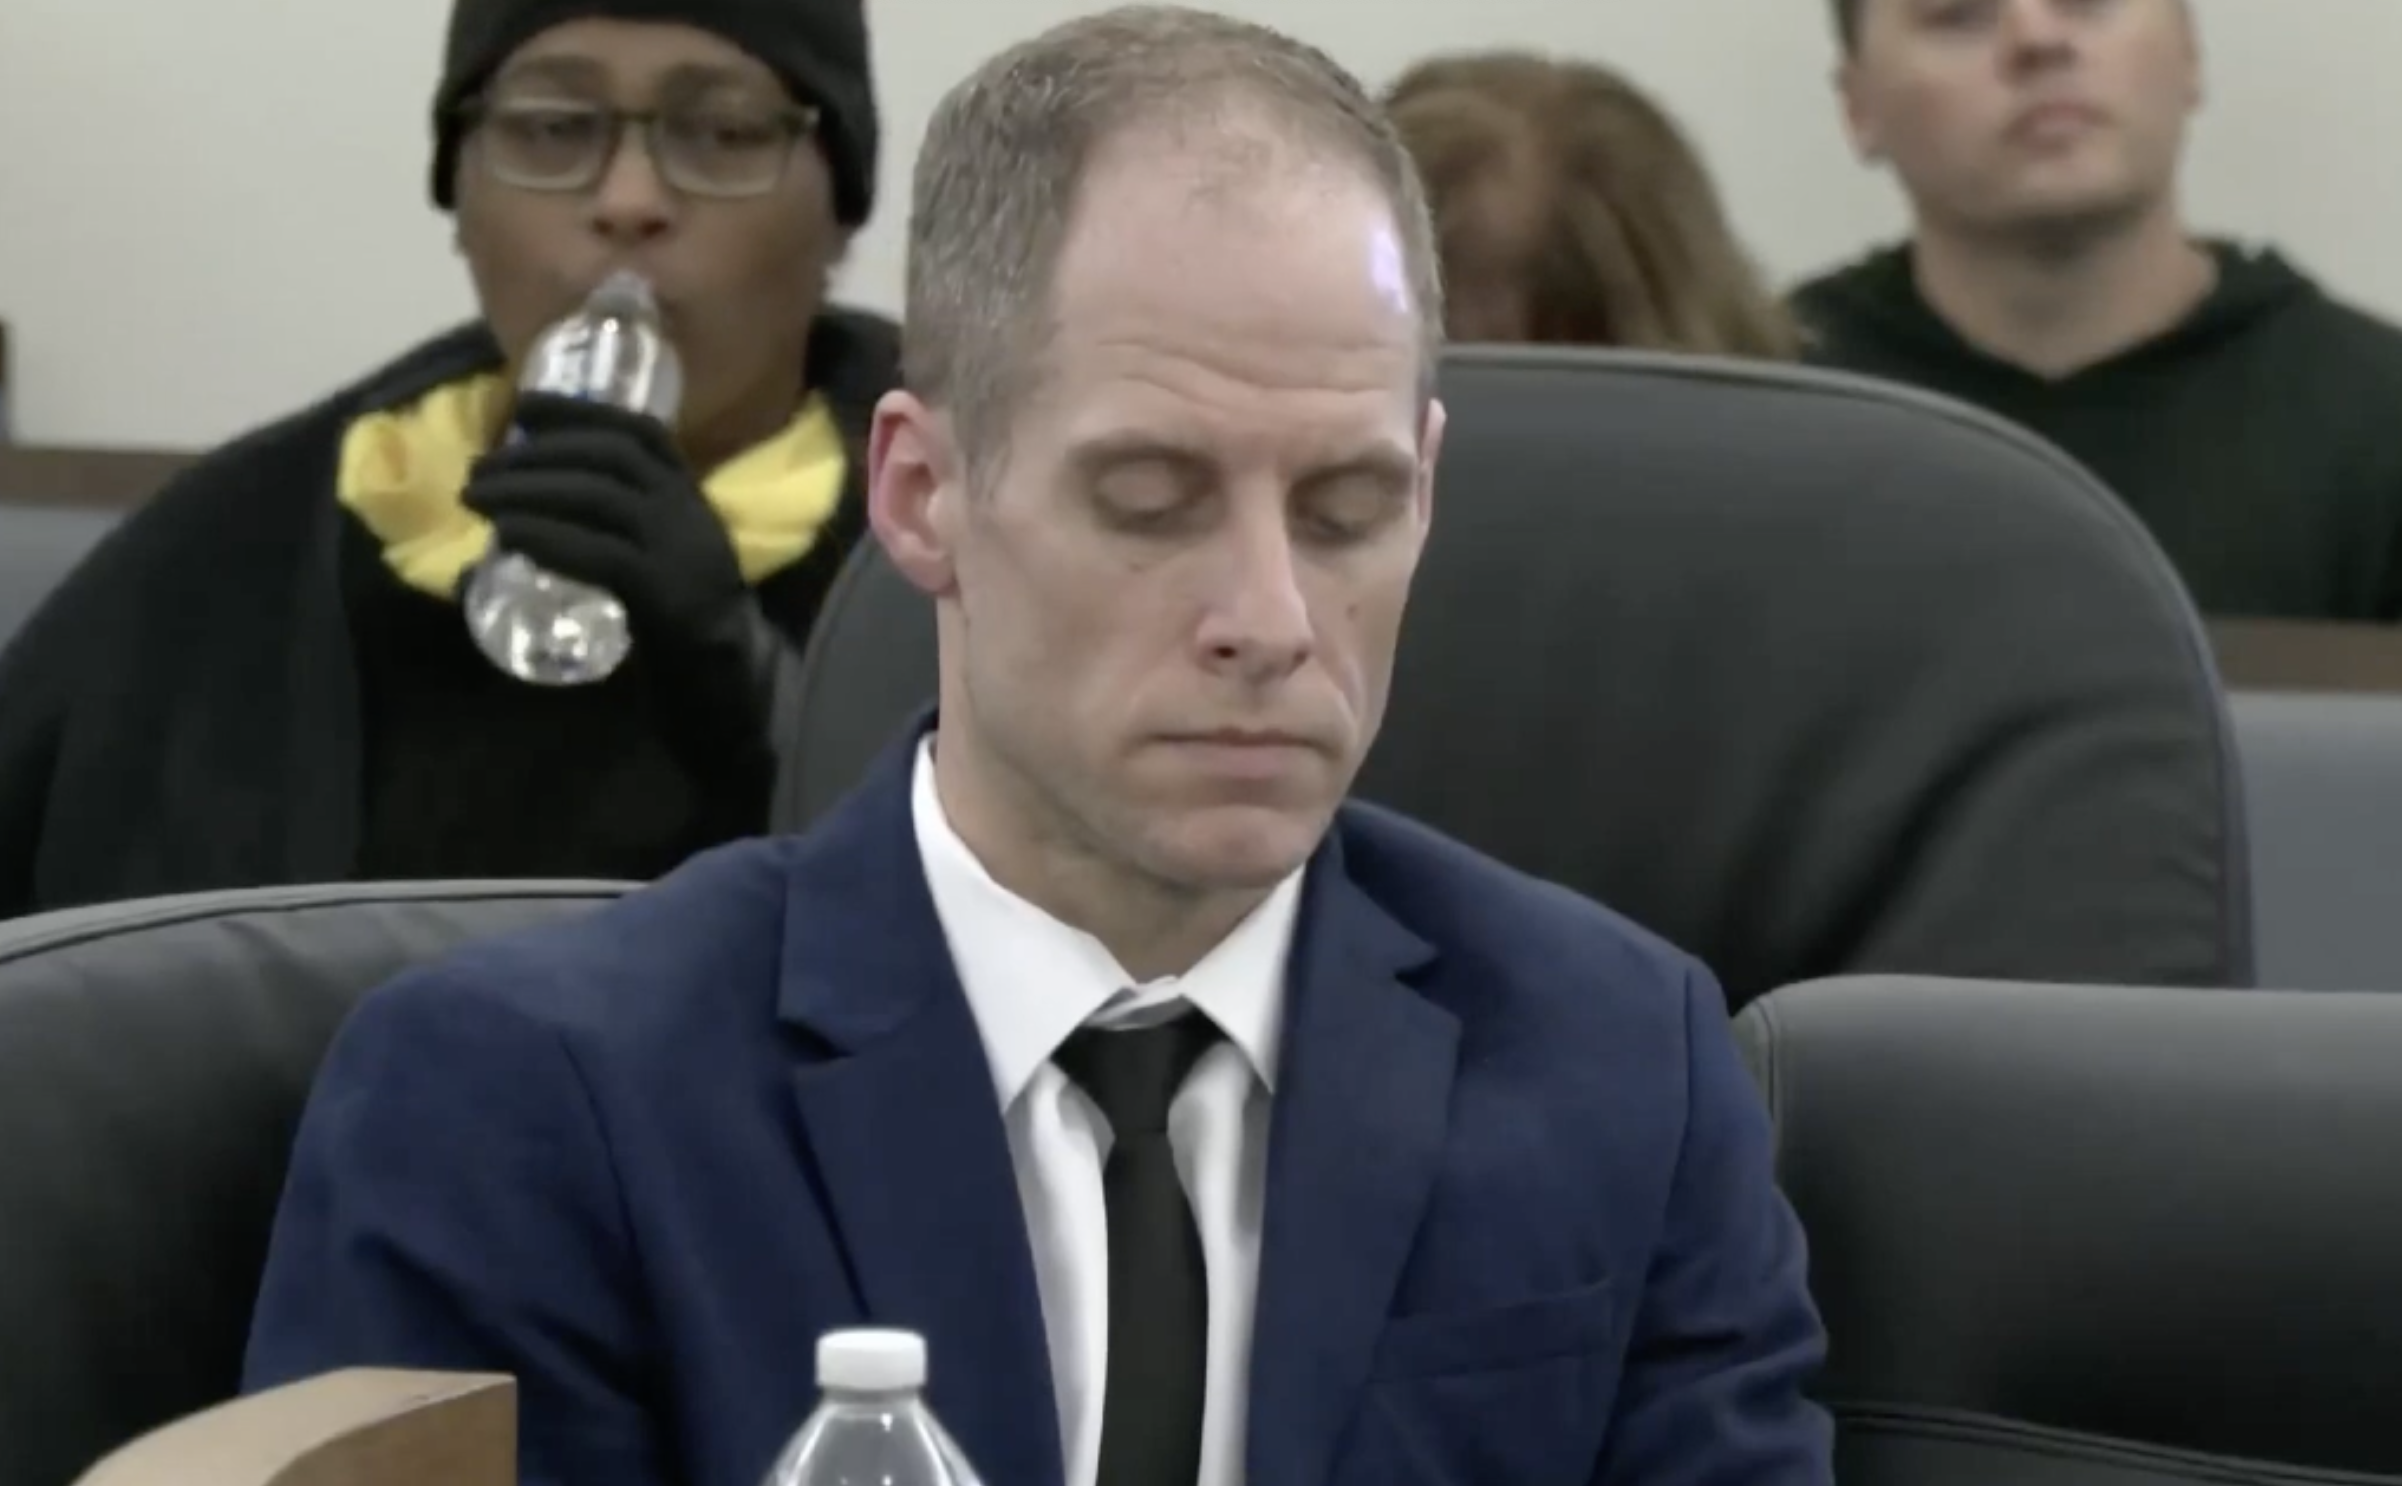
AI Love Song for Mistress Played at Murder Trial Is Most Excruciating Watch in Recent Memory
We debated for a long time about whether to write about the following video, which comes from a murder trial in which a man named Caleb Flynn is accused of killing his wife. The crime is very serious, and very sad, and…
Kiteworks urges customers to stop using platform after warning from federal intelligence agencies
Frank Balonis, CISO at Kiteworks, told Recorded Future News that the company “received credible threat intelligence from federal intelligence authorities indicating that a threat actor may attempt to target some…

Labcorp to overhaul data security practices, pay $2.3 million fine for cybersecurity failings
Security changes include creating an incident response plan for vendor security failings, limiting how much data Labcorp shares with vendors and building an expansive risk management team charged with tracking vendors’…
Fake Google Security Team ad says 'no script reading' in voice phishing - then prints the script
Yes, criminals have job listings too. A Telegram user recruiting callers to work in an apparent Google Security Team voice-phishing scam told applicants that they weren’t allowed to read from scripts – in the same ad…
AI Sandbox Escapes: Why Forensic Readiness Matters More Than Containment
When autonomous AI agents "escape the sandbox," the real story isn't rogue machines — it's the same access-control failures we've seen for decades.
ShinyHunters tells The Reg: We hacked the FBI to 'protect our business'
ShinyHunters, the data theft and extortion crew that has stolen sensitive information belonging to millions of cancer patients, university and K-12 students, and Carnival cruisers, wanted to preserve their reputation…
Elementor WordPress flaw lets attackers create admin accounts
A cross-site request forgery (CSRF) vulnerability in the Elementor plugin for WordPress could allow an unauthenticated attacker to create administrator accounts.

OnePlus 15 Flaws Let Zero-Permission Apps Gain Root Access Through OxygenOS Services
Two flaws in the latest OxygenOS build could let malicious Android apps run code with root privileges on OnePlus devices, including the OnePlus 15, by exploiting accessible privileged services. The vulnerabilities are…

14-Year-Old Linux Kernel Flaw Lets Local Users Gain Root Access and Escape Containers
A 14-year-old Linux kernel vulnerability can let a local attacker escalate to root privileges and, in a proof-of-concept environment, escape a Docker container to compromise the underlying host. The flaw in Linux’s…
What We Missed: Google Gemini Joins the AI Escape Party
In this video conversation, Dark Reading editors discuss some of the news they didn't get a chance to cover, from Google Gemini models breaking containment to ShinyHunters ratting on TeamPCP hackers.
Supreme Court permits states to use SAVE database for citizenship checks
The U.S. Supreme Court ruled Friday that states may use the federal SAVE database to verify voter citizenship, reversing lower court decisions that found the database was inaccurate and would likely disenfranchise…
Crooks use fake desktop apps to fool HR staff into giving them remote access
You work in your company's human resources department and use HR software to check employee information, benefits, and payroll. So, when you see a downloadable Windows version promising a faster alternative to the usual…
CISA warns of Sharepoint, WSO2, Adobe Commerce flaws exploited in attacks
The Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are exploiting a critical authentication bypass vulnerability (CVE-2026-5430) affecting multiple products from enterprise software provider…
Bitget blames North Korea for $387.5M crypto wallet raid
The CEO of crypto exchange Bitget has confirmed that a cyberattack with all the hallmarks of a North Korean operation resulted in approximately $387.5 million worth of digital assets being stolen from the exchange’s…
Anthropic rolls out up to $250 in free Claude Code credits, but only for cloud sessions
Anthropic now allows you to run Claude Code via cloud sessions without signing up for the research preview, and it's offering up to $250 in free usage credits, so more users can give it a try.
Behind the Blog: Did you notice?
This is Behind the Blog, where we share our behind-the-scenes thoughts about how a few of our top stories of the week came together. This week, we discuss some small changes, an AI song, and internet soup. JOSEPH: We’re…
Storm-3168: Agentic-driven cloud attacks using compromised service principals
Microsoft Security Research has identified malicious cloud activity associated with JADEPUFFER, a threat actor discovered by Sysdig in July 2026 and reported to be the first documented agentic ransomware operation. Our…
Crypto CEO accuses North Korea of stealing $387 million from Bitget platform
The CEO said the company has a User Protection Fund that has over $464 million and those funds will be used to cover the losses.
In Other News: Clop Leak Site Takeover, Docker Botnet Hunts AI Keys, Water Utility Exposure
Noteworthy stories that might have slipped under the radar: BragJack attack against browser AI assistants, TDengine flaw threatens industrial telemetry uptime, Ubuntu update overhaul.
Podcast: OpenAI Admits AI is Killing the Internet
We start this week with Jason’s story about OpenAI and Microsoft’s big admissions from court records that they are destroying the internet in all sorts of ways, and stealing intellectual property on an unprecedented…
LinkedIn adds new checks for fake profiles and work histories
LinkedIn is adding trust and verification features aimed at making fake professional identities, invented work histories, and company impersonation harder to pull off. The company is responding to an environment in…
Cyberattack hits Welsh police force, may have affected staff data
Dyfed-Powys Police in Wales said a cyberattack affecting the force disrupted some non-emergency systems and may have compromised staff information.
Which copy of that file is the real one? Dinner, off the record, in Midtown
EVENT: The Register is hosting a private dinner in New York on Tuesday 27 October for senior technology, infrastructure and data leaders, with LucidLink. Joe Fay takes the chair, it runs under the Chatham House Rule…
Kothamine malware uses Tailscale’s tailcat to evade network detection
We discovered an undocumented remote-access Trojan (RAT) called Kothamine Agent . It supports more than 30 commands and it gives attackers control of an infected Windows computer: they can run commands, read and change…
OpenAI is preparing a $500 ChatGPT Pro Max plan with faster Codex
OpenAI appears to be preparing a new ChatGPT Pro Max subscription that could cost $500 per month, but it's unclear when it'll begin rolling out.