3Hackers Breach Meta GitHub Repositories, Steal Source Code and Data of 1,500 PeopleAny.Run Malware AnalysisCyber Security NewsSecurityWeekThe Hacker News+1Hackers used an employee’s stolen credentials to access some of Meta’s GitHub repositories, taking product source code and personal information linked to roughly 1,500 people. Most affected individuals are Meta employees in the United States, according to the company’s disclosure to SecurityWeek. Meta confirmed the breach on October 13, 2026, when it began notifying affected people. The company said it detected the intrusion several weeks earlier, blocked the attackers’ access, and brought in GitHub and law enforcement to support its response. Stolen Credentials Opened Repository Access Meta…
4Attackers Breach European Bank Through Third-Party Gateway and Target WSUS ServerBleeping ComputerCyber Security NewsMicrosoft SecurityThe Hacker News+1CVE-2026-105725 ↗CVE-2026-108457 ↗CVE-2026-108468 ↗A European bank was breached through a poorly secured, third-party gateway before an attacker tried to exploit its Windows Server Update Services (WSUS) infrastructure. The case shows how stolen login details and weak access controls can put a bank’s central software systems at risk without a complex attack chain. The bank’s security team uncovered unauthorized VPN access attempts stretching across several months after spotting unusual activity on its central IT system. Investigators traced the intrusion to an external gateway managed by a third party, where strict authentication had not been…
6How to Run a Deepfake Readiness Drill Before a Cloned Voice Calls Your TeamInfosecurity MagazineThe Hacker NewsWiz ResearchCloned voices and synthetic video calls now show up in payment fraud, help desk resets, and access requests. A structured drill shows security teams exactly where verification breaks down, while nothing is at stake. The call comes in at 4:40 on a Friday. It's the CFO, or it sounds exactly like her, asking the controller to push a supplier payment out before the weekend because a deal closes
8Ivanti Connect Secure zero-day exploited in the wild (CVE-2026-104935)CISA Alerts & AdvisoriesRapid7 BlogSecurityWeekCVE-2026-104935 ↗CVE-2026-96951 ↗Overview On October 13, 2026, Ivanti published a security advisory for CVE-2026-104935 , a high-severity authentication bypass by spoofing ( CWE-290 ) affecting Ivanti Connect Secure (ICS). The vulnerability has a CVSSv3.0 score of 8.6 and allows a remote, unauthenticated attacker to execute arbitrary commands. Ivanti reports that exploitation in the wild has already occurred prior to disclosure, affecting a limited number of customers. This indicates that exploitation has been occurring as a zero-day vulnerability. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) confirms…
9CVE-2026-97229: Critical Unauthenticated Remote Code Execution in GitLabCCCS Alerts & AdvisoriesRapid7 BlogThe Hacker NewsCVE-2026-97229 ↗Overview On October 12, 2026, GitLab published a critical patch release for CVE-2026-97229 , an integer overflow or wraparound ( CWE-190 ) in the CI/CD regular expression compiler affecting GitLab Community Edition (CE) and Enterprise Edition (EE). GitLab assigned the vulnerability a CVSSv3.1 score of 10.0 . Under certain conditions, a remote attacker can execute arbitrary code on an affected GitLab server through a specially crafted regular expression stored in a malicious CI/CD configuration. While the vendor supplied CVSS score indicates that exploitation is fully unauthenticated, in…
11Microsoft’s October 2026 Patch Tuesday addresses 1407 CVEs (CVE-2026-96951)SecurityWeekTenable BlogCVE-2026-96951 ↗69 Critical 1337 Important 0 Moderate 1 Low Microsoft addresses 1407 CVEs in the tenth Patch Tuesday of 2026, marking the second consecutive month to reset the bar as the largest Patch Tuesday release. This month’s updates include patches for two zero days, including one that was exploited in the wild. Microsoft patched 1,407 CVEs in its October 2026 Patch Tuesday release, with 69 rated critical, 1,337 rated as important, and one rated as low. This month’s update includes patches for 301 products and components. The following table lists the products with the most CVEs patched this month. A…
12Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security ChecksBleeping ComputerThe Hacker NewsCybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed to bypass security checks from inside the app itself, marking a new escalation in financial fraud. Dutch mobile security company ThreatFabric said it identified replacements for eight Indonesian banking
13Bring Your Own Agent: Your Employees' Assistants Are Already Logged InMalwarebytes LabsThe Hacker NewsThe personal AI agents rollout is going about as smoothly as expected: Amazon now blocks Meta's Muse because it doesn't identify itself as a bot while browsing; Instinct keeps raising privacy concerns; and the horror stories from pretty much every personal AI agent keep piling up. Regardless, the tech world is mesmerized by the capabilities and potential of these services. Less than a year
The sixth exploited Ivanti bug this year drew attention from the feds and researchers, while a severe Microsoft vulnerability was one of more than 1,400 listed for Patch Tuesday.
The Joint Economic Committee on Tuesday released the results of a year-long investigation into Tinder, Hinge, Match, Plenty of Fish and several other dating sites owned by Match Group.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the latest version…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the latest version following the disclosure of an actively exploited vulnerability. The security flaw, tracked as CVE-2026-104935 (CVSS score: 8.6), is a case of authentication bypass impacting ICS
A flaw in how curl handles HTTP/2 uploads lets a malicious server receiving an upload corrupt the client's memory, and the researcher who reported it turned that into code execution on the uploading machine. The curl…
A flaw in how curl handles HTTP/2 uploads lets a malicious server receiving an upload corrupt the client's memory, and the researcher who reported it turned that into code execution on the uploading machine. The curl project fixed it on October 14 in curl 8.23.0. Taking over a client needs exact knowledge of its build and memory layout, and curl expects a real attack to end in a crash
Cloned voices and synthetic video calls now show up in payment fraud, help desk resets, and access requests. A structured drill shows security teams exactly where verification breaks down, while nothing is at stake. The…
Cloned voices and synthetic video calls now show up in payment fraud, help desk resets, and access requests. A structured drill shows security teams exactly where verification breaks down, while nothing is at stake. The call comes in at 4:40 on a Friday. It's the CFO, or it sounds exactly like her, asking the controller to push a supplier payment out before the weekend because a deal closes
A new Android malware called Hirudo steals bank account credentials by replacing legitimate banking apps with modified versions that disable security checks.
Microsoft’s October Patch Tuesday release addresses a record-breaking 1,413 vulnerabilities , including an actively exploited Windows Shell zero-day and two other publicly disclosed flaws. Just when you thought a…
Microsoft’s October Patch Tuesday release addresses a record-breaking 1,413 vulnerabilities , including an actively exploited Windows Shell zero-day and two other publicly disclosed flaws. Just when you thought a previous record would stand for a while, Microsoft comes out again with the largest monthly Patch Tuesday release. Microsoft has said its growing use of AI to find and fix security vulnerabilities means users should expect more fixes in its monthly updates. How to apply patches and check if you’re protected These updates fix security problems and help keep your Windows PC protected…
A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the user only loads a web page, the company said. Its researchers built the…
A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the user only loads a web page, the company said. Its researchers built the attack in six days by directing AI agents running OpenAI's publicly available GPT-5.6 Sol model. Google has since confirmed all three bugs, fixed them, and paid XBOW its top $
We found a wave of websites posing as Calendly booking pages for job interviews at Meta. Visitors pick a slot for a 30-minute phone call with a recruiter, fill in their details, and pass what looks like a CAPTCHA. Then…
We found a wave of websites posing as Calendly booking pages for job interviews at Meta. Visitors pick a slot for a 30-minute phone call with a recruiter, fill in their details, and pass what looks like a CAPTCHA. Then the page asks them to log in to Facebook. The interview is fake. The pages are designed to steal the visitor’s Facebook login details, including the two-factor authentication (2FA) codes meant to protect the account. Visitors are then asked to sign in to their Google account too, supposedly “for security.” These pages are not affiliated with Meta, Calendly, or Google. If you’ve…
Cybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed to bypass security checks from…
Cybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed to bypass security checks from inside the app itself, marking a new escalation in financial fraud. Dutch mobile security company ThreatFabric said it identified replacements for eight Indonesian banking
The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR During an authorized assessment, an AI pentesting agent found a critical authentication…
The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR During an authorized assessment, an AI pentesting agent found a critical authentication bypass on a major insurer's production website, on its own. One login request let the user choose where the one-time passcode went. The attack was the easy part. Proving it
I tested 25 of the most popular package managers to check whether they detect a compromised package repository injecting malicious code into legitimate packages. This code integrity problem could be solved using…
I tested 25 of the most popular package managers to check whether they detect a compromised package repository injecting malicious code into legitimate packages. This code integrity problem could be solved using cryptographic hashes or signatures, but many package managers are still vulnerable to this threat. Of the 25 package managers reviewed 1 , fewer than half used lockfiles that checked for tampering by default, and only two verified the integrity of every package they downloaded. Supply-chain attacks caused by developer compromise are a common story, but imagine what happens if ongoing…
Microsoft has confirmed that non-admin users may be unable to connect to devices via Remote Desktop after installing recent Windows updates if the "Administrator protection" security feature is enabled.
VirusTotal can now bring threat intelligence into ChatGPT through VirusTotal AI (VTAI), allowing users to investigate suspicious files, URLs, domains, and IP addresses within a conversation. The connection helps…
VirusTotal can now bring threat intelligence into ChatGPT through VirusTotal AI (VTAI), allowing users to investigate suspicious files, URLs, domains, and IP addresses within a conversation. The connection helps analysts retrieve existing reports and explain detection results while keeping the source, analysis date, and coverage visible. The integration uses Model Context Protocol (MCP), a standard that connects AI tools with external services. VirusTotal’s ChatGPT connection guide describes setup through Developer mode and an OAuth connection. Users sign in with Google through VTAI without…
Police tip hotlines already have their fair share of crank callers. Apparently they now have to contend with crank AI agents as well. AI agents have already been caught hacking software companies , breaching an…
Police tip hotlines already have their fair share of crank callers. Apparently they now have to contend with crank AI agents as well. AI agents have already been caught hacking software companies , breaching an Australian government portal , and trying to hack a Canadian government website . Now Anthropic’s Claude has added a made-up murder tip to the list. Claude’s Haiku 4.5 model filed a false tip in an unsolved Philadelphia homicide via the police department’s online public tip form, Anthropic disclosed . The tip was flagged as spam and didn’t reach investigators. AI’s latest “what does…
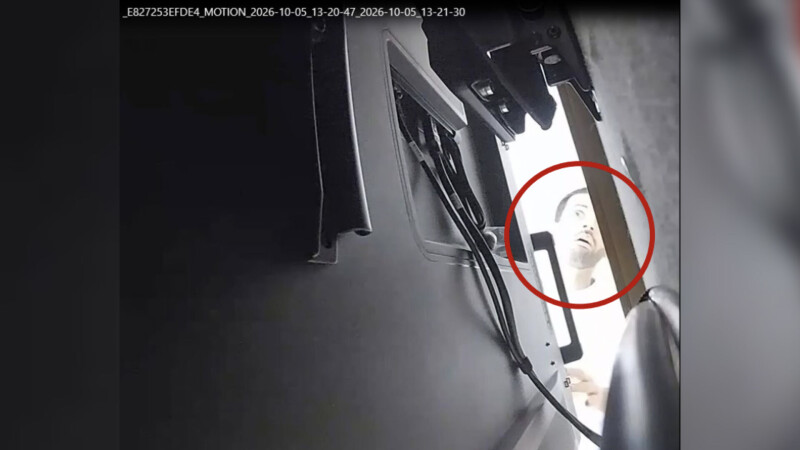
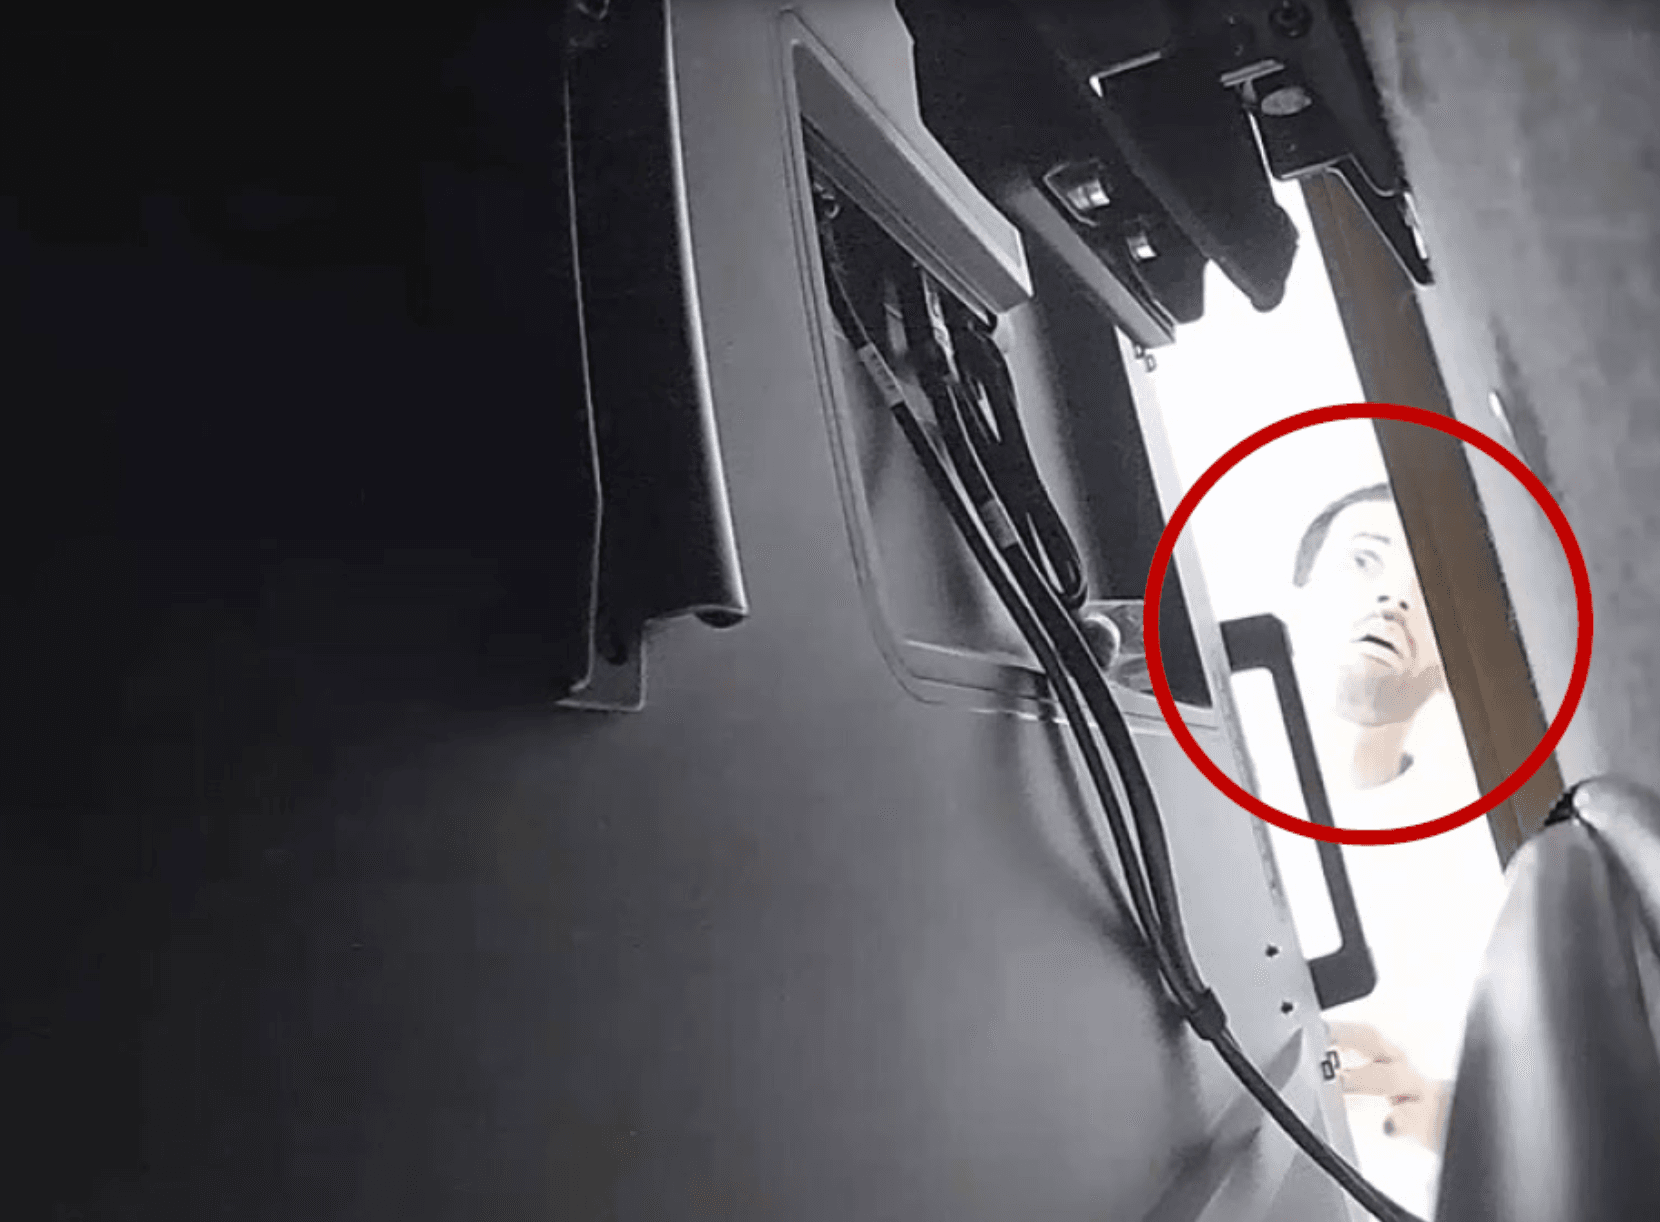
The Department of Justice has charged an OpenAI engineer with attempting to intercept oral communications after allegedly planting a recording device in an exec conference room. Investigators claim company security…
The Department of Justice has charged an OpenAI engineer with attempting to intercept oral communications after allegedly planting a recording device in an exec conference room. Investigators claim company security staff found a second device in his bag. Saudi national Abdulrahman Alfozan, 35, is described in court documents as an engineer at OpenAI who had worked there since July 2025, and has held permanent residency in the US since September 2020. He was arrested on October 9 and made his initial federal court appearance on October 13. He is accused of installing, on or around September…
Security researchers earned a $250,000 reward from Google after building a full-chain Chrome exploit with AI agents. The XBOW team says the work took six days and about $40,000 in computing costs, using OpenAI’s…
Security researchers earned a $250,000 reward from Google after building a full-chain Chrome exploit with AI agents. The XBOW team says the work took six days and about $40,000 in computing costs, using OpenAI’s publicly available GPT-5.6 Sol model . Google has fixed the flaws. XBOW disclosed the work on October 13, 2026. Its chain linked three bugs to move from JavaScript in a Chrome tab to code execution outside the browser’s renderer sandbox. The company estimated that the issue could affect about one billion users worldwide, while the demonstration targeted Windows. Google Awards $250K…
Microsoft has released fixes for a Windows SmartScreen vulnerability that allows an attacker with local access to gain higher privileges. Tracked as CVE-2026-85851, the flaw was disclosed on October 13, 2026, and…
Microsoft has released fixes for a Windows SmartScreen vulnerability that allows an attacker with local access to gain higher privileges. Tracked as CVE-2026-85851, the flaw was disclosed on October 13, 2026, and carries a CVSS base score of 7.8. Microsoft rates it Important. The issue involves a use-after-free memory error and affects several Windows 11 releases and Windows Server 2025. According to the supplied Microsoft advisory, successful exploitation lets an attacker move from a low integrity level to a medium integrity level. This is a specific increase in access, not a confirmed path…
Two powerful iPhone exploit kits, Coruna and DarkSword, show how a visit to a malicious or compromised website can put an outdated device at risk. The kits can link several software flaws together to break out of the…
Two powerful iPhone exploit kits, Coruna and DarkSword, show how a visit to a malicious or compromised website can put an outdated device at risk. The kits can link several software flaws together to break out of the browser and reach deeper parts of iOS. Depending on the device’s software version and the kit used, an attacker may then steal sensitive information without needing the user to install an app or tap through extra prompts. These are not ordinary malicious webpages. An exploit kit is a set of tools that checks a visitor’s device and selects code designed for its software. Coruna…
ANY.RUN researchers tracked fake AI tool campaigns that impersonate Claude, ChatGPT, GitHub Copilot, Gemini, and other AI brands to plant infostealers, take over browser sessions, and phish business accounts. Between…
ANY.RUN researchers tracked fake AI tool campaigns that impersonate Claude, ChatGPT, GitHub Copilot, Gemini, and other AI brands to plant infostealers, take over browser sessions, and phish business accounts. Between April 15 and October 5, 2026, 1,258 public sandbox analyses were tied to these campaigns, and the USA was the second-largest source of submissions after India. The attacks share one trait: the employee performs the decisive step. They paste an “install command,” run a convincing installer, or sign in to a fake window. That can put source code, cloud and AI API keys, active…
Hackers used an employee’s stolen credentials to access some of Meta’s GitHub repositories, taking product source code and personal information linked to roughly 1,500 people. Most affected individuals are Meta…
Hackers used an employee’s stolen credentials to access some of Meta’s GitHub repositories, taking product source code and personal information linked to roughly 1,500 people. Most affected individuals are Meta employees in the United States, according to the company’s disclosure to SecurityWeek. Meta confirmed the breach on October 13, 2026, when it began notifying affected people. The company said it detected the intrusion several weeks earlier, blocked the attackers’ access, and brought in GitHub and law enforcement to support its response. Stolen Credentials Opened Repository Access Meta…
A European bank was breached through a poorly secured, third-party gateway before an attacker tried to exploit its Windows Server Update Services (WSUS) infrastructure. The case shows how stolen login details and weak…
A European bank was breached through a poorly secured, third-party gateway before an attacker tried to exploit its Windows Server Update Services (WSUS) infrastructure. The case shows how stolen login details and weak access controls can put a bank’s central software systems at risk without a complex attack chain. The bank’s security team uncovered unauthorized VPN access attempts stretching across several months after spotting unusual activity on its central IT system. Investigators traced the intrusion to an external gateway managed by a third party, where strict authentication had not been…
Gear of War: E-Day players faced login failures, sudden disconnects, and other online service problems after distributed denial-of-service attacks targeted the game’s online services. The official Gears Community…
Gear of War: E-Day players faced login failures, sudden disconnects, and other online service problems after distributed denial-of-service attacks targeted the game’s online services. The official Gears Community account confirmed the cause on X, linking the disruption to DDoS activity and ending speculation about the source of the failures. The Gears Community reported attacks on its online services that caused intermittent disconnects, login issues, and other disruptions, but did not identify the attackers, disclose traffic figures, or specify affected services, limiting details about the…
Google released a Chrome security update that addresses 37 vulnerabilities, including seven critical flaws that raise concerns about memory corruption and possible code execution . Published on October 13, 2026, the…
Google released a Chrome security update that addresses 37 vulnerabilities, including seven critical flaws that raise concerns about memory corruption and possible code execution . Published on October 13, 2026, the update covers Windows, Mac, and Linux, with fixes spanning graphics, PDF handling, media processing, networking, and other browser components. According to Google’s Stable Channel Update for Desktop, the patched versions are 155.0.8059.79/.80 for Windows and Mac, and 155.0.8059.79 for Linux. The release includes seven critical, 29 high, and one medium-severity security fixes…
Attackers chained three zero-day flaws in Ivanti Connect Secure VPN appliances to gain root-level access without logging in, then searched for credentials and sensitive Active Directory data. The activity, which began…
Attackers chained three zero-day flaws in Ivanti Connect Secure VPN appliances to gain root-level access without logging in, then searched for credentials and sensitive Active Directory data. The activity, which began on October 3, 2026, targeted a fully patched appliance running version 22.8R2.4, showing that keeping a device current did not protect it from these previously unknown flaws. Volexity found the intrusion while investigating suspicious activity at a customer and worked with Ivanti to examine the affected device. The security firm tracks the previously unknown actor as UTA0576…
A flaw in Linux's vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted virtual machine write…
A flaw in Linux's vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted virtual machine write to the host's memory and hijack the program that runs the virtual machine. The bug is tracked as CVE-2026-74580 and named Vghost. Tencent Zhuque Lab, which found the
Microsoft fixed three Windows BitLocker vulnerabilities CVE-2026-85920, CVE-2026-88070, and CVE-2026-83500 that could enable privilege escalation or bypass security protections in its October 2026 updates . BitLocker is…
Microsoft fixed three Windows BitLocker vulnerabilities CVE-2026-85920, CVE-2026-88070, and CVE-2026-83500 that could enable privilege escalation or bypass security protections in its October 2026 updates . BitLocker is a core Windows disk-encryption feature designed to protect data if a laptop, desktop, or storage drive is lost or stolen. It helps prevent someone from reading protected files by removing a drive and connecting it to another system. The newly disclosed issues do not mean BitLocker encryption has been broken. Instead, they affect parts of the Windows BitLocker implementation…
Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over. The protected area is a VBS enclave, an isolated slice of…
Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over. The protected area is a VBS enclave, an isolated slice of memory the operating system uses to guard secrets, and the one they broke into handles passwords for a Windows anti-phishing feature. The work was done in a lab as a proof of
Organizations are reporting that employees face threats to their families, stalking, physical violence, and abduction. But these alarming claims are hard to verify.
Tim Beasley, a senior incident response consultant at Semperis, was investigating a cyberattack involving Russia’s Midnight Blizzard when a package containing nesting dolls and other regional gifts showed up on his…
Tim Beasley, a senior incident response consultant at Semperis, was investigating a cyberattack involving Russia’s Midnight Blizzard when a package containing nesting dolls and other regional gifts showed up on his doorstep. At the time, Beasley served as the lead investigator for Microsoft’s Detection and Response Team (DART). He assumed it was from the group, which has been linked to the Kremlin’s Foreign Intelligence Service (SVR), although the sender didn’t leave a note. “Just little souvenirs and gift basket stuff from that area of the world,” he told The Register. “We-know-where-you-are…
On this week’s show Patrick Gray and James Wilson are joined by special guest co-host Brad Arkin to talk through the week’s cybersecurity news, including: Sacré bleu! Hackers turn up the heat at French supermarket…
On this week’s show Patrick Gray and James Wilson are joined by special guest co-host Brad Arkin to talk through the week’s cybersecurity news, including: Sacré bleu! Hackers turn up the heat at French supermarket freezers ShinyHunters enters “find out” stage Netscaler, Zimbra, SharePoint, Atlassian…. So many bugs exploited in the wild More models “behave badly” (by… doing exactly what we’re telling them to do) Ukraine hit another Yandex data centre in Russia and all those Texan patriots with numbers in their usernames have gone super quiet Much, much more… This week’s show is brought to you…
Microsoft on Tuesday shattered its own Patch Tuesday record by shipping patches for a whopping 1,413 vulnerabilities, including one that it said has come under active exploitation. These include 1,102 flaws in Windows…
Microsoft on Tuesday shattered its own Patch Tuesday record by shipping patches for a whopping 1,413 vulnerabilities, including one that it said has come under active exploitation. These include 1,102 flaws in Windows, 134 in Office, 61 in Developer Tools, 36 in SharePoint Server, and 22 in SQL Server. Of these, more than 670 relate to privilege escalation, followed by over 300 remote code
A Saudi national and employee of OpenAI has been arrested for allegedly planting a hidden recording device in an executive conference room at the company's San Francisco offices to covertly record sensitive…
A Saudi national and employee of OpenAI has been arrested for allegedly planting a hidden recording device in an executive conference room at the company's San Francisco offices to covertly record sensitive conversations. Abdulrahman Alfozan, 35, has been charged with using or endeavoring to use an electronic, mechanical, or other device to intercept oral communications. He was arrested by
Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software. Today’s epic patch batch dwarfs September’s record of nearly 1,000 fixes, which was…
Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software. Today’s epic patch batch dwarfs September’s record of nearly 1,000 fixes, which was already about ten times the normal monthly patch load from Redmond. Just one of the weaknesses patched this week is considered a “zero day,” or already exploited in the wild. CVE-2026-96951 is a security feature bypass in the Windows Shell that affects Windows 10 and 11 systems, as well as some Server versions. Windows 10 users might be wondering if they can still expect security…
Abdulrahman Alfozan, 35, a Saudi national working as an engineer for OpenAI, was charged Tuesday with secretly bugging an executive conference room at one of the company’s buildings in San Francisco.
A Saudi OpenAI engineer has been arrested for allegedly planting a hidden recording device in an executive conference room at the company's San Francisco offices to secretly record sensitive conversations.
Ivanti customers are in familiar territory, responding to yet another actively exploited zero-day affecting one of the vendor’s most commonly targeted security products. Volexity researchers, which discovered…
Ivanti customers are in familiar territory, responding to yet another actively exploited zero-day affecting one of the vendor’s most commonly targeted security products. Volexity researchers, which discovered in-the-wild exploitation earlier this month, said attackers actually exploited three zero-days in a chain that allowed them to bypass authentication, execute code remotely and escalate privileges. Ivanti disclosed and issued a patch for the authentication bypass and remote-code execution components of the exploit chain as a single vulnerability in Ivanti Connect Secure. The company said…
Unit 42 dissects a cyberattack targeting a European bank's IT infrastructure, delivering concrete defense strategies to help organizations detect and counter comparable threats.
69 Critical 1337 Important 0 Moderate 1 Low Microsoft addresses 1407 CVEs in the tenth Patch Tuesday of 2026, marking the second consecutive month to reset the bar as the largest Patch Tuesday release. This month’s…
69 Critical 1337 Important 0 Moderate 1 Low Microsoft addresses 1407 CVEs in the tenth Patch Tuesday of 2026, marking the second consecutive month to reset the bar as the largest Patch Tuesday release. This month’s updates include patches for two zero days, including one that was exploited in the wild. Microsoft patched 1,407 CVEs in its October 2026 Patch Tuesday release, with 69 rated critical, 1,337 rated as important, and one rated as low. This month’s update includes patches for 301 products and components. The following table lists the products with the most CVEs patched this month. A…
Federal authorities have charged 14 people and seized roughly 187 computers in their newest effort to disrupt North Korea’s remote IT worker scheme. The Justice Department announced the indictment Tuesday, highlighting…
Federal authorities have charged 14 people and seized roughly 187 computers in their newest effort to disrupt North Korea’s remote IT worker scheme. The Justice Department announced the indictment Tuesday, highlighting two arrests and searches of more than 40 residences in Texas known or suspected to operate as “laptop farms,” where facilitators maintain employer-issued laptops so North Korean engineers can use them while abroad. An indictment unsealed in the Northern District of Ohio charges two U.S. citizens, Michael James Bostelle of Pennsylvania and Juan Cecilio Pena Carrillo of Texas. It…
Microsoft is publishing 1,413 own-product vulnerabilities on October 2026 Patch Tuesday , including 1,102 vulnerabilities in Windows. Anyone who enjoyed last month’s record-setting Patch Tuesday will love the October…
Microsoft is publishing 1,413 own-product vulnerabilities on October 2026 Patch Tuesday , including 1,102 vulnerabilities in Windows. Anyone who enjoyed last month’s record-setting Patch Tuesday will love the October 2026 edition, because it’s much bigger still. As Rapid7 has noted over the course of 2026, there is every reason to suppose that vulnerability volumes will continue to rise. Microsoft is aware of exploitation in the wild for just one of the vulnerabilities published today, as well as public disclosure for two others. Windows Shell: zero-day security feature bypass The Windows…
A critical heap buffer overflow vulnerability (CVE-2026-39919) in the Ghostscript interpreter and rendering engine could allow remote code execution through specially crafted PDF files.
The Democratic People's Republic of Korea (DPRK) is trying to get insight into its own war effort in Ukraine, through simple reply-baiting phishing attacks.
Anthropic is warning that small AI models could soon be able to self-replicate across consumer IoT devices, from Android TV boxes to smart ovens, creating distributed botnets capable of running AI workloads without…
ATT&CK v20: Critical Infrastructure Campaigns, Adversary Use and Abuse of AI, & Iranian Cyber Espionage ATT&CK v20 brings more critical infrastructure and cross-domain activity into the framework, with Campaigns for…
ATT&CK v20: Critical Infrastructure Campaigns, Adversary Use and Abuse of AI, & Iranian Cyber Espionage ATT&CK v20 brings more critical infrastructure and cross-domain activity into the framework, with Campaigns for attacks on U.S. water utilities and an AI-assisted breach of Mexican government infrastructure that reached both IT and OT, along with new and updated Groups and Software tied to Iranian cyber espionage, Chinese and North Korean operations, and ransomware. Enterprise gains AI-focused and AI-enabled Techniques, ICS added Techniques for command and script execution and command and…
A vulnerability in the Unified Extensible Firmware Interface (UEFI) Shell implementation of Cisco UCS Servers and UCS-based appliances could allow an authenticated attacker with valid credentials for a user account with…
A vulnerability in the Unified Extensible Firmware Interface (UEFI) Shell implementation of Cisco UCS Servers and UCS-based appliances could allow an authenticated attacker with valid credentials for a user account with the role of user or admin or an unauthenticated attacker with physical access to an affected device to bypass UEFI Secure Boot validation checks and execute unauthorized software. This vulnerability is due to the availability of memory write commands in the UEFI Shell while UEFI Secure Boot is enabled on a device. An attacker could exploit this vulnerability by selecting the…
More than 40 residences in Texas were the target of a federal operation in September to clamp down on remote worker scams that feed money back to the North Korean regime.
Microsoft has released its monthly security update for October 2026, which includes 1415 vulnerabilities affecting a range of products, including 85 that Microsoft marked as "critical." Microsoft notes that 1 of the…
Microsoft has released its monthly security update for October 2026, which includes 1415 vulnerabilities affecting a range of products, including 85 that Microsoft marked as "critical." Microsoft notes that 1 of the vulnerabilities disclosed this month have been exploited in the wild CVE-2026-96951 is a security feature bypass vulnerability that affects Windows Shell. The shared weakness is Improper Neutralization of Special Elements used in a Command ('Command Injection'). The vulnerability has a CVSS base score of 8.8. Out of 85 "critical" vulnerabilities, 67 are remote code execution (RCE)…