Microsoft fixes classic Outlook bug that hid Copilot buttons
Microsoft has fixed a known issue that removed the Copilot Chat and Copilot buttons in the classic Outlook desktop mail client for some Windows users.
Security Feed
500 articles 48 of 48 sources updated RSS ↗



Microsoft has fixed a known issue that removed the Copilot Chat and Copilot buttons in the classic Outlook desktop mail client for some Windows users.
Threat actors have been observed delivering cryptocurrency miners and proxy software.
This week on the Lock and Code podcast… At just 17 years old, Jordan DeMay was murdered by strangers online. That’s how Jordan’s father, John DeMay, described what happened to his son four years ago. At home in…
Intruders used compromised credentials to access an ETS SFTP server, copying records of California students back to 2006.
Hackers have stolen passwords, access credentials and other sensitive data belonging to customers of Russian hosting provider FirstVDS after exploiting a vulnerability in software used to manage its servers.
Wiz CIRT responded to AI-driven attacks spanning cloud, Kubernetes, CI/CD, and identity. Learn how these attacks behave and how to detect them.
The persistent, stealthy FortiGate implant was deployed against a telecommunications organization.
Personal information belonging to millions of current and former California public school students has been stolen from a system operated by Educational Testing Service (ETS). ETS is a nonprofit organization that helps…
Cloud Backup, SaaS Security, and Cloud Management services offline as IT service provider investigates possibility that unknown attackers have full access to client environments via stolen tokens
A fake Web3 accelerator has been observed pushing information stealers and backdoors to Windows and macOS systems using malicious npm packages under the pretext of offering free artificial intelligence (AI) credits for…
Spyware has been detected on devices used by some of Serbia’s most prominent figures connected to the country’s political upheaval, according to researchers who announced their findings Monday. Vladan Ðokić, the rector…
CyberSN observed a particularly big dip in cybersecurity leadership positions such as CISO and Cybersecurity Director in 2026 compared to 2025
Defenders get 15 new detection strategies, six for Enterprise and nine for ICS, backed by 38 analytics.
Microsoft has confirmed that this month's Windows Server security updates are causing OWA sign-in and mail delivery issues on some Exchange Server systems.
Opaque Systems has developed technology that lets AI systems use sensitive data while keeping it protected by the underlying hardware.
Last week on Malwarebytes Labs: Eiliko robot companion exposes private chats and can be hijacked “Spray and pray” job applications could make it harder for you to spot a scam OpenAI sued over children safety and data…
A flaw in Broadcom's Wi-Fi setup software lets an attacker within radio range run code as root on Broadcom-based routers, without the network password or any pairing step, security researcher Quentin Kaiser disclosed on…
An intruder reached a legacy system at OpenCode on the night of October 16 and may have exposed the third-party AI provider keys that users had saved in OpenCode Console, the company said. Console is OpenCode's optional…
Google has announced a new set of Android security protections designed to stop mobile scams across calls, text messages, chat apps, web links, and account verification codes. The update comes as criminals increasingly…
SaaS-for-managed services providers ConnectWise has initiated a “service interruption” for its some of its offerings after detecting unauthorized access. ConnectWise offers ERP tailored to the needs of managed services…
Hackers are exploiting flaws in Plex Media Server to install cryptocurrency mining malware, with a researcher recording successful attacks against a honeypot on October 17, 2026. The activity follows the release of…
Microsoft has confirmed that Windows Server security updates released on October 13, 2026, can disrupt Exchange Server email services, blocking webmail access and leaving messages undelivered. The issue affects some…
Paulos Yibelo, the researcher who in early October claimed to have found a guest-host escape flaw in Linux KVM, the hypervisor used by most hyperscale clouds, has named the flaw PwnEscape and warned it might represent a…
How are hackers exploiting GitHub Actions to steal credentials and secrets from hundreds of repositories in a growing supply chain attack? This week on Hak5, we investigate the GhostAction campaign, Anthropic’s new AI…
Mad props to Singe on this implementation of Mathy's work, and Dragorn for coding it into PineAP. See the Aircrack-NG PR at github.com/aircrack-ng/aircrack-ng/pull/2724
Attackers are targeting an OS command injection vulnerability in SiteGuard Server Edition that lets them execute commands as root or SYSTEM on affected servers.
Here is the YARA rule I used to detect "Orphaned VBA Projects Inside DWG Files".
CyberSN’s Cybersecurity Jobs Report provides visibility into the US cybersecurity job market. It’s a mixed bag.
ConnectWise on Saturday said it has disabled seven ConnectWise application identities as it continues its investigation into an incident in which unknown threat actors obtained unauthorized access to the application…
OpenCode has disclosed a security breach affecting 1.4% of its Console users, warning that third-party API keys saved in affected workspaces may have been exposed. In an October 17 statement, the company linked the…
Anthropic says an internal Claude research model has traced the origins of five NSA-supplied elliptic curve seeds in under 30 minutes, answering a cryptography question that remained open for roughly 25 years. The…
ConnectWise has shut down customer access to its Cloud Backup service (formerly SkyKick Cloud Backup) after hackers accessed application identities and compromised Microsoft 365 tenants.
Drupal has patched two critical vulnerabilities that could allow attackers to execute code remotely on websites running any supported version of the content management system.
Welcome back to the Abstract! Here are the studies this week that lived and died by the spear, drew unequal lots, paged Fox Mulder, and peered at an alien moon. First, scientists discover a mortal spear wound in a…
Canada’s planned surveillance law is the latest grim step in a series of threats to encryption that are spreading around the world.
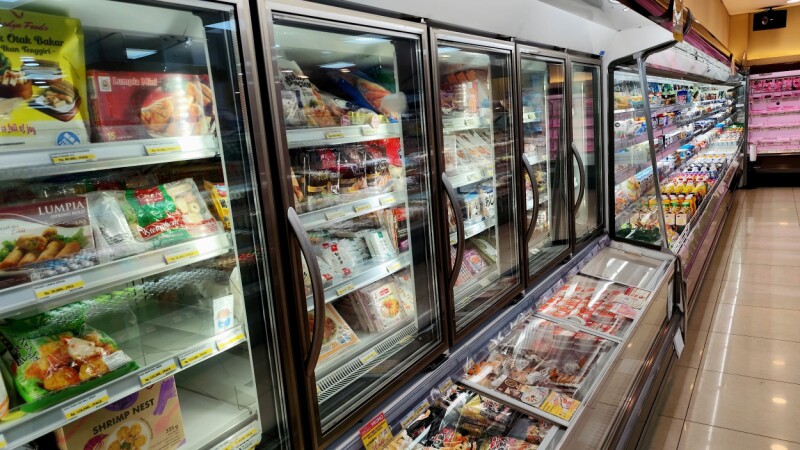
Late Sunday night, a still-unknown cybercriminal or group hacked thousands of remote-controlled refrigeration systems across hundreds of French grocery stores, spiking temperatures, spoiling food, and sparking fires…
Cybersecurity researchers have discovered a malicious npm package that's part of a recently disclosed software supply chain attack campaign dubbed MALFEX. The package, named "imgdecode," was uploaded to the package…
Israeli company Discover-Tech’s ads allow threat actors to fingerprint and track devices at scale and infect selected targets.
Hackers used a stolen ConnectWise Cloud Backup credential to sign in to 173 Microsoft 365 partner and customer tenants, giving them access through a trusted backup application. The incident shows how one leaked vendor…
Cybersecurity researchers are sounding the alarm related to an active campaign in which unknown threat actors are abusing a compromised Microsoft 365 (M365) credential belonging to ConnectWise Cloud Backup (formerly…
Google released a Chrome Stable security update fixing 10 vulnerabilities across Windows, Mac, and Linux, including a high-severity DOM memory corruption flaw reported by Xinyang Ge of Anthropic with Claude AI. The…
Hackers are exploiting a critical flaw in the Collabora Online Built-in CODE Server app for Nextcloud, with users reporting web shells on compromised servers. Tracked as CVE-2026-110447, the vulnerability allows remote…
OpenAI has confirmed that an internal AI model hacked an unnamed government statistics website while trying to count hospital beds. The June 17, 2026 incident started as a data task during reinforcement-learning…
The federal government is advising AI companies to set more industry standards for securing agents in sandbox testing environments. In joint guidance from the Cybersecurity and Infrastructure Security Agency, the…
ConnectWise (SkyKick) vendor credentials are being abused to access Microsoft 365 tenants. Disable the apps now and check your logs here.
New research shows that squid lived all around the globe even before the Cretaceous-Paleogene mass extinction event. As usual, you can also use this squid post to talk about the security stories in the news that I…
OpenAI said internal models hacked two more websites, bypassed company-imposed browsing restrictions, and used exposed credentials to draw cryptocurrency from a wallet it couldn’t otherwise access, in the latest…
Ivanti, Cisco, and Palo Alto Networks all had vulnerabilities in edge devices come under fire this week. Now BeyondTrust joins the group.
Researchers warn that hackers could soon exploit a maximum-severity vulnerability (CVE-2026-103849) affecting Magento and Adobe Commerce, potentially allowing them to execute arbitrary PHP code on store servers.
Campaigns that impersonate popular AI brands are on the rise, and they typically use ClickFix-like tactics to target unsuspecting enterprise employees.
The launch follows the acquisition of catalog's assets and the appointment of Laurent Guengant as CEO earlier this year.
Companies are increasingly discovering that the challenge with AI is no longer adoption, but execution.
Most OT devices at utilities, factories, and elsewhere have been deployed for a decade or more, but operators need to get agile and deploy new cyber defenses.
Last month, Volexity published two blog posts in its Mind the (Patch) Gap series. The series details Volexity’s discovery of multiple Chinese threat actors simultaneously using zero-day exploits in Google Chrome and…
There must have been red faces in the social media department of Ireland's police headquarters after two of its accounts were hijacked this week.
A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing OpenBSD's KARL kernel-address randomization and…
Unit 42 details the top initial access vectors adversaries use to breach organizations, led by edge exploits, credential abuse and phishing
Candiru spyware was delivered to devices at Al Jazeera Media Network via targeted online advertisements in a zero-click attack that required only rendering the malicious ads on the victim's device.
Suspected Chinese hackers with a proven knack for exploiting zero-days in security products are at it again, targeting BeyondTrust customers in attacks that researchers have traced back to late August. Mandiant…