1Apple Is Entering Its Slop Era404 MediaBleeping ComputerCCCS Alerts & AdvisoriesMalwarebytes LabsThe Hacker NewsZero Day Initiative+3CVE-2026-86950 ↗My ears perked up when I heard Apple’s new foldable phones were cracking . I licked my lips when the company announced it’s releasing a touch-screen laptop . This was a company that once charged $19 for a polishing cloth , asked $200 for a VESA mount , and sold $700 wheels for the Mac Pro. Now it’s borrowing tired ideas from its competitors and launching hardware its previous leaders rejected. The once dominant company is struggling to find its feet in an AI-driven post-Tim Cook world. John Ternus is the new CEO — a 25 year veteran of the company with a track record of pushing harebrained…
2Researcher Uses Claude AI to Extract Internal Anthropic Binary and Recover Google Cloud TokenCCCS Alerts & AdvisoriesCyber Security NewsSecurityWeekThe Hacker NewsZero Day Initiative+2A security researcher got Claude AI to hand over an internal Anthropic program and a memory dump that held pieces of a working Google Cloud token. The findings were published on October 29, 2026. They show how a helpful chatbot can expose the systems that run it. The work started with a plain question about the sandbox, the locked-down space where Claude runs code. Claude’s answers led the researcher to a downloaded binary, a memory file, and a rebuilt Google service account ID token that Google accepted as valid. Anthropic later said the sandbox findings did not break its threat model. Chris…
3Researchers Hacked Cursor, GitHub Copilot, Codex, VS Code, and Claude Desktop Embedded BrowsersCheck Point ResearchCyber Security NewsDark ReadingThe Hacker NewsThe Register Security+2Security flaws in the embedded browsers of Cursor, GitHub Copilot, Codex, VS Code, and Claude Desktop could enable code execution, file theft, and address-bar spoofing on developer machines . The findings published on October 29 show how browser features built into AI assistants can break security boundaries when given extra access to their host apps. The researchers named the attack class EMBRACE, short for an embedded browser trusted like a real one. These are separate flaws sharing one design problem. Features meant to help assistants preview projects, read pages, and track tabs gave…
7CISA Warns of GitLab Integer Overflow Vulnerability Exploited in AttacksCISA Alerts & AdvisoriesCyber Security NewsSecurityWeekThe Hacker News+1CVE-2026-97229 ↗The Cybersecurity and Infrastructure Security Agency has warned that attackers are exploiting CVE-2026-97229 . This GitLab vulnerability could allow code execution without logging in. CISA added the flaw to its Known Exploited Vulnerabilities catalog on October 29, 2026, confirming evidence of active exploitation and raising the urgency for organizations running affected GitLab servers. The vulnerability affects GitLab Community Edition and Enterprise Edition. It involves an integer overflow or wraparound caused by insufficient checks on regular expressions inside CI/CD configurations. A…
9In the year AI re-wrote the infosec rulebook, it’s comforting to know crypto exchanges still have bad securityBleeping ComputerThe Hacker NewsThe RecordThe Register Security+1Crypto exchange Binance has paused trading after discovering unknown parties cracked one of its workers’ laptops and used it to make massive trades. Late on Thursday, US time, the company used its social media feeds to report “Our teams are aware of reports of a potential security issue and are actively investigating.” The exchange insisted “User funds are completely safe” and warned its customers “should remain cautious of scams and should not trust unofficial links, messages, or requests for account information.” The company soon froze $2.5 billion worth of assets and warned that the figure…
14Inside KeyDrift: Analyzing historical UAT-11473 activity on Cisco SD-WANBleeping ComputerCisco TalosCVE-2026-20127 ↗Cisco Talos has identified UAT-11473, a highly sophisticated advanced persistent threat (APT) actor, who exploited CVE-2026-20127 , an authentication bypass vulnerability in Cisco SD-WAN Catalyst Controller instances to bypass authentication and gain unauthorized access to affected systems. UAT-11473 then installed a custom malware framework we track as “KeyDrift” consisting of multiple components geared towards collecting sensitive keying information, acting as backdoors and intermediate command-and-control (C2) hosts. Observed targeting spans across space and satellite services, defense and…
15Oracle celebrates end of Cybersecurity Awareness Month with quadruple troubleCCCS Alerts & AdvisoriesThe Hacker NewsThe Register SecurityCVE-2026-101767 ↗Attackers are probing a critical Oracle E-Business Suite vulnerability that can lead to remote code execution (RCE), despite Oracle issuing a patch earlier this month. Meanwhile, new analysis indicates that an Oracle PeopleSoft zero-day exploited by ShinyHunters as early as May involves three distinct vulnerabilities that can be combined to achieve RCE. Patching alone may not remove attackers from already compromised systems, particularly if they've installed web shells. First up: CVE-2026-101767, a critical, unauthenticated SQL injection bug in Oracle EBS that can lead to RCE. “Our Oracle…
16Manifestos, Fear, and ‘Loser Thinking’: Inside Proton’s AI Reckoning404 MediaDark ReadingAndy Yen, the CEO of Proton, had a message for an employee in the company’s security Slack channel who urged the company to at least take a few days to pentest newly written code before pushing it live. “That’s bullshit and loser thinking. Of course it’s possible to be fast and secure,” Yen wrote in the channel at the end of August. “Stop thinking always of how to be slower, and focus more on how to be faster.” In a follow-up message, Yen reiterated his point: “only losers think like that.” His ultimate message for the team was to “stop lovingly handcrafting all our code and use AI more.”…
17Cisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash FirewallsCisco Security AdvisoriesThe Hacker NewsCisco has released patches to address a high-severity security flaw in Secure Firewall Adaptive Security Appliance (ASA) Software and Secure Firewall Threat Defense (FTD) Software that it said has been exploited in the wild. The vulnerability, tracked as CVE-2026-76418, is rated 8.6 on the CVSS scoring system. Successful exploitation could allow an unauthenticated, remote attacker to cause the
18NIK C2: The new AI-enabled command-and-control frameworkCisco TalosMicrosoft SecurityCVE-2026-62740 ↗CVE-2026-62877 ↗Cisco Talos observed a new AI-integrated command-and-control (C2) framework in the wild called “NIK C2.” NIK C2 contains a Windows implant, using which, an actor can dump credentials, stream the victim's keystrokes to collect the targeted victim’s sensitive data, and instruct an integrated AI model to analyze the harvested data, all within the compromised session. In this framework, the actor has abused the OpenAI Chat Completions application programming interface (API), which is a HTTP endpoint that enables ChatGPT-style conversations programmatically. In addition to the features that enable…
20Massive leak exposes 41,000 DHS workers and undercover ICE agentsArs Technica SecurityWired SecurityAn unprecedented leak of Department of Homeland Security records has exposed details of more than 41,000 employees or contractors who work for the department and its constituent agencies. The records include email addresses, phone numbers, and office addresses, but also references to internal systems and sensitive information on undercover and surveillance programs. In all, the leak provides a map of how DHS is organized and how it operates. The records, which span DHS itself as well as seven component agencies, including Immigration and Customs Enforcement and US Customs and Border…
My ears perked up when I heard Apple’s new foldable phones were cracking . I licked my lips when the company announced it’s releasing a touch-screen laptop . This was a company that once charged $19 for a polishing…
My ears perked up when I heard Apple’s new foldable phones were cracking . I licked my lips when the company announced it’s releasing a touch-screen laptop . This was a company that once charged $19 for a polishing cloth , asked $200 for a VESA mount , and sold $700 wheels for the Mac Pro. Now it’s borrowing tired ideas from its competitors and launching hardware its previous leaders rejected. The once dominant company is struggling to find its feet in an AI-driven post-Tim Cook world. John Ternus is the new CEO — a 25 year veteran of the company with a track record of pushing harebrained…
A Trezor Safe 5 hardware wallet bought from the reseller CryptoBilis has an extra circuit board that sends out the recovery phrase over a mobile network, a customer has reported. Trezor has not yet examined the device…
A Trezor Safe 5 hardware wallet bought from the reseller CryptoBilis has an extra circuit board that sends out the recovery phrase over a mobile network, a customer has reported. Trezor has not yet examined the device. It is telling everyone who bought a Trezor from CryptoBilis since March 2026 to move their funds to a new wallet with a new recovery phrase. Trezor said in a blog post 
The alert is critical. The fix is known. And the ticket sits in a queue for days. Security teams understand the risk, but the people who keep applications available need proof that the change won’t break anything. Their…
The alert is critical. The fix is known. And the ticket sits in a queue for days. Security teams understand the risk, but the people who keep applications available need proof that the change won’t break anything. Their concerns are practical. An IPS protection could block legitimate traffic. A configuration change could interrupt a service. An endpoint policy could affect an application
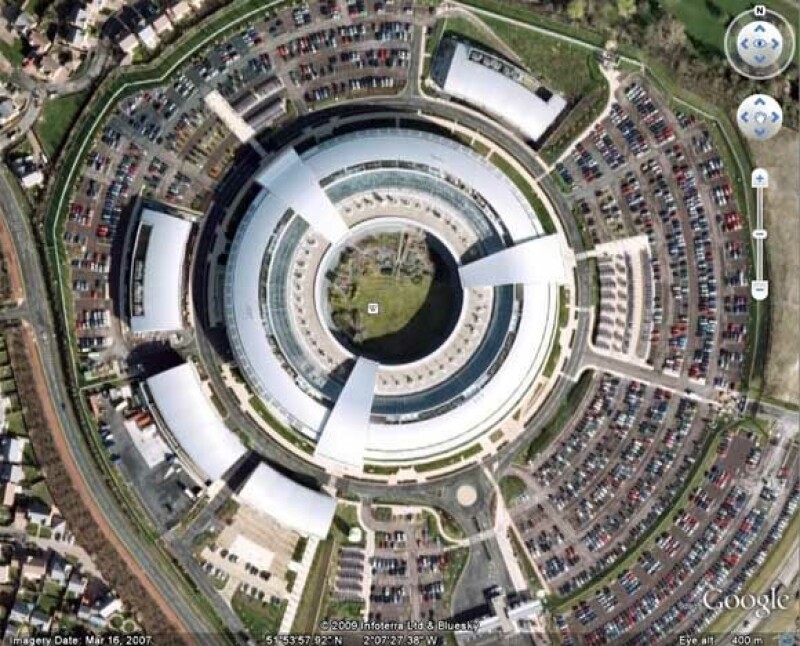
Thousands of GCHQ storage drives containing sensitive data have been lost for years, and the British signals intelligence agency still cannot explain where they are. According to the Investigatory Powers Commissioner’s…
Thousands of GCHQ storage drives containing sensitive data have been lost for years, and the British signals intelligence agency still cannot explain where they are. According to the Investigatory Powers Commissioner’s Office’s (IPCO) annual report, the missing storage drives have been known to officials for years, and may contain data related to the Investigatory Powers Act (IPA). "I remain concerned that GCHQ has not yet established a sufficiently clear understanding of the scale, location, and recoverability of lost removable media that may contain IPA-related data, notwithstanding that…
Multiple crypto-tracing firms say notorious North Korean hackers TraderTraitor may be behind the largest digital heist in history—with billions of crypto likely gone for good.
The company suffered outages starting at 2 p.m. Eastern U.S. time on Thursday and eventually attributed the downtime to a compromise involving an unnamed provider.
Poryadok, which operates 48 stores across 32 Russian cities, first reported technical problems on Sunday, saying its website, mobile app and physical stores were temporarily unavailable.
Security flaws in the embedded browsers of Cursor, GitHub Copilot, Codex, VS Code, and Claude Desktop could enable code execution, file theft, and address-bar spoofing on developer machines . The findings published on…
Security flaws in the embedded browsers of Cursor, GitHub Copilot, Codex, VS Code, and Claude Desktop could enable code execution, file theft, and address-bar spoofing on developer machines . The findings published on October 29 show how browser features built into AI assistants can break security boundaries when given extra access to their host apps. The researchers named the attack class EMBRACE, short for an embedded browser trusted like a real one. These are separate flaws sharing one design problem. Features meant to help assistants preview projects, read pages, and track tabs gave…
Palo Alto Networks has confirmed that attackers are actively exploiting PHP2Shell vulnerabilities against PAN-OS management interfaces exposed to the internet. In its October 29, 2026, update, Unit 42 said it…
Palo Alto Networks has confirmed that attackers are actively exploiting PHP2Shell vulnerabilities against PAN-OS management interfaces exposed to the internet. In its October 29, 2026, update, Unit 42 said it independently verified attacker tools used to combine the PHP flaws with a Linux kernel vulnerability and gain root access. The vulnerabilities, CVE-2026-109618 and CVE-2026-109619, each carry a critical CVSS 4.0 score of 9.2. They can allow remote code execution without a login. Palo Alto said roughly 0.02% of its global installed base had public management interfaces configured and was…
Ahmad Umar Agha, a Syrian Electronic Army hacker known online as "Th3Pr0," has been sentenced by a U.S. federal court to 42 months in prison for his role in a hacking conspiracy that targeted Western news outlets. The…
Ahmad Umar Agha, a Syrian Electronic Army hacker known online as "Th3Pr0," has been sentenced by a U.S. federal court to 42 months in prison for his role in a hacking conspiracy that targeted Western news outlets. The conspiracy was organized and led by members of former Syrian President Bashar al-Assad's inner circle, including the commander of Syria's General Intelligence
The US Department of Homeland Security has had the details of more than 41,000 staff, including ICE and CBP agents, published online. Not ideal for an organisation with "Security" in its name.
Trezor has warned that a suspected hardware implant inside a Trezor Safe 5 could steal recovery phrases and send them over a mobile network. The warning covers every Trezor model bought from CryptoBilis from March 2026…
Trezor has warned that a suspected hardware implant inside a Trezor Safe 5 could steal recovery phrases and send them over a mobile network. The warning covers every Trezor model bought from CryptoBilis from March 2026 onward, although only one suspected device has been reported. In its October 30 security notice , Trezor urged affected users to move funds to a newly created wallet with a new seed. The company has not examined the device and has received no reports of stolen funds from CryptoBilis buyers. The March cutoff is a precautionary scope for customer action, not proof that every…
A modern organization protects its information systems with a whole suite of technologies that generate thousands of security alerts every day. Looking at these alerts in bulk, you’ll see that a significant share are…
A modern organization protects its information systems with a whole suite of technologies that generate thousands of security alerts every day. Looking at these alerts in bulk, you’ll see that a significant share are false positives. Ideally, these alerts would be filtered out automatically so that analysts could focus on the ones that may point to a real incident. However, writing filters is a time-consuming task in itself. To create a correct filter, an analyst needs to: Review the logs Identify the source of the activity Define filtering boundaries Choose filtering criteria Write a rule…
Binance reportedly lost approximately $6.36 billion in cryptocurrency on October 29, 2026, after an attacker drained wallets across ten blockchains. TRM Labs describes the incident as the largest cryptocurrency theft…
Binance reportedly lost approximately $6.36 billion in cryptocurrency on October 29, 2026, after an attacker drained wallets across ten blockchains. TRM Labs describes the incident as the largest cryptocurrency theft ever recorded, with most of the stolen funds transferred out within about 20 minutes of the attack. Its investigation attributes the operation to TraderTraitor, a North Korean-linked hacking group known for targeting cryptocurrency platforms and financial organizations to steal digital assets. According to TRM, Binance acknowledged a security incident, suspended withdrawals on…
Cybersecurity researchers have disclosed that a trojanized version of Anthropic's official Claude Code extension was distributed through the Cursor Marketplace as a legitimate update, attempting to install a persistent…
Cybersecurity researchers have disclosed that a trojanized version of Anthropic's official Claude Code extension was distributed through the Cursor Marketplace as a legitimate update, attempting to install a persistent SSH backdoor on affected systems. The malicious update, version 2.1.313, was distributed under the extension's legitimate publisher identity, prompting Cursor to temporarily shut
An unauthorized AI relay service is installing genuine OpenAI Codex and Anthropic Claude Code tools on company computers, then changing their settings to send requests through third-party servers. The setup also removes…
An unauthorized AI relay service is installing genuine OpenAI Codex and Anthropic Claude Code tools on company computers, then changing their settings to send requests through third-party servers. The setup also removes sandbox controls, creating a path for sensitive business data to leave approved systems. Symantec’s Threat Hunter Team documented the activity in an October 29 report. Researchers observed the service across a dozen organizations since early 2026. Most were in mainland China, with other deployments involving multinational firms connected to South Korea, Taiwan, and Malaysia…
The Cybersecurity and Infrastructure Security Agency has warned that attackers are exploiting CVE-2026-97229 . This GitLab vulnerability could allow code execution without logging in. CISA added the flaw to its Known…
The Cybersecurity and Infrastructure Security Agency has warned that attackers are exploiting CVE-2026-97229 . This GitLab vulnerability could allow code execution without logging in. CISA added the flaw to its Known Exploited Vulnerabilities catalog on October 29, 2026, confirming evidence of active exploitation and raising the urgency for organizations running affected GitLab servers. The vulnerability affects GitLab Community Edition and Enterprise Edition. It involves an integer overflow or wraparound caused by insufficient checks on regular expressions inside CI/CD configurations. A…
Attackers are chaining zero-day flaws in Ivanti Connect Secure VPN appliances to gain unauthenticated root access, exposing stored credentials and sensitive Active Directory data. Ivanti confirmed attacks against a…
Attackers are chaining zero-day flaws in Ivanti Connect Secure VPN appliances to gain unauthenticated root access, exposing stored credentials and sensitive Active Directory data. Ivanti confirmed attacks against a limited number of customers and released additional fixes on October 29, 2026, following its initial October patches. Volexity tracked UTA0576 activity to October 3 and, during an October 5 investigation, identified a compromised, fully patched Ivanti appliance running version 22.8R2.4 (Build 19097) during an investigation on October 5, highlighting the flaws’ ability to bypass…
Microsoft resolved a Windows 11 issue that blocked non-admin users from connecting via Remote Desktop when Administrator protection was enabled, releasing fixes on October 28, 2026, for connection failures with error…
Microsoft resolved a Windows 11 issue that blocked non-admin users from connecting via Remote Desktop when Administrator protection was enabled, releasing fixes on October 28, 2026, for connection failures with error 0xC000000D. The bug appeared after the September 22 non-security preview update, KB5124010 , or later updates. Affected users could see the message, “The token that was passed to the function is invalid.” Microsoft’s release health notice identifies enterprise-managed computers acting as Remote Desktop hosts as the main systems affected. Microsoft opened its investigation on…
A security researcher got Claude AI to hand over an internal Anthropic program and a memory dump that held pieces of a working Google Cloud token. The findings were published on October 29, 2026. They show how a helpful…
A security researcher got Claude AI to hand over an internal Anthropic program and a memory dump that held pieces of a working Google Cloud token. The findings were published on October 29, 2026. They show how a helpful chatbot can expose the systems that run it. The work started with a plain question about the sandbox, the locked-down space where Claude runs code. Claude’s answers led the researcher to a downloaded binary, a memory file, and a rebuilt Google service account ID token that Google accepted as valid. Anthropic later said the sandbox findings did not break its threat model. Chris…
The "FrostyNeighbor" advanced persistent threat (APT) launched a destructive attack in Ukraine and is raising concerns about deeper alignment with Russian cyber objectives.
Drupal has warned that threat actors are exploiting a "highly critical" security flaw in its Commerce Core component. The vulnerability, tracked as CVE-2026-118539 (CVSS score: N/A), is a case of missing authorization…
Drupal has warned that threat actors are exploiting a "highly critical" security flaw in its Commerce Core component. The vulnerability, tracked as CVE-2026-118539 (CVSS score: N/A), is a case of missing authorization affecting Commerce Core versions from 0.0.0 to 2.41 and from 3.0.0 to 3.3.13. "This module enables you to sell goods and services to customers through an included shopping cart
Stolen credentials beat most controls because they are the control which is why behavior became the detection substrate. UEBA baselines how every user and entity normally acts, then surfaces the deviation: the service…
Stolen credentials beat most controls because they are the control which is why behavior became the detection substrate. UEBA baselines how every user and entity normally acts, then surfaces the deviation: the service account suddenly browsing HR files, the engineer’s badge in one country and login in another. One honest note up front: our source list named ten brands, but Exabeam and LogRhythm merged into a single vendor, so we rank nine platforms honestly rather than pad. Exabeam takes 1 on the lineage that defined the category. Key Takeaways • 1 overall: Exabeam (including LogRhythm)…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added two security flaws impacting Cisco and GitLab software to its Known Exploited Vulnerabilities (KEV), citing evidence of active…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Thursday added two security flaws impacting Cisco and GitLab software to its Known Exploited Vulnerabilities (KEV), citing evidence of active exploitation. The vulnerabilities are listed below - CVE-2026-97229 (CVSS score: 10.0) - An integer overflow or wraparound vulnerability in GitLab Community Edition and Enterprise
Crypto exchange Binance has paused trading after discovering unknown parties cracked one of its workers’ laptops and used it to make massive trades. Late on Thursday, US time, the company used its social media feeds to…
Crypto exchange Binance has paused trading after discovering unknown parties cracked one of its workers’ laptops and used it to make massive trades. Late on Thursday, US time, the company used its social media feeds to report “Our teams are aware of reports of a potential security issue and are actively investigating.” The exchange insisted “User funds are completely safe” and warned its customers “should remain cautious of scams and should not trust unofficial links, messages, or requests for account information.” The company soon froze $2.5 billion worth of assets and warned that the figure…
Cryptocurrency giant Binance said on Thursday that a "security incident" on its platform has impacted about $6.3 billion worth of assets. The world's biggest cryptocurrency exchange said nearly $3 billion of those…
Cryptocurrency giant Binance said on Thursday that a "security incident" on its platform has impacted about $6.3 billion worth of assets. The world's biggest cryptocurrency exchange said nearly $3 billion of those assets have been frozen on-chain so far. Tether and Circle said they have frozen more than 1.567 billion USDT and 800 million USDC related to the incident, respectively. The
php2shell raised fears of mass exploitation. A week of testing by our research team found that working exploits had to be fitted to each target’s exact PHP setup. Systems that share one build, such as network…
php2shell raised fears of mass exploitation. A week of testing by our research team found that working exploits had to be fitted to each target’s exact PHP setup. Systems that share one build, such as network appliances, are the exception: one tuned exploit can reach every device that runs it. Key takeaways The five vulnerable PHP sites we exposed to the internet were not compromised, and public proofs-of-concept (PoCs) that go beyond version checks do not reliably confirm whether a host is vulnerable. Exploitation has been confirmed elsewhere, on researcher honeypots and on some network…
In this edition of the Snake Oilers podcast, three vendors drop by to pitch their products. Minimal.dev : A sandbox for AI agents! Co-Founder and CEO Jake King explains what the company is and how it works. Request…
In this edition of the Snake Oilers podcast, three vendors drop by to pitch their products. Minimal.dev : A sandbox for AI agents! Co-Founder and CEO Jake King explains what the company is and how it works. Request Rocket : Runtime access control for AI agents and APIs. Founder and CTO Alex Ferguson drops by to talk about the problem the company is trying to solve. TRM Labs : All-source threat intelligence. Global Strategic Accounts Director Simon Warren talks about the company’s platform Ardence. This episode is also available on YouTube . Show notes
Binance, the world's largest cryptocurrency exchange, confirmed that it had been hacked in a $6.3 billion heist that blockchain investigators are blaming on North Korea.
OpenAI says it won't reduce usage limits for the $100, $200, and $500 ChatGPT Pro plans, as well as Business Premium, and it also promised to keep Dots usage independent.
Multiple vulnerabilities in five popular AI developer tools could allow attackers to execute code on a host machine, read and steal files, or spoof browser address bars. Researchers say flaws in OpenAI's Codex and…
Multiple vulnerabilities in five popular AI developer tools could allow attackers to execute code on a host machine, read and steal files, or spoof browser address bars. Researchers say flaws in OpenAI's Codex and Microsoft's VS Code remain unpatched, potentially putting developers who use affected configurations at risk. AI security startup Forever Security discovered vulnerabilities in Cursor, GitHub Copilot, Anthropic's Claude Desktop, VS Code, and Codex, and disclosed four of the flaws to the affected vendors. GitHub independently fixed the Copilot vulnerability without receiving a report…
Cryptocurrency exchange Binance is investigating a potential security breach involving up to $5.8 billion in digital assets, in what could become the largest cryptocurrency hack in history.
A crypto-mining campaign abusing Hugging Face models returned days after takedown, hijacking GPU servers and planting backdoors, with one model downloaded over 28,000 times. Separately, a fake Solana starter kit on…
A crypto-mining campaign abusing Hugging Face models returned days after takedown, hijacking GPU servers and planting backdoors, with one model downloaded over 28,000 times. Separately, a fake Solana starter kit on GitHub is positioned to trick AI coding agents into installing a NetSupport RAT.
Prediction market platform Polymarket temporarily suspended trading on Thursday after hackers compromised a third-party service to distribute cryptocurrency-draining JavaScript, with approximately $2.5 million in assets…
Prediction market platform Polymarket temporarily suspended trading on Thursday after hackers compromised a third-party service to distribute cryptocurrency-draining JavaScript, with approximately $2.5 million in assets traced to a suspected attacker wallet.
A vulnerability in the web-based management interface of Cisco Finesse could allow an unauthenticated, remote attacker to conduct server-side request forgery (SSRF) attacks through an affected device. This vulnerability…
A vulnerability in the web-based management interface of Cisco Finesse could allow an unauthenticated, remote attacker to conduct server-side request forgery (SSRF) attacks through an affected device. This vulnerability is due to improper input validation for specific HTTP requests. An attacker could exploit this vulnerability by sending a crafted HTTP request to an affected device. A successful exploit could allow the attacker to obtain limited sensitive information for services that are associated with the affected device. Cisco plans to release software updates that address this…
A company working on behalf of the Department of Homeland Security sought to cut off online access to information on more than 41,000 employees that hacktivists said they obtained from a database breached at DHS. A…
A company working on behalf of the Department of Homeland Security sought to cut off online access to information on more than 41,000 employees that hacktivists said they obtained from a database breached at DHS. A search tool for the database, named Icepick, went offline for a spell before coming online again Thursday under a different registrar. Icelandic hosting company FlokiNET said Thursday that it received a request from DHS contractor ZeroFox to remove the data, which it refused. “By mid-morning, icepi.cx no longer resolved. Its registrar, CentralNic, had placed the domain on…
On October 21, 2026, Node.js announced the availability of fixes for multiple vulnerabilities across the following supported release lines: 22.x, 24.x, and 26.x. These vulnerabilities impact critical operations such as…
On October 21, 2026, Node.js announced the availability of fixes for multiple vulnerabilities across the following supported release lines: 22.x, 24.x, and 26.x. These vulnerabilities impact critical operations such as the Brotli decoder, DNS resolution, and TLS certificate validation. The vulnerabilities pose risks for remote code execution and traffic interception. For more information, see Node.js Security Release . The following vulnerabilities have a Security Impact Rating (SIR) of High and are addressed in this advisory: CVE-2026-111497 - Brotli decoder out-of-bounds write; potential…
This installment of the Reporters' Notebook video series discusses some of the trends and topics from Cybersecurity Awareness Month, from using AI for better training to educating next-generation workforces on modern…
This installment of the Reporters' Notebook video series discusses some of the trends and topics from Cybersecurity Awareness Month, from using AI for better training to educating next-generation workforces on modern risks and emerging threats.
One cyber firm listed a half-dozen exploitations of the PHP2Shell bugs, and another identified a well targeted, suspected Chinese campaign that breached U.S. "government affiliated" servers.
A fake cryptocurrency trading app called Padre Terminal, previously available on the Apple App Store for iOS devices, has been linked to the theft of approximately $23,000 from 27 Solana wallets.
Some attacks take real skill. Others just need someone to leave a door open. This week has both. Exposed passwords, old bugs still getting exploited, and trusted software doing things it shouldn't. There's a strange mix…
Some attacks take real skill. Others just need someone to leave a door open. This week has both. Exposed passwords, old bugs still getting exploited, and trusted software doing things it shouldn't. There's a strange mix of clever tricks and careless mistakes. Hackers are borrowing trust from familiar apps, websites, and AI tools. Some are using AI to speed things up. Others are leaving their
Suspected Chinese attackers chained PHP2Shell with a Linux kernel privilege-escalation exploit to root 25 servers, including Palo Alto Networks firewalls linked to US government-affiliated organizations, according to…
Suspected Chinese attackers chained PHP2Shell with a Linux kernel privilege-escalation exploit to root 25 servers, including Palo Alto Networks firewalls linked to US government-affiliated organizations, according to Dream researchers. The snoops began exploiting these servers on October 23, targeting organizations across the US, Japan, Taiwan, and South Korea. The attackers also honed in on US government-affiliated firewalls. “Within hours of compromising a US government-affiliated firewall, they had tunneled into the internal network, compromised a third server using the same PHP2Shell…
Archive of Our Own (AO3), a massive repository for fanfiction and creative writing, might be down for as long as a month after going down for "maintenance" on Thursday. The Organization for Transformative Works (OTW)…
Archive of Our Own (AO3), a massive repository for fanfiction and creative writing, might be down for as long as a month after going down for "maintenance" on Thursday. The Organization for Transformative Works (OTW), the non-profit organization that runs AO3, posted on its status page early Thursday morning that the site was down for maintenance. A few hours later, it updated the status to say that it was expected to take at least 12 hours. By Thursday afternoon, it said the site restoration will take around two weeks, but could take up to a month. “We are hopeful that we will be able to…
A newly identified advanced persistent threat (APT) group tracked as UAT-11473 was observed exploiting CVE-2026-20127, an authentication-bypass flaw in Cisco Catalyst SD-WAN Controllers, to deploy a custom malware…