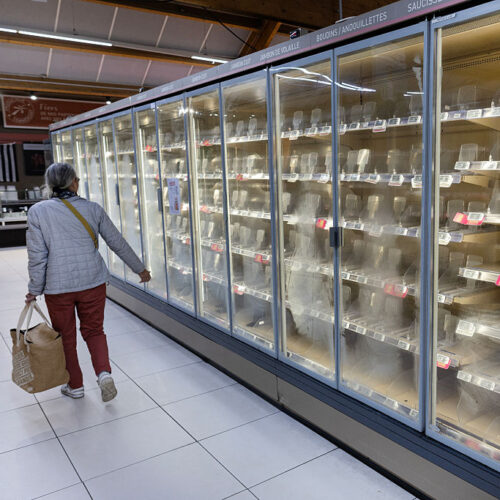
Supermarket Refrigeration Attack Widens to Copeland, Dixell Controllers
Roughly 700 French supermarkets were hit by the cyberattacks, for which no group has claimed responsibility.
Security Feed
500 articles 48 of 48 sources updated RSS ↗









Roughly 700 French supermarkets were hit by the cyberattacks, for which no group has claimed responsibility.
X says it has nuked more than 13,000 accounts involved in three suspected foreign influence operations targeting US political debate. In a post on Wednesday evening, the platform linked the operations to Iran, Russia…
Drupal core has a critical flaw in its Field UI module that could let an attacker run code on the site's server, and fixes were shipped on October 14 in Drupal 11.4.10, 11.3.19, and 10.6.19. An attacker cannot reach the…
The NCSC publishes its recommendations for configuring post-quantum cryptography in TLS. Now is time to migrate.
Recommended profiles to securely configure TLS for the most common versions and scenarios, with additional guidance for managing older versions.
Law enforcement authorities from 17 countries in Latin America and Europe have arrested 95 suspects in an INTERPOL-coordinated operation targeting the distribution of child sexual abuse material (CSAM) through online…
The Federal Trade Commission (FTC) has filed a complaint accusing Digital Forensics Corporation of exploiting people already targeted by sextortionists . We have talked about sextortion and recovery scams in the past…
Attackers are impersonating popular AI products to distribute malware, steal browser sessions, and compromise business accounts. ANY.RUN linked 1,258 public sandbox analyses to fake AI campaigns between April and…
Palo Alto Networks on Wednesday issued security updates for a high-severity flaw in PAN-OS software that has come under active exploitation. The vulnerability, tracked as CVE-2026-0322 (CVSS score: 8.6), is a case of…
CVE-2026-35029 and CVE-2026-59823 affect LiteLLM, which is commonly used by enterprises to connect their AI applications to providers like OpenAI and Anthropic
Delivered via phishing, the malware provides reconnaissance, remote execution, and data exfiltration capabilities.
Hackers who broke into the UK's Legal Aid Agency last year stole records dating back nearly five decades, the government has admitted, revealing the breach was far more extensive than previously thought. The Legal Aid…
Photos you take with your phone and some digital cameras can contain hidden information, including where they were taken. You can strip that data out before sharing a photo with someone, which would help to protect your…
AI is already part of digital forensics and incident response work, with or without a policy in place to govern it. The issue is that these tools are growing more confident in their own output faster than practitioners…
The Indian government has directed telecom service providers (TSPs) in the country to mandatorily display callers' registered names along with their numbers for incoming calls starting November 1, 2026, in an effort to…
Welcome, once again, to PWNED, the weekly column where we gawk at organizations that have made serious security mistakes. Normally, we’re talking about businesses or maybe the odd school that messes up, but today we’re…
The Hirudo malware combines elements of a traditional banking trojan and a full-featured RAT.
That online ad you saw for earbuds, a drone or bubble gum-scented car air freshener may have been a gateway for mercenary spyware that can infect your device without you ever having to click on it. The Citizen Lab at…
Microsoft and partners reveal a major Chinese-language phishing network centered around the Yam Store marketplace
Researchers at The Citizen Lab have for the first time released technical evidence of sophisticated mercenary spyware being distributed via online advertising.
Personal information such as names, addresses, Social Security numbers, and driver’s license numbers was compromised.
UK officials have stopped short of committing to AI-specific measures in the Cyber Security and Resilience Bill despite ministers promising to legislate wherever necessary. The uncertainty comes amid warnings about…
Microsoft has resolved a known issue that was causing black screens, desktop loading issues, and Explorer crashes after installing Windows 11 updates released since August.
UAT-6275 hackers have used a known WinRAR flaw to plant malware on Windows systems while targeting government organizations across the Commonwealth of Independent States (CIS). The activity shows how an unpatched…
The credential-theft campaign known as GhostAction has ramped up, targeting more than 30,000 repositories across 3,000 users and organizations. The spike, according to GitGuardian, was observed on October 8 and 9, 2026…
The ICO has handed the Metropolitan Police a reprimand and enforcement notice after privacy failings linked to the Auror platform
James Robinson never planned a cybersecurity career — seven companies and one deputy CISO role later, he leads security at Netskope.
The Legal Aid Agency (LAA), an executive agency of the UK's Ministry of Justice that manages the country's Public Defender Service, says attackers who breached its IT systems in April 2025 stole records dating back to…
DLP’s old reputation blocking legitimate work while real exfiltration walked out died with the pattern-only era. The 2026 winners judge context, ride enforcement points you already run, and explain every block…
The Information Commissioner's Office (ICO) has reprimanded London's Metropolitan Police Service (MPS) and issued an enforcement notice after officers used a retail crime platform without the force's approval or…
Every SOC question eventually becomes “what does this file actually do?” and the answer’s cost ranges from a free hash lookup to hypervisor-grade detonation. Evaluating detonation environments alongside the best malware…
Threat actors are exploiting a critical security flaw in Langflow, according to an alert from Previdian. Langflow is an open-source platform that allows developers to build artificial intelligence (AI) applications and…
DevSecOps succeeds when security rides the pipeline instead of blocking it and fails when ten scanners produce ten backlogs nobody owns. Modern engineering teams aligning with enterprise DevSecOps playbooks recognize…
Hundreds of stores lost millions of dollars because they hired third parties to manage the outdated OT firmware running their cooling systems.
The company says it’s aware of limited exploitation against customers’ firewalls, and it has made IoCs available.
Singapore-based Ahsay Backup has released security updates to address two security flaws in AhsayCBS that have been exploited by bad actors to drop web shells and XMRig cryptocurrency miners. The vulnerabilities in…
Unauthenticated, remote attackers could write arbitrary files to the operating system and execute commands with root privileges.
Some of the excitement about decision models follows from TypeSafe AI's claim that its Jev decision model cannot hallucinate and that "the model never makes type errors." Yet decision models, which answer questions with…
A fake Google Chrome app appeared on Google Play with a screenshot showing more than 100,000 downloads, raising fresh concerns about app checks and paid search results. The listing copied Chrome’s name, icon, and…
Microsoft has disclosed three Active Directory vulnerabilities that could let a remote attacker bypass a key security feature in Windows domain environments. The issues are tracked as CVE-2026-69982, CVE-2026-96252, and…
Hackers are exploiting a high-severity flaw in Palo Alto Networks PAN-OS that allows authenticated attackers to run code with root privileges on affected firewalls. Tracked as CVE-2026-0322, the vulnerability affects…
Cisco has warned that attackers are actively exploiting a critical zero-day vulnerability in Cisco Secure Email Gateway that can give them root access to affected appliances. Tracked as CVE-2026-76519, the flaw carries…
[This is a Guest Diary by Zachary Norwood, an ISC intern as part of the SANS.edu BACS program]
A ransomware negotiator attended a cybersecurity conference, only to be arrested by the FBI in connection with its investigation into the ShinyHunters gang. Meanwhile, hackers get the keys to ASOS's app and the chance…
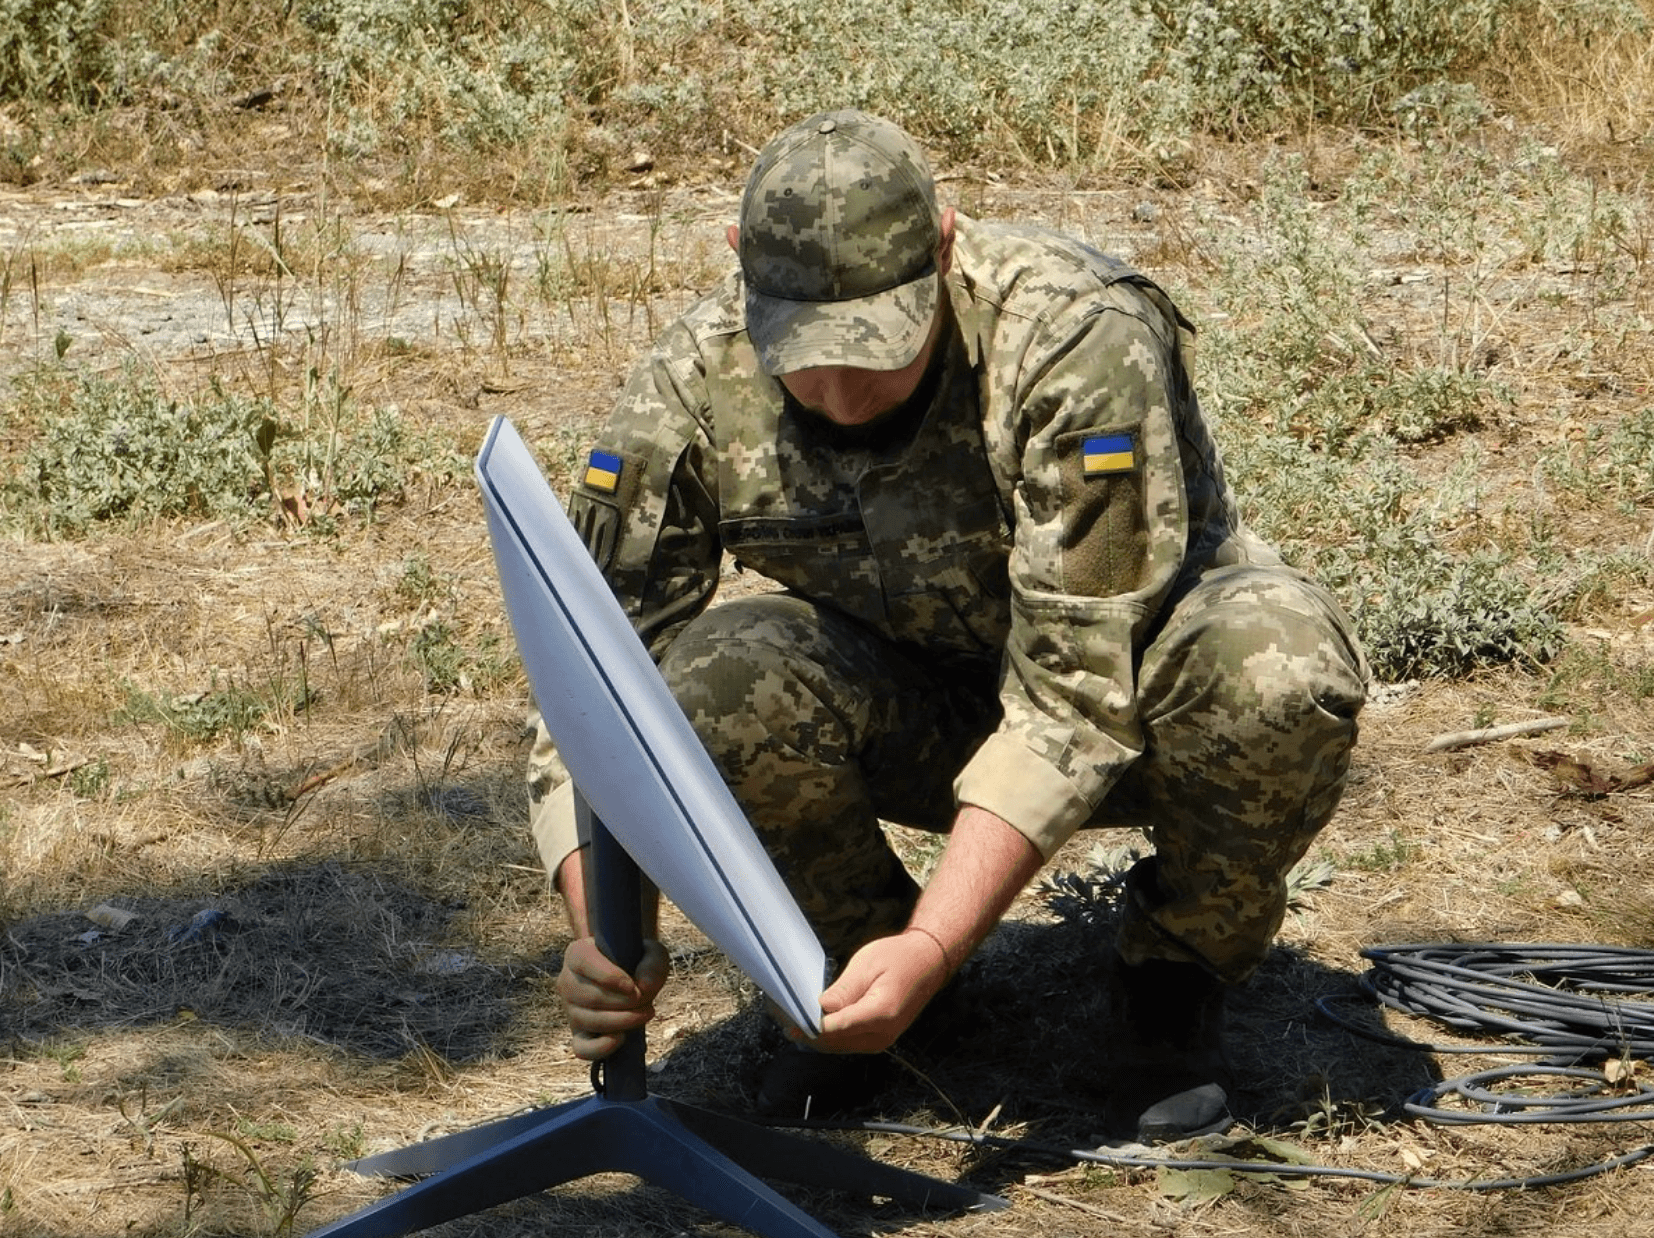
The Ukrainian military can again use SpaceX’s Starshield satellite service on the move, a Defense Ministry source told Recorded Future News on Thursday, days after sudden restrictions disrupted drone missions along the…
Palo Alto Networks has released security updates for a high-severity PAN-OS RCE zero-day, tracked as CVE-2026-0322, that has been exploited in attacks targeting firewalls.
We investigated an intrusion where attackers exploited CVE-2024-47575 to target 500+ firewalls and deploy PEERSTITCH, a memory-resident ARM64 malware.
Authorities in the Republic of North Macedonia filed charges against the alleged administrator of OLVX, a cybercrime marketplace that sold stolen personal data, credentials and malicious tools for attacks since 2023…
Cisco “strongly” implored customers to patch yet another critical, make-me-root vulnerability in its Secure Email Gateway (SEG), one that has already been exploited in zero-day attacks. A Cisco spokesperson told The…
Earlier this week, a mass hack of refrigeration systems at an estimated 700 supermarkets throughout France caused them to suddenly malfunction, causing spoilage of untold tons of perishables and, in some cases, fires…
CVE-2026-104935, a high-severity authentication bypass + RCE vulnerability, was only partially discovered and patched in July, leaving an opening for threat actors to capitalize on.
A raid on a home in a North Macedonian village led to the arrest of the suspected administrator of the OLVX market, according to the Balkan country's Interior Ministry along with the FBI.
A sprawling cybercrime marketplace supplied cloud infrastructure and phishing kits that helped fuel more than 1 billion phishing messages worldwide.
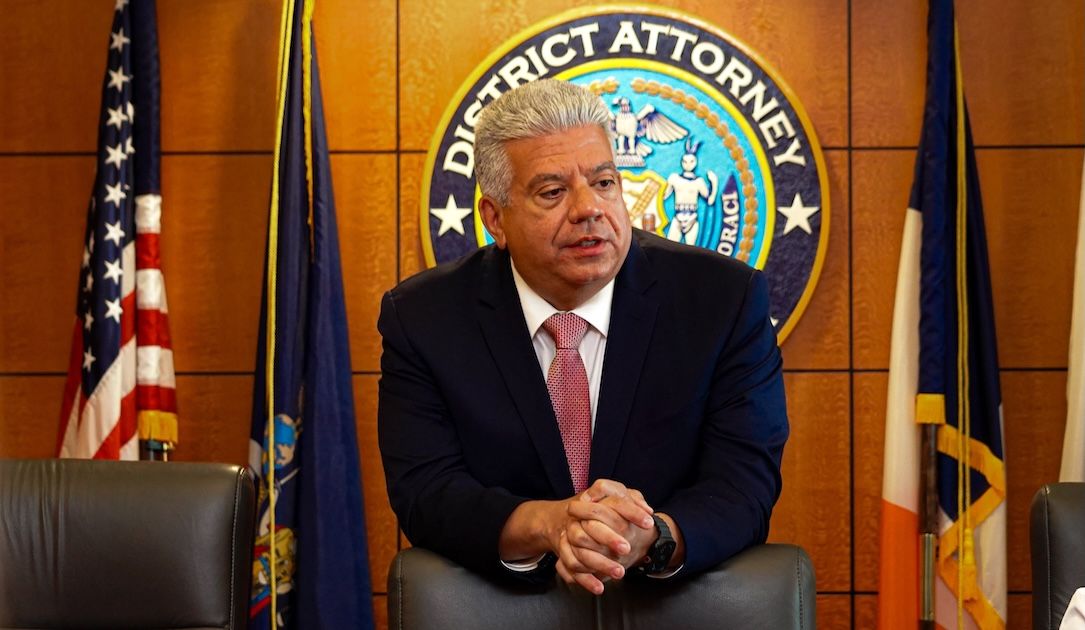
Russian-speaking Brooklyn residents began tipping off local authorities to a cryptocurrency fraud scheme three years ago, leading to an operation to take down the associated servers and domains.
Integrate your existing code scanners into Wiz for a unified view of application risk across your environment.
A bug in Claude Code Desktop's preview pane can allow adversaries to quietly steal credentials from developers, including SSH private keys, AWS credentials, and Claude 0Auth tokens.
The U.S. Department of Justice (DoJ) has disrupted the Famous Chollima threat group's operations by arresting two suspects, charging 14 individuals, and seizing nearly 187 laptops used in North Korean remote IT worker…
Researchers at security startup Xbow used OpenAI's GPT-5.6 Sol model to help chain three zero-day vulnerabilities in Chrome into an exploit capable of executing code outside the browser's sandbox on Windows machines…
Learn what the dark web looks like with an exploration of the far reaches of the internet, how you can get there, and what you might find… from a safe distance.
Attackers are exploiting a critical flaw in Cisco Secure Email Gateway that lets a sender with no login write files to the appliance's operating system, Cisco said in an advisory on Wednesday. The attacker sends an…
F5 has disclosed three serious security flaws in NGINX Plus and NGINX Open Source that can let remote, unauthenticated attackers crash worker processes by sending crafted HTTP requests. In certain setups, the memory…