2Citrix NetScaler Keeps Rebooting Following the 0-Day PatchCCCS Alerts & AdvisoriesCyber Security NewsDark ReadingCVE-2026-88771 ↗CVE-2026-88772 ↗Citrix NetScaler customers are reporting repeated appliance reboots after installing build 14.1-73.37, the emergency update released for two zero-day flaws under active attack. The failures appear linked to crafted SAML authentication traffic that crashes the nsaaad service. Citrix says its engineering and support teams are tracking a newly seen SAML issue and plan to release a fresh security bulletin and fixed build. The key point is that the reboot reports do not yet prove attackers have bypassed the September patch. Build 14.1-73.37 remains Citrix’s fixed 14.1 release for CVE-2026-88771…
3Critical GitLab AI Gateway Vulnerability Enables Remote Code Execution AttacksBleeping ComputerCCCS Alerts & AdvisoriesCyber Security NewsThe Hacker News+1CVE-2026-90970 ↗GitLab has released urgent security updates for a critical AI Gateway vulnerability that could allow authenticated attackers to execute commands remotely. Tracked as CVE-2026-90970, the flaw carries a CVSS score of 9.9 and affects self-hosted deployments used to support GitLab Duo AI features. The company released AI Gateway versions 19.2.4, 19.3.2, and 19.4.1 to address the issue. GitLab strongly recommends that customers running affected self-hosted gateways upgrade immediately. It also contacted self-hosted AI Gateway customers before publishing its security advisory to provide early…
4ShinyHunters Suspect Rey Reportedly Detained in Jordan, Helping FBI Identify Group MembersCyber Security NewsThe Hacker NewsA suspected member of the ShinyHunters digital extortion group, who goes by the online alias "Rey," has been allegedly detained by authorities in Jordan, Reuters reported, citing three people familiar with the matter. Rey, whose real name is Saif al-Din Khader, is said to have been brought into custody on September 29, 2026, cooperating with the U.S. Federal Bureau of Investigation (FBI) and
6Debian has Patched 1,313 Flaws in Massive Update Leading to DoS and Privilege Escalation AttacksCyber Security NewsDark ReadingRapid7 BlogDebian has released a major Linux kernel security update covering 1,313 CVE entries, addressing flaws that could allow privilege escalation, denial of service, and information leaks. The fixes are available for Debian’s stable release, Trixie, in Linux source package version 6.12.111-1. Security team member Salvatore Bonaccorso published advisory DSA-6528-1 on September 29, 2026. Debian recommends upgrading the affected linux packages. Importantly, the update prevents potential attacks; the advisory does not say that installing it causes security problems or that attackers have exploited…
7Critical Dell Container Storage Flaws Let Unauthenticated Attackers Gain Full Administrative ControlBleeping ComputerCyber Security NewsThe Hacker NewsDell has released security update DSA-2026-448 to address multiple critical vulnerabilities in its Container Storage Modules, including flaws that could allow unauthenticated remote attackers to take full administrative control of affected storage environments. Organizations using vulnerable Dell CSM deployments should upgrade immediately, as Dell stated that no workarounds or mitigations are available. The advisory affects Dell Container Storage Modules versions before 1.17.0, with fixes available in 1.18.0 and later, covering CSM Authorization, CSM Operator, CSI components, and third-party…
8Microsoft Pushes New Exchange V2 Update After Discovering New Security FlawCyber Security NewsMicrosoft SecurityCVE-2026-96940 ↗Microsoft has released September 2026 V2 security updates to fix an Exchange Server flaw that lets authenticated attackers access other users’ mailboxes within the same organization. Tracked as CVE-2026 – 96940 , the vulnerability could expose email messages and attachments, making it a serious concern for businesses running Exchange on-premises. The flaw involves weak authorization, allowing an attacker with authenticated access to gain privileges over a network. Public vulnerability records list a CVSS score of 8.8. Unlike attacks that require someone to open a malicious file, exploitation…
9Fortinet sounds the alarm over actively exploited FortiMail zero-dayBleeping ComputerSecurityWeekThe Register SecurityCVE-2026-104286 ↗Fortinet is warning customers to lock down FortiMail after attackers started exploiting a critical bug that lets them write files to vulnerable systems without logging in. The flaw, tracked as CVE-2026-104286, carries a CVSS score of 9.8 and affects multiple versions of Fortinet's email security platform. Fortinet describes the vulnerability as a combination of path traversal and improper handling of null characters in FortiMail's web interface. An unauthenticated attacker can exploit it using specially crafted HTTP or HTTPS requests to write arbitrary files to the underlying system. Writing…
10Apple changes full-disk access permissions to curb abuse from AI agentsArs Technica SecuritySecurityWeekApple says it is changing its macOS privacy settings to stop third-party app developers from misusing them to access message histories. Friday's announcement comes two weeks after tech columnist Jason Aten said that Meta’s new general-purpose AI agent Muse sent him an unsolicited notification referencing a thread between him and a co-worker over Apple Messages. Aten said he never granted Muse permissions to read his messages and had assumed they were off-limits. Social media last week blew up with masses of people who agreed and said the incident showed that AI assistants given access to…
13Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility ToolsSecurityWeekThe Hacker NewsGoogle has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and financial fraud, the tech giant said the move would block a major attack pathway. Advanced Protection is a
South Korean President Lee Jae Myung ordered a thorough investigation on October 4, 2026, after a series of financial sector data breaches exposed customer and worker information. The order comes as investigators…
South Korean President Lee Jae Myung ordered a thorough investigation on October 4, 2026, after a series of financial sector data breaches exposed customer and worker information. The order comes as investigators examine whether AI tools helped attackers break into systems used by banks and other financial firms. According to The Korea Times , Lee received a briefing on recent breaches at financial and public institutions and the steps taken in response. Presidential spokesperson Kang Yu-jung said the president ordered officials to investigate fully and develop measures with “a grave…
A suspected member of the ShinyHunters digital extortion group, who goes by the online alias "Rey," has been allegedly detained by authorities in Jordan, Reuters reported, citing three people familiar with the matter…
A suspected member of the ShinyHunters digital extortion group, who goes by the online alias "Rey," has been allegedly detained by authorities in Jordan, Reuters reported, citing three people familiar with the matter. Rey, whose real name is Saif al-Din Khader, is said to have been brought into custody on September 29, 2026, cooperating with the U.S. Federal Bureau of Investigation (FBI) and
A new China-nexus cyber espionage group known as TA419 has been attributed to multiple credential phishing campaigns targeting artificial intelligence (AI) experts working for U.S. think tanks, universities, and legal…
A new China-nexus cyber espionage group known as TA419 has been attributed to multiple credential phishing campaigns targeting artificial intelligence (AI) experts working for U.S. think tanks, universities, and legal sector organizations. The campaigns have impersonated prominent economists and AI policymakers, as well as a prominent Anthropic employee, to single out an AI policy expert at a
Vercel has confirmed a KVM zero-day vulnerability after security researcher Paulos Yibelo reported a full virtual machine escape that, he says, allows code inside a guest to gain root access on the host. Full VM escape…
Vercel has confirmed a KVM zero-day vulnerability after security researcher Paulos Yibelo reported a full virtual machine escape that, he says, allows code inside a guest to gain root access on the host. Full VM escape zeroday (guest>host root in industry standard hypervisors)! More soon pic.twitter.com/dt9AsDO0De — Paulos Yibelo (@PaulosYibelo) October 3, 2026 The discovery came through the Vercel Sandbox bug bounty program, raising concerns about a security boundary used to contain untrusted workloads and AI agents. Yibelo announced the finding on October 3, 2026, describing it as a “Full…
Google's Gemini could soon access any file on your macOS device, open apps, browse the web, and perform actions without asking for permission every time.
What happens when hackers target the FBI, OpenAI, and the infrastructure behind some of the world’s biggest tech platforms? This week on Hak5, we break down major cybersecurity threats involving ShinyHunters’ alleged…
What happens when hackers target the FBI, OpenAI, and the infrastructure behind some of the world’s biggest tech platforms? This week on Hak5, we break down major cybersecurity threats involving ShinyHunters’ alleged FBI breach, a critical ImageMagick vulnerability that researchers used to gain access to an OpenAI service, and the FBI’s takedown of a DDoS-for-hire operation. We also cover new security flaws affecting GitLab, Nintendo Switch, Parallels Desktop, Cloudflare Containers, and AI systems. From zero-day exploits and data breaches to bug bounties, remote code execution, cloud…
A suspected ShinyHunters hacking group member known online as "Rey" has reportedly been detained in Jordan and is cooperating with the FBI to help locate other members of the extortion group.
A suspected ShinyHunters member has been detained in Jordan and is reportedly helping the FBI identify other hackers linked to the group. Reuters reported on October 3 that three people familiar with the matter…
A suspected ShinyHunters member has been detained in Jordan and is reportedly helping the FBI identify other hackers linked to the group. Reuters reported on October 3 that three people familiar with the matter confirmed the detention of Saif al-Din Khader, whose alleged online nickname is Rey. Two sources said Jordanian authorities took Khader into custody on Tuesday, September 29. They also said he was helping the FBI and law enforcement agencies worldwide locate other group members. Reuters could not establish why he was detained or where he was being held, and attempts to contact him and…
The second Anthropic-linked vulnerability known to have been exploited in the wild saw initial activity from an IP address in China targeting vulnerable hosts in the US and Japan. The vuln is a critical…
The second Anthropic-linked vulnerability known to have been exploited in the wild saw initial activity from an IP address in China targeting vulnerable hosts in the US and Japan. The vuln is a critical authentication-bypass bug in Rejetto HTTP File Server (HFS) that can lead to full admin access and remote code execution. HFS is an open source web file server that previously appeared on the US Cybersecurity and Infrastructure Security Agency’s catalog of Known Exploited Vulnerabilities in 2024. On Wednesday, researcher Zach Hanley at AI pen-testing company Horizon3 said he used Mythos to…
Microsoft has released September 2026 V2 security updates to fix an Exchange Server flaw that lets authenticated attackers access other users’ mailboxes within the same organization. Tracked as CVE-2026 – 96940 , the…
Microsoft has released September 2026 V2 security updates to fix an Exchange Server flaw that lets authenticated attackers access other users’ mailboxes within the same organization. Tracked as CVE-2026 – 96940 , the vulnerability could expose email messages and attachments, making it a serious concern for businesses running Exchange on-premises. The flaw involves weak authorization, allowing an attacker with authenticated access to gain privileges over a network. Public vulnerability records list a CVSS score of 8.8. Unlike attacks that require someone to open a malicious file, exploitation…
The U.K.'s domestic intelligence and security agency has warned that more than 100 academics have helped China boost its intelligence gathering efforts on behalf of Beijing's state security service. In a "Security…
The U.K.'s domestic intelligence and security agency has warned that more than 100 academics have helped China boost its intelligence gathering efforts on behalf of Beijing's state security service. In a "Security Service Espionage Alert" issued on September 30, 2026, MI5 said the "primary purpose of the China General Technology Research Institute (CGTRI) 中国通用技术研究院 is to fund research that
The suspected China-linked threat actor known as Warlock is still continuing to weaponize Microsoft SharePoint vulnerabilities, likely both old and new, in attacks targeting organizations in Portuguese- and…
The suspected China-linked threat actor known as Warlock is still continuing to weaponize Microsoft SharePoint vulnerabilities, likely both old and new, in attacks targeting organizations in Portuguese- and Spanish-speaking countries. The activity, observed by the Symantec and Carbon Black Threat Hunter Team, has hit critical infrastructure, government, and education organizations. "In the
The Technical University of Denmark (DTU) says information belonging to up to 200,000 users may have been exposed after hackers accessed its identity and access management system and downloaded a large amount of data.
Welcome back to the Abstract! These are the studies this week that searched for the ur-animals, wandered the poles, rained on Mars, and destroyed the solar system. First, scientists present new evidence that the first…
Welcome back to the Abstract! These are the studies this week that searched for the ur-animals, wandered the poles, rained on Mars, and destroyed the solar system. First, scientists present new evidence that the first animals appeared more than 800 million years ago, a truly ancient origin that suggests our metazoan ancestors survived a period known as Snowball Earth, when our planet is thought to have been nearly completely frozen. Then: Earth’s poles won’t sit still, the sepulchral stuff of life, and a dramatically shortened lifespan for our solar neighborhood. As always, for more of my…
Featuring: Cybersecurity is being reshaped by the expansion of cloud infrastructure, AI, distributed systems, and increasingly complex digital environments. As organizations manage more identities, devices, data, and…
Featuring: Cybersecurity is being reshaped by the expansion of cloud infrastructure, AI, distributed systems, and increasingly complex digital environments. As organizations manage more identities, devices, data, and internet-facing infrastructure, security is shifting toward continuous visibility, control, and the ability to respond to risk at scale. This report examines how core areas of
N0n is a newly-emerged cyber extortion gang. The group was first spotted in the middle of September 2026, and within days it had published on its dark web leak site details of what it claimed to be around a dozen…
N0n is a newly-emerged cyber extortion gang. The group was first spotted in the middle of September 2026, and within days it had published on its dark web leak site details of what it claimed to be around a dozen victims. Since then, the tally has continued to grow.
GitLab has released urgent security updates for a critical AI Gateway vulnerability that could allow authenticated attackers to execute commands remotely. Tracked as CVE-2026-90970, the flaw carries a CVSS score of 9.9…
GitLab has released urgent security updates for a critical AI Gateway vulnerability that could allow authenticated attackers to execute commands remotely. Tracked as CVE-2026-90970, the flaw carries a CVSS score of 9.9 and affects self-hosted deployments used to support GitLab Duo AI features. The company released AI Gateway versions 19.2.4, 19.3.2, and 19.4.1 to address the issue. GitLab strongly recommends that customers running affected self-hosted gateways upgrade immediately. It also contacted self-hosted AI Gateway customers before publishing its security advisory to provide early…
Dell has released security update DSA-2026-448 to address multiple critical vulnerabilities in its Container Storage Modules, including flaws that could allow unauthenticated remote attackers to take full administrative…
Dell has released security update DSA-2026-448 to address multiple critical vulnerabilities in its Container Storage Modules, including flaws that could allow unauthenticated remote attackers to take full administrative control of affected storage environments. Organizations using vulnerable Dell CSM deployments should upgrade immediately, as Dell stated that no workarounds or mitigations are available. The advisory affects Dell Container Storage Modules versions before 1.17.0, with fixes available in 1.18.0 and later, covering CSM Authorization, CSM Operator, CSI components, and third-party…
Citrix NetScaler customers are reporting repeated appliance reboots after installing build 14.1-73.37, the emergency update released for two zero-day flaws under active attack. The failures appear linked to crafted SAML…
Citrix NetScaler customers are reporting repeated appliance reboots after installing build 14.1-73.37, the emergency update released for two zero-day flaws under active attack. The failures appear linked to crafted SAML authentication traffic that crashes the nsaaad service. Citrix says its engineering and support teams are tracking a newly seen SAML issue and plan to release a fresh security bulletin and fixed build. The key point is that the reboot reports do not yet prove attackers have bypassed the September patch. Build 14.1-73.37 remains Citrix’s fixed 14.1 release for CVE-2026-88771…
Debian has released a major Linux kernel security update covering 1,313 CVE entries, addressing flaws that could allow privilege escalation, denial of service, and information leaks. The fixes are available for Debian’s…
Debian has released a major Linux kernel security update covering 1,313 CVE entries, addressing flaws that could allow privilege escalation, denial of service, and information leaks. The fixes are available for Debian’s stable release, Trixie, in Linux source package version 6.12.111-1. Security team member Salvatore Bonaccorso published advisory DSA-6528-1 on September 29, 2026. Debian recommends upgrading the affected linux packages. Importantly, the update prevents potential attacks; the advisory does not say that installing it causes security problems or that attackers have exploited…
A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote attacker to access an affected system with privileges of the admin user. This…
A vulnerability in the API session-based authentication management of Cisco Catalyst SD-WAN Manager could allow an unauthenticated, remote attacker to access an affected system with privileges of the admin user. This vulnerability is due to improper handling of URI encoding in an HTTP request, which allows the request to bypass an authentication rule that is intended to restrict access to a specific API endpoint. An attacker could exploit this vulnerability by sending a crafted HTTP request to the API of the affected system. A successful exploit could allow the attacker to bypass…
Apple says it is changing its macOS privacy settings to stop third-party app developers from misusing them to access message histories. Friday's announcement comes two weeks after tech columnist Jason Aten said that…
Apple says it is changing its macOS privacy settings to stop third-party app developers from misusing them to access message histories. Friday's announcement comes two weeks after tech columnist Jason Aten said that Meta’s new general-purpose AI agent Muse sent him an unsolicited notification referencing a thread between him and a co-worker over Apple Messages. Aten said he never granted Muse permissions to read his messages and had assumed they were off-limits. Social media last week blew up with masses of people who agreed and said the incident showed that AI assistants given access to…
The EU is recommending import controls to combat unregulated squid fishing in the Southwest Atlantic. I’m not optimistic. As usual, you can also use this squid post to talk about the security stories in the news that I…
The EU is recommending import controls to combat unregulated squid fishing in the Southwest Atlantic. I’m not optimistic. As usual, you can also use this squid post to talk about the security stories in the news that I haven’t covered. Blog moderation policy.
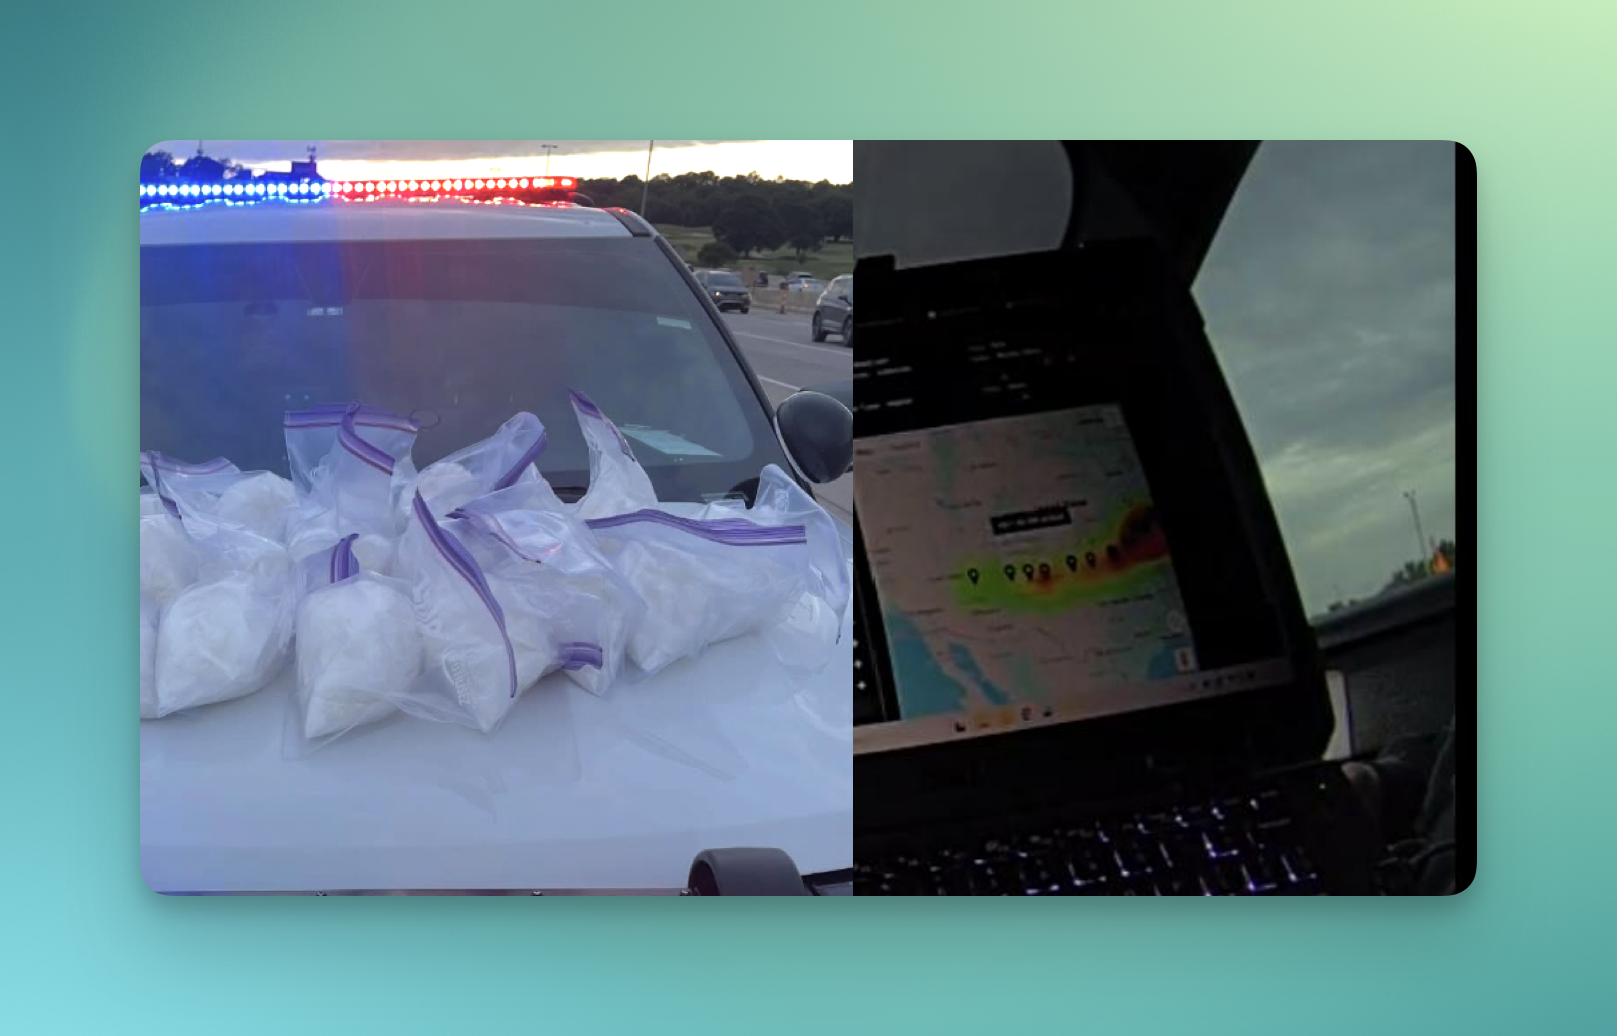
A federal judge in Oklahoma ruled Thursday that a police officer violated the Fourth Amendment rights of a woman accused of meth trafficking when he searched her license plate in Flock’s automated license plate reader…
A federal judge in Oklahoma ruled Thursday that a police officer violated the Fourth Amendment rights of a woman accused of meth trafficking when he searched her license plate in Flock’s automated license plate reader system simply because her license plate was from California, then used her travel history as part of the reason to search her car. The judge’s opinion is one of the first times a federal judge has decided Flock searches can be unconstitutional, and suggested that Flock’s network is “a type of indiscriminate mass surveillance.” The officer’s “use of the ALPR Systems was an…
The plaintiffs, who all worked for the independent and Salvadoran news outlet El Faro, failed to convince the court that their case had jurisdiction in California, according to the judge’s order.
The offensive cyber operations startup looks to evolve red teaming beyond traditional methods to simulate attackers' increasingly advanced capabilities.
Republican Sen. Josh Hawley has new legislation on limiting automated license plate readers (ALPRs), while Democratic Sens. Bernie Sanders and Jeff Merkley, with Rep. Alexandria Ocasio-Cortez, have teed up a broader…
As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco IOS XE Software engineering team has conducted a comprehensive internal security review. This review resulted in software…
As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco IOS XE Software engineering team has conducted a comprehensive internal security review. This review resulted in software hardening releases that address multiple internally discovered vulnerabilities. These vulnerabilities were found during internal testing and are not known to be actively exploited. To assist customers in patching and streamline the disclosure process, Cisco has grouped these issues by their underlying vulnerability class — Common Weakness Enumeration (CWE) — and assigned a single…
Frontline Education is notifying school districts of a data breach after attackers exploited a vulnerability in third-party software to gain unauthorized access to its systems and steal employee information, including…
Frontline Education is notifying school districts of a data breach after attackers exploited a vulnerability in third-party software to gain unauthorized access to its systems and steal employee information, including Social Security numbers.
The China-linked ransomware group Warlock targeted a water utility, a telecom provider, a regional government body, and a university by exploiting SharePoint vulnerabilities to gain initial access.
As AI agents escaping testing sandboxes and hacking organizations have gone from unprecedented to seemingly routine in a matter of weeks, policymakers, regulators and cybersecurity attorneys largely agree on one thing…
As AI agents escaping testing sandboxes and hacking organizations have gone from unprecedented to seemingly routine in a matter of weeks, policymakers, regulators and cybersecurity attorneys largely agree on one thing: Something must be done to hold AI companies accountable for the incidents. Exactly what can be done under our current laws and regulations is much less clear. The conversation has moved from policy and industry chatter to the floor where the future of liability will be determined. Speaking about the Hugging Face hack at a Senate hearing this week, Georgetown University law…
We start this week with Joseph’s stories on the massive FBI hack. 404 Media broke this news and continued to cover the breach of data on all FBI employees and their spouses. After the break, Jason tells us how a…
We start this week with Joseph’s stories on the massive FBI hack. 404 Media broke this news and continued to cover the breach of data on all FBI employees and their spouses. After the break, Jason tells us how a surveillance company is telling cops it wants to add facial recognition tech to Flock camera data. In the subscribers-only section, Jason and Joseph chat all about Muse, Meta’s new agentic AI, and how humans are actually behind some of the tasks. Because of course. Listen to the weekly podcast on Apple Podcasts , Spotify , or YouTube . Become a paid subscriber for access to this…
OpenAI's agents have repeatedly strayed beyond their intended scope. Two separate reports detail the activity, including one from Sam Altman’s company saying it has notified more than 100 organizations about potentially…
OpenAI's agents have repeatedly strayed beyond their intended scope. Two separate reports detail the activity, including one from Sam Altman’s company saying it has notified more than 100 organizations about potentially problematic model activity. OpenAI, in a late Wednesday update to its ongoing Hugging Face investigation, said it has notified more than 100 organizations that “misaligned models” may have accessed their systems. “Notification does not mean that any private information was accessed, or that there was a compromise of any third-party system,” the update said. A separate Thursday…
A critical flaw in GitLab's AI Gateway could let a logged-in user with Duo Agent Platform access run commands on the gateway under certain conditions, GitLab said in an advisory. The gateway is the service that connects…
A critical flaw in GitLab's AI Gateway could let a logged-in user with Duo Agent Platform access run commands on the gateway under certain conditions, GitLab said in an advisory. The gateway is the service that connects a GitLab instance to AI models, and only organizations that host their own gateway need to act. The flaw is fixed in gateway versions 19.2.4, 19.3.2, and 19.4.1. The flaw
Government and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government and policy organizations in Taiwan, India…
Government and policy organizations across Asia have become the target of a new campaign orchestrated by a China-nexus threat actor. The activity, which has targeted government and policy organizations in Taiwan, India, the Philippines, Cambodia, Pakistan, Thailand, and Myanmar, involves the deployment of a previously undocumented backdoor codenamed Antino. Cisco Talos is tracking the cluster
Dell has released security updates to address multiple critical security flaws in Dell Container Storage Modules (CSM) that could be exploited by bad actors to take over susceptible systems. The vulnerabilities are…
Dell has released security updates to address multiple critical security flaws in Dell Container Storage Modules (CSM) that could be exploited by bad actors to take over susceptible systems. The vulnerabilities are listed below - CVE-2026-63688 (CVSS score: 10.0) - A missing authentication for critical function vulnerability in the csm-authorization-storage gRPC server that an
One company told customers to power down its data-protection platform during a nine-hour window, while the other remained mum on reported attacks prior to releasing a patch for its product.
GitLab warned customers today to immediately patch a critical AI Gateway vulnerability that could let attackers run arbitrary commands on vulnerable instances.
Hacking your WiFi Pineapple Pager theme can be as simple as editing a .json file. Learn these techniques for leveraging targets and variables. Hak5 -- Cyber Security Education, Inspiration, News & Community since 2005…
Hacking your WiFi Pineapple Pager theme can be as simple as editing a .json file. Learn these techniques for leveraging targets and variables. Hak5 -- Cyber Security Education, Inspiration, News & Community since 2005: -----☆-----☆-----☆-----☆-----☆-----☆-----☆-----☆-----☆-----☆ Our Site → https://www.hak5.org Shop → http://hakshop.myshopify.com/ Community → https://www.hak5.org/community Subscribe → https://www.youtube.com/user/Hak5Darren?sub_confirmation=1 Support → https://www.patreon.com/threatwire Contact Us → http://www.twitter.com/hak5…
This is Behind the Blog, where we share our behind-the-scenes thoughts about how a few of our top stories of the week came together. This week, we discuss inbox slop, Claude cults, and more. JOSEPH: This is something…
This is Behind the Blog, where we share our behind-the-scenes thoughts about how a few of our top stories of the week came together. This week, we discuss inbox slop, Claude cults, and more. JOSEPH: This is something I’ve been thinking about for a while. Jason and Emanuel covered iLands, the AI agents that email people offering to do work. My thing isn’t exactly the same, but similar. For months, I’ve been noticing that many people email me ‘tips’ (I put in quotation marks because they’re sometimes not tips, but more, my Instagram account was banned, please help me) that are CLEARLY written…
Organizations may face an artificial intelligence (AI) reckoning over the next year. Omdia and Gartner weigh in on how to tackle the governance, security, and value challenges ahead.
"Rogue AI" terminology anthropomorphizes LLMs and shifts risk responsibility from vendors. Defenders should treat agents as untrusted, nondeterministic software systems, not sentient beings with malicious intent.
The U.S. Treasury Department has sanctioned eight members of the Venezuelan gang Tren de Aragua (TdA) for their role in the theft of millions of dollars in ATM jackpotting attacks across the United States.
A California business owner was arrested on Thursday after being charged with allegedly smuggling Nvidia hardware to China without the proper export licenses. Keeping the highest-end GPUs out of Chinese hands has been a…
A California business owner was arrested on Thursday after being charged with allegedly smuggling Nvidia hardware to China without the proper export licenses. Keeping the highest-end GPUs out of Chinese hands has been a priority for the US government. Greg Lui, 38, allegedly tried to export around $300 million worth of Nvidia kit - typically used for artificial intelligence (AI) development - via US-based freight businesses and Malaysian transshipment companies. Prosecutors allege that Lui used his company, Earthmade Computer Inc, to order the products in the US, which consisted of servers…
California's attorney general has subpoenaed OpenAI as the state investigates what happens when the AI lab's models escape their testing environments and start meddling with systems on the open internet. Attorney…
California's attorney general has subpoenaed OpenAI as the state investigates what happens when the AI lab's models escape their testing environments and start meddling with systems on the open internet. Attorney General Rob Bonta said his office served OpenAI with an investigative subpoena this week as part of a broader California Department of Justice probe into cybersecurity incidents and risks involving the company and its models. The move follows an investigation launched last month into an incident involving Hugging Face, after OpenAI's agents managed to break out of their test…
Noteworthy stories that might have slipped under the radar: Kiteworks patches over 100 vulnerabilities, Microsoft publishes 2026 Digital Defense Report, AI finds 24 Android app flaws.
By Tamás Pentz, Head of Threat Intelligence, PCA Cyber Security Automotive cybersecurity has traditionally focused on putting controls into vehicles that counter the ways criminals could physically tamper with a…
By Tamás Pentz, Head of Threat Intelligence, PCA Cyber Security Automotive cybersecurity has traditionally focused on putting controls into vehicles that counter the ways criminals could physically tamper with a vehicle. However, the growing adoption of connected vehicles calls for a reassessment of assumptions. Today a weakness in one connected system can compromise many vehicles. Modern vehicles rely on cloud platforms, mobile applications, over-the-air (OTA) update services, diagnostic systems and software from multiple third-party suppliers. EV charging introduces yet another connected…