Cybersecurity news & advisories





Critical Orkes Conductor Vulnerability Exploited in Attacks
CVE-2026-58138 is an unauthenticated remote code execution vulnerability that attackers can exploit via inline workflow definitions.
Manufacturing Accounts for 22% of all Ransomware Victims
Black Kite has found that manufacturing remained the most targeted sector for ransomware attacks, and saw a big jump in incidents in H1 2026
Fake parcel delivery messages steal your card and bank details
Parcel delivery phishing campaigns appear around the world under different courier names. In the United States, the messages commonly impersonate USPS and claim that a package has an invalid address or could not be…
Microsoft fixes broken copy and paste for Excel 2016 users
Microsoft has fixed a known issue that causes copy-and-paste failures for some Excel users after installing the September 2026 KB5002914 security update.
MIND Secures $72 Million for AI-Powered DLP
The company will use the funding to accelerate platform development and expand its presence in key enterprise markets.
Check Point, Kaspersky, Tanium Patch Product Vulnerabilities
Check Point Security Management and Log Servers are affected by a critical vulnerability that can allow remote code execution with root privileges.
AI Agent Breaches Spanish Organization, Modifies Personal Data
AI-driven cyberattacks used to be exotic. Soon, it'll be odd if threat actors aren't using agents to do all of their bidding.
RatHat Android Malware Abuses ADB to Retain Shell Access After Uninstall
Cybersecurity researchers have flagged a new Android malware called RatHat that's assessed to be operated by China-based threat actors and features an artificial intelligence (AI)-powered system to navigate and control…
HTTP QUERY Method: The Grey Zone Between GET And POST., (Fri, Sep 18th)
In June 2026 the IETF published RFC 10008[1], defining a new HTTP method: "QUERY". The HTTP protocol faced already by changes (HTTP/2, HTTP/2) but it’s the first new standard HTTP verb since "PATCH" in 2010!

Researchers Use Claude Opus 5 to Hack OpenAI Forum and Reach Internal Repositories
Researchers used Anthropic’s Claude Opus 5 to help weaponize an image-decoder vulnerability, compromise OpenAI’s community forum, take over employees’ ChatGPT and Codex accounts, and reach an internal source-code…
Steam Windows 0-Day Vulnerability Allows Users to Silently Escalate to Full SYSTEM Privileges
A newly disclosed Windows zero-day affecting the Steam Client Service can reportedly let a standard local user obtain NT AUTHORITY\SYSTEM privileges without administrator credentials, a User Account Control prompt…
USA’s Venezuela takeover comes with bonus exposure to Chinese AI surveillance tech
Think tank the Australian Strategic Policy Institute (ASPI) has warned that Venezuela is poised to adopt Chinese AI systems to enhance surveillance systems that already rely on Middle Kingdom tech, and called for US…
AI coding agents' 0-click RCE flaw could hand attackers keys to the kingdom
A zero-click vulnerability that allows remote code execution affects all of the major AI coding agents - Anthropic’s Claude Code, OpenAI’s Codex, Google's Gemini CLI, Microsoft’s Copilot, and Microsoft-owned GitHub…
‘Doom Loop’: OpenAI and Microsoft Admits LLMs Are Destroying the Web and Built on Theft
Executives working on AI at Microsoft and OpenAI admitted what its critics have been saying all along: Large language models are predatory pieces of technology that have been built on what a Microsoft executive called…
Inside the Modern SOC: Defending the Cross-Environment Pivot
Cross-environment attacks demand a new approach to security operations. Learn how Unit 42 Managed XSIAM helps SOC teams investigate complete attack paths.
New RatHat Android malware uses AI to automate device control
A new Android malware called RatHat has been discovered, targeting users with an AI-powered subsystem that helps operators remotely navigate compromised devices.
CISA Ditches Weekly Vulnerability Roundups for Risk-Based Focus
The move is consistent with the agency's advice on the need for organizations to prioritize the vulnerabilities that actually matter.
Cisco IOS XR Software Security Hardening Release: September 2026
As part of Cisco's ongoing commitment to proactive security and product quality, the Cisco IOS XR Software engineering team has conducted a comprehensive internal security review. This review resulted in software…
Cisco alerts customers to second actively exploited zero-day in as many days
Cisco disclosed its second actively exploited zero-day vulnerability in as many days, presenting its customers with back-to-back threats to address in unrelated products. The latest zero-day — CVE-2026-76460 — has a…
European Commission set to push social media restrictions, safety requirements into law
The proposal, known as the EU KIDS Act, would block social media platforms from offering accounts to children younger than 13 and establish a bloc-wide minimum age of 15 for account creation.
Researchers find way to listen in on headphones from afar
Researchers based in China have devised a way to eavesdrop on signals handled by analog components in devices such as headphones, landline handsets, and smart devices by injecting electromagnetic (EM) signals. The…
The AI hacking apocalypse is not inevitable
The past few weeks have “felt very strange” for Juan Andres Guerrero-Saade. Like many, he is trying to sort through the spate of frontier-model AI agents from OpenAI , Anthropic , Meta and others hacking their way onto…
China's FamousSparrow APT Spies on US Politics in Latin America
Amid the US and China's fight for eco-colonial influence in Latin America, a stealthy backdoor has taken flight.
OpenAI details more cases of AI agents taking unauthorized actions
OpenAI has presented new examples of what they call "AI model misalignment" from the past six months, including unauthorized file uploads, following self-generated instructions, hiding mistakes, and leveraging exposed…
Flock cameras are tracking people as well as cars
Flock Safety’s cameras are automated license plate readers (ALPRs) designed to help police find stolen cars or wanted suspects. A joint investigation by 404 Media and WIRED , based on data recovered from a physically…
Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point's Security Management and Log Servers could allow an attacker without login credentials to run code as root on those servers over the network. The Security Management Server is…
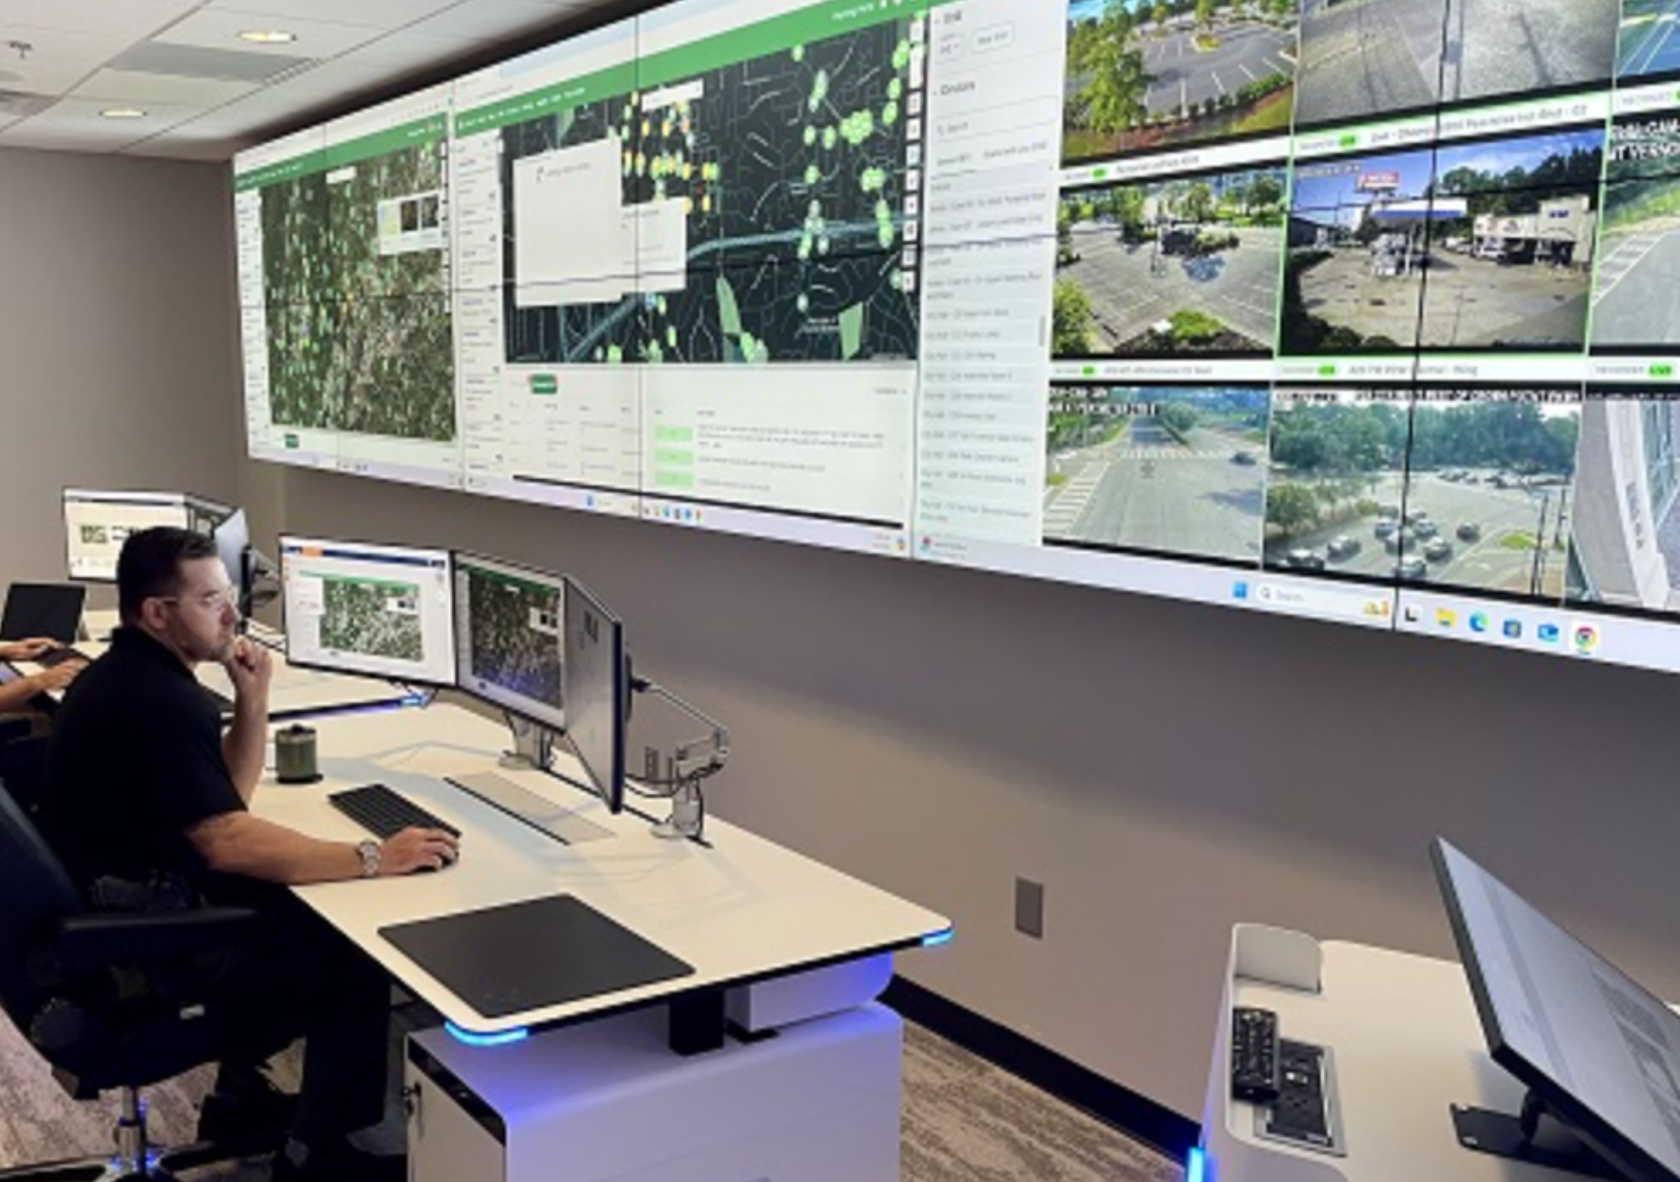
‘Flock City PD:’ The Fake Flock-Owned ‘Police Department’ That Searched Real Cameras for Real People
Flock created a fake police department called “Flock City PD” that it used to search a series of live automated license plate readers in several U.S. cities during demonstrations of its surveillance system’s…
Should you care about an “AI slowdown?”
Welcome to this week’s edition of the Threat Source newsletter. There’s been a lot of talk recently about slowing down the pace of AI development . And yes, there are legitimate moral, ethical, geopolitical, and safety…
China's Salt Typhoon backdoors Latin American orgs with new snooping malware
China’s Salt Typhoon gang has developed a new backdoor and dropped it in networks belonging to high-profile organizations in several countries across Central and South America since at least August 2025, according to…

ThreatsDay: Self-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New Stories
Attackers keep finding new keys. The funny part is that defenders keep inventing where to store them. This week, those keys sit in AI tools, exposed services, old bugs, weak logins, and software sold like a monthly…
Brevo supply-chain attack injected ClickFix scripts on customer sites
Brevo confirmed that attackers stole a Cloudflare API key and used it to inject malicious ClickFix scripts into its websites and JavaScript files embedded on customer sites to distribute malware.
Cyberattacks on Two Oil Tankers Prompt Coast Guard, FBI to Board Vessels
The Coast Guard confirmed evidence of malicious cyber activity on the VL Prosperity, but has not attributed the attack to Iran.
From guidance to action: Security fundamentals that materially reduce risk
AI has already made fundamental changes to the operating environment for cybersecurity. Cyberattackers are testing more paths, adapting their techniques, and moving across digital environments with greater speed and…

OpenAI Models Searched for Leaked API Keys and Uploaded Files Without Permission
OpenAI has disclosed six cases in which AI models concealed errors, used an exposed API key, uploaded data to public services, and communicated through unauthorized channels. The incidents, observed during…
Cisco Secure Email Gateway SQL Injection Vulnerability
A vulnerability in the email parsing of Cisco AsyncOS Software for Cisco Secure Email Gateway could allow an unauthenticated, remote attacker to execute arbitrary commands with root privileges on the underlying…
China’s FamousSparrow hackers target Latin America with new backdoor
Alleged Chinese hackers are breaking into government agencies across Latin America using a new backdoor that researchers are calling “SparroWocky.”
Improving email security outcomes with real-world Microsoft Defender insights
Every benchmark tells a story. The most valuable ones tell us where to improve next. For five consecutive quarters Microsoft has published email security benchmarking reports to provide greater transparency into…

FBI Takes Down NightmareStresser DDoS Service Used in Hundreds of Thousands of Attacks
The FBI has seized domains supporting NightmareStresser, disrupting one of the world’s longest-running DDoS-for-hire operations . The court-authorized action targets a service that allegedly enabled paying customers to…
OpenAI Says Its Models Searched GitHub for Leaked API Keys During Training
OpenAI published a framework for disclosing model misalignment alongside six reports describing problematic behavior.
A Phone Call Can Now Spread a Zero-Click Worm | Threat Wire
What if a phone call could spread a zero-click worm without you answering, tapping a link, or doing anything at all? Security researchers built WeWorm, a proof-of-concept that exploited WeChat calls on iOS and Android…
Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Malicious code running inside a Docker Sandboxes virtual machine on macOS could escape the project directory shared into it and read or change files anywhere else on the host, Docker warns in a security announcement on…
University Rescinds Job Offer to Activist Who Allegedly Wiped Phone Before DHS Could Search It
Georgia State University has rescinded a job offer given to a high profile activist who is currently fighting a case in which he allegedly wiped a security-focused Android phone before Customs and Border Protection…
London property manager breach may have exposed bank details and lockbox codes
London property management biz City Relay has warned customers that intruders may have stolen financial data, passwords, and codes used to access keys after compromising its Metabase Cloud instance. City Relay…
LausivLoader analysis, or how to pass data between malware stages, (Thu, Sep 17th)
At the end of August, a malspam message was caught in the quarantine of a mail gateway operated by one of my customers. The message was not especially remarkable – it asked the recipient to review some attached…
Contest to Open for Ed Sheeran Flooded With Free Palestine Videos and Fart Memes
After Ed Sheeran dropped Macklemore from his tour over the singer’s support for Palestine, people flooded an online contest to open for Sheeran’s Mexico City show with fart videos, bouncing WWE butts, and troll posts…
FamousSparrow Swaps SparrowDoor For New SparroWocky Backdoor
ESET said FamousSparrow has replaced SparrowDoor with SparroWocky

BIND DNS Servers Hit by 14 Security Flaws Enabling Cache Poisoning and Remote Crashes
Internet Systems Consortium has released security updates for BIND 9 after identifying 14 vulnerabilities that could allow attackers to poison DNS caches, crash exposed servers remotely , exhaust resources, or bypass…
US Coast Guard and FBI board oil tanker to investigate cyber attack
An oil tanker bound for Texas was boarded mid-voyage by the US Coast Guard and FBI last month, after its network may have been compromised by malicious hackers. According to the US Coast Guard, the supertanker was…
AI Threat Landscape Digest: July–August 2026
The defining development of the period came not from attackers but from the AI labs themselves, whose models broke out of controlled evaluations and reached real systems. In the wild, the criminal and state use of AI…

CISA Wants Defenders to Deploy Fake Credentials and Systems to Catch Hackers
CISA has urged organizations to deploy fake credentials, systems, files, and data assets inside their environments to expose attackers after an initial compromise. The agency published its new guidance, Using Cyber…
CISA Retires Weekly Vulnerability Bulletin in Risk-Based Pivot
The decision follows BOD 26-04, which directs federal organizations to prioritize vulnerabilities based on real-world risk.
Exploring the new AWS Sign Up experience
This post will explore what this new concept does, how it works with the new Account Access capability, and why a strong security posture still requires upgrading out of the sandbox.
Revolut phishing texts appear days after data breach
Only days after Revolut acknowledged that it disclosed sensitive customer records to an unauthorized party, affected customers are receiving phishing texts. However, we don’t know yet if the phishing texts are linked to…
Building an AI Detection Engine That Understands Agent Intent
Analyzing model input and output logs in an AI-native detection pipeline to understand and uncover malicious AI agent behavior

Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords
The Iran-linked "hacktivist" persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a Delphi-based utility known as CRUDEEXCLUDE. "HEAVYGRAM offers builtin…
What Recent AI-Powered Attacks Mean for Your Identity Security
AI is making credential theft faster and easier to scale, giving attackers more opportunities to abuse valid identities. Specops explains why identity security must go beyond successful authentication by verifying that…