Security Feed
Cybersecurity news & advisories
500 articles 45 of 45 sources updated RSS ↗






Latest
Hackers now scanning systems for recently-patched Oracle flaw
Attackers have begun probing the Internet for systems unpatched against a recently disclosed critical Oracle E-Business Suite (EBS) vulnerability.
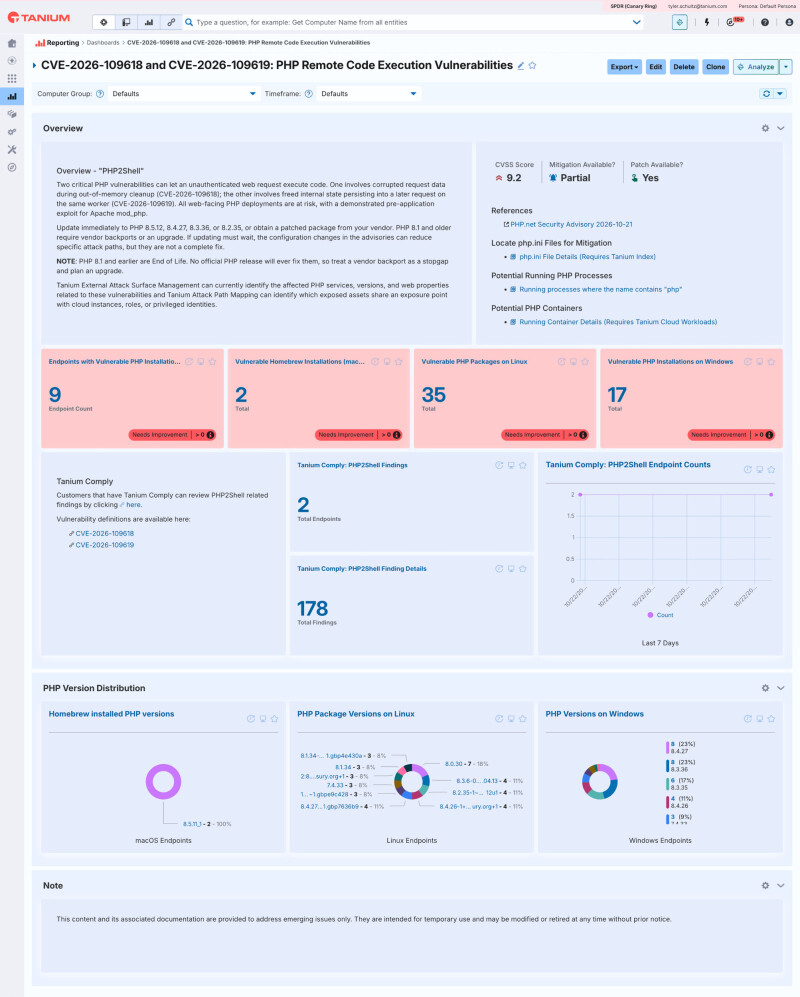
China-Linked Hackers Exploit PHP2Shell to Root Firewalls
The attackers chained PHP2Shell and Fragnesia exploits and hacked two servers of a US government-affiliated organization.
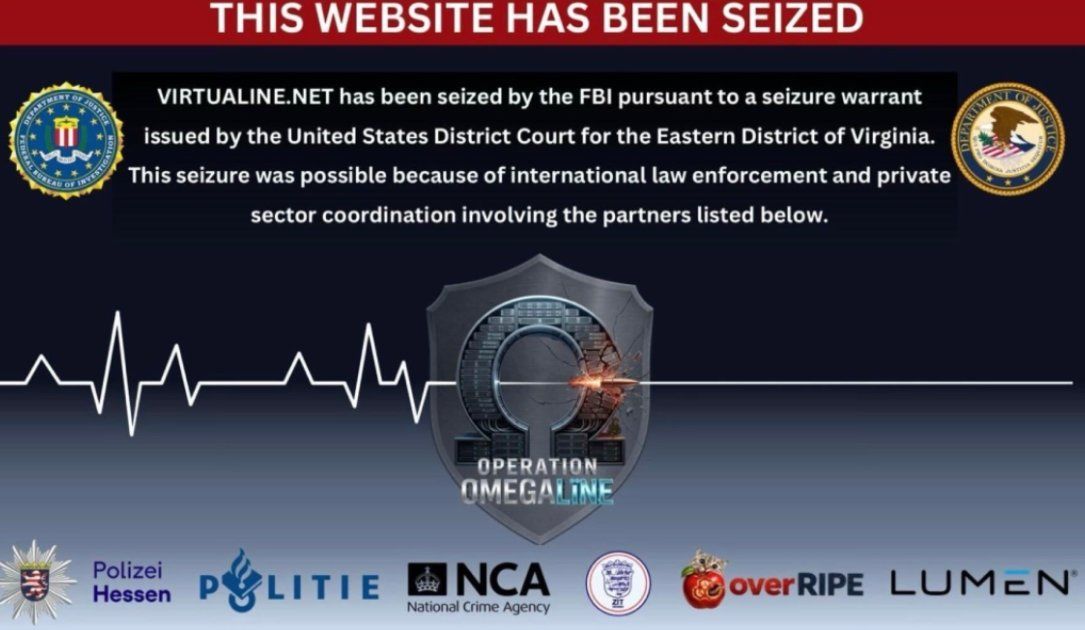
FBI seizes ‘bulletproof’ hosting site accused of facilitating child abuse, money laundering
The FBI seized the domain of a “bulletproof” hosting provider accused of facilitating a range of cybercrimes, including money laundering and the distribution of child sexual abuse material.
Cisco open sources tool for detecting AI agents on hacking sprees
Cisco has open sourced a behavior detection engine that watches AI agents, to help security teams prevent rogue agents from going off the rails like they did with the Hugging Face hack – or worse. It’s called Project…
123 Reg discloses 'AI cyberattack' on customer data, suspects China nexus
UK domain registrar 123 Reg (no relation – Ed) says it was the victim of an “AI-driven cyberattack” that exposed customer data. Customers began receiving their notification emails this week, informing them that their…
Adobe Fixes 8 Critical Campaign Classic Flaws Allowing Code Execution and Security Bypass
Adobe has released patches to address multiple critical security flaws in Campaign Classic that, if successfully exploited, could result in arbitrary code execution, security feature bypass, and privilege escalation…
Chrome and Firefox updates fix serious security flaws. Install them now
On October 27, Google issued a new Stable channel update for Chrome. Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 156.0.8078.73/.74 for Windows and Mac and 156.0.8078.73 for…
Hackers Compromise Camera Management Software to Deploy Malware on Windows Computers
Hackers have compromised camera management software to deploy malware on Windows computers, using a legitimate Microsoft program to run malicious code and maintain access. The activity shows how software used to manage…
Long-Hidden Flaws Patched in EPICS Research Facility Control Software
Four EPICS Base flaws found by an autonomous system could let attackers crash processes at particle accelerators and fusion labs.
CISA warns of hackers now exploiting critical Node2Shell flaw
On Tuesday, the US Cybersecurity and Infrastructure Security Agency (CISA) confirmed that hackers have begun exploiting a critical Brotli vulnerability known as Node2Shell, Broccoli2Shell, and HTTP2Shell.
Hackers Actively Exploiting New Oracle EBS RCE Vulnerability
Hackers have begun testing a critical Oracle E-Business Suite vulnerability that can let them run commands without logging in. Threat intelligence firm Defused reported exploratory exploit attempts against its decoy…

American Organizations Under Attack: Skyw4lker Device Code Phishing Campaign Exposed
Modern phishing campaigns can compromise American businesses without relying on traditional credential theft. Attackers can abuse legitimate cloud services, authentication mechanisms, and trusted business workflows to…
Nobody Trusts the Security Questionnaire. We Rely on It Anyway
The process that gates nearly every B2B deal is a self-assessment the sender distrusts and the receiver accepts. There is finally a better basis for trust between companies.

FortiBleed 2.0 Reveals Thousands of Fortinet VPN and Active Directory Credentials in Exposed Configurations
FortiBleed 2.0 investigation, published October 27, revealed 40,573 cleartext secret records in exposed FortiGate configurations, including 37,076 local-user passwords and 1,576 Active Directory LDAP bind records…
Millions of security cameras at risk: DoS vulnerability in Intelbras devices
Background Network-connected surveillance cameras are now widespread in both home and enterprise environments, so securing them is essential to safeguarding physical spaces and sensitive assets. As these devices…

Microsoft Releases Emergency Windows Updates to Block Compromised eMudhra Certificates
Microsoft released emergency Windows trust updates after discovering eight recoverable eMudhra intermediate CA private keys that could let attackers forge trusted certificates or sign malicious content. Microsoft said…

Hackers Use CyberStrikeAI Agents to Automate Network Scanning, Exploitation, and Data Theft
Hackers have abused CyberStrikeAI, an open-source penetration-testing platform, to coordinate 44 AI agents across network scanning, exploitation, persistence, and data theft. The activity primarily targeted Japanese…
Secrets Management Firm Infisical Valued at $600 Million After $40 Million Raise
The company will use the Series B funds to expand its platform for securing AI agents’ access to sensitive systems.
Nefilim and Hive ransomware affiliate gets 70 months in prison
A Ukrainian national was sentenced to 70 months in prison for his role in ransomware attacks targeting hospitals, government entities, and high-revenue businesses worldwide between 2018 and 2021.
Coinbase Customer Data Exposed Via Analytics Vendor Amplitude Security Incident
Coinbase has disclosed that a security incident at analytics provider Amplitude exposed contact information belonging to a small subset of its customers. The cryptocurrency exchange said it found no evidence of…

ICE Is Running One of the Largest Anti-Left Surveillance Operations in US History
ICE’s Homeland Security Investigations is engaged in far-reaching spying against left-wing activists that rivals the FBI and CIA crackdowns on the Civil Rights and anti-war movements.
CISA Warns of PHP2Shell Vulnerabilities Actively Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency has added two critical PHP vulnerabilities , jointly known as PHP2Shell, to its Known Exploited Vulnerabilities catalog after confirming real-world exploitation…
Hackers Start Probing Fresh Oracle EBS Vulnerability
CVE-2026-101767 is an unauthenticated SQL injection that can be exploited for remote code execution.

Hackers Hijack Government and School Subdomains to Promote Illegal Gambling Websites
Hackers have abused government and school domains to promote illegal gambling websites, creating unauthorized subdomains while leaving the institutions’ main websites running normally. Two unrelated operations used…
CISA Warns of Node2Shell Exploitation as Honeypots Log Attack Attempts
CISA added the Brotli flaw to its KEV catalog, and two honeypot operators logged attempts, including one that used a broken exploit.
Anthropic's Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux Exploits
An unreleased Anthropic AI model found security flaws in Chrome, Safari, Android, Windows, and Linux and chained them into working proof-of-concept exploits, the company said in its latest report. The exploits were…

Top 10 Best Ransomware Recovery Solutions in 2026 [Ranked & Scored]
Prevention lost; now what? That question not backup-window math defines ransomware recovery , a discipline measured in hours-to-business and judged on three hard problems: finding the clean restore point, proving it’s…

Top 9 Best Backup & Recovery Solutions in 2026 [Ranked & Scored]
Ransomware crews attack backups before they attack production encrypting or deleting recovery points first, then ransoming what’s left. That inverted kill chain has turned backup from an infrastructure checkbox into a…

FBI Seizes Virtualine Domain Over Alleged Criminal Hosting and Bitcoin Money Laundering
The U.S. Department of Justice (DoJ) on Tuesday announced the seizure of a domain associated with a bulletproof hosting provider (BPH) named Virtualine. The move was in response to the service being used to commit and…

Japan's GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud Breach
Japan's GMO Internet Group is offering up to $1 million in total for tips that help catch the attackers who breached its Onamae.com Desktop Cloud service, after refusing to pay an extortion demand. The reward program…

Tailscale Patches SSH Flaws That Could Let Hacked Devices Gain Root Access on Other Servers
Tailscale has released version 1.104.4 to fix flaws in its built-in SSH server that could let an attacker reach services and files on other servers that only the root user should be able to touch. The flaws are in how…

ShinyHunters-Exploited Oracle PeopleSoft Zero-Day Turns Out to Be Three Chained Flaws
The critical Oracle PeopleSoft bug that ShinyHunters has exploited since May is not one flaw but three chained together, the researchers who reported it said this week. Oracle patched all three under a single…
Third Serengeti Sweep Tops 1,400 Arrests as Investigations Mature
Interpol's annual Operation Serengeti, now on its third iteration, led to 1,462 arrests across 20 African countries and the US, recovering $105 million in stolen funds.

Adobe Commerce PolyShell Attacks Breach Hundreds of Stores as Brotli Exploit Traffic Emerges
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday added two vulnerabilities impacting Adobe Commerce and Magento, and Google's Brotli decoder library to its Known Exploited Vulnerabilities…
Risky Business #857 -- AI FUD intensifies
On this week’s show Patrick Gray and James Wilson are joined by special guest co-host Alex Stamos to talk through the week’s cybersecurity news, including: Everyone’s still panicking about “misbehaving” AI models that…
Japan's GMO urges customers to shut down PCs amid ransomware threat
The GMO Group has urged customers to disconnect their systems from the internet and shut down computers after a threat actor who breached the company's Onamae Desktop Cloud threatened to launch a ransomware attack today.
OpenAI's GPT-6.1 Terra is safer overall, but shows more destructive-action flags in tests
OpenAI confirmed GPT-6.1 Terra is safer overall than some of its older models, but its safety testing also found other problems.
UNM Health ransomware attack disrupts patient care, surgeries
The University of New Mexico Health Sciences Center disclosed a cyberattack that caused system outages and disrupted patient care and academic activities.
Vulnerabilities in node.js Affecting Cisco Products: October 2026
On October 21, 2026, Node.js announced the availability of fixes for multiple vulnerabilities across the following supported release lines: 22.x, 24.x, and 26.x. These vulnerabilities impact critical operations such as…
Before you file that AI bug report, OpenAI has some advice
Even OpenAI is admitting there is a lot of AI slop in the security space. An executive for the frontier AI company said Tuesday that AI -generated vulnerability reports are overwhelming open-source maintainers, leading…
3 Frameworks to Protect CISOs & Orgs Against AI Liability
Cyber leaders can get ahead of AI liability with rigorous documentation, transparency, and smart contract negotiations with AI vendors.
Hackers hijack Convertr analytics script to steal payment card data
A credit card skimming group reportedly compromised a shared analytics script used by e-commerce platform Convertr to steal shoppers' payment data during checkout.
Vulnerabilities in PHP Affecting Cisco Products: October 2026
On October 21, the PHP Foundation announced the availability of a Critical PHP Security release addressing two critical vulnerabilities: CVE-2026-109618 - RCE via OOM corruption CVE-2026-109619 - RCE via stale global…
External Teams Chats Anchor 15-Minute Malware Delivery
Mail bombing is getting a new look with a wide-scale, ongoing social engineering campaign that might be tied to the Black Basta ransomware gang.
All the security risks Anthropic is worried about before its IPO
Anthropic said its AI systems could drastically reshape the software and cybersecurity sectors in the “near term,” while also laying out a litany of cybersecurity and regulatory risks facing the company as it prepares…
Nefilim, Hive ransomware operator given five-year-plus sentence after guilty plea
Ukrainian national Artem Stryzhak, 36, had pleaded guilty last year to charges related to participating in at least two well-known ransomware groups.
Code-execution flaw in UEFI firmware affects most servers on planet Earth
Defenders across the world face the burden of responding to yet another botched code-execution vulnerability, this time in boot-time firmware used by most of the world’s server vendors and data centers. The…
SBOMs Alone Can't Reveal the Scope of a Supply Chain Attack
A recent Shai-Hulud attack shows defenders need real-time visibility into production code and affected services to respond to supply chain compromises.
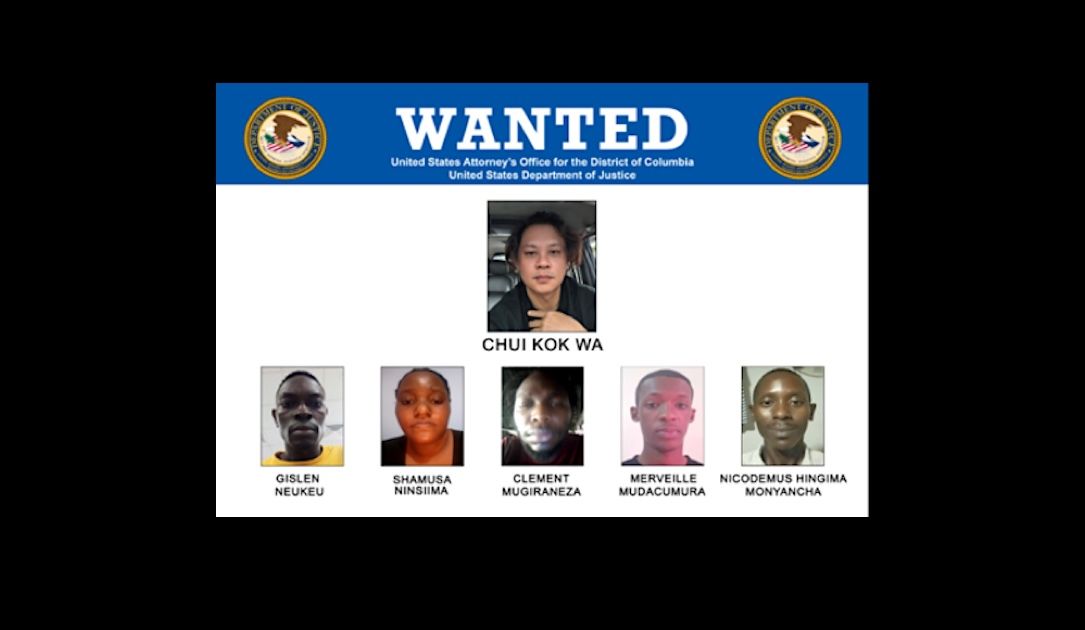
US indicts Malaysian national after Madagascar scam operation uncovered
DOJ action against five foreign nationals — plus a sting in Madagascar — highlight the expanding global reach of the scam center industry.
AI 'hacker' finds 4 severe bugs in popular industrial control software in under 4 hours
An autonomous AI agent discovered four vulnerabilities in the decades-old, widely used EPICS (Experimental Physics and Industrial Control System) open source software toolkit, including a critical flaw that could allow…
Prolific Hive and Nefilim ransomware affiliate sentenced to 70 months in prison
A 36-year-old Ukrainian national was sentenced to 70 months in prison for participating in a string of ransomware attacks targeting various critical infrastructure operators and businesses from the middle of 2018 to…

CyberStrikeAI Uses 44 AI Agents to Automate Hacking Operations Against Japan Targets
Cybersecurity researchers have disclosed details of three cyber attacks targeting organizations in Japan in which artificial intelligence (AI) was a key element, either in the driving seat or to assist a human operator…
Microsoft releases Windows OOB updates to distrust eMudhra certificates
Microsoft has released out-of-band (OOB) Windows updates to remove trust in certificates tied to compromised eMudhra certificate authority keys, protecting systems that do not receive automatic certificate trust updates.
Cisco Informational for Emergency Distrust of eMudhra Root and Intermediate Certificate Authorities
Between October 17 and October 20, 2026, a critical security compromise involving Certificate Authorities that are managed by eMudhra was uncovered. A security researcher demonstrated that the private keys for eight…
Beware the Slasher: AI Could Kill Off Cybersecurity Pros' Skills
Nathan Hamiel outlines potential SecOps horror in the AI midst, as core technical capabilities go the way of reading an atlas or remembering phone numbers.
'Aokigahara' Stealer Targets 'Developer Keyrings' & AI Assistants
The malware's focus on AI tools expands the traditional infostealer playbook to expose a forest of AI sessions, sensitive business data, and developer infrastructure from a single compromised endpoint.
Warp discloses breach exposing AI agent logs, user telemetry data
Agent decision logs and telemetry data belonging to Warp agentic development environment users were exposed in an attack on a third-party vendor in the project's infrastructure.
Day 2 of canceled classes at University of New Mexico after Health Sciences Center cyberattack
The University of New Mexico is canceling classes across the medicine, nursing, and pharmacy faculties for a second day amid continued efforts to recover from a "cybersecurity event." The attack targeted the Health…