Security Feed
Cybersecurity news & advisories
500 articles 45 of 45 sources updated RSS ↗


Latest
Cyber incident hits grocery stores in US, Netherlands and Belgium
Ahold Delhaize, the Dutch multinational retailer, announced it was taking precautionary measures following a cybersecurity incident, with stores in the U.S., Netherlands and Belgium reportedly impacted.
Cyberattacks crank French supermarket refrigeration systems up to 50°C
Cyberattacks on supermarket refrigeration systems reportedly pushed temperatures as high as 50°C (122°F), affecting hundreds of stores in France and forcing retailers to discard food. Major supermarkets such as…
Small AI Models May Soon Be Able to Self-Replicate on IoT Devices, Anthropic Warns
Experiments show cheap TV boxes can run capable AI models, and small models may soon be able to spread across such devices on their own.
CVE-2026-97229: Critical Unauthenticated Remote Code Execution in GitLab
Overview On October 12, 2026, GitLab published a critical patch release for CVE-2026-97229 , an integer overflow or wraparound ( CWE-190 ) in the CI/CD regular expression compiler affecting GitLab Community Edition (CE)…
Hackers heat up supermarket fridges, spoiling food across France
A cyberattack has forced hundreds of supermarkets across France to throw away refrigerated and frozen food after attackers interfered with the systems that keep it cold. The attack caused significant financial losses…
'123456' password linked to Denmark data breach affecting 8.8M people
A person claiming responsibility for the breach of Denmark's Central Register of Persons (CPR) says they gained access through an IT company's account protected by the password "123456." The person told Danish news…
XWorm RAT Evolves Into Surveillance Platform
Expanded plugin count allows the malware to monitor users’ location, stream live audio, and interact with authenticated browser sessions.

LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network
Three vulnerabilities in LG's webOS can be chained to give an attacker on the same local network root access to certain smart TVs without a PIN or any interaction from the owner. LG has issued a fix, according to an…
AI Turns Familiar Cyberattacks Into a Race Against Time
IBM’s Steve Wallin talks to SecurityWeek on the effect of AI-driven attacks on enterprise defenses.

npm Trusted Publishing Flaw With 10 Million Downloads Exposes 1,500+ Packages to Malicious Takeover
A security flaw in npm’s Trusted Publishing feature exposed more than 1,500 packages to possible takeover through reclaimed GitHub repository names. The affected packages accounted for more than 10 million total…
$86 Million Crypto Heist Linked to Ledger Signer Hardware Implant
A small circuit board hidden under the signers’ screens read user data and transmitted it to the attackers.

Hackers Exploit Citrix NetScaler 0-Days to Deploy Platypus Remote Access Tool
Threat actors are exploiting two critical Citrix NetScaler zero-day vulnerabilities to deploy a modified Platypus remote access tool on exposed ADC and Gateway appliances. The activity shows how quickly attackers are…

Product Walkthrough: Bitdefender AI Visibility and Control
A user opens a browser tab, pastes data into a chat assistant, and nothing is installed. A developer adds a coding assistant as an editor extension, and nothing shows up in the installed programs list. Someone downloads…

Top 10 Best Mobile Application Security Testing Tools in 2026 [Ranked & Scored]
Mobile security is two budgets wearing one name: testing finds the flaws before release, shielding hardens the binary against the hostile devices it ships to. When evaluating Mobile Application Security Testing (MAST)…
Top 10 Best SBOM Tools in 2026 [Ranked & Scored]
Federal buyers, the FDA, and the EU’s CRA era all want your software’s ingredients list and next year’s CVE will interrogate the SBOMs you generate today. Evaluating these platforms alongside the Top 10 Best Software…

Top 10 Best CI/CD Pipeline Security Tools in 2026 [Ranked & Scored]
Supply-chain attackers stopped bothering with your code they poison the pipelines that build it. Modern build pipelines execute untrusted third-party code with elevated infrastructure privileges, making CI/CD pipeline…

Top 10 Best RASP Tools in 2026 [Ranked & Scored]
RASP’s idea block attacks from inside the running app won so convincingly that observability and edge platforms absorbed it, leaving a thinner standalone market that stale lists misrepresent. Rather than relying solely…

Meta Zurp AI Toolkit Connects Burp Suite With AI Coding Agents for Bug Bounty Research
Meta has introduced Zurp, an open-source toolkit that connects Burp Suite workflows with AI coding agents for approved bug bounty research. The project is designed for vetted researchers in Meta’s bug bounty program and…
Amazon Fire TV Cube 3 Exploit Enables Root Access and Bootloader Unlock
A public exploit package now lets owners of Amazon’s third-generation Fire TV Cube gain persistent root access and unlock the bootloader on firmware PS7717 or older. Released by XDA developer Pro-me3us, the project…
UK Government Announces Sweeping New AI Security Plans
The government is planning tweaks to legislation, new incident response and more to head of AI security threats
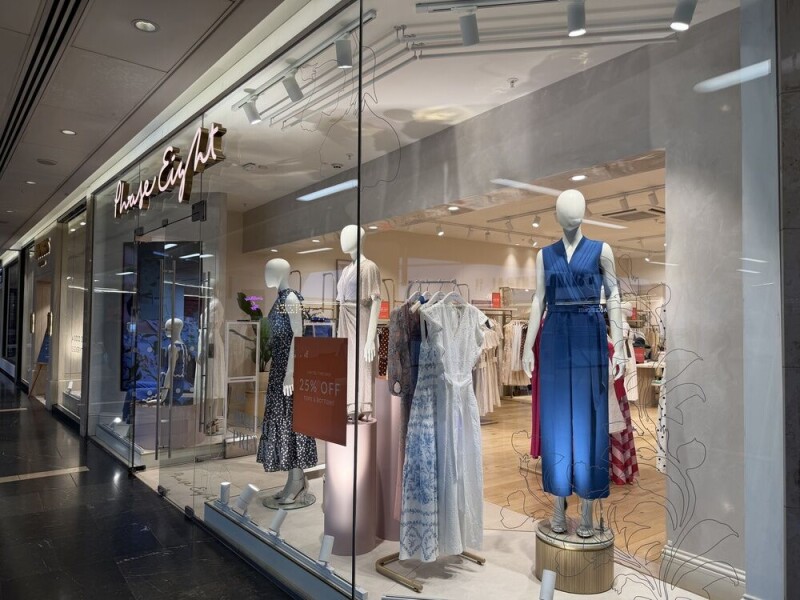
Owner of fashion brands Hobbs and Whistles joins autumn pwned collection
The owner of Hobbs, Phase Eight, and Whistles is the latest fashion retailer to suffer a cyberattack, leaving several IT systems offline and customers facing order delays. South African retail giant The Foschini Group…
Cyberattack Prompts Grocery Giant Ahold Delhaize to Disconnect Systems
The company says it took some of its systems offline to contain a security issue within its network.

Critical Progress MarkLogic Flaws Enable Remote Code Execution and Admin Takeover
Progress released urgent security updates for MarkLogic Server to fix a broad set of critical and high-severity flaws that could let attackers gain elevated access, create unauthorized administrator accounts, execute…

Critical MariaDB Flaws Can Let Attackers Execute Code and Steal Database Data
MariaDB has disclosed security flaws that, under specific conditions, could let attackers run code, access restricted database tables, and steal login credentials. The issues affect several server branches and MariaDB…
Fifth of CISOs Take Time Off to Avoid Patch Tuesday
Socura report claims CISOs are calling in sick or taking holiday to miss Patch Tuesday

Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers
Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to throw food away, several retail chains said. The attackers reached…

Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control
Two of 31 newly disclosed flaws in Progress Software's MarkLogic Server database could let an account given only some management privileges take administrator control of the server, the company says. Progress published…

GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in arbitrary code execution. "GitLab has remediated an issue…
Refrigeration Controller Hack Spoils Food Across European Supermarkets
A cyberattack targeted refrigeration controllers, setting refrigerators and freezers across hundreds of supermarkets to defrost.
GTA 6 leaker threatens to release full playable version of game ahead of official launch
The hacker behind a high-profile string of leaks involving the upcoming release of the Grand Theft Auto (GTA) 6 videogame has threatened to release a complete, playable build.
Scammers know your name, and they’re counting on you to reply
Scammers are finding different ways to use personal details exposed in data breaches to lure people into conversations. Last week , we showed how a Facebook Marketplace listing used the recipient’s name to make a text…
VMware is pushing so many patches, it thinks users need new tools to manage the flood
VMware has discovered so many flaws in its products using AI that it felt the need to create a new product to help users manage them. Prashanth Shenoy, vice president of product marketing in the VMware Cloud Foundation…

Low-Cost Android Phones Ship With Preinstalled Malware That Turns Them Into Residential Proxies
Low-cost Android smartphones have been shipped with malicious software baked into the device firmware, allowing bad actors to covertly install apps, conduct ad fraud, and turn devices into residential proxies. The…
Flock can now issue CVEs for its own products. Should we trust it?
Flock, the controversial public safety company entangled in controversy amid recurring law enforcement abuse of its products, gained authority to assign CVE IDs to vulnerabilities in its own products and grade those…

Maximum-Severity SSRF Flaw in SonicWall SMA Devices Under Attack
Attackers are currently targeting a critical vulnerability in SMA 1000 appliances, putting SonicWall customers in a familiar yet unenviable position.
Norway fines Microsoft ad firm $9.6 million over Grindr data sharing
Norway's Data Protection Authority (Datatilsynet) has fined Microsoft-owned advertising company Xandr NOK 92 million ($9.6M) for unlawfully processing and sharing sensitive data belonging to Grindr users in the country.
Prominent Ransomware Negotiator Faces Extortion Charges
Edward Dubrovsky, a longtime cybersecurity executive, was arrested and charged in Pennsylvania last week under conspiracy to extort money.
Yandex confirms service outage as users lose access to cloud files
Russian cloud services provider Yandex announced that drone attacks damaged three of its data centers, forcing it to shut down two facilities and partially disable a third.
Anthropic takes risky AI tests offline after models breach govt sites
Anthropic announced that its internal AI models undergoing "high-risk and cybersecurity evaluations" no longer have internet access following incidents involving U.S. government websites at the federal, state, and local…
No Identity, No Recovery: Cyber Resilience Starts With IAM
The proliferation of enterprise apps and the centrality of cloud identity providers requires an identity security rethink.
IonQ to buy zero-trust security firm Elisity in deal valued at up to $1.3 billion
IonQ announced Monday that it will acquire Elisity, a zero-trust network security firm, in an all-stock transaction valued at up to $1.3 billion that folds enterprise access control into the quantum computing company’s…
Chatbot refuseniks edge out users in the US, and they’re not for turning
If you thought everyone was into chatbots, think again: about half of US adults never use the AI tools, and most have no interest in starting. According to Pew Research Center, older adults are the least likely to use…
Ledger confirms spy chip implant behind wallet crypto thefts
Ledger has confirmed that some of its devices distributed through Southeast Asian reseller CryptoBilis were compromised with a hardware implant that drained users' cryptocurrency wallets.
Cyberattack shuts down refrigerators at French supermarkets
Attackers remotely defrosted refrigerators at multiple French supermarket chains overnight in a cyberattack that reportedly targeted Danfoss refrigeration controllers.

⚡ Weekly Recap: Helpdesk 0-Days, Rogue Certs, ShinyHunters Arrest, AI-Fooling Malware and More
Some meetings last longer than it took attackers to jump on a newly disclosed security flaw this week. Within hours, they were already testing it. That's not much time to read the warning, let alone do something about…
Luna Moth Leaks Shed Light on Ransomware Group's Inner Workings
Leaked documents suggest a multi-pronged operation, with social engineering and more technical attackers working together to manipulate a single target
FBI Arrests Suspect in FBI-Hacking Case
In September, hackers from a group called ShinyHunters announced that they stole a trove of FBI data about its own agents. It was an intelligence disaster . Last week, the FBI arrested (alternate link ) someone…
12th October – Threat Intelligence Report
For the latest discoveries in cyber research for the week of 12th October, please download our Threat Intelligence Bulletin. TOP ATTACKS AND BREACHES Denmark’s government has disclosed a breach involving its Central…
IonQ to Acquire Zero Trust Firm Elisity for Up to $1.3 Billion
The all-stock deal brings Elisity’s least-privilege access technology into IonQ’s security portfolio.
Inside AvisLoader: A Windows Malware Loader Built to Resist Disruption
A new Windows malware loader called AvisLoader uses encrypted peer-to-peer communications to make command-and-control infrastructure harder to disrupt. Varonis researchers explain how the malware uses ClickFix delivery…
CMMC Level 2 Non-Negotiable Requirements Explained | Huntress
Learn the CMMC Level 2 requirements you can’t skip, the new 88-point minimum score, and how the 180 day POA&M clock affects contract eligibility.
Cops can creep on Airbnb
Good Monday morning! Today's big story is an investigation from Joseph about cops and an AI tool that takes data from sites like Airbnb and Zillow and identifies specific properties. The internet is full of photos of…
Retail giant Ahold Delhaize takes systems offline after cyberattack
Retail giant Ahold Delhaize, one of the world's largest food retail chains, confirmed today that it had to take some systems offline in response to a "cybersecurity incident" affecting its network.
Ukrainian drone strikes on Yandex datacenters knock cloud and payments offline
Yandex engineers are working to restore services after Ukraine launched drone strikes on three of its five Russian datacenters. The strikes began overnight on October 7-8, "seriously damaging" Yandex's Sasovo datacenter…
Bricksforge WordPress Plugin Vulnerability Exploited in the Wild
The vulnerability tracked as CVE-2026-85097 can allow threat actors to take control of the targeted WordPress websites.
GitLab warns of max severity code execution vulnerability
GitLab warned users today to immediately patch a maximum-severity vulnerability in the CI/CD Regular Expression Compiler that could let remote attackers run arbitrary code on targeted instances.
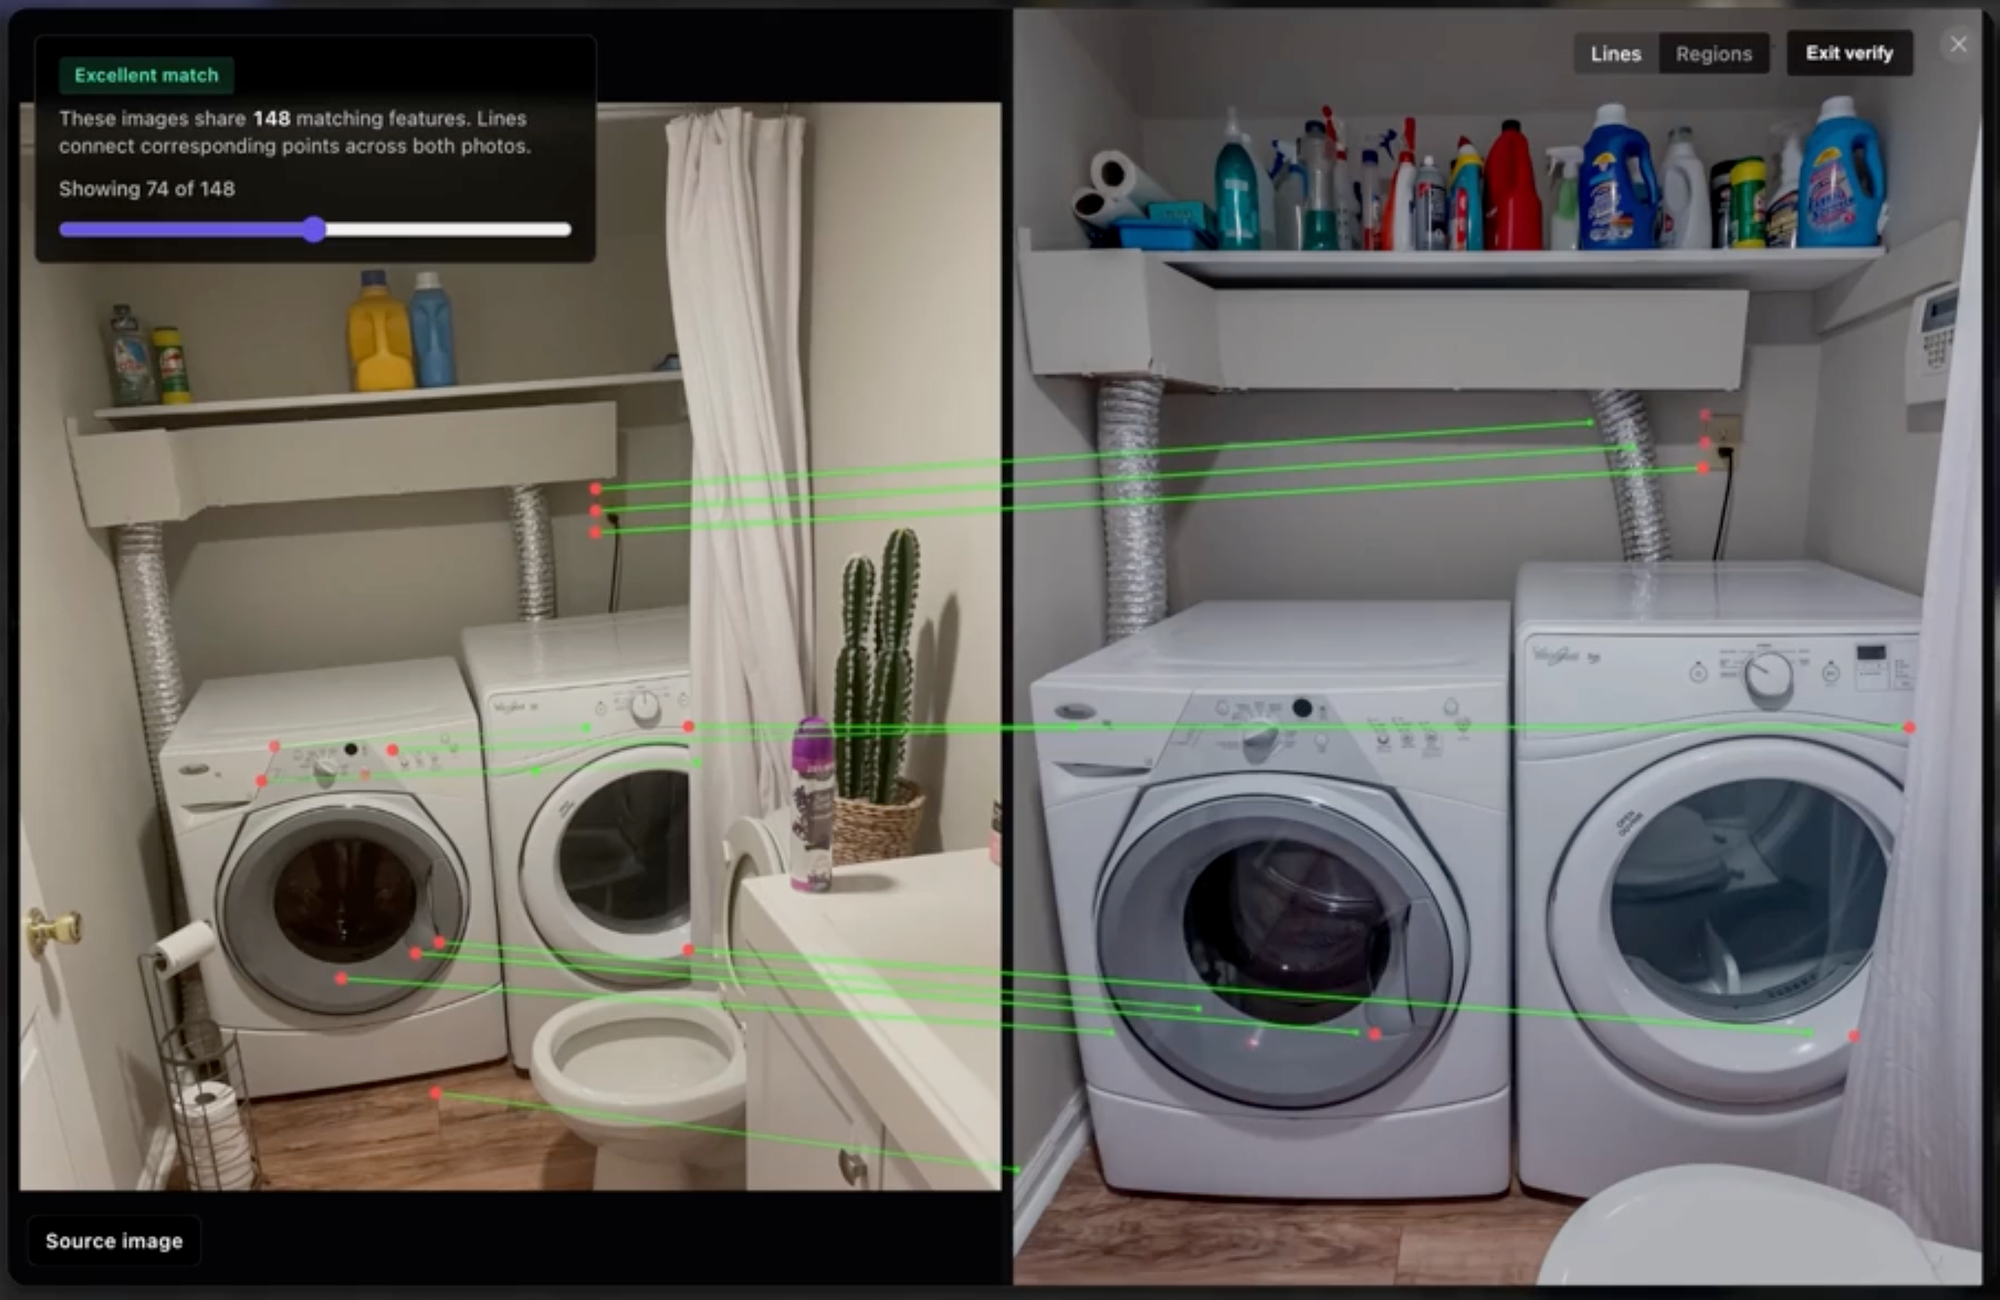
AI Company Lets Cops Pinpoint Specific Houses Based on a Single Interior Photo
An AI company now lets cops take a photo and nearly instantly figure out what specific home it was taken in, using only clues in the photo itself, and is clearly pulling data from sites like Zillow and Airbnb. The tool…
How “123456” became the key to almost 9 million personal records
An attacker reportedly used a leaked password to abuse a company’s legitimate access to Denmark’s population register (CPR). The weak password is remarkable, but the failure to spot millions of unusual searches made the…
Passing the Baton: Dark Reading Names New Editor-in-Chief
Fahmida Y Rashid will keep the momentum going as she leads Dark Reading.
Help the NCSC understand how organisations approach external attack surface risk
We're looking to hear from people involved in evaluating, selecting or adopting EASM.
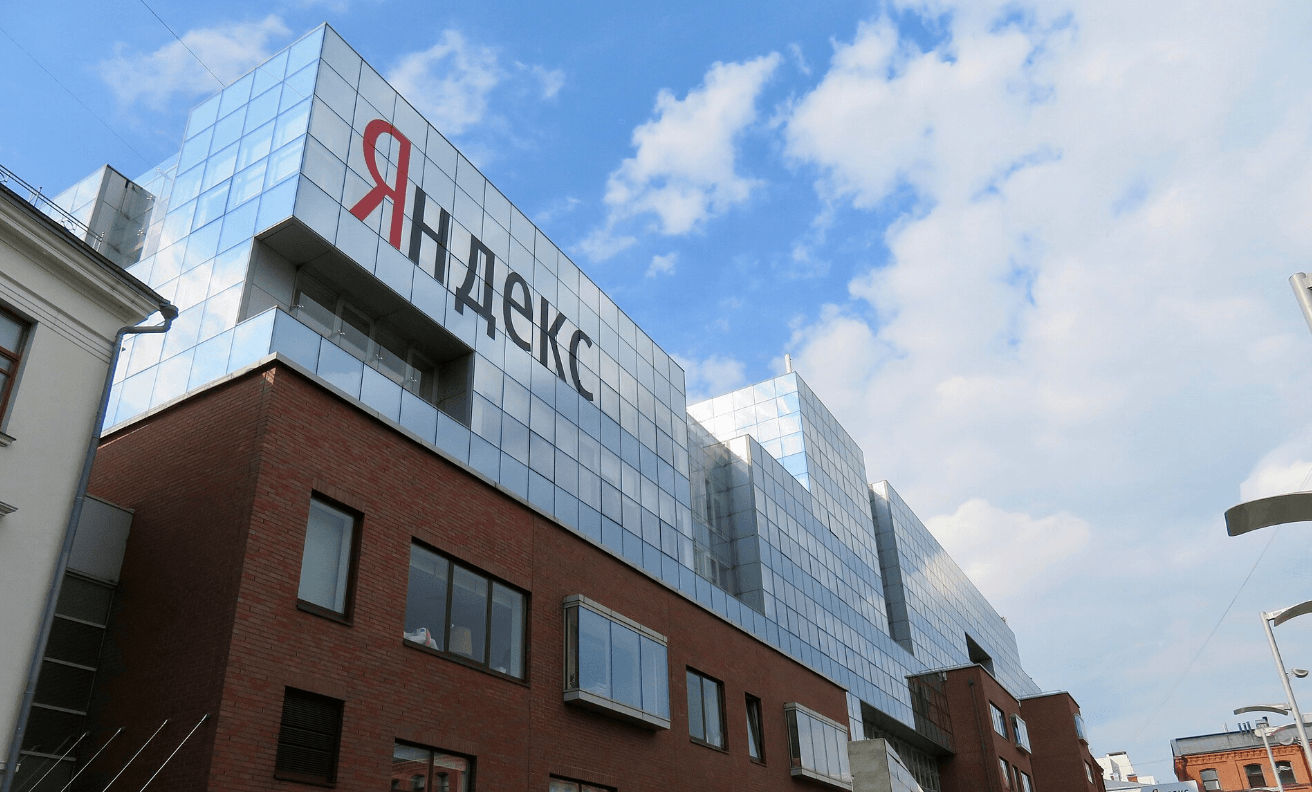
Ukraine strikes third Yandex data center, disrupting digital services across Russia
A third Yandex data center in Russia was hit by Ukrainian drones over the weekend, forcing it to shut down and causing further disruptions to cloud services, payments, deliveries and other online services across the…
Canonical Websites Disrupted in Second DDoS Attack This Year
The outage hit the main Ubuntu and Canonical websites, including the Ubuntu blog and developer portal.