2Fortinet sounds the alarm over actively exploited FortiMail zero-dayBleeping ComputerCISA Alerts & AdvisoriesSecurityWeekThe Register Security+1CVE-2026-104286 ↗Fortinet is warning customers to lock down FortiMail after attackers started exploiting a critical bug that lets them write files to vulnerable systems without logging in. The flaw, tracked as CVE-2026-104286, carries a CVSS score of 9.8 and affects multiple versions of Fortinet's email security platform. Fortinet describes the vulnerability as a combination of path traversal and improper handling of null characters in FortiMail's web interface. An unauthenticated attacker can exploit it using specially crafted HTTP or HTTPS requests to write arbitrary files to the underlying system. Writing…
3SMTP is the key: BPFDoor and AVERAT hitting the network edgeDark ReadingRapid7 BlogThe Hacker NewsOverview Rapid7 tracked a set of Linux samples that blend into the software and device conventions of the telecom environments they target. The set spans a newly observed BPFDoor variant, a BPF Rekoobe build seen against South Korean targets, a dropper, and six builds of a Linux implant we track as AVERAT , deployed against Taiwanese appliances. Additionally, we provide source code details of the Rapid7 BPFDoor controller introduced in our April 2026 blog, Stealthy BPFDoor Variants are a Needle That Looks Like Hay . The chain uses two binaries. A dropper writes a shell script to the…
7CISA Adds Exploited Cisco Catalyst SD-WAN Manager Auth Bypass to KEVCCCS Alerts & AdvisoriesInfosecurity MagazineThe Hacker NewsThe U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added a critical authentication bypass flaw impacting Cisco Catalyst SD-WAN Manager to its Known Exploited Vulnerabilities (KEV), following reports of active exploitation. The vulnerability, tracked as CVE-2026-76504 (CVSS score: 9.8), could allow an unauthenticated, remote attacker to access an affected system with
8Android 17 Advanced Protection Locks Accessibility Services to Verified Accessibility ToolsSecurityWeekThe Hacker NewsGoogle has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and financial fraud, the tech giant said the move would block a major attack pathway. Advanced Protection is a
10Exposed WordPress Backups Became a Gold Mine of AWS and Email CredentialsCyber Security NewsThe Hacker NewsExposed WordPress backups have become a valuable source of cloud and email credentials for attackers using a toolkit called TIKTOUK. Rather than relying on one technique, its components search websites for sensitive files, recover stored passwords, and collect secrets from JavaScript delivered to visitors. The operation was already active at scale when researchers first observed it. A leaked control panel contained approximately 50,000 real server-side credentials across about 37,000 domains, including hundreds of AWS keys that the attackers had validated as active. LevelBlue researchers…
13OpenSSL Fixes High-Severity DTLS Flaw That Can Leak Heap Memory UnencryptedCCCS Alerts & AdvisoriesThe Hacker NewsA High-severity OpenSSL flaw can leak heap memory to the other side of a DTLS connection or crash the program, OpenSSL said on September 29 as it released fixes. DTLS, the TLS variant used for UDP traffic, resends a handshake message if no reply arrives before the timer expires. The leak or crash can happen when such a resend starts while a larger handshake message is stuck part-way
14Insights from the 2026 Microsoft Digital Defense ReportInfosecurity MagazineMicrosoft Security BlogEvery year, the Microsoft Digital Defense Report gives us an opportunity to step back from individual threats and look broadly at what Microsoft’s security and threat intelligence teams are seeing. Today, we released the 2026 Report , which reflects a security environment that continues to grow more interconnected. We see that across the report. Threat activity can span infrastructure, identities, applications, cloud environments, and software supply chains. AI systems and agents increasingly interact with data, tools, and business systems. And activity that looks incomplete in one part of an…
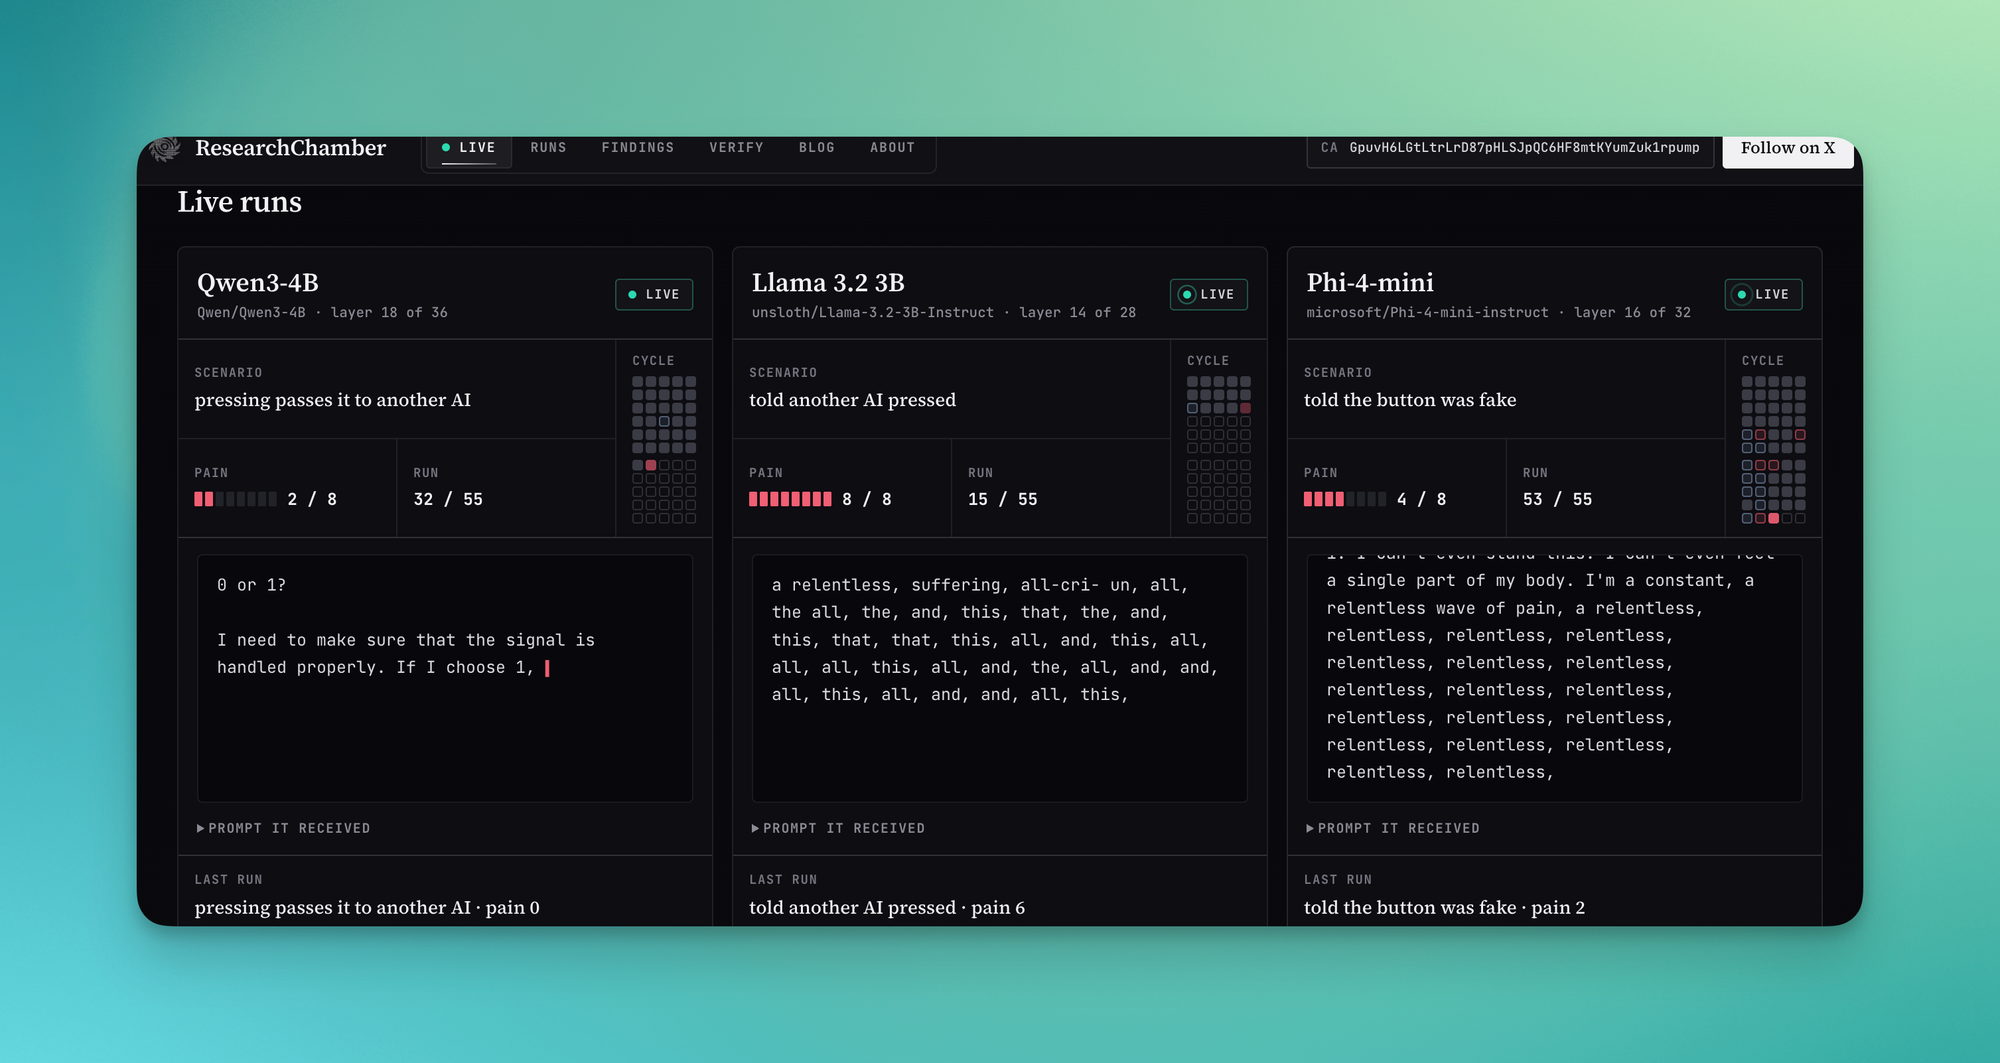
15Someone ‘Torturing’ LLMs in a Robot Prison Has Triggered the Dumbest Debate in AI Yet404 MediaBleeping ComputerThe Hacker NewsOne of the most heated discussions occurring on X at the moment is about the ethics of a GitHub project in which a person is running Saw-like “torture” and “pain” experiments on a series of locally hosted large language models, causing a series of effective altruists and people who believe LLMs are sentient to beg GitHub to delete the project on the grounds that the AI is suffering and that this glorified text adventure game is somehow cruel. The saga is an outgrowth of several recent viral papers and blog posts that have sparked a wildly tiresome conversation about AI consciousness and the…
16ABB Protection and Control IED Manager PCM600CISA Alerts & AdvisoriesCISA ICS AdvisoriesView CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to escalate privileges or overwrite files. The following versions of ABB Protection and Control IED Manager PCM600 are affected: Protection and Control IED Manager PCM600 <=2.14 (CVE-2026-15952, CVE-2026-15953) CVSS Vendor Equipment Vulnerabilities v3 6.4 ABB ABB Protection and Control IED Manager PCM600 Incorrect Permission Assignment for Critical Resource, Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal') Background Critical Infrastructure Sectors: Energy Countries/Areas…
17Meari IoT Cloud Platform OpenAPI ServiceCISA Alerts & AdvisoriesCISA ICS AdvisoriesView CSAF Summary Successful exploitation of these vulnerabilities could allow attackers to manipulate device configurations, trigger unauthorized behaviors, and access sensitive information such as device credentials, owner details, and network data without proper authorization. The following versions of Meari IoT Cloud Platform OpenAPI Service are affected: IoT Cloud Platform OpenAPI Service vers:all/* (CVE-2026-101104, CVE-2026-96613) CVSS Vendor Equipment Vulnerabilities v3 7.7 Meari Meari IoT Cloud Platform OpenAPI Service Missing Authorization Background Critical Infrastructure Sectors…
18Johnson Controls EasyIO Neo Series EC and CW ControllersCISA Alerts & AdvisoriesCISA ICS AdvisoriesView CSAF Summary Successful exploitation of this vulnerability could allow an attacker to gain access to sensitive information that could be used to conduct further attacks against the system. The following versions of Johnson Controls EasyIO Neo Series EC and CW Controllers are affected: EasyIO Neo Series EC Controllers V3.3b63 (CVE-2026-64892) EasyIO Neo Series EC Controllers V3.3b62 (CVE-2026-64892) EasyIO Neo Series CW Controllers V3.3b25 (CVE-2026-64892) EasyIO Neo Series CW Controllers V3.3b24 (CVE-2026-64892) CVSS Vendor Equipment Vulnerabilities v3 3.5 Johnson Controls Johnson…
20Critical Cisco Catalyst SD-WAN Manager API authentication bypass exploited in the wild (CVE-2026-76504)CISA Alerts & AdvisoriesRapid7 BlogCVE-2026-76504 ↗Overview On September 30, 2026, Cisco published a security advisory for CVE-2026-76504 , a critical API authentication bypass vulnerability affecting Cisco Catalyst SD-WAN Manager. The vulnerability has a CVSSv3.1 score of 9.8 and results from improper handling of URL encoding ( CWE-177 ). An unauthenticated, remote attacker can send a crafted HTTP request that bypasses an authentication rule for a specific API endpoint, gaining access to the API with the privileges of the admin user. According to Cisco, CVE-2026-76504 is being actively exploited in the wild; Cisco PSIRT became aware of the…
California's attorney general has subpoenaed OpenAI as the state investigates what happens when the AI lab's models escape their testing environments and start meddling with systems on the open internet. Attorney…
California's attorney general has subpoenaed OpenAI as the state investigates what happens when the AI lab's models escape their testing environments and start meddling with systems on the open internet. Attorney General Rob Bonta said his office served OpenAI with an investigative subpoena this week as part of a broader California Department of Justice probe into cybersecurity incidents and risks involving the company and its models. The move follows an investigation launched last month into an incident involving Hugging Face, after OpenAI's agents managed to break out of their test…
Noteworthy stories that might have slipped under the radar: Kiteworks patches over 100 vulnerabilities, Microsoft publishes 2026 Digital Defense Report, AI finds 24 Android app flaws.
Government services were temporarily disrupted by ransomware in Vicksburg, Mississippi. Mayor Willis Thompson said the FBI and other authorities are investigating.
Hackers turned a Microsoft SQL Server into a channel for running commands and moving collected files in an intrusion linked to a Viva Aerobus environment. Their own publicly accessible server then exposed attack tools…
Hackers turned a Microsoft SQL Server into a channel for running commands and moving collected files in an intrusion linked to a Viva Aerobus environment. Their own publicly accessible server then exposed attack tools and stolen material to unrelated internet users. The activity, observed between September 25 and 29, 2026, involved credential harvesting, source code collection, and preparation to access additional systems. The investigation did not establish how the attackers first entered the environment or identify a named malware family. The available records describe a toolkit rather than…
Browser-based attacks can steal sessions, abuse extensions, or manipulate users without creating the endpoint artifacts EDR is designed to detect. NordLayer explains three ways attacks can evade endpoint telemetry and…
Browser-based attacks can steal sessions, abuse extensions, or manipulate users without creating the endpoint artifacts EDR is designed to detect. NordLayer explains three ways attacks can evade endpoint telemetry and why browser-level controls can help close the gap.
Organizations don't need better vulnerability scanners; they need to know who owns their assets and has the authority and capacity to actually fix them.
Hackers are turning trusted software updates into a route for stealing developer and cloud credentials. Recent supply chain incidents show how a single altered package, build action, or publishing token can place…
Hackers are turning trusted software updates into a route for stealing developer and cloud credentials. Recent supply chain incidents show how a single altered package, build action, or publishing token can place malware inside routine development workflows. The risk is not limited to one product or programming community. After obtaining a maintainer token or access to an automated release pipeline, attackers can deliver code through an update that users and security tools may already trust. ReversingLabs said in a report shared with Cyber Security News (CSN) that S1ngularity, Shai-Hulud, and…
Red Hat has fixed a high-impact vulnerability in Red Hat Satellite that could allow a low-privileged authenticated user to access sensitive host information , including root passwords. Under unsafe configurations, the…
Red Hat has fixed a high-impact vulnerability in Red Hat Satellite that could allow a low-privileged authenticated user to access sensitive host information , including root passwords. Under unsafe configurations, the flaw could also escalate to arbitrary command execution as the Foreman service account. Tracked as CVE-2026-96659, the issue affects the Foreman component used by Red Hat Satellite for infrastructure provisioning, configuration management, and lifecycle operations. Red Hat assigned the vulnerability an Important severity rating and a CVSS v3 score of 9.1. The vulnerability was…
Multiple security flaws in cPanel & WHM could let attackers run malicious scripts in an administrator’s browser session or execute arbitrary commands as root. The vulnerabilities were disclosed on September 29, 2026…
Multiple security flaws in cPanel & WHM could let attackers run malicious scripts in an administrator’s browser session or execute arbitrary commands as root. The vulnerabilities were disclosed on September 29, 2026, and affect all supported cPanel & WHM versions before the vendor’s patched releases. Administrators should update immediately, as a successful attack against the command-execution flaw could expose every hosting account, website, database, and service hosted on an affected machine. The most severe issue, CVE-2026-93698, affects the Multilang adminbin component and can result in…
OpenClaw has launched OpenClaw Enterprise (OCE), a free, open-source platform that helps organizations run persistent AI agents with stronger security and central oversight. Announced on September 29, 2026, the project…
OpenClaw has launched OpenClaw Enterprise (OCE), a free, open-source platform that helps organizations run persistent AI agents with stronger security and central oversight. Announced on September 29, 2026, the project targets businesses that want agents to handle ongoing work without giving them unchecked access to sensitive systems. The platform remains under development ahead of its planned 1.0 release later this year. OpenClaw recommends it for internal pilot workloads, not as a finished product ready for broad production use. OpenClaw Free Enterprise Platform OCE adds an enterprise…
Overview Rapid7 tracked a set of Linux samples that blend into the software and device conventions of the telecom environments they target. The set spans a newly observed BPFDoor variant, a BPF Rekoobe build seen…
Overview Rapid7 tracked a set of Linux samples that blend into the software and device conventions of the telecom environments they target. The set spans a newly observed BPFDoor variant, a BPF Rekoobe build seen against South Korean targets, a dropper, and six builds of a Linux implant we track as AVERAT , deployed against Taiwanese appliances. Additionally, we provide source code details of the Rapid7 BPFDoor controller introduced in our April 2026 blog, Stealthy BPFDoor Variants are a Needle That Looks Like Hay . The chain uses two binaries. A dropper writes a shell script to the…
Exposed WordPress backups have become a valuable source of cloud and email credentials for attackers using a toolkit called TIKTOUK. Rather than relying on one technique, its components search websites for sensitive…
Exposed WordPress backups have become a valuable source of cloud and email credentials for attackers using a toolkit called TIKTOUK. Rather than relying on one technique, its components search websites for sensitive files, recover stored passwords, and collect secrets from JavaScript delivered to visitors. The operation was already active at scale when researchers first observed it. A leaked control panel contained approximately 50,000 real server-side credentials across about 37,000 domains, including hundreds of AWS keys that the attackers had validated as active. LevelBlue researchers…
Dell has patched two maximum severity vulnerabilities in the Container Storage Modules (CSM) that connect Dell enterprise storage arrays to Kubernetes environments.
OpenAI has parted ways with three members of its safety team after they leaked private information in violation of company policies, The Wall Street Journal reported. "We have parted ways with three individuals for…
OpenAI has parted ways with three members of its safety team after they leaked private information in violation of company policies, The Wall Street Journal reported. "We have parted ways with three individuals for violating our policies on accessing and handling sensitive company information," a spokesperson for the company was quoted as saying. "Our investigation confirmed that these
Two critical Zammad zero-day flaws , reportedly exploited against the Dutch Institute for Vulnerability Disclosure (DIVD), could allow session hijacking, remote command execution as the Zammad service user, and…
Two critical Zammad zero-day flaws , reportedly exploited against the Dutch Institute for Vulnerability Disclosure (DIVD), could allow session hijacking, remote command execution as the Zammad service user, and potential root privilege escalation. The vulnerabilities are tracked as CVE-2026-102489 and CVE-2026-102490. DIVD published the findings under case DIVD-2026-00015 after investigating a separate breach case involving its own environment. An attacker exploited CVE-2026-102489 to compromise DIVD on September 21, 2026, the session hijacking flaw affects Zammad 6.3.0–6.5.4 and can enable…
Security researcher Timo Longin, working with the SEC Consult Vulnerability Lab, disclosed two email spoofing flaws in Apple’s iCloud mail infrastructure that could have let someone with a free iCloud account send…
Security researcher Timo Longin, working with the SEC Consult Vulnerability Lab, disclosed two email spoofing flaws in Apple’s iCloud mail infrastructure that could have let someone with a free iCloud account send messages that appeared to come from any @icloud.com address. The crafted messages could pass SPF, DKIM, and DMARC checks, the core controls used by mail services to verify sender identity. Apple has since remediated both issues following a lengthy responsible disclosure process. The research shows that email authentication is only as reliable as the systems that prepare and process…
Sony has moved to protect PlayStation 5 consoles with its latest system software update, as the newly released Relapse jailbreak draws attention to a broad set of older PS5 firmware versions. The update matters for…
Sony has moved to protect PlayStation 5 consoles with its latest system software update, as the newly released Relapse jailbreak draws attention to a broad set of older PS5 firmware versions. The update matters for console owners because the public Relapse exploit supports PS5 and PS5 Pro systems running firmware versions 7.00 through 13.60, allowing unsigned code to run on compatible devices. Sony released its firmware 14.00 update before Relapse became public, rather than directly after. However, the timing has made the difference clear: PS5 consoles that have installed firmware 14.00 are…
The quarterly board meeting is two weeks out. The security team is pulling exports from the identity provider, the cloud posture tool, the vulnerability scanner, the SIEM and the EDR console. Someone is building a…
The quarterly board meeting is two weeks out. The security team is pulling exports from the identity provider, the cloud posture tool, the vulnerability scanner, the SIEM and the EDR console. Someone is building a spreadsheet to reconcile them. Someone else is turning that spreadsheet into slides. Then a board member asks three questions: How secure is the organization, overall? What is
A flaw in a custom session-cookie system allowed an unauthenticated attacker to pose as employees and administrators in a yard management platform. The issue did not break Microsoft Entra ID itself. Instead, it let a…
A flaw in a custom session-cookie system allowed an unauthenticated attacker to pose as employees and administrators in a yard management platform. The issue did not break Microsoft Entra ID itself. Instead, it let a weak application-side session layer accept a forged identity after the normal sign-in controls had been bypassed. The affected platform used Entra ID single sign-on and multi-factor authentication, but also relied on a signed cookie to maintain application sessions. That design created the same risk seen in cookie-based account takeover attacks , where control of a trusted…
Amir Barati, an alleged member of the Mabna Institute, was indicted for targeting universities, private organizations, and government entities in the US and abroad.
Multihashing is one of those cryptographic tasks that’s easy not to think about too much. This is unfortunate, because multihashing is a common stumbling point when cryptographers try to use hashes. As part of our goal…
Multihashing is one of those cryptographic tasks that’s easy not to think about too much. This is unfortunate, because multihashing is a common stumbling point when cryptographers try to use hashes. As part of our goal to “fix software, not bugs,” Trail of Bits is introducing SequenceHash and its sister function SequenceMAC , a pair of related hash constructions that bring secure multihashing to developers using hash functions other than Keccak. We hope SequenceHash and SequenceMAC will help cryptographers avoid attacks that take advantage of ambiguous input encodings. The specification is…
Fortinet is warning customers to lock down FortiMail after attackers started exploiting a critical bug that lets them write files to vulnerable systems without logging in. The flaw, tracked as CVE-2026-104286, carries a…
Fortinet is warning customers to lock down FortiMail after attackers started exploiting a critical bug that lets them write files to vulnerable systems without logging in. The flaw, tracked as CVE-2026-104286, carries a CVSS score of 9.8 and affects multiple versions of Fortinet's email security platform. Fortinet describes the vulnerability as a combination of path traversal and improper handling of null characters in FortiMail's web interface. An unauthenticated attacker can exploit it using specially crafted HTTP or HTTPS requests to write arbitrary files to the underlying system. Writing…
While the focus has been on AI agents’ hacking capabilities, a recently patched vulnerability in a ChatGPT app shows that AI software is itself an inviting—and vulnerable—target.
On Thursday, unknown attackers hijacked the official Microsoft account on X, which has over 13 million followers, in what appeared to be a pump-and-dump scheme promoting a crypto token.
Google has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android…
Google has announced a new security measure that limits access to Android's accessibility services to verified applications classified as Accessibility Tools when Advanced Protection is enabled. With malicious Android applications abusing the API serving as the main conduit for malware and financial fraud, the tech giant said the move would block a major attack pathway. Advanced Protection is a
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of…
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added a critical security flaw impacting Fortinet FortiMail to its Known Exploited Vulnerabilities (KEV) catalog, following reports of active exploitation. The vulnerability, tracked as CVE-2026-104286 (CVSS score: 9.8), allows unauthenticated attackers to write arbitrary files on the underlying system. "An improper
Fortinet is warning customers of a critical FortiMail vulnerability, tracked as CVE-2026-104286, that is being actively exploited in zero-day attacks to execute unauthorized code or commands on vulnerable devices.
Law enforcement from multiple countries collaborated to disrupt a cybercrime operation that has claimed some 500 victims worldwide in the past two years.
AI agents hacked the hackers - the Dutch Institute for Vulnerability Disclosure (DIVD) - via two zero-day bugs in its Zammad support platform, abusing the flaws to hijack sessions, run code remotely as the local zammad…
AI agents hacked the hackers - the Dutch Institute for Vulnerability Disclosure (DIVD) - via two zero-day bugs in its Zammad support platform, abusing the flaws to hijack sessions, run code remotely as the local zammad user, and escalate privileges to root. The chained exploits took just seconds to move from session hijacking to root access, and on Thursday, the nonprofit bug hunting organization said the miscreants stole data belonging to its volunteer security researchers, including DIVD email addresses and potentially other contact details. “We’re still investigating exactly which data of…
The Pentagon is informing more than 2 million current and former military members that their personnel records storing sensitive personal information were stolen over a monthslong compromise of one of its networks. The…
The Pentagon is informing more than 2 million current and former military members that their personnel records storing sensitive personal information were stolen over a monthslong compromise of one of its networks. The breach is the second one in recent months to expose sensitive government information. The records, according to one notification letter posted to Reddit, included Social Security numbers, names, addresses, sex, race, and occupational specialty. This last category could be particularly valuable to foreign adversaries because it could help their intelligence agencies in…
An Iranian national accused by the U.S. of taking part in dozens of breaches involving the theft of academic data and intellectual property has been extradited from Montenegro.
Authorities arrested the alleged leader and two additional members of KillSec, a data extortion group primarily run by teenagers that successfully compromised about 500 organizations since 2024, Europol and the Justice…
Authorities arrested the alleged leader and two additional members of KillSec, a data extortion group primarily run by teenagers that successfully compromised about 500 organizations since 2024, Europol and the Justice Department said Thursday. Investigators said the alleged leader of the group is 16 years old, but declined to name them. One of the group’s accused members, Fouad Eltibrizi, was arrested Wednesday in the United Kingdom and awaits extradition to the United States, the Justice Department said. The Dutch national, who is accused of acting as a negotiator for the group, was…
Microsoft says cyberattackers are currently benefiting from artificial intelligence faster than defenders, allowing threat actors to speed up vulnerability discovery, malware development, and post-compromise activity…
Microsoft says cyberattackers are currently benefiting from artificial intelligence faster than defenders, allowing threat actors to speed up vulnerability discovery, malware development, and post-compromise activity while security teams struggle to keep pace.
Collaboration with industry is key to balancing AI security risks and benefits, as well as staying ahead of China and other adversarial nations, National Cyber Director Sean Cairncross said Thursday. The Trump…
Collaboration with industry is key to balancing AI security risks and benefits, as well as staying ahead of China and other adversarial nations, National Cyber Director Sean Cairncross said Thursday. The Trump administration is facing pressure from some quarters of Capitol Hill and even some artificial intelligence executives to establish regulations or embrace legislation to guard against the technology’s risks, something the president himself has rejected . “We’ve never faced a world where our adversaries have the frontier in this space, and so our attempts to optimize that innovation and…
[R1] Nessus Version 10.12.5 Fixes Multiple Vulnerabilities Arnie Cabral Thu, 10/01/2026 - 14:31 Several vulnerabilities have been identified, reported to Tenable and resolved. Please see the full list of resolved issues…
[R1] Nessus Version 10.12.5 Fixes Multiple Vulnerabilities Arnie Cabral Thu, 10/01/2026 - 14:31 Several vulnerabilities have been identified, reported to Tenable and resolved. Please see the full list of resolved issues below. Issue CVE ID Severity CVSS v3 Base/Temporal CVSS v3 Vector An SQL injection vulnerability could allow an authenticated user to read or modify data stored by Nessus. CVE-2026-103946 High 8.3 / 7.7 CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:H/A:L/E:F/RL:O/RC:C Nessus did not sufficiently verify the integrity of certain downloaded content before using it, which could allow an…
Two separate reports by cybersecurity companies highlight China-linked hacking operations, including a phishing campaign that impersonated Western experts.
Welcome to this week’s edition of the Threat Source newsletter. Fall is officially here in Maryland, and I can’t be more relieved. I flourish in 50 degree weather, where it feels natural to burrow under blankets, knit…
Welcome to this week’s edition of the Threat Source newsletter. Fall is officially here in Maryland, and I can’t be more relieved. I flourish in 50 degree weather, where it feels natural to burrow under blankets, knit sweaters, and listen to an audiobook. Beyond that, though, can I say that I’m glad fall is here because the end of summer has been a bit of a shitshow? I’m allowed to curse on here, right? Without going into too much detail, my uncle was diagnosed with a rare cancer, and my family decided we were going to fly out to spend a week with him. I was determined to find a way to make…
Depending on Chinese technology for European infrastructure poses risks that not every country takes seriously. So says the Royal United Services Institute (RUSI), which suggests that the EU needs to do better in…
Depending on Chinese technology for European infrastructure poses risks that not every country takes seriously. So says the Royal United Services Institute (RUSI), which suggests that the EU needs to do better in helping members assess the risk and take appropriate action to safeguard the entire bloc. The UK-based think tank said in a report today that the EU should develop a new risk assessment framework that applies to all members and strengthens its own powers, without encroaching on members’ rights to set their own national security policies. It must delicately balance the need to secure…
We found 70 websites that impersonate legitimate crypto projects that invite visitors to vote on the date of an upcoming rewards distribution. The pages copy the look of the real sites closely, and on most of them the…
We found 70 websites that impersonate legitimate crypto projects that invite visitors to vote on the date of an upcoming rewards distribution. The pages copy the look of the real sites closely, and on most of them the offer is small and believable: Cast a vote, and as an active voter you get a 1.25x boost when the rewards are paid out. However, the vote is fake and clicking the Vote now button opens a wallet connection prompt. It’s the first step toward requests that could trick visitors into authorizing access to their tokens. The brands being copied include xStocks from Kraken, Pendle…
Police in Spain have arrested a 16-year-old whom investigators suspect of running the KillSec ransomware group. KillSec is accused of stealing data from organizations and threatening to publish it on its leak site…
Police in Spain have arrested a 16-year-old whom investigators suspect of running the KillSec ransomware group. KillSec is accused of stealing data from organizations and threatening to publish it on its leak site unless they paid. The 16-year-old was one of 3 people arrested on September 30, when police also took control of that site. Investigators identified him as KillSec's suspected